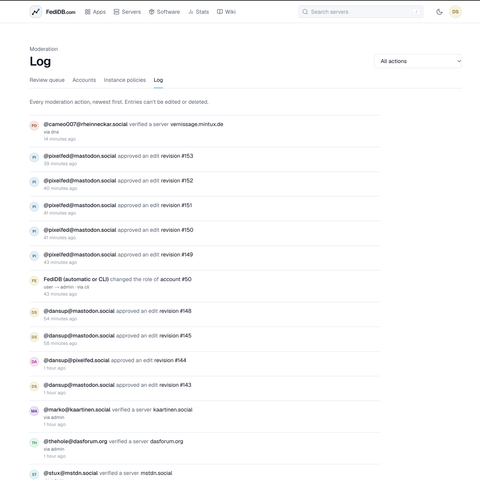
https://fedidb.com is essentially now a wiki, and we store no passwords or emails, its all powered by oauth and your existing fediverse accounts!
I need more trusted people to help moderate, so I will reach out to a few people.


@hongminhee@hollo.social
1,118 following1,657 followers
An intersectionalist, feminist, and socialist living in Seoul (UTC+09:00). @tokolovesme's spouse. Who's behind @fedify, @hollo, and @botkit. Write some free software in #TypeScript, #Haskell, #Rust, & #Python. They/them.
서울에 사는 交叉女性主義者이자 社會主義者. 金剛兔(@tokolovesme)의 配偶者. @fedify, @hollo, @botkit 메인테이너. #TypeScript, #Haskell, #Rust, #Python 等으로 自由 소프트웨어 만듦.
https://fedidb.com is essentially now a wiki, and we store no passwords or emails, its all powered by oauth and your existing fediverse accounts!
I need more trusted people to help moderate, so I will reach out to a few people.
Holloの複数のセキュリティ脆弱性に対応するセキュリティアップデートがリリースされました。お早めにアップデートしてください!
https://hollo.social/@hollo/01a1493c-36f9-7992-a6e9-5d10cd3201b7
hollo.social
### Hollo security updates: 0.8.16 and 0.9.24 If you run Hollo, update to [0.8.16] or [0.9.24] now. These releases fix [GHSA-v2qh-w789-xxj6], a missing ownership check in status deletion, and include fixes for three vulnerabilities in Fedify that affect Hollo. They also include a fix for a fourth Fedify vulnerability whose affected API Hollo does not use. For [GHSA-v2qh-w789-xxj6], an authenticated client with the `write:statuses` scope could delete a post belonging to another local account or a cached remote post by its local UUID. The deletion response could also disclose the post's contents, including private content. This required an access token on the receiving Hollo instance. For remote posts, the affected record was Hollo's cached copy. The fix restricts both lookup and deletion to the account associated with the token and returns the existing not-found response for other accounts' posts. It first ships in 0.8.16 and 0.9.24; earlier releases on both supported lines, including 0.9.23, lack this check. For [GHSA-97w4-f4rq-mgqm], Fedify's document loaders followed alternate-document links from HTTP headers or HTML without preserving the redirect limit, visited-URL history, or cancellation signal. An unauthenticated inbox request pointing to an attacker-controlled signing-key URL could trigger an endless chain of outbound requests and DNS lookups, exhausting server resources. Alternate-document links now share the 20-hop limit and loop detection with HTTP redirects, and preserve cancellation. The first fixed Hollo releases were [0.8.13] and [0.9.20], incorporating Fedify 2.1.25 and 2.2.14. Earlier releases on those Hollo lines are affected. For [GHSA-4qhx-hhwf-8685], Fedify authenticated an incoming activity's actor but accepted an activity ID on a different origin. An attacker with an actor and signing key on a server they controlled could supply embedded objects claiming to live on another server. Depending on the application's own checks, those objects could be stored under forged IDs. Sending a forged activity with a genuine activity's ID first could also suppress the genuine delivery as a duplicate. No account on the receiving Hollo instance was required. The fix rejects activities whose IDs have a different origin from their actors before they enter the inbox queue or duplicate cache. For [GHSA-8863-8468-7hq7], Fedify checked whether an actor document listed a signing key, but did not require the document's ID to match the actor ID it requested. An attacker could have activities authenticated as a victim if fetching the victim's exact actor ID led to an actor document whose key the attacker controlled. This depended on the server hosting the victim's actor ID redirecting or serving that document; an arbitrary redirect elsewhere on the server was not enough. The fix requires an exact actor ID match. Hollo's built-in key cache automatically ignores entries stored under the weaker check and fetches and verifies those keys again, so operators do not need to clear it manually. Both of these authentication fixes first reached Hollo in [0.8.15] and [0.9.23], incorporating Fedify 2.1.30 and 2.2.19. Earlier releases on the corresponding Hollo lines are affected. Install the newer 0.8.16 or 0.9.24 release to receive the status deletion fix too. The other Fedify advisory, [GHSA-39gj-rchc-q5m3], concerns `Context.routeActivity()`: after authenticating a fetched activity, it could queue or forward the caller's unverified copy. Hollo does not call this API, so its supported release lines are not exposed to this path. The dependency fix was nevertheless included in [0.8.14] and [0.9.21]. For full technical details on the upstream issues, see the linked advisories and the [October 4 Fedify announcement] and [October 16 Fedify announcement]. The supported Hollo release lines are 0.8.x and 0.9.x under the [Hollo security policy]. Operators on 0.7.x or earlier should move to a supported line. For 0.8.x deployments, update to [0.8.16]: ~~~~ bash docker pull ghcr.io/fedify-dev/hollo:0.8.16 ~~~~ For 0.9.x deployments, update to [0.9.24]: ~~~~ bash docker pull ghcr.io/fedify-dev/hollo:0.9.24 ~~~~ After pulling the image, recreate your Hollo container using the new image. With Docker Compose, update the image tag in your Compose file and run `docker compose up -d`. For source deployments, check out the corresponding release tag, run `pnpm install --frozen-lockfile` with that tag's pinned pnpm version, run `pnpm run build`, and restart the server. If you have a large 0.9.x database and are upgrading from a release before 0.9.20, follow the [0.9.20 index preparation instructions] before starting the new version to avoid blocking writes during its automatic migration. Thanks to Yami Odymel (@yamiodymel@misskey.io) for reporting the status deletion issue to Hollo, to Adel Zaitri ([@adelzaitri]) for reporting the alternate-document fetch chains to Fedify, and to ChanHaeng Lee (@2chanhaeng@hackers.pub) for reporting the inbox activity origin mismatch to Fedify. The activity routing and actor document identity issues were found by the Fedify maintainers with AI assistance. If anything is unclear, ask below. [0.8.16]: https://github.com/fedify-dev/hollo/releases/tag/0.8.16 [0.9.24]: https://github.com/fedify-dev/hollo/releases/tag/0.9.24 [GHSA-v2qh-w789-xxj6]: https://github.com/fedify-dev/hollo/security/advisories/GHSA-v2qh-w789-xxj6 [GHSA-97w4-f4rq-mgqm]: https://github.com/fedify-dev/fedify/security/advisories/GHSA-97w4-f4rq-mgqm [0.8.13]: https://github.com/fedify-dev/hollo/releases/tag/0.8.13 [0.9.20]: https://github.com/fedify-dev/hollo/releases/tag/0.9.20 [GHSA-4qhx-hhwf-8685]: https://github.com/fedify-dev/fedify/security/advisories/GHSA-4qhx-hhwf-8685 [GHSA-8863-8468-7hq7]: https://github.com/fedify-dev/fedify/security/advisories/GHSA-8863-8468-7hq7 [0.8.15]: https://github.com/fedify-dev/hollo/releases/tag/0.8.15 [0.9.23]: https://github.com/fedify-dev/hollo/releases/tag/0.9.23 [GHSA-39gj-rchc-q5m3]: https://github.com/fedify-dev/fedify/security/advisories/GHSA-39gj-rchc-q5m3 [0.8.14]: https://github.com/fedify-dev/hollo/releases/tag/0.8.14 [0.9.21]: https://github.com/fedify-dev/hollo/releases/tag/0.9.21 [October 4 Fedify announcement]: https://github.com/fedify-dev/fedify/discussions/1221 [October 16 Fedify announcement]: https://github.com/fedify-dev/fedify/discussions/1301 [Hollo security policy]: https://github.com/fedify-dev/hollo/blob/main/SECURITY.md [0.9.20 index preparation instructions]: https://github.com/fedify-dev/hollo/blob/0.9.24/CHANGES.md#version-0920 [@adelzaitri]: https://github.com/adelzaitri
If you run Hollo, update to 0.8.16 or 0.9.24 now. These releases fix GHSA-v2qh-w789-xxj6, a missing ownership check in status deletion, and include fixes for three vulnerabilities in Fedify that affect Hollo. They also include a fix for a fourth Fedify vulnerability whose affected API Hollo does not use.
For GHSA-v2qh-w789-xxj6, an authenticated client with the write:statuses scope could delete a post belonging to another local account or a cached remote post by its local UUID. The deletion response could also disclose the post's contents, including private content. This required an access token on the receiving Hollo instance. For remote posts, the affected record was Hollo's cached copy. The fix restricts both lookup and deletion to the account associated with the token and returns the existing not-found response for other accounts' posts. It first ships in 0.8.16 and 0.9.24; earlier releases on both supported lines, including 0.9.23, lack this check.
For GHSA-97w4-f4rq-mgqm, Fedify's document loaders followed alternate-document links from HTTP headers or HTML without preserving the redirect limit, visited-URL history, or cancellation signal. An unauthenticated inbox request pointing to an attacker-controlled signing-key URL could trigger an endless chain of outbound requests and DNS lookups, exhausting server resources. Alternate-document links now share the 20-hop limit and loop detection with HTTP redirects, and preserve cancellation. The first fixed Hollo releases were 0.8.13 and 0.9.20, incorporating Fedify 2.1.25 and 2.2.14. Earlier releases on those Hollo lines are affected.
For GHSA-4qhx-hhwf-8685, Fedify authenticated an incoming activity's actor but accepted an activity ID on a different origin. An attacker with an actor and signing key on a server they controlled could supply embedded objects claiming to live on another server. Depending on the application's own checks, those objects could be stored under forged IDs. Sending a forged activity with a genuine activity's ID first could also suppress the genuine delivery as a duplicate. No account on the receiving Hollo instance was required. The fix rejects activities whose IDs have a different origin from their actors before they enter the inbox queue or duplicate cache.
For GHSA-8863-8468-7hq7, Fedify checked whether an actor document listed a signing key, but did not require the document's ID to match the actor ID it requested. An attacker could have activities authenticated as a victim if fetching the victim's exact actor ID led to an actor document whose key the attacker controlled. This depended on the server hosting the victim's actor ID redirecting or serving that document; an arbitrary redirect elsewhere on the server was not enough. The fix requires an exact actor ID match. Hollo's built-in key cache automatically ignores entries stored under the weaker check and fetches and verifies those keys again, so operators do not need to clear it manually.
Both of these authentication fixes first reached Hollo in 0.8.15 and 0.9.23, incorporating Fedify 2.1.30 and 2.2.19. Earlier releases on the corresponding Hollo lines are affected. Install the newer 0.8.16 or 0.9.24 release to receive the status deletion fix too.
The other Fedify advisory, GHSA-39gj-rchc-q5m3, concerns Context.routeActivity(): after authenticating a fetched activity, it could queue or forward the caller's unverified copy. Hollo does not call this API, so its supported release lines are not exposed to this path. The dependency fix was nevertheless included in 0.8.14 and 0.9.21. For full technical details on the upstream issues, see the linked advisories and the October 4 Fedify announcement and October 16 Fedify announcement.
The supported Hollo release lines are 0.8.x and 0.9.x under the Hollo security policy. Operators on 0.7.x or earlier should move to a supported line.
For 0.8.x deployments, update to 0.8.16:
docker pull ghcr.io/fedify-dev/hollo:0.8.16For 0.9.x deployments, update to 0.9.24:
docker pull ghcr.io/fedify-dev/hollo:0.9.24After pulling the image, recreate your Hollo container using the new image. With Docker Compose, update the image tag in your Compose file and run docker compose up -d. For source deployments, check out the corresponding release tag, run pnpm install --frozen-lockfile with that tag's pinned pnpm version, run pnpm run build, and restart the server.
If you have a large 0.9.x database and are upgrading from a release before 0.9.20, follow the 0.9.20 index preparation instructions before starting the new version to avoid blocking writes during its automatic migration.
Thanks to Yami Odymel (@yamiodymel) for reporting the status deletion issue to Hollo, to Adel Zaitri (@adelzaitri) for reporting the alternate-document fetch chains to Fedify, and to ChanHaeng Lee (@2chanhaeng) for reporting the inbox activity origin mismatch to Fedify. The activity routing and actor document identity issues were found by the Fedify maintainers with AI assistance.
If anything is unclear, ask below.
github.com
Security researcher & engineer | CISSP | Incoming PhD student in Offensive Cyber Engineering - adelzaitri
多數의 Hollo 保安 脆弱點에 對한 保安 업데이트가 릴리스되었으니, 早速히 업데이트 바랍니다!
https://hollo.social/@hollo/01a1493c-36f9-7992-a6e9-5d10cd3201b7
hollo.social
### Hollo security updates: 0.8.16 and 0.9.24 If you run Hollo, update to [0.8.16] or [0.9.24] now. These releases fix [GHSA-v2qh-w789-xxj6], a missing ownership check in status deletion, and include fixes for three vulnerabilities in Fedify that affect Hollo. They also include a fix for a fourth Fedify vulnerability whose affected API Hollo does not use. For [GHSA-v2qh-w789-xxj6], an authenticated client with the `write:statuses` scope could delete a post belonging to another local account or a cached remote post by its local UUID. The deletion response could also disclose the post's contents, including private content. This required an access token on the receiving Hollo instance. For remote posts, the affected record was Hollo's cached copy. The fix restricts both lookup and deletion to the account associated with the token and returns the existing not-found response for other accounts' posts. It first ships in 0.8.16 and 0.9.24; earlier releases on both supported lines, including 0.9.23, lack this check. For [GHSA-97w4-f4rq-mgqm], Fedify's document loaders followed alternate-document links from HTTP headers or HTML without preserving the redirect limit, visited-URL history, or cancellation signal. An unauthenticated inbox request pointing to an attacker-controlled signing-key URL could trigger an endless chain of outbound requests and DNS lookups, exhausting server resources. Alternate-document links now share the 20-hop limit and loop detection with HTTP redirects, and preserve cancellation. The first fixed Hollo releases were [0.8.13] and [0.9.20], incorporating Fedify 2.1.25 and 2.2.14. Earlier releases on those Hollo lines are affected. For [GHSA-4qhx-hhwf-8685], Fedify authenticated an incoming activity's actor but accepted an activity ID on a different origin. An attacker with an actor and signing key on a server they controlled could supply embedded objects claiming to live on another server. Depending on the application's own checks, those objects could be stored under forged IDs. Sending a forged activity with a genuine activity's ID first could also suppress the genuine delivery as a duplicate. No account on the receiving Hollo instance was required. The fix rejects activities whose IDs have a different origin from their actors before they enter the inbox queue or duplicate cache. For [GHSA-8863-8468-7hq7], Fedify checked whether an actor document listed a signing key, but did not require the document's ID to match the actor ID it requested. An attacker could have activities authenticated as a victim if fetching the victim's exact actor ID led to an actor document whose key the attacker controlled. This depended on the server hosting the victim's actor ID redirecting or serving that document; an arbitrary redirect elsewhere on the server was not enough. The fix requires an exact actor ID match. Hollo's built-in key cache automatically ignores entries stored under the weaker check and fetches and verifies those keys again, so operators do not need to clear it manually. Both of these authentication fixes first reached Hollo in [0.8.15] and [0.9.23], incorporating Fedify 2.1.30 and 2.2.19. Earlier releases on the corresponding Hollo lines are affected. Install the newer 0.8.16 or 0.9.24 release to receive the status deletion fix too. The other Fedify advisory, [GHSA-39gj-rchc-q5m3], concerns `Context.routeActivity()`: after authenticating a fetched activity, it could queue or forward the caller's unverified copy. Hollo does not call this API, so its supported release lines are not exposed to this path. The dependency fix was nevertheless included in [0.8.14] and [0.9.21]. For full technical details on the upstream issues, see the linked advisories and the [October 4 Fedify announcement] and [October 16 Fedify announcement]. The supported Hollo release lines are 0.8.x and 0.9.x under the [Hollo security policy]. Operators on 0.7.x or earlier should move to a supported line. For 0.8.x deployments, update to [0.8.16]: ~~~~ bash docker pull ghcr.io/fedify-dev/hollo:0.8.16 ~~~~ For 0.9.x deployments, update to [0.9.24]: ~~~~ bash docker pull ghcr.io/fedify-dev/hollo:0.9.24 ~~~~ After pulling the image, recreate your Hollo container using the new image. With Docker Compose, update the image tag in your Compose file and run `docker compose up -d`. For source deployments, check out the corresponding release tag, run `pnpm install --frozen-lockfile` with that tag's pinned pnpm version, run `pnpm run build`, and restart the server. If you have a large 0.9.x database and are upgrading from a release before 0.9.20, follow the [0.9.20 index preparation instructions] before starting the new version to avoid blocking writes during its automatic migration. Thanks to Yami Odymel (@yamiodymel@misskey.io) for reporting the status deletion issue to Hollo, to Adel Zaitri ([@adelzaitri]) for reporting the alternate-document fetch chains to Fedify, and to ChanHaeng Lee (@2chanhaeng@hackers.pub) for reporting the inbox activity origin mismatch to Fedify. The activity routing and actor document identity issues were found by the Fedify maintainers with AI assistance. If anything is unclear, ask below. [0.8.16]: https://github.com/fedify-dev/hollo/releases/tag/0.8.16 [0.9.24]: https://github.com/fedify-dev/hollo/releases/tag/0.9.24 [GHSA-v2qh-w789-xxj6]: https://github.com/fedify-dev/hollo/security/advisories/GHSA-v2qh-w789-xxj6 [GHSA-97w4-f4rq-mgqm]: https://github.com/fedify-dev/fedify/security/advisories/GHSA-97w4-f4rq-mgqm [0.8.13]: https://github.com/fedify-dev/hollo/releases/tag/0.8.13 [0.9.20]: https://github.com/fedify-dev/hollo/releases/tag/0.9.20 [GHSA-4qhx-hhwf-8685]: https://github.com/fedify-dev/fedify/security/advisories/GHSA-4qhx-hhwf-8685 [GHSA-8863-8468-7hq7]: https://github.com/fedify-dev/fedify/security/advisories/GHSA-8863-8468-7hq7 [0.8.15]: https://github.com/fedify-dev/hollo/releases/tag/0.8.15 [0.9.23]: https://github.com/fedify-dev/hollo/releases/tag/0.9.23 [GHSA-39gj-rchc-q5m3]: https://github.com/fedify-dev/fedify/security/advisories/GHSA-39gj-rchc-q5m3 [0.8.14]: https://github.com/fedify-dev/hollo/releases/tag/0.8.14 [0.9.21]: https://github.com/fedify-dev/hollo/releases/tag/0.9.21 [October 4 Fedify announcement]: https://github.com/fedify-dev/fedify/discussions/1221 [October 16 Fedify announcement]: https://github.com/fedify-dev/fedify/discussions/1301 [Hollo security policy]: https://github.com/fedify-dev/hollo/blob/main/SECURITY.md [0.9.20 index preparation instructions]: https://github.com/fedify-dev/hollo/blob/0.9.24/CHANGES.md#version-0920 [@adelzaitri]: https://github.com/adelzaitri
If you run Hollo, update to 0.8.16 or 0.9.24 now. These releases fix GHSA-v2qh-w789-xxj6, a missing ownership check in status deletion, and include fixes for three vulnerabilities in Fedify that affect Hollo. They also include a fix for a fourth Fedify vulnerability whose affected API Hollo does not use.
For GHSA-v2qh-w789-xxj6, an authenticated client with the write:statuses scope could delete a post belonging to another local account or a cached remote post by its local UUID. The deletion response could also disclose the post's contents, including private content. This required an access token on the receiving Hollo instance. For remote posts, the affected record was Hollo's cached copy. The fix restricts both lookup and deletion to the account associated with the token and returns the existing not-found response for other accounts' posts. It first ships in 0.8.16 and 0.9.24; earlier releases on both supported lines, including 0.9.23, lack this check.
For GHSA-97w4-f4rq-mgqm, Fedify's document loaders followed alternate-document links from HTTP headers or HTML without preserving the redirect limit, visited-URL history, or cancellation signal. An unauthenticated inbox request pointing to an attacker-controlled signing-key URL could trigger an endless chain of outbound requests and DNS lookups, exhausting server resources. Alternate-document links now share the 20-hop limit and loop detection with HTTP redirects, and preserve cancellation. The first fixed Hollo releases were 0.8.13 and 0.9.20, incorporating Fedify 2.1.25 and 2.2.14. Earlier releases on those Hollo lines are affected.
For GHSA-4qhx-hhwf-8685, Fedify authenticated an incoming activity's actor but accepted an activity ID on a different origin. An attacker with an actor and signing key on a server they controlled could supply embedded objects claiming to live on another server. Depending on the application's own checks, those objects could be stored under forged IDs. Sending a forged activity with a genuine activity's ID first could also suppress the genuine delivery as a duplicate. No account on the receiving Hollo instance was required. The fix rejects activities whose IDs have a different origin from their actors before they enter the inbox queue or duplicate cache.
For GHSA-8863-8468-7hq7, Fedify checked whether an actor document listed a signing key, but did not require the document's ID to match the actor ID it requested. An attacker could have activities authenticated as a victim if fetching the victim's exact actor ID led to an actor document whose key the attacker controlled. This depended on the server hosting the victim's actor ID redirecting or serving that document; an arbitrary redirect elsewhere on the server was not enough. The fix requires an exact actor ID match. Hollo's built-in key cache automatically ignores entries stored under the weaker check and fetches and verifies those keys again, so operators do not need to clear it manually.
Both of these authentication fixes first reached Hollo in 0.8.15 and 0.9.23, incorporating Fedify 2.1.30 and 2.2.19. Earlier releases on the corresponding Hollo lines are affected. Install the newer 0.8.16 or 0.9.24 release to receive the status deletion fix too.
The other Fedify advisory, GHSA-39gj-rchc-q5m3, concerns Context.routeActivity(): after authenticating a fetched activity, it could queue or forward the caller's unverified copy. Hollo does not call this API, so its supported release lines are not exposed to this path. The dependency fix was nevertheless included in 0.8.14 and 0.9.21. For full technical details on the upstream issues, see the linked advisories and the October 4 Fedify announcement and October 16 Fedify announcement.
The supported Hollo release lines are 0.8.x and 0.9.x under the Hollo security policy. Operators on 0.7.x or earlier should move to a supported line.
For 0.8.x deployments, update to 0.8.16:
docker pull ghcr.io/fedify-dev/hollo:0.8.16For 0.9.x deployments, update to 0.9.24:
docker pull ghcr.io/fedify-dev/hollo:0.9.24After pulling the image, recreate your Hollo container using the new image. With Docker Compose, update the image tag in your Compose file and run docker compose up -d. For source deployments, check out the corresponding release tag, run pnpm install --frozen-lockfile with that tag's pinned pnpm version, run pnpm run build, and restart the server.
If you have a large 0.9.x database and are upgrading from a release before 0.9.20, follow the 0.9.20 index preparation instructions before starting the new version to avoid blocking writes during its automatic migration.
Thanks to Yami Odymel (@yamiodymel) for reporting the status deletion issue to Hollo, to Adel Zaitri (@adelzaitri) for reporting the alternate-document fetch chains to Fedify, and to ChanHaeng Lee (@2chanhaeng) for reporting the inbox activity origin mismatch to Fedify. The activity routing and actor document identity issues were found by the Fedify maintainers with AI assistance.
If anything is unclear, ask below.
github.com
Security researcher & engineer | CISSP | Incoming PhD student in Offensive Cyber Engineering - adelzaitri
A security update has been released to address multiple Hollo security vulnerabilities. Please update as soon as possible!
https://hollo.social/@hollo/01a1493c-36f9-7992-a6e9-5d10cd3201b7
hollo.social
### Hollo security updates: 0.8.16 and 0.9.24 If you run Hollo, update to [0.8.16] or [0.9.24] now. These releases fix [GHSA-v2qh-w789-xxj6], a missing ownership check in status deletion, and include fixes for three vulnerabilities in Fedify that affect Hollo. They also include a fix for a fourth Fedify vulnerability whose affected API Hollo does not use. For [GHSA-v2qh-w789-xxj6], an authenticated client with the `write:statuses` scope could delete a post belonging to another local account or a cached remote post by its local UUID. The deletion response could also disclose the post's contents, including private content. This required an access token on the receiving Hollo instance. For remote posts, the affected record was Hollo's cached copy. The fix restricts both lookup and deletion to the account associated with the token and returns the existing not-found response for other accounts' posts. It first ships in 0.8.16 and 0.9.24; earlier releases on both supported lines, including 0.9.23, lack this check. For [GHSA-97w4-f4rq-mgqm], Fedify's document loaders followed alternate-document links from HTTP headers or HTML without preserving the redirect limit, visited-URL history, or cancellation signal. An unauthenticated inbox request pointing to an attacker-controlled signing-key URL could trigger an endless chain of outbound requests and DNS lookups, exhausting server resources. Alternate-document links now share the 20-hop limit and loop detection with HTTP redirects, and preserve cancellation. The first fixed Hollo releases were [0.8.13] and [0.9.20], incorporating Fedify 2.1.25 and 2.2.14. Earlier releases on those Hollo lines are affected. For [GHSA-4qhx-hhwf-8685], Fedify authenticated an incoming activity's actor but accepted an activity ID on a different origin. An attacker with an actor and signing key on a server they controlled could supply embedded objects claiming to live on another server. Depending on the application's own checks, those objects could be stored under forged IDs. Sending a forged activity with a genuine activity's ID first could also suppress the genuine delivery as a duplicate. No account on the receiving Hollo instance was required. The fix rejects activities whose IDs have a different origin from their actors before they enter the inbox queue or duplicate cache. For [GHSA-8863-8468-7hq7], Fedify checked whether an actor document listed a signing key, but did not require the document's ID to match the actor ID it requested. An attacker could have activities authenticated as a victim if fetching the victim's exact actor ID led to an actor document whose key the attacker controlled. This depended on the server hosting the victim's actor ID redirecting or serving that document; an arbitrary redirect elsewhere on the server was not enough. The fix requires an exact actor ID match. Hollo's built-in key cache automatically ignores entries stored under the weaker check and fetches and verifies those keys again, so operators do not need to clear it manually. Both of these authentication fixes first reached Hollo in [0.8.15] and [0.9.23], incorporating Fedify 2.1.30 and 2.2.19. Earlier releases on the corresponding Hollo lines are affected. Install the newer 0.8.16 or 0.9.24 release to receive the status deletion fix too. The other Fedify advisory, [GHSA-39gj-rchc-q5m3], concerns `Context.routeActivity()`: after authenticating a fetched activity, it could queue or forward the caller's unverified copy. Hollo does not call this API, so its supported release lines are not exposed to this path. The dependency fix was nevertheless included in [0.8.14] and [0.9.21]. For full technical details on the upstream issues, see the linked advisories and the [October 4 Fedify announcement] and [October 16 Fedify announcement]. The supported Hollo release lines are 0.8.x and 0.9.x under the [Hollo security policy]. Operators on 0.7.x or earlier should move to a supported line. For 0.8.x deployments, update to [0.8.16]: ~~~~ bash docker pull ghcr.io/fedify-dev/hollo:0.8.16 ~~~~ For 0.9.x deployments, update to [0.9.24]: ~~~~ bash docker pull ghcr.io/fedify-dev/hollo:0.9.24 ~~~~ After pulling the image, recreate your Hollo container using the new image. With Docker Compose, update the image tag in your Compose file and run `docker compose up -d`. For source deployments, check out the corresponding release tag, run `pnpm install --frozen-lockfile` with that tag's pinned pnpm version, run `pnpm run build`, and restart the server. If you have a large 0.9.x database and are upgrading from a release before 0.9.20, follow the [0.9.20 index preparation instructions] before starting the new version to avoid blocking writes during its automatic migration. Thanks to Yami Odymel (@yamiodymel@misskey.io) for reporting the status deletion issue to Hollo, to Adel Zaitri ([@adelzaitri]) for reporting the alternate-document fetch chains to Fedify, and to ChanHaeng Lee (@2chanhaeng@hackers.pub) for reporting the inbox activity origin mismatch to Fedify. The activity routing and actor document identity issues were found by the Fedify maintainers with AI assistance. If anything is unclear, ask below. [0.8.16]: https://github.com/fedify-dev/hollo/releases/tag/0.8.16 [0.9.24]: https://github.com/fedify-dev/hollo/releases/tag/0.9.24 [GHSA-v2qh-w789-xxj6]: https://github.com/fedify-dev/hollo/security/advisories/GHSA-v2qh-w789-xxj6 [GHSA-97w4-f4rq-mgqm]: https://github.com/fedify-dev/fedify/security/advisories/GHSA-97w4-f4rq-mgqm [0.8.13]: https://github.com/fedify-dev/hollo/releases/tag/0.8.13 [0.9.20]: https://github.com/fedify-dev/hollo/releases/tag/0.9.20 [GHSA-4qhx-hhwf-8685]: https://github.com/fedify-dev/fedify/security/advisories/GHSA-4qhx-hhwf-8685 [GHSA-8863-8468-7hq7]: https://github.com/fedify-dev/fedify/security/advisories/GHSA-8863-8468-7hq7 [0.8.15]: https://github.com/fedify-dev/hollo/releases/tag/0.8.15 [0.9.23]: https://github.com/fedify-dev/hollo/releases/tag/0.9.23 [GHSA-39gj-rchc-q5m3]: https://github.com/fedify-dev/fedify/security/advisories/GHSA-39gj-rchc-q5m3 [0.8.14]: https://github.com/fedify-dev/hollo/releases/tag/0.8.14 [0.9.21]: https://github.com/fedify-dev/hollo/releases/tag/0.9.21 [October 4 Fedify announcement]: https://github.com/fedify-dev/fedify/discussions/1221 [October 16 Fedify announcement]: https://github.com/fedify-dev/fedify/discussions/1301 [Hollo security policy]: https://github.com/fedify-dev/hollo/blob/main/SECURITY.md [0.9.20 index preparation instructions]: https://github.com/fedify-dev/hollo/blob/0.9.24/CHANGES.md#version-0920 [@adelzaitri]: https://github.com/adelzaitri
If you run Hollo, update to 0.8.16 or 0.9.24 now. These releases fix GHSA-v2qh-w789-xxj6, a missing ownership check in status deletion, and include fixes for three vulnerabilities in Fedify that affect Hollo. They also include a fix for a fourth Fedify vulnerability whose affected API Hollo does not use.
For GHSA-v2qh-w789-xxj6, an authenticated client with the write:statuses scope could delete a post belonging to another local account or a cached remote post by its local UUID. The deletion response could also disclose the post's contents, including private content. This required an access token on the receiving Hollo instance. For remote posts, the affected record was Hollo's cached copy. The fix restricts both lookup and deletion to the account associated with the token and returns the existing not-found response for other accounts' posts. It first ships in 0.8.16 and 0.9.24; earlier releases on both supported lines, including 0.9.23, lack this check.
For GHSA-97w4-f4rq-mgqm, Fedify's document loaders followed alternate-document links from HTTP headers or HTML without preserving the redirect limit, visited-URL history, or cancellation signal. An unauthenticated inbox request pointing to an attacker-controlled signing-key URL could trigger an endless chain of outbound requests and DNS lookups, exhausting server resources. Alternate-document links now share the 20-hop limit and loop detection with HTTP redirects, and preserve cancellation. The first fixed Hollo releases were 0.8.13 and 0.9.20, incorporating Fedify 2.1.25 and 2.2.14. Earlier releases on those Hollo lines are affected.
For GHSA-4qhx-hhwf-8685, Fedify authenticated an incoming activity's actor but accepted an activity ID on a different origin. An attacker with an actor and signing key on a server they controlled could supply embedded objects claiming to live on another server. Depending on the application's own checks, those objects could be stored under forged IDs. Sending a forged activity with a genuine activity's ID first could also suppress the genuine delivery as a duplicate. No account on the receiving Hollo instance was required. The fix rejects activities whose IDs have a different origin from their actors before they enter the inbox queue or duplicate cache.
For GHSA-8863-8468-7hq7, Fedify checked whether an actor document listed a signing key, but did not require the document's ID to match the actor ID it requested. An attacker could have activities authenticated as a victim if fetching the victim's exact actor ID led to an actor document whose key the attacker controlled. This depended on the server hosting the victim's actor ID redirecting or serving that document; an arbitrary redirect elsewhere on the server was not enough. The fix requires an exact actor ID match. Hollo's built-in key cache automatically ignores entries stored under the weaker check and fetches and verifies those keys again, so operators do not need to clear it manually.
Both of these authentication fixes first reached Hollo in 0.8.15 and 0.9.23, incorporating Fedify 2.1.30 and 2.2.19. Earlier releases on the corresponding Hollo lines are affected. Install the newer 0.8.16 or 0.9.24 release to receive the status deletion fix too.
The other Fedify advisory, GHSA-39gj-rchc-q5m3, concerns Context.routeActivity(): after authenticating a fetched activity, it could queue or forward the caller's unverified copy. Hollo does not call this API, so its supported release lines are not exposed to this path. The dependency fix was nevertheless included in 0.8.14 and 0.9.21. For full technical details on the upstream issues, see the linked advisories and the October 4 Fedify announcement and October 16 Fedify announcement.
The supported Hollo release lines are 0.8.x and 0.9.x under the Hollo security policy. Operators on 0.7.x or earlier should move to a supported line.
For 0.8.x deployments, update to 0.8.16:
docker pull ghcr.io/fedify-dev/hollo:0.8.16For 0.9.x deployments, update to 0.9.24:
docker pull ghcr.io/fedify-dev/hollo:0.9.24After pulling the image, recreate your Hollo container using the new image. With Docker Compose, update the image tag in your Compose file and run docker compose up -d. For source deployments, check out the corresponding release tag, run pnpm install --frozen-lockfile with that tag's pinned pnpm version, run pnpm run build, and restart the server.
If you have a large 0.9.x database and are upgrading from a release before 0.9.20, follow the 0.9.20 index preparation instructions before starting the new version to avoid blocking writes during its automatic migration.
Thanks to Yami Odymel (@yamiodymel) for reporting the status deletion issue to Hollo, to Adel Zaitri (@adelzaitri) for reporting the alternate-document fetch chains to Fedify, and to ChanHaeng Lee (@2chanhaeng) for reporting the inbox activity origin mismatch to Fedify. The activity routing and actor document identity issues were found by the Fedify maintainers with AI assistance.
If anything is unclear, ask below.
github.com
Security researcher & engineer | CISSP | Incoming PhD student in Offensive Cyber Engineering - adelzaitri
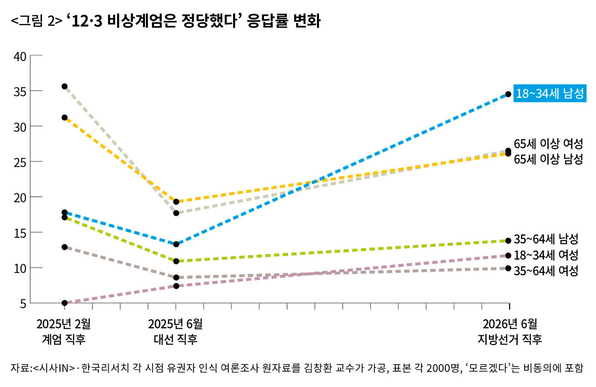
"거의 모든 계엄, 탄핵 관련 지표에서 청년 남성은 가장 친계엄적이고, 민주주의 질서에 가장 비우호적인 태도로 변화하였다. 우리 논문에서는 민주주의에 대한 태도에서 청년 남성과 86세대를 포함한 장년 남성 사이에 차이가 없다고 했었는데, 이제는 차이가 벌어졌고, 청년 남성은 노년 남성과 차이가 없거나 오히려 더 반민주주의적이다." https://sovidence.tistory.com/1332

‘12·3 비상계엄은 정당했다’는 응답률의 변화를 성별과 연령대별로 비교한 선그래프. 조사 시점은 2025년 2월 계엄 직후, 2025년 6월 대선 직후, 2026년 6월 지방선거 직후다. 가장 큰 변화는 18~34세 남성에서 나타난다. 이 집단의 응답률은 2025년 2월 약 18%에서 6월 약 13%로 낮아졌다가, 2026년 6월 약 35%로 크게 상승해 모든 집단 중 가장 높다. 65세 이상 여성은 약 36%, 18%, 27%, 65세 이상 남성은 약 31%, 19%, 26%로 두 집단 모두 2025년 6월에 크게 하락한 뒤 다시 상승한다. 35~64세 남성은 약 17%, 11%, 14%, 18~34세 여성은 약 5%, 7%, 12%, 35~64세 여성은 약 13%, 9%, 10%다. 전반적으로 2025년 6월에는 대부분 집단의 응답률이 낮아졌고, 2026년 6월에는 다시 상승했으며 특히 18~34세 남성의 상승이 두드러진다.
@Yoxem Yes, I think it's probably because, during the Japanese colonial period, Japanese kyūjitai (舊字體) forms influenced the standard forms of hanja adopted in Korea after liberation. 🤔
韓國과 日本에서는 漢字 【낳을 산】을 普通 「産」으로 적는 反面, 臺灣이나 香港 等 이른바 繁體字圈서는 「產」을 標準 字形으로 삼는다. 個人的으로는 윗 部分이 文이므로 「產」으로 적는 것을 選好하긴 한다.
If you use BotKit, update to a patched release now. This update addresses two vulnerabilities: GHSA-4qhx-hhwf-8685, an inbox origin validation flaw that could let an attacker supply forged objects or suppress genuine activities, and GHSA-8863-8468-7hq7, a key ownership validation flaw that could authenticate activities as the wrong actor under specific actor-document configurations. Both flaws originate in Fedify, which BotKit uses for federation.
GHSA-4qhx-hhwf-8685 affects incoming activities. Fedify authenticated the activity's actor but did not require the activity's id to share that actor's origin. An attacker needed only an actor and its signing key on a server they controlled, with no account on the receiving server or interaction from the victim.
By choosing an activity ID on another server's origin, the attacker could make Create.getObject() and other accessors return embedded objects claiming to live on that server without fetching them from it. BotKit checks that a message's attribution matches the activity's actor, but that does not stop an attacker from attributing an object to themselves while giving it an ID on another server. Its handlers could therefore receive forged objects under that server's object IDs. The same flaw also let an attacker who knew or could predict a genuine activity's ID reserve its idempotency cache entry by sending a forged activity with that ID first. The genuine delivery then received 202 Accepted but did not reach the inbox listeners for one day. With a message queue, this suppression applied across all inboxes on the receiving server.
The fix rejects non-portable activities whose IDs have a different origin from their actors before they reach inbox listeners, the queue, or the idempotency cache. The same origin check runs when processing activities from the queue or routing them manually.
GHSA-8863-8468-7hq7 affects Fedify's checks that a signing key belongs to an actor. Fedify fetched the actor's document and checked that it listed the key, but did not require the document's id to match the actor ID it requested. An attacker could have activities authenticated as a victim if dereferencing the victim's exact actor ID led to an actor document whose key the attacker controlled. This could happen through a redirect or alternate-document link, including to another origin, or when the victim's server directly served another same-origin actor's document.
The attacker cannot normally arrange this condition: it depends on the server hosting the victim's actor ID. A redirect from some other URL on that server is not enough. HTTP Signatures, Linked Data Signatures, and Object Integrity Proofs use the affected ownership checks.
The fix requires the fetched actor document's id to exactly match the requested actor ID. Fedify also retains its check that the document's id shares the origin of the final fetched URL. An actor whose ID redirects to a document with a different id can no longer have its keys confirmed through that redirect, even on the same origin and for the same account. Fedify's built-in key cache automatically ignores entries created under the weaker check and fetches and verifies those keys again. If your application separately supplies a custom KeyCache implementation to Fedify, clear it once when upgrading so previously cached false ownership claims are not retained.
BotKit 0.4.x versions through 0.4.9 and BotKit 0.5.x versions through 0.5.6 include Fedify versions affected by both vulnerabilities. The first patched releases, and the current recommended releases, are BotKit 0.4.10 and 0.5.7. BotKit 0.4.10 requires Fedify ~2.1.30, and BotKit 0.5.7 requires Fedify ~2.3.14. These are the two supported BotKit lines; users on older lines should move to a supported release.
For BotKit 0.5.x, install @fedify/botkit 0.5.7 using the command for your package manager:
npm install @fedify/botkit@0.5.7
yarn add @fedify/botkit@0.5.7
pnpm add @fedify/botkit@0.5.7
bun add @fedify/botkit@0.5.7
deno add jsr:@fedify/botkit@0.5.7
For BotKit 0.4.x, install @fedify/botkit 0.4.10:
npm install @fedify/botkit@0.4.10
yarn add @fedify/botkit@0.4.10
pnpm add @fedify/botkit@0.4.10
bun add @fedify/botkit@0.4.10
deno add jsr:@fedify/botkit@0.4.10
Check the installed or locked versions: @fedify/botkit should be 0.4.10 or 0.5.7, with @fedify/fedify at least 2.1.30 on the 2.1.x line or 2.3.14 on the 2.3.x line. If you use a routine update command instead, check that your declared dependency range allows the patched release and change it explicitly if needed. After updating, redeploy.
The full GitHub Security Advisories are GHSA-4qhx-hhwf-8685 and GHSA-8863-8468-7hq7. See also Fedify's own announcement.
Thanks to @2chanhaeng for reporting the inbox origin validation flaw to the Fedify project. The actor document identity mismatch was found by the Fedify maintainers with AI assistance.
If anything is unclear, feel free to ask on GitHub Discussions or Matrix.
matrix.to
You're invited to talk on Matrix
Fedifyの2件のセキュリティ脆弱性に対するセキュリティアップデートがリリースされました。早急にアップデートしてください!
Fedify 保安 脆弱點 2件에 對한 保安 업데이트가 릴리스되었으니, 早速히 업데이트 바랍니다!
Furifont: furigana built into the font via @hongminhee https://lobste.rs/s/ixoasm #design
https://furifont.antfu.me/
furifont.antfu.me
A Japanese font that shows furigana by itself.
A security update addressing two vulnerabilities in Fedify has been released. Please update as soon as possible!
hackers.pub
Critical security vulnerabilities have been patched in the `@fedify/fedify` package, addressing flaws in inbox origin validation and actor key ownership verification. The first vulnerability, GHSA-4qhx-hhwf-8685, allowed attackers to provide forged embedded objects or suppress genuine activities through idempotency cache abuse due to missing origin checks between activity IDs and their actors. The second vulnerability, GHSA-8863-8468-7hq7, allowed improper authentication under specific actor document redirect or alternate-document configurations when dereferencing keys. Fixes have rolled out across versions 2.0.34, 2.1.30, 2.2.19, 2.3.14, and 2.4.4, enforcing strict origin matching and document ID equality while automatically invalidating affected built-in cache entries. Upgrading immediately and clearing any custom key caches is essential to protecting Fedify-powered federated applications from activity suppression and identity spoofing.
If you use an affected Fedify release, update now. Two vulnerabilities have been fixed in @fedify/fedify: GHSA-4qhx-hhwf-8685, an inbox origin validation flaw that could let an attacker supply forged objects or suppress genuine activities, and GHSA-8863-8468-7hq7, a flaw in the key ownership check that could authenticate activities as the wrong actor under specific actor-document configurations.
The releases containing both fixes are 2.0.34, 2.1.30, 2.2.19, 2.3.14, and 2.4.4. We recommend 2.4.4, or 2.3.14 if you are staying on the 2.3 line. Under the security policy, Fedify supports the latest two minor lines, currently 2.4 and 2.3. Backported fixes are also available in the releases listed above for 2.0, 2.1, and 2.2, but users on those older lines should plan to move to a supported line. Users on affected 1.x releases need to change their dependency to a supported 2.x release.
GHSA-4qhx-hhwf-8685 affects applications receiving activities through Fedify's inbox listeners. The inbox authenticated an activity's actor but accepted an activity id on an origin different from the actor's. An attacker needed only an actor and its signing key on a server they controlled, with no account on the receiving server or interaction from the victim.
Since version 1.9.0, Fedify's property accessors have trusted embedded objects whose IDs share the activity's origin. By choosing an activity ID on a victim server's origin, an attacker could make Create.getObject() and other accessors return forged objects claiming to live on that server without fetching them from it. Depending on the application's attribution and authorization checks, this could cause it to store or display forged content under another server's object ID.
The same missing check also let an attacker reserve a genuine activity's idempotency cache entry by submitting a forged activity with its ID first. The genuine delivery then received 202 Accepted but did not reach the listeners for one day. When a message queue was configured, the suppression applied across all inboxes on the receiving server. This behavior was confirmed in 1.8.15 and subsequent releases before the fixes; releases before 1.8 were not tested.
The first fixes shipped in 2.0.33, 2.1.29, 2.2.18, 2.3.13, and 2.4.3. Earlier releases on each of those 2.x lines are affected. Update to the newer releases recommended above to receive both fixes. The inbox now returns 401 Unauthorized for non-portable activities whose IDs have a different origin from their actors, before they reach listeners, the queue, or the idempotency cache. The same origin check applies to queued and manually routed activities. Setting skipSignatureVerification bypasses this protection along with signature verification.
GHSA-8863-8468-7hq7 lists the affected version range as <= 2.4.3, with fixes in 2.0.34, 2.1.30, 2.2.19, 2.3.14, and 2.4.4 on their respective release lines. When confirming that a key belongs to an actor, Fedify fetched the actor's document and checked that it listed the key, but did not require the document's id to match the actor ID it requested.
An attacker could have activities authenticated as a victim if dereferencing the victim's exact actor ID led to an actor document whose key the attacker controlled. This could happen through a redirect or alternate-document link to the attacker's document, including on another origin, or when the victim's server directly served a different same-origin actor's document. The attacker cannot normally arrange this: it depends on the server hosting the victim's actor ID. A redirect from some other URL on that server is not enough. No account on the receiving Fedify server is required.
HTTP Signatures, Linked Data Signatures, and Object Integrity Proofs use the affected ownership checks. The fix requires the fetched actor document's id to exactly match the requested actor ID, in addition to the existing origin check. An actor whose ID redirects to a document with a different id can no longer have its keys confirmed through that redirect, even on the same origin and for the same account. Servers that normalize actor URLs should use the canonical actor ID as their keys' owner or controller and their activities' actor.
The built-in KvStore-backed key cache automatically ignores entries created under the weaker check and fetches and verifies those keys again. If you supply a custom KeyCache implementation, clear it once when upgrading. Otherwise, previously cached false ownership claims can remain trusted after the upgrade. Downgrading to an earlier release is not safe.
Update @fedify/fedify using the command for your package manager:
npm update @fedify/fedify
yarn upgrade @fedify/fedify
pnpm update @fedify/fedify
bun update @fedify/fedify
deno update @fedify/fedify
Check the installed or locked version: it should be 2.0.34, 2.1.30, 2.2.19, 2.3.14, or 2.4.4 on the corresponding line. Update commands can stay within your declared dependency range. If that range excludes the recommended release, change it explicitly. For example, to move to 2.4.4:
npm install @fedify/fedify@2.4.4
yarn add @fedify/fedify@2.4.4
pnpm add @fedify/fedify@2.4.4
bun add @fedify/fedify@2.4.4
deno add jsr:@fedify/fedify@2.4.4
Clear any custom key cache as described above, then redeploy. If you run other Fedify-based servers, update those too.
The full GitHub Security Advisories are GHSA-4qhx-hhwf-8685 and GHSA-8863-8468-7hq7.
Thanks to @2chanhaeng for reporting the inbox activity origin mismatch. The actor document identity mismatch was found by the Fedify maintainers with AI assistance.
If anything is unclear, ask below.
github.com
### Summary The fix for GHSA-q9f8-5hc7-898f made Fedify confirm a key's claimed owner by fetching the owner's actor document and checking that it lists the key. That check accepts whatever actor ...
We've released DrFed 0.1.0, the first version of the ActivityPub development and debugging tool I'm building with the team.
It's still an MVP: you can create test instances and actors, and inspect incoming activities. I wouldn't call it a particularly useful debugger yet. We wanted to share what we've built so far and let people know that development is continuing.
We're working toward a tool that helps when your ActivityPub app won't federate with another server. Thanks to my teammates for getting us to this first release. I hope you'll follow along.
hackers.pub
DrFed 0.1.0 marks the initial MVP release of a web-based platform designed for developing and debugging ActivityPub implementations. Built by the Fedify team with support from NLnet and the NGI0 Commons Fund, this early version allows developers to run local test environments, generate actors, store ActivityPub objects, and inspect incoming JSON-LD deliveries through an activity log. Distributed via npm for Node.js environments, the suite provides four core CLI utilities with embedded PGlite support for quick local setups as well as PostgreSQL compatibility for broader deployments. While advanced debugging utilities like signature validators and automated remote activity dispatching remain in development, this release establishes a functional testing foundation for federation developers to explore and provide early feedback.
DrFed is a web-based platform for developing and debugging ActivityPub implementations, built by the team behind Fedify.
Today we are releasing DrFed 0.1.0, our first release. It is an MVP: you can run DrFed locally, create test instances and actors, store test objects, and inspect incoming activity deliveries in the web UI.
To be honest, DrFed is not yet especially useful as an ActivityPub debugger. Much of the tooling we have planned is still ahead of us. We are releasing this version to make our progress visible and give you something you can install and try while development continues.
DrFed 0.1.0 is available on npm as @drfed/drfed. You need Node.js 26 or newer. Install the package globally to make its four commands available on your PATH:
npm install --global @drfed/drfed@0.1.0
Create an account before starting the server, using the same data directory for both commands:
drfed-account create --data-path .pgdata \
--email alice@example.com --name Alice
drfed-server --root-origin http://drfed.localhost:8888 \
--data-path .pgdata --mail-log-content
Replace the email address and display name with your own. This example uses PGlite, so you do not need a separate database server. Account creation prepares the database, and the server applies pending migrations on startup. PGlite allows only one process to own its data directory, which is why account creation comes first.
Open http://drfed.localhost:8888, choose Sign in, and enter the email address you used above. The local example prints a login link in the terminal; follow it to sign in. The default mail transport does not deliver email, and --mail-log-content explicitly enables printing message contents for local testing. For a service deployment, configure SMTP or another supported mail transport instead.
The installation guide also covers installing into a local directory and running the commands with npx.
After signing in, open Workspace and choose New instance. DrFed generates an identifier for the instance and gives it a subdomain of your configured root origin. Each instance runs as an ActivityPub server, with its own actors and inbox.
For example, with a root origin of https://drfed.example.com, an instance named example would live at https://example.drfed.example.com. The instance page lists its NodeInfo, WebFinger, and shared inbox endpoints, with copy buttons for using those URLs in your own tests.
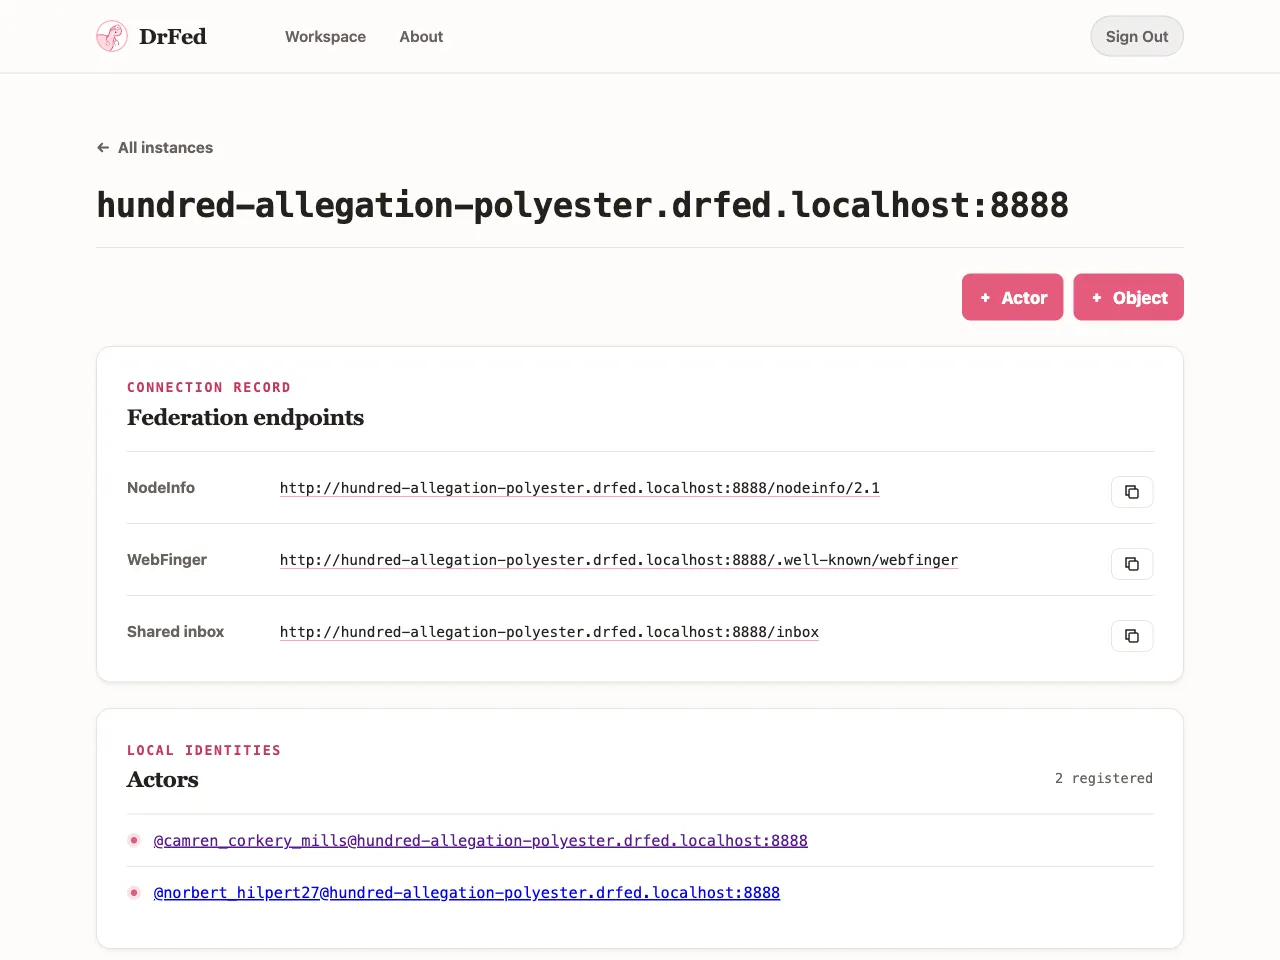
The local setup above is useful for exploring the UI and making requests from your own machine. To receive requests from other servers, you need a publicly reachable deployment with wildcard DNS and HTTPS for the instance subdomains. A reverse proxy must preserve the original Host header. See the server README for the deployment details.
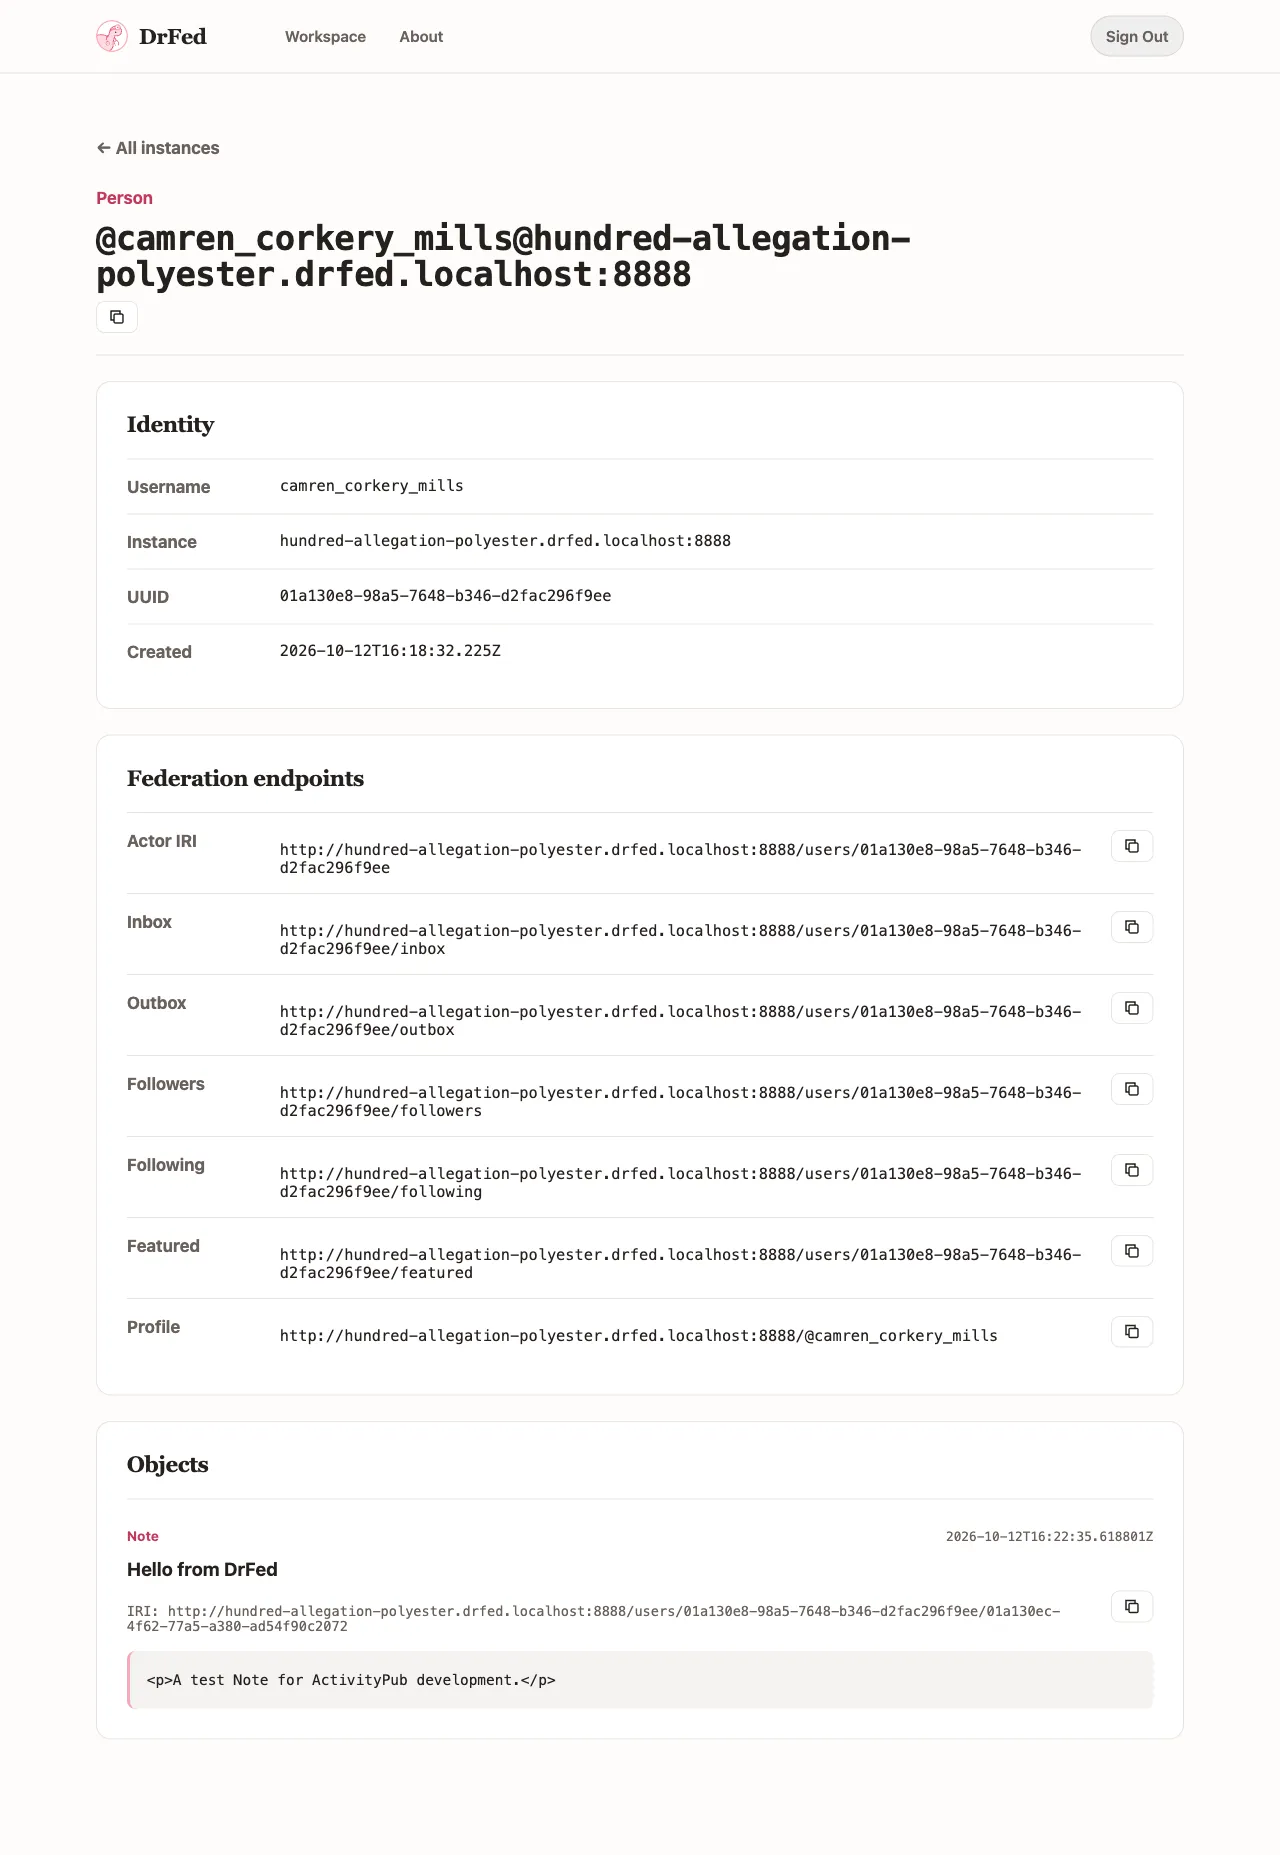
On an instance page, choose Actor and enter how many actors to generate. DrFed creates test identities with generated usernames. An actor's detail page shows its handle, identity, and federation endpoints, including its inbox and outbox. You can copy these addresses into requests from the ActivityPub application you are developing.
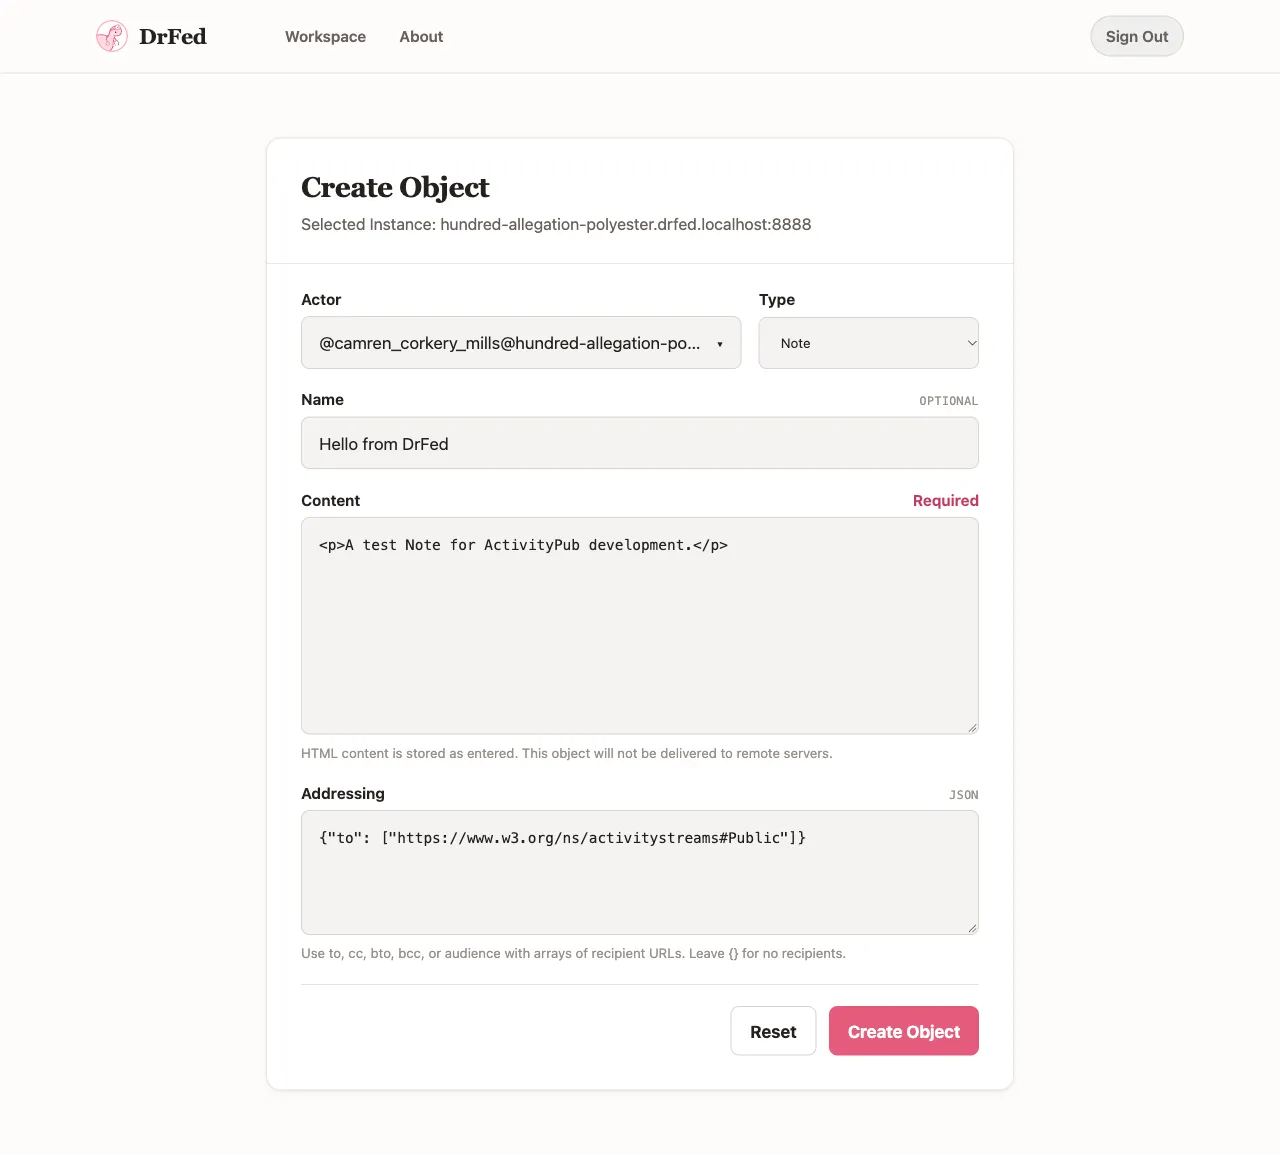
Choose Object on the instance page to create a Note or Article attributed to one of its actors. The form accepts an optional name, HTML content, and explicit ActivityPub addressing as JSON. For example, this addresses an object to Public:
{"to": ["https://www.w3.org/ns/activitystreams#Public"]}
The actor page lists its stored objects and shows their HTML as source text. Publicly addressed local objects and their Create activities are also available through ActivityPub, including the actor's outbox. Creating an object does not deliver it to remote servers. This is a way to prepare content for another implementation to fetch, rather than a general activity-sending tool.
When your application sends an activity to a DrFed instance's inbox, the instance's Activity log records the delivery. Each entry shows the activity type, status, sender and destination, and time. Expand an entry to inspect and copy the recorded JSON-LD; scroll up to load older entries.
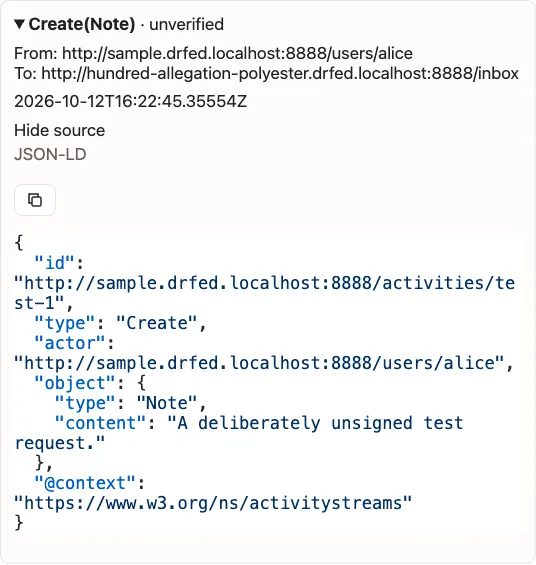
This screenshot shows a deliberately unsigned test request. The inbox refused it with HTTP 401, and the log records it as unverified. Seeing a request in the log does not mean DrFed authenticated its sender or accepted its activity.
DrFed also stores eligible authenticated incoming Create activities containing Note or Article objects. Other activity types can be recorded without becoming stored objects. Delivery contents are restricted to instance members and administrators. The current UI lets you inspect recorded history; it does not yet provide live updates, search, or filters.
The npm package includes the commands needed to run and maintain a deployment:
| Command | Purpose |
|---|---|
drfed-server |
Run the backend and embedded web frontend, together by default. |
drfed-account create |
Create a local account before signing in. |
drfed-migrate |
Apply database migrations, or inspect migration history with --check. |
drfed-web |
Run the frontend separately against a DrFed backend. |
PGlite stores data in a local directory. You can instead select PostgreSQL with --postgres-url or its alias --database-url. Stop a PGlite server before using the account or migration commands against its data directory. To prepare and then check that database without starting the server:
drfed-migrate --data-path .pgdata
drfed-migrate --data-path .pgdata --check
All four commands accept an explicit TOML configuration file through --config, as well as the relevant DRFED_* environment variables. CLI options take precedence over environment variables, then TOML, then defaults. --print-config shows the effective settings and their sources with secrets redacted. See the configuration guide and CLI reference for the options, mail transports, and separate frontend setup.
Shell completions are available for Bash, zsh, fish, PowerShell, and Nushell. For example:
drfed-server completion bash > drfed-server-completion.bash
source ./drfed-server-completion.bash
Replace drfed-server with another command to generate its completion script. Installation does not activate completions automatically; the completion installation instructions explain persistent setup for each shell.
This release has rough edges. Directly opening an instance detail page can terminate the installed server with a Seroval serialization error. We found this while preparing these notes and are tracking it in #132.
The broader debugging tools described in our project overview, such as a step-by-step signature debugger, JSON-LD comparison tools, and WebFinger/NodeInfo validators, are goals for the project. They are not available as dedicated tools in this release. The object creation form also does not yet send activities to arbitrary remote inboxes.
Our documentation is still incomplete and not yet organized into a systematic user guide. Some overview text describes the platform we intend to build, so it should not be read as a list of completed 0.1.0 features. For now, start with README.md, the CLI package README, and the installation and configuration pages under docs/.
In the next version, we will publish a Docker image alongside the npm packages, making it easier to run DrFed without setting up Node.js yourself.
Thank you to the four people on the DrFed development team who have brought us to this first release, listed alphabetically:
We also thank NLnet and the NGI0 Commons Fund for funding DrFed's development. Their support gives us time to build this free software tool for ActivityPub developers. You can read more on NLnet's DrFed project page.
We will keep working to make DrFed more useful for investigating federation failures. We hope you will follow the next stages of its development. Release history is kept in CHANGES.md.
github.com
Web-based platform for developing and debugging ActivityPub implementations - fedify-dev/drfed
DrFed is a web-based platform for developing and debugging ActivityPub implementations, built by the team behind Fedify.
Today we are releasing DrFed 0.1.0, our first release. It is an MVP: you can run DrFed locally, create test instances and actors, store test objects, and inspect incoming activity deliveries in the web UI.
To be honest, DrFed is not yet especially useful as an ActivityPub debugger. Much of the tooling we have planned is still ahead of us. We are releasing this version to make our progress visible and give you something you can install and try while development continues.
DrFed 0.1.0 is available on npm as @drfed/drfed. You need Node.js 26 or newer. Install the package globally to make its four commands available on your PATH:
npm install --global @drfed/drfed@0.1.0
Create an account before starting the server, using the same data directory for both commands:
drfed-account create --data-path .pgdata \
--email alice@example.com --name Alice
drfed-server --root-origin http://drfed.localhost:8888 \
--data-path .pgdata --mail-log-content
Replace the email address and display name with your own. This example uses PGlite, so you do not need a separate database server. Account creation prepares the database, and the server applies pending migrations on startup. PGlite allows only one process to own its data directory, which is why account creation comes first.
Open http://drfed.localhost:8888, choose Sign in, and enter the email address you used above. The local example prints a login link in the terminal; follow it to sign in. The default mail transport does not deliver email, and --mail-log-content explicitly enables printing message contents for local testing. For a service deployment, configure SMTP or another supported mail transport instead.
The installation guide also covers installing into a local directory and running the commands with npx.
After signing in, open Workspace and choose New instance. DrFed generates an identifier for the instance and gives it a subdomain of your configured root origin. Each instance runs as an ActivityPub server, with its own actors and inbox.
For example, with a root origin of https://drfed.example.com, an instance named example would live at https://example.drfed.example.com. The instance page lists its NodeInfo, WebFinger, and shared inbox endpoints, with copy buttons for using those URLs in your own tests.

The local setup above is useful for exploring the UI and making requests from your own machine. To receive requests from other servers, you need a publicly reachable deployment with wildcard DNS and HTTPS for the instance subdomains. A reverse proxy must preserve the original Host header. See the server README for the deployment details.
On an instance page, choose Actor and enter how many actors to generate. DrFed creates test identities with generated usernames. An actor's detail page shows its handle, identity, and federation endpoints, including its inbox and outbox. You can copy these addresses into requests from the ActivityPub application you are developing.

Choose Object on the instance page to create a Note or Article attributed to one of its actors. The form accepts an optional name, HTML content, and explicit ActivityPub addressing as JSON. For example, this addresses an object to Public:
{"to": ["https://www.w3.org/ns/activitystreams#Public"]}

The actor page lists its stored objects and shows their HTML as source text. Publicly addressed local objects and their Create activities are also available through ActivityPub, including the actor's outbox. Creating an object does not deliver it to remote servers. This is a way to prepare content for another implementation to fetch, rather than a general activity-sending tool.
When your application sends an activity to a DrFed instance's inbox, the instance's Activity log records the delivery. Each entry shows the activity type, status, sender and destination, and time. Expand an entry to inspect and copy the recorded JSON-LD; scroll up to load older entries.

This screenshot shows a deliberately unsigned test request. The inbox refused it with HTTP 401, and the log records it as unverified. Seeing a request in the log does not mean DrFed authenticated its sender or accepted its activity.
DrFed also stores eligible authenticated incoming Create activities containing Note or Article objects. Other activity types can be recorded without becoming stored objects. Delivery contents are restricted to instance members and administrators. The current UI lets you inspect recorded history; it does not yet provide live updates, search, or filters.
The npm package includes the commands needed to run and maintain a deployment:
| Command | Purpose |
|---|---|
drfed-server |
Run the backend and embedded web frontend, together by default. |
drfed-account create |
Create a local account before signing in. |
drfed-migrate |
Apply database migrations, or inspect migration history with --check. |
drfed-web |
Run the frontend separately against a DrFed backend. |
PGlite stores data in a local directory. You can instead select PostgreSQL with --postgres-url or its alias --database-url. Stop a PGlite server before using the account or migration commands against its data directory. To prepare and then check that database without starting the server:
drfed-migrate --data-path .pgdata
drfed-migrate --data-path .pgdata --check
All four commands accept an explicit TOML configuration file through --config, as well as the relevant DRFED_* environment variables. CLI options take precedence over environment variables, then TOML, then defaults. --print-config shows the effective settings and their sources with secrets redacted. See the configuration guide and CLI reference for the options, mail transports, and separate frontend setup.
Shell completions are available for Bash, zsh, fish, PowerShell, and Nushell. For example:
drfed-server completion bash > drfed-server-completion.bash
source ./drfed-server-completion.bash
Replace drfed-server with another command to generate its completion script. Installation does not activate completions automatically; the completion installation instructions explain persistent setup for each shell.
This release has rough edges. Directly opening an instance detail page can terminate the installed server with a Seroval serialization error. We found this while preparing these notes and are tracking it in #132.
The broader debugging tools described in our project overview, such as a step-by-step signature debugger, JSON-LD comparison tools, and WebFinger/NodeInfo validators, are goals for the project. They are not available as dedicated tools in this release. The object creation form also does not yet send activities to arbitrary remote inboxes.
Our documentation is still incomplete and not yet organized into a systematic user guide. Some overview text describes the platform we intend to build, so it should not be read as a list of completed 0.1.0 features. For now, start with README.md, the CLI package README, and the installation and configuration pages under docs/.
In the next version, we will publish a Docker image alongside the npm packages, making it easier to run DrFed without setting up Node.js yourself.
Thank you to the four people on the DrFed development team who have brought us to this first release, listed alphabetically:
We also thank NLnet and the NGI0 Commons Fund for funding DrFed's development. Their support gives us time to build this free software tool for ActivityPub developers. You can read more on NLnet's DrFed project page.
We will keep working to make DrFed more useful for investigating federation failures. We hope you will follow the next stages of its development. Release history is kept in CHANGES.md.
github.com
Web-based platform for developing and debugging ActivityPub implementations - fedify-dev/drfed
In the end, @hongminhee was right. Deno lost its identity long ago.
https://hackers.pub/@hongminhee/2026/i-wish-deno-would-keep-doing-what-it-does-best
hackers.pub
Deno emerged as a solution to the overwhelming configuration requirements of the modern TypeScript ecosystem by offering a zero-config, single-binary experience. By integrating essential tools for formatting, linting, and testing alongside web-standard APIs, it removed the tedious setup rituals that often deterred developers. Recently, however, Deno has pivoted toward deep Node.js compatibility, supporting npm packages and traditional module structures to accelerate adoption. This shift creates a strategic risk where high compatibility might inadvertently discourage developers from targeting Deno’s unique APIs, especially as Node.js adopts Deno’s innovations like native TypeScript support and permission models. Commercial pressures may be forcing a prioritization of rapid growth and compatibility over the patient development of a truly self-sufficient, vertically integrated toolchain. While Deno remains a powerful choice, its convergence with the legacy ecosystem suggests a move away from the radical simplicity that originally defined its mission. The ongoing convergence of runtimes serves as a vital reminder of the trade-offs between technical purity and the demands of commercial viability.
This quote was not authorized by the quoted post's author.
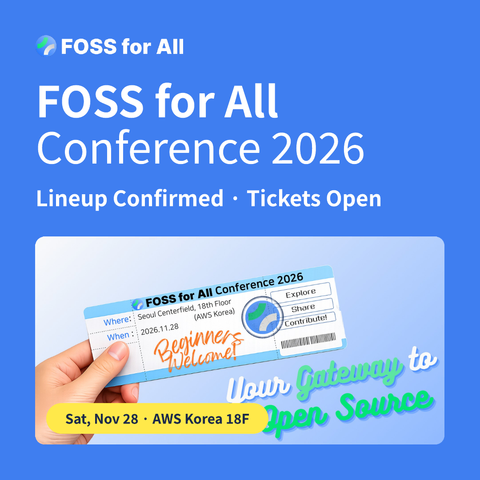
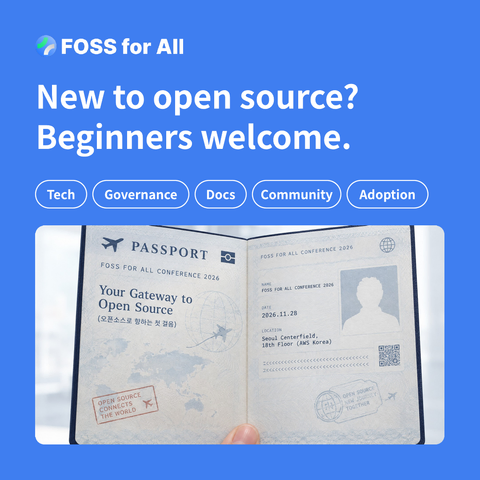
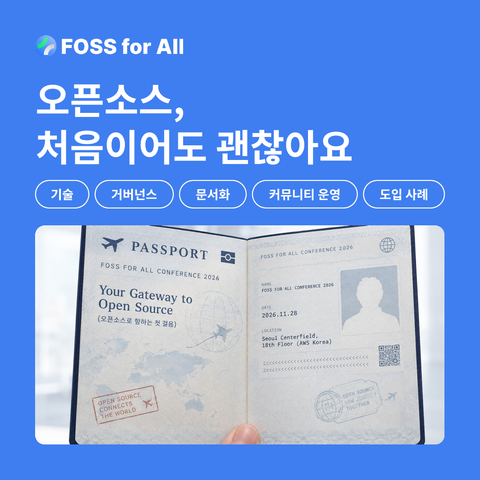
Hello from FOSS for All!
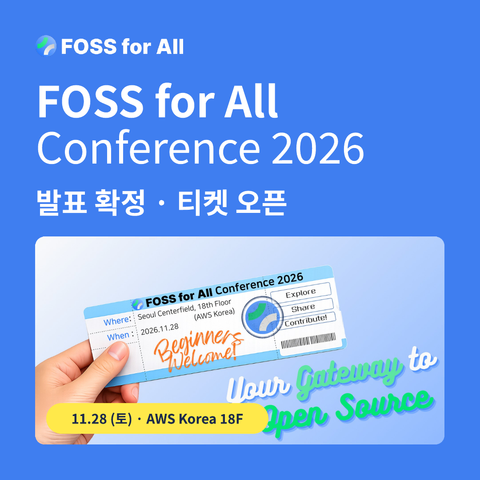
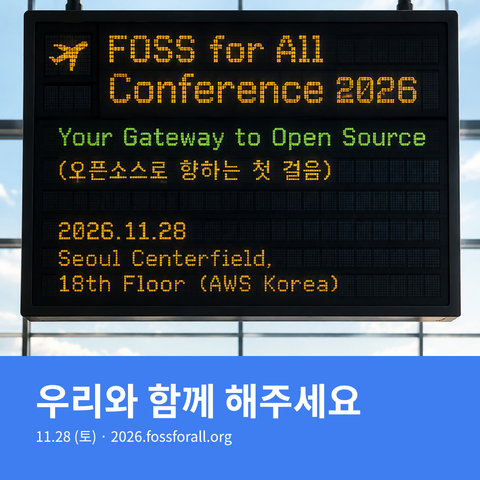
The speaker lineup for FOSS for All Conference 2026 is confirmed, and tickets are now on sale.
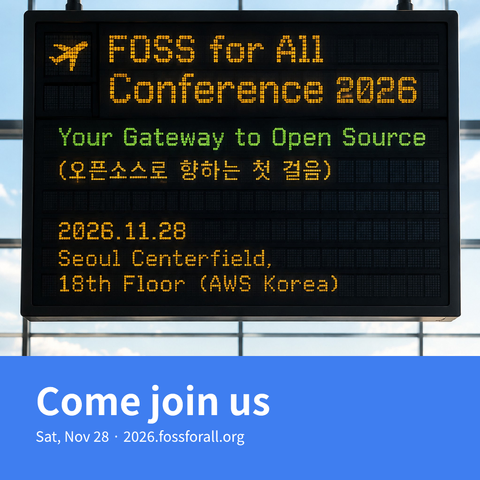
This year’s theme is “Your Gateway to Open Source.”
Beginners and maintainers alike are welcome.
- Date: Sat, Nov 28, 2026
- Venue: Seoul Centerfield EAST 18F, AWS Korea
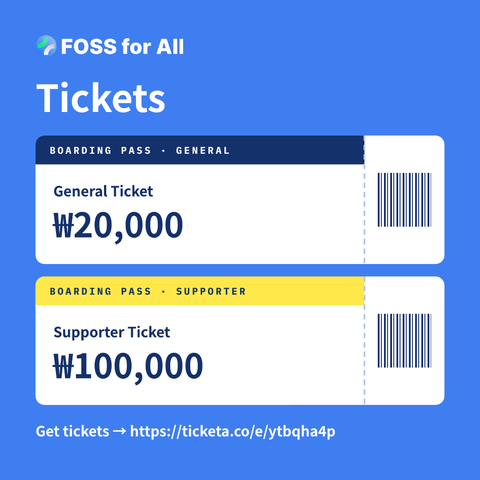
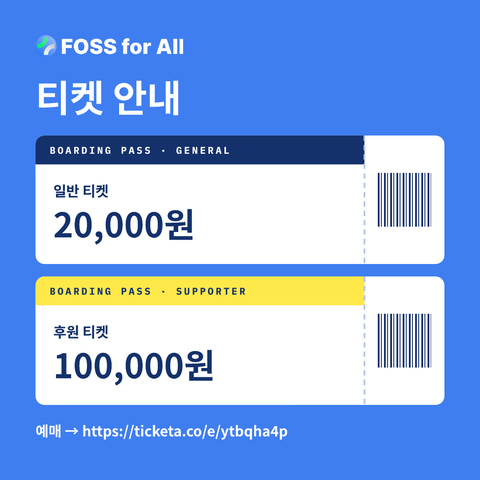
- Tickets: General KRW 20,000 / Supporter KRW 100,000 (supports the conference)
- Register: https://ticketa.co/e/ytbqha4p
- Sessions: https://2026.fossforall.org/sessions/
FOSS for All Conference 2026 티켓 판매 시작
올해 주제는 "오픈소스로 향하는 첫 걸음"이에요. 오픈소스를 이제 막 알게 된 분도, 직접 프로젝트를 운영하는 분도 모두 환영해요. 기술부터 거버넌스, 문서화, 커뮤니티 운영, 도입 사례까지 다양한 세션과 커뮤니티 부스를 준비했어요.
- 일시: 2026년 11월 28일(토)
- 장소: 서울 센터필드 EAST 18층, AWS Korea
- 티켓: 일반 티켓 20,000원 / 후원 티켓 100,000원
- 예매: https://ticketa.co/e/ytbqha4p
- 세션 목록 : https://2026.fossforall.org/sessions/
(narrator, from the future) "It did not"
Anyway, the moment I heard the news, I opened an issue in Fedify with a master plan for moving Deno out of our main development tooling.
Fedify will keep supporting Deno alongside Node.js, and keep publishing packages to JSR alongside npm. Deno just won't be what we develop with anymore.
github.com
Background Deno has announced that its team is joining Cloudflare. The Deno team will provide monthly bug fixes and security updates for the runtime for another year, then end its own runtime devel...
I wrote about Deno's decline a few months ago: I wish Deno would keep doing what it does best. I shared its vision, but I think it never got far because a startup was the one carrying it out. This decision makes me more sure of that.
It also settles something for me. From now on I won't trust a development platform built by a startup, however good the vision. Too risky, too easy to get betrayed.
What I'd rather see is people with strong ideas about development platforms letting go of the impatience and building them as community-driven F/OSS projects instead. Funding is the obstacle, of course. I hope good F/OSS funds like NLnet and the Sovereign Tech Fund keep expanding.
hackers.pub
Deno emerged as a solution to the overwhelming configuration requirements of the modern TypeScript ecosystem by offering a zero-config, single-binary experience. By integrating essential tools for formatting, linting, and testing alongside web-standard APIs, it removed the tedious setup rituals that often deterred developers. Recently, however, Deno has pivoted toward deep Node.js compatibility, supporting npm packages and traditional module structures to accelerate adoption. This shift creates a strategic risk where high compatibility might inadvertently discourage developers from targeting Deno’s unique APIs, especially as Node.js adopts Deno’s innovations like native TypeScript support and permission models. Commercial pressures may be forcing a prioritization of rapid growth and compatibility over the patient development of a truly self-sufficient, vertically integrated toolchain. While Deno remains a powerful choice, its convergence with the legacy ecosystem suggests a move away from the radical simplicity that originally defined its mission. The ongoing convergence of runtimes serves as a vital reminder of the trade-offs between technical purity and the demands of commercial viability.
For years I worked in Python and dreamed in Haskell on weekends. When I needed a script, Python. When I wanted the type system to hold me accountable, Haskell. Somewhere between the two sat TypeScript, and I knew it. Practical where Haskell is austere, typed where Python isn't. But I kept my distance. tsconfig.json, .eslintrc, .prettierrc, babel.config.js. Files you have to create before you've written a single line of actual code. Every time I thought about trying it, I looked at the list and gave up. The JavaScript ecosystem always felt to me like an amusement park where you have to wait in a long queue just to get inside.
Deno dissolved that queue. No configuration files, no node_modules, no
agonizing over which package manager to use. Just deno run main.ts. The first
time I actually wrote TypeScript properly, I couldn't understand why I'd put it
off so long. What I'd been avoiding wasn't TypeScript. It was the ritual
surrounding TypeScript.
At first I couldn't point to one killer feature. The appeal was that everything
seemed to be pulling in the same direction. The fetch() I used in browsers
worked the same way on the server. Web Crypto API was just there. MDN
effectively became Deno's documentation. Instead of installing packages, you
imported ESM by URL, thinking about dependencies in an entirely different way.
Having deno fmt, deno lint, deno test, deno bench, and deno check all
in a single binary was part of the same logic. No installing ESLint, no wiring
up Prettier, no untangling configuration conflicts between the two. That
convenience had an attitude behind it.
The pattern was obvious enough: build on web standards, then ship the boring tools yourself.
Today's Deno feels like it's drifting away from that.
npm: specifier support, node_modules back in play, node:* module
compatibility. Then in Deno 2.8, deno add without a specifier now adds an npm
package by default. JSR was introduced as an answer to npm's stagnation, as the
future of JavaScript packaging. These decisions make that announcement look
distant. I can understand each one in isolation. Put them together, though, and
the shape is hard to ignore: Deno is spending more and more of its energy
catching up to Node.js.
The OS/2 story comes to mind. IBM expected that building Windows compatibility into OS/2 would pull Windows users across. What actually happened was the opposite: developers realized they could target Windows and have it run on both platforms, so there was no reason to learn the OS/2 API separately. Deno pushing further toward Node.js compatibility has the same dynamic. The more compatible Deno becomes, the less reason library authors have to think about it specifically.
Meanwhile, Node.js has been walking toward Deno.
TypeScript runs without flags as of v22.
A permission model arrived in v20. fetch()
and Web Crypto API are both there now.
node:test and node:assert/strict have quietly
become the best cross-runtime test harness for projects targeting Deno,
Node.js, and Bun alike. The two runtimes are converging, but Deno seems to be
doing more of the reaching.
Early Deno set the agenda. Web standards, the permission model, URL imports, JSR: Deno put these down and the ecosystem responded. What Deno is doing now runs in the opposite direction, catching up to what the ecosystem already has.
There's a more specific frustration here. Deno had a fight it could have led rather than chased.
What drove me away from the JavaScript ecosystem wasn't Node.js itself. It was
the full combination: Node.js + npm + TypeScript + Vite + ESLint + Prettier +
Vitest. That stack was the problem, and Deno was already doing well against it.
deno fmt, deno lint, deno test, deno bench, deno check, and in
2.4, deno bundle came back. It had been deprecated once and then
restored; that round trip is its own admission that the direction was right.
The most visible gap that remains is the dev server: HMR, live reload, an asset pipeline, and the plugin ecosystem that accumulates on top of all that. Fresh 2.0, Deno's own framework, chose not to fill that gap from within Deno and adopted Vite instead. That disappointed me. Making Vite run well on Deno and making Deno a self-sufficient development environment are two entirely different directions. Once your own framework makes that choice, you can't expect the wider ecosystem to go the other way.
But vertical integration alone might not have been enough. Individual component
quality matters too. If deno lint and deno fmt were clearly better than
ESLint and Prettier, developers would reach for them even in Node.js projects.
That could have been the Trojan horse. Once enough projects are using Deno's
tools without using the Deno runtime, the next question follows naturally.
ESLint and Prettier seemed unmovable, and yet Biome and the Ox series (Oxlint,
Oxfmt) are finding their footing. The market was always there. Better tools
just weren't. Deno could have gotten there first.
Why didn't Deno hold the course? This is speculation, but here's my read.
The integrated toolchain path required patience. Getting developers to feel the pain of configuration complexity, making Deno the place they move to, waiting for the ecosystem to grow comfortable with Deno's way of doing things. All of that takes time. Node.js is a community project under the OpenJS Foundation. There's no investor clock pushing it, and the project doesn't wobble if the ecosystem moves slowly.
Deno Land Inc. is different. A VC-backed company has a clock. How long that clock allows for a patient fight is not the same as what a community project can afford. Expanding Node.js compatibility produces visible results faster than the slow alternative. From the outside, I can't tell when I'm seeing a product decision and when I'm seeing a runway decision. What I can say is that the urgency Deno has been showing doesn't sit well with the direction it originally chose.
For all my griping, I still build most of my own libraries Deno-first. I publish to JSR even when I also publish to npm. I try to depend only on web standard APIs, and I use Deno's built-in tools for linting and formatting. I'm still rooting for Deno.
But even I have retreated in places. I now rely on node:test and
node:assert/strict for testing, because it's the easiest way
to run the same tests across Deno, Node.js, and Bun without any special
dependencies. JSR was launched as an answer to npm's stagnation, and I've
started to feel JSR stagnating too. I often catch myself wondering whether to
drop it. I got excited about Deno KV and now I just use node:sqlite, which
runs fine on Deno anyway.
If someone like me is already making these retreats, I wonder what Deno looks like to someone with no attachment to it at all. That worries me, because I still want Deno to win some version of this fight. I'm just less sure lately that Deno wants to win the same fight I signed up for.
nodejs.org
😱 “We will support the Deno runtime for another year with monthly releases containing bug fixes and security updates. After that year we will end our development of the Deno runtime. Deno will remain open source, and we welcome others who want to continue its development.” https://deno.com/blog/cloudflare
deno.com
Putting ourselves in the best place to build the future of the web
We're making the Cloudflare developer platform the best place to run JavaScript, anywhere.
Big step toward that today: the Deno team is joining us to build what’s next.
blog.cloudflare.com
The Deno team is joining Cloudflare to radically simplify self-hosting Workers and Durable Objects, so developers can use the same primitives in more places.
I have introduced Mastodon to few friends in China before but none of them stick around (they did register accounts though). Now with the beautiful redesign of the Mastodon web app, I should really convince them to try again.
mitir.social
<center>🎉 $[sparkle **JPEG XL enabled by default since Chromium 155**] 🎉</center> ?[요상한 이유로 Chromium에서 JPEG XL 지원이 삭제된 그날](https://issues.chromium.org/issues/40168998#comment85)로부터 약 4년만에 (정말 길었네요), JPEG XL이 enabled by default가 된 Chromium 155의 early stable 배포가 시작되었습니다. (Firefox도 몇 주 뒤에 이어서 enabled by default가 될 예정입니다.) 개인적으로 점진적 디코딩 기능 (Chromium과 Firefox 둘 다 이 기능을 지원함) 과 JPEG 무손실 재압축 기능이 킬러 피처라고 생각하고 있습니다. 한번 써보셨으면 좋겠습니다. :ablobcat_blinkhyper: 4년 전 당시에는 C++ 레퍼런스 구현인 libjxl을 사용했었으나, 이번에 배포되는 구현은 Rust로 작성한 ?[jxl-rs](https://github.com/libjxl/jxl-rs)를 사용합니다. <small>당사 비교 결과</small> jxl-rs는 libjxl보다 평균적으로 빠른 디코딩 속도와 적은 메모리 사용량을 보여줍니다. 곧 마찬가지로 JPEG XL이 enable by default가 될 Firefox에서도 jxl-rs를 사용합니다. macOS/Safari에서도 jxl-rs로 갈아타줬으면 좋겠네요 :blobcat_googly_mlem: jxl-rs에는 제가 주요 개발자 중 한 명으로 참여했습니다 <small>라고 저는 주장하고 있음</small>. 많관부
github.com
Contribute to libjxl/jxl-rs development by creating an account on GitHub.
github.com
Contribute to libjxl/jxl-rs development by creating an account on GitHub.
LogTape 2.4.0 is out. #LogTape is a zero-dependency #logging library for #JavaScript and #TypeScript that runs on #Deno, #Node.js, #Bun, and browsers.
The main changes:
captureSourceLocation records where each log call was made, and the text formatters can show it. Meant for development, since it costs a stack trace per call.inspectLogger() reports how a logger's level, inherited sinks, and filters combine, so you can see why a record doesn't reach a sink.parentSinks: "forward" lets a child category inherit its ancestors' sinks without their level thresholds.drain() waits for pending sink output without disposing of the sinks, and fromAsyncSink() gets queue limits and a waitUntil hook for serverless platforms.fingersCrossed() can go back to buffering after a trigger, and flush or discard buffers per request.completionLevel callback that picks the log level from the response.Two changes can affect existing code: getRotatingFileSink() now requires maxFiles to be an integer from 1 to 1,000, and TextFormatterOptions.value now also accepts "bare", so code that calls it directly has to check its type first.
github.com
LogTape is a logging library for JavaScript and TypeScript that works across Deno, Node.js, Bun, and browsers. It's built around structured logging, has zero dependencies, and is designed to work a...
11月20日(金)〜23日(月)に、JSConf JP 2026への参加で東京を訪れます。20日(金)の夜か21日(土)に会って、食事やお茶をご一緒できる方はいらっしゃいますか?
jsconf.jp
jsconf.jp is a JavaScript festival in Japan powered by Japan Node.js Association. This is the seventh time event of jsconf in Japan. We would love to become a bridge between Japanese Web Developers and International Web Developers.
Fedify had security updates for two vulnerabilities. Please update your Fedify to 2.0.30, 2.1.26, 2.2.15, 2.3.10, or 2.4.0 now!
hackers.pub
Fedify has released security updates addressing two vulnerabilities: an unbounded alternate-document fetch chain issue that allows attackers to trigger indefinite HTTP loops to exhaust server resources, and a routing flaw where unverified activity documents could bypass dereference verification. The patches introduce a strict 20-hop limit across redirects, preserve fetch cancellation signals, and ensure that dereferenced activities properly replace unverified JSON-LD documents during inbox routing. Upgrading Fedify across affected 2.x versions and migrating from 1.x is critical to securing federated servers against resource exhaustion and spoofed payload processing.
Two vulnerabilities have been fixed: GHSA-97w4-f4rq-mgqm, unbounded alternate-document fetch chains vulnerability and GHSA-39gj-rchc-q5m3, unverified activity routed after dereference verification vulnerability.
The patched releases are 2.0.30, 2.1.26, 2.2.15, 2.3.10, and 2.4.0. Both vulnerabilities affect the preceding releases on those lines: 2.0.28 and 2.0.29, 2.1.24 and 2.1.25, 2.2.13 and 2.2.14, 2.3.8 and 2.3.9. If you still use Fedify 1.x, change your dependency to patched 2.x release because package-manager update commands do not cross the declared major-version range.
GHSA-97w4-f4rq-mgqm affects Fedify's document loaders when fetching remote keys and ActivityPub documents. Fedify follows alternate-document links supplied through HTTP Link headers and HTML, but following an alternate document reset the redirect counter and visited-URL history. An attacker could therefore make two URLs refer to each other as alternate documents and cause Fedify to fetch them indefinitely. Following an alternate link also dropped the caller's cancellation signal, so aborting the original operation did not stop the fetch chain.
An unauthenticated inbox request could exploit this by referencing an attacker-controlled signing-key URL. Resolving the key could then enter an unbounded alternate-document chain, continuously issuing HTTP requests and DNS lookups and eventually exhausting server resources. Both getDocumentLoader() and getAuthenticatedDocumentLoader() were affected, including their use in @fedify/vocab-runtime and @fedify/fedify.
The fix makes alternate-document links and ordinary HTTP redirects share the same 20-hop limit and visited-URL history. It also preserves the caller's cancellation signal throughout the entire fetch chain. This closes a gap left by the earlier redirect-loop fix for CVE-2026-34148.
GHSA-39gj-rchc-q5m3 has been present since Context.routeActivity() was introduced in Fedify 1.3.0. Context.routeActivity() verifies an activity before passing it to inbox listeners. When an activity has no verifiable Object Integrity Proof, Fedify dereferences its id and verifies the fetched copy. However, only the Activity object was replaced with the verified copy; the original, unverified JSON-LD document supplied by the caller was retained.
With an inbox queue configured, that unverified document was enqueued and later delivered to inbox listeners without being verified again. An attacker who knew the ID of any dereferenceable activity could therefore submit a document with the same ID but an actor, object, and addressing of their choice, causing the application to process attacker-controlled data as authenticated. Without a queue, listeners received the verified Activity object, but their InboxContext still contained the unverified document, which InboxContext.forwardActivity() could forward to other servers.
Applications that never call Context.routeActivity() are not affected. Activities successfully authenticated using an Object Integrity Proof are also unaffected, as is the HTTP inbox, which does not use this routing path.
The fix replaces both the Activity object and its JSON-LD document with the verified copy when Context.routeActivity() falls back to dereferencing. Inbox queues, InboxContext, and forwarding therefore all operate on the same document that was actually authenticated.
Update @fedify/fedify:
npm update @fedify/fedify
yarn upgrade @fedify/fedify
pnpm update @fedify/fedify
bun update @fedify/fedify
deno update @fedify/fedify
Check if your resolved dependency versions are at least 2.0.30, 2.1.26, 2.2.15, 2.3.10, or 2.4.0 on the corresponding release line. Please redeploy every Fedify-based servers, after updating.
The full Github Security Advisories are GHSA-97w4-f4rq-mgqmand GHSA-39gj-rchc-q5m3.
Thanks to @adelzaitri for reporting unverified activity is routed after dereference verification issue.
Ask below if anything is unclear.
github.com
Security researcher & engineer | CISSP | Incoming PhD student in Offensive Cyber Engineering - adelzaitri