@hongminhee@hollo.social · Reply to 洪 民憙 (Hong Minhee)
The pull request is merged now: https://w3id.org/fep/f799.
w3id.org

@hongminhee@hollo.social
1,123 following1,656 followers
An intersectionalist, feminist, and socialist living in Seoul (UTC+09:00). @tokolovesme's spouse. Who's behind @fedify, @hollo, and @botkit. Write some free software in #TypeScript, #Haskell, #Rust, & #Python. They/them.
서울에 사는 交叉女性主義者이자 社會主義者. 金剛兔(@tokolovesme)의 配偶者. @fedify, @hollo, @botkit 메인테이너. #TypeScript, #Haskell, #Rust, #Python 等으로 自由 소프트웨어 만듦.
The pull request is merged now: https://w3id.org/fep/f799.
w3id.org
Okay, now it's merged!
w3id.org
The Web Can't Afford a JavaScript Runtime Monoculture via @hongminhee https://lobste.rs/s/x6n380 #javascript
https://redmonk.com/kholterhoff/2026/10/27/js-runtime-monoculture/
redmonk.com
Earlier this month Deno announced its whole team is joining Cloudflare. In the announcement, Ryan Dahl, who created Node.js and started Deno in 2018, also explains that development of the Deno runtime will stop after one year. That leaves the web with two major general-purpose runtimes, the OpenJS Foundation’s Node.js and Anthropic’s Bun, alongside Cloudflare’s
blah.rako.space
Following my previous proposal, FEP-22cd: Attributing translations, I've now drafted a proposal for FEP-f799: Coordinated Inbox Delivery Suspension. @nyanrus also helped out this time! The PR hasn't been merged yet, but you can read it here in the meantime.
codeberg.org
DongU Kang (@nyanrus@sukhi.f3liz.casa) and I (@hongminhee@hollo.social) have drafted a proposal for announcing temporary suspensions of ActivityPub inbox delivery, primarily for scheduled maintenance. Peers can defer queued and new deliveries until the announced end time or an earlier cancellation, avoiding predictable failed requests during the interruption. This complements 503 Service Unavailable and Retry-After rather than replacing existing retry policies.
A DeliverySuspension object can cover one inbox or all inboxes at an HTTPS origin. Mutual links establish which actor can control delivery suspensions for that target. HTTP Link headers let peers discover a notice they missed, and signed objects can be served from static storage while the application is offline. Peers keep their own limits on suspension duration and queue storage, and resume gradually to avoid overwhelming a recovering server.
https://codeberg.org/fediverse/fep/pulls/954
Feedback welcome, especially on controller verification and how this would fit existing delivery queues and retry policies. Thanks!
codeberg.org
fep - Fediverse Enhancement Proposals
@jackalope_tracks 알려주신 링크가 https://jpendleton.substack.com/about 쪽으로 리다이렉트되는 것 같은데, 이 링크가 맞나요? 아티클(article)이 아니라 作家 紹介 페이지 같아서요!
jpendleton.substack.com
Asylum seeker, whistleblower, political prisoner, and plaintiff in Pendleton v. United States, et al., No. 1:25-CV-01218 (D.C. 2025). Click to read Turnkey Tyranny, by J. E. Pendleton, a Substack publication. Launched a year ago.
DongU Kang (@nyanrus@sukhi.f3liz.casa) and I (@hongminhee@hollo.social) have drafted a proposal for announcing temporary suspensions of ActivityPub inbox delivery, primarily for scheduled maintenance. Peers can defer queued and new deliveries until the announced end time or an earlier cancellation, avoiding predictable failed requests during the interruption. This complements 503 Service Unavailable and Retry-After rather than replacing existing retry policies.
A DeliverySuspension object can cover one inbox or all inboxes at an HTTPS origin. Mutual links establish which actor can control delivery suspensions for that target. HTTP Link headers let peers discover a notice they missed, and signed objects can be served from static storage while the application is offline. Peers keep their own limits on suspension duration and queue storage, and resume gradually to avoid overwhelming a recovering server.
https://codeberg.org/fediverse/fep/pulls/954
Feedback welcome, especially on controller verification and how this would fit existing delivery queues and retry policies. Thanks!
codeberg.org
fep - Fediverse Enhancement Proposals
The Social Web Foundation is pleased to announce the Social Web Devroom at FOSDEM 2027, and invite participants to submit proposals for talks for the event.
FOSDEM is an exciting free and open source software event in Brussels, Belgium that brings together thousands of enthusiasts from around the world. The event spans the weekend of January 30 to January 31, 2027 and features discussion tracks (“devrooms”) for scores of different technology topics. This is the third FOSDEM Social Web Devroom.
The Social Web Devroom will be a 5 hour track.
There will be two available talk formats:
The Social Web Devroom is open to talks all about the Social Web, AKA the Fediverse, including:
Submit talk proposals to https://pretalx.fosdem.org/fosdem-2027/cfp. Select “Social Web” from the “Track” dropdown, and include the length of your talk (8/25) in the submission notes. (Note that the “Lightning Talks” track is a separate event-wide track; if you’re proposing a Social Web micro-talk, please choose the “Social Web” track!)
All attendees and speakers must be familiar with and agree to the FOSDEM Code of Conduct.
Questions about topics, formats, or the Social Web in general should go to contact@socialwebfoundation.org.
AI ban should not be an excuse to exclude minorities, as I heard some communities started banning non English speakers who use machine translation
이 짤이 벌써 10年도 넘었구나. 좋아하는 블랙 조크지만 韓國語 話者가 아니면 웃긴 포인트들을 제대로 알아채기 힘들 듯…? 😂 프로필 寫眞과 닉네임이 伊藤博文인 點(게다가 日本語 읽기가 아니라 韓國語 漢字音 읽기인 「이등박문」)이나, 朴正熙를 굳이 그의 創氏改名한 日本姓인 「高木」로 부른 點이나, 「內地」라는 表現이 韓國語에서 갖는 뉘앙스라든가…
參考로, 伊藤博文와 朴正熙 둘 다 射殺된 날이 10月 26日로 같다. (伊藤博文은 1909年 10月 26日, 朴正熙는 1979年 10月 26日.)
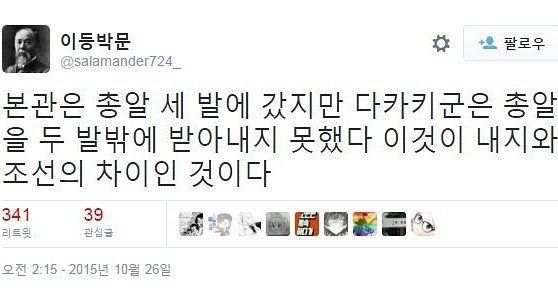
2015年 10月 26日 午前 2時 15分에 Twitter에 게시된 한 트윗의 캡처. 「이등박문」(伊藤博文의 韓國語 漢字音 읽기; ID: @salamander724_)이라는 닉네임의 使用者가 쓴 글. 「本官은 銃알 세 發에 갔지만 高木 君은 銃알을 두 發 밖에 받아내지 못했다. 이것이 內地와 朝鮮의 差異인 것이다.」
If you run Hollo, update to 0.8.17 or 0.9.25 now. These releases fix GHSA-r48c-xx2h-fv4g, a DNS rebinding vulnerability in Fedify that could bypass Hollo's server-side request forgery (SSRF) protection and cause requests to reach internal services.
Fedify checked that a hostname resolved only to public addresses, then let the HTTP client resolve it again when connecting. An attacker controlling the hostname's DNS answers could return a public address for validation and a private or loopback address for the connection. Redirects and alternate-document links had the same gap.
The affected Fedify paths used by Hollo include remote document loading (authenticated or not), outbound activity delivery, and WebFinger lookups. On Node.js, which Hollo uses, the fix restricts connections to addresses that passed validation. Hollo's ALLOW_PRIVATE_ADDRESS=true option still permits private destinations; leave it unset for public federation. For full technical details, see the Fedify security announcement and the advisory linked above.
All releases on the supported Hollo 0.8.x and 0.9.x lines up to and including 0.8.16 and 0.9.24 are affected. 0.8.17 and 0.9.25 are the first fixed releases and the latest on those lines, incorporating Fedify 2.1.31 and 2.2.20 respectively. Hollo 0.7.x and earlier are no longer supported under the Hollo security policy; operators on those lines should move to a supported release.
For 0.8.x deployments, update to 0.8.17:
docker pull ghcr.io/fedify-dev/hollo:0.8.17For 0.9.x deployments, update to 0.9.25:
docker pull ghcr.io/fedify-dev/hollo:0.9.25After pulling the image, recreate your Hollo container using the new image. With Docker Compose, update the image tag in your Compose file and run docker compose up -d. For source deployments, check out the corresponding release tag, run pnpm install --frozen-lockfile using the pnpm version pinned in that tag's package.json, run pnpm run build, and restart the server.
If you have a large 0.9.x database and are upgrading from a release before 0.9.20, follow the 0.9.20 index preparation instructions before starting the new version to avoid blocking writes during the new version's automatic migration.
Thanks to @finalchild for reporting the DNS rebinding issue to the Fedify project.
If anything is unclear, ask below.
github.com
Federated single-user microblogging software. Contribute to fedify-dev/hollo development by creating an account on GitHub.
If you use BotKit, update to a patched release now. GHSA-r48c-xx2h-fv4g is a DNS rebinding vulnerability in Fedify, which BotKit uses for federation. An attacker could bypass its server-side request forgery (SSRF) protection and cause your bot's server to reach internal services. Deno deployments need additional network restrictions; upgrading BotKit alone does not close the vulnerability on Deno.
Fedify checked that a hostname resolved only to public addresses, then let fetch() resolve it again when connecting. An attacker controlling the hostname's DNS answers could return a public address for validation and a private or loopback address for the connection. This affects remote document loading, both anonymous and authenticated, as well as outbound activity delivery, NodeInfo lookups, and WebFinger lookups. Redirects and alternate-document links were subject to the same gap.
On Node.js and Bun, the fix makes connections only to addresses that passed validation. Bun deployments that set HTTP_PROXY, HTTPS_PROXY, or ALL_PROXY, including their lowercase forms, should use Bun 1.4.3 or later. Alternatively, unset those variables for the bot process or configure the proxy to refuse private destinations. Earlier Bun versions can send requests through a proxy that resolves the hostname again. With the fix applied, HTTPS requests to non-default ports fail on Bun versions before 1.3.11 because those versions cannot verify a pinned connection's certificate against the original hostname. See the Bun deployment guidance.
Deno's fetch() cannot pin connections to validated addresses. Use Deno 2.8.1 or later with the documented --deny-net list covering private IPv4 ranges, [::1], and [::], and listen on a Unix domain socket behind a reverse proxy, since the deny list also blocks listening on those IP addresses. Private IPv6 ranges also need network-level restrictions. If that setup is unsuitable, apply equivalent outbound restrictions at the firewall or container network layer. Follow the Deno deployment mitigation for the full deny list and deployment requirements.
BotKit 0.4.x versions through 0.4.10 and BotKit 0.5.x versions through 0.5.7 include affected Fedify versions. The first releases containing the fix, and the current recommended releases, are BotKit 0.4.11 and 0.5.8, which upgrade Fedify to 2.1.31 and 2.3.15, respectively. These are the two supported BotKit lines under the security policy; users on older lines should move to a supported release.
For BotKit 0.5.x, install @fedify/botkit 0.5.8 using the command for your package manager:
npm  install @fedify/botkit@0.5.8
yarn add     @fedify/botkit@0.5.8
pnpm add     @fedify/botkit@0.5.8
bun  add     @fedify/botkit@0.5.8
deno add     jsr:@fedify/botkit@0.5.8
For BotKit 0.4.x, install @fedify/botkit 0.4.11:
npm  install @fedify/botkit@0.4.11
yarn add     @fedify/botkit@0.4.11
pnpm add     @fedify/botkit@0.4.11
bun  add     @fedify/botkit@0.4.11
deno add     jsr:@fedify/botkit@0.4.11
Check the installed or locked versions: @fedify/botkit should be 0.4.11 or 0.5.8. The affected Fedify packages, @fedify/fedify, @fedify/vocab-runtime, and @fedify/webfinger, should resolve to at least 2.1.31 on the 2.1.x line, 2.2.20 on 2.2.x, 2.3.15 on 2.3.x, or 2.4.5 on 2.4.x. Update any direct dependencies on those packages too. If you use a routine update command instead, check that your declared dependency range allows a patched release and change it explicitly if needed. Apply the runtime mitigations above and redeploy all web and worker processes.
The full GitHub Security Advisory is GHSA-r48c-xx2h-fv4g. See also Fedify's own announcement.
Thanks to @finalchild for reporting the DNS rebinding issue to the Fedify project.
If anything is unclear, feel free to ask on GitHub Discussions or Matrix.
matrix.to
You're invited to talk on Matrix
A security update addressing two vulnerabilities in Fedify has been released. Please update as soon as possible!
hackers.pub
Fedify has patched two server-side request forgery (SSRF) vulnerabilities across its supported release lines: a medium-severity DNS rebinding flaw that bypassed private address checks during outbound network requests, and a low-severity issue in the CLI where unvalidated page and favicon lookups could target internal endpoints. The core DNS rebinding vulnerability stems from resolving hostnames separately during validation and connection phases, leaving operations like document loading, activity delivery, and WebFinger lookups susceptible to reaching private networks. While Node.js and Bun pin validated addresses directly—with specific version considerations for proxying and certificate checks on Bun—Deno environments cannot pin connections and require network-level mitigations such as specific permission flags or container firewalls. Operators must also upgrade the CLI tool separately or utilize flags to disable risky requests. Understanding these runtime nuances and version requirements is crucial for ensuring internal network boundaries remain thoroughly protected against SSRF exploits.
The quoted post is hidden while awaiting the author's approval.
If you use an affected Fedify release, update now. Two server-side request forgery vulnerabilities have been addressed: GHSA-r48c-xx2h-fv4g, a DNS rebinding bypass of Fedify's private address checks, and GHSA-cj5r-cw77-6gwp, unvalidated page and favicon requests in fedify nodeinfo. Deno deployments need additional network restrictions; upgrading Fedify alone does not close the DNS rebinding vulnerability.
The patched releases are 2.0.35, 2.1.31, 2.2.20, 2.3.15, and 2.4.5. Update to the corresponding release on your minor line, with the runtime mitigations described below. The affected releases on these lines are 2.0.34 and earlier, 2.1.30 and earlier, 2.2.19 and earlier, 2.3.14 and earlier, and 2.4.4 and earlier. For ongoing support, the security policy covers the latest two minor lines, 2.3 and 2.4. Users on releases before 2.0 should move to a supported release.
Fedify checked that a hostname resolved only to public addresses, then let fetch() resolve it again when connecting. An attacker controlling the hostname's DNS answers could return a public address for validation and a private or loopback address for the connection, causing requests to reach internal services. Redirects and alternate-document links were subject to the same gap.
This affects document loading, including authenticated document loading, outbound activity delivery, NodeInfo lookups, and WebFinger lookups in @fedify/fedify, @fedify/vocab-runtime, and @fedify/webfinger. On Node.js and Bun, the fix makes connections only to addresses that passed validation. Calling validatePublicUrl() before an application's own fetch() still does not pin that connection. Setting allowPrivateAddress: true continues to permit private destinations.
On Bun, deployments with HTTP_PROXY, HTTPS_PROXY, or ALL_PROXY set, including their lowercase forms, should upgrade to Bun 1.4.3 or later. Alternatively, unset those variables for the Fedify process or configure the proxy to refuse private destinations. Older Bun versions may send requests through a proxy that resolves the hostname again. On Bun versions before 1.3.11, Fedify now refuses HTTPS requests to non-default ports because those Bun versions cannot verify a pinned connection's certificate against the original hostname. See the Bun deployment guidance.
Deno's fetch() cannot pin connections to validated addresses. Use Deno 2.8.1 or later with the documented --deny-net list and a Unix domain socket behind a reverse proxy, plus network-level restrictions for private IPv6 ranges. If that setup is unsuitable, apply equivalent outbound restrictions at the firewall or container network layer. Follow the Deno deployment mitigation.
An operator running fedify nodeinfo against a malicious instance could cause the CLI to send a GET request to a loopback, link-local, or private address from the operator's machine. The NodeInfo lookup validated destinations, but the subsequent page and favicon requests used plain fetch() with automatic redirects. A malicious favicon URL or page redirect could therefore reach an internal endpoint.
The attacker does not directly receive the response body, but the request can affect an internal endpoint with GET side effects. The fix validates page, favicon, and redirect destinations, skipping the favicon when a destination is private while still showing the NodeInfo document. Upgrade @fedify/cli separately from the library. Until then, --no-favicon or --raw avoids these page and favicon requests. The Bun and Deno caveats above also apply to the CLI.
Use the command for your package manager to install 2.4.5 explicitly:
npm  install @fedify/fedify@2.4.5
yarn add     @fedify/fedify@2.4.5
pnpm add     @fedify/fedify@2.4.5
bun  add     @fedify/fedify@2.4.5
deno add jsr:@fedify/fedify@2.4.5
If you stay on another minor line, substitute 2.0.35, 2.1.31, 2.2.20, or 2.3.15 as appropriate. Update direct dependencies on @fedify/vocab-runtime and @fedify/webfinger to the same release as well. Check the resolved versions in your lockfile, since an ordinary update command can stay within a vulnerable dependency range or leave a transitive dependency locked. Apply the runtime mitigations above and redeploy all web and worker processes.
For an npm-installed global CLI:
npm install -g @fedify/cli@2.4.5For other installation methods, reinstall the corresponding patched version using the CLI installation instructions. Check fedify --version before using it against an untrusted instance.
Thanks to @finalchild for reporting the DNS rebinding issue and to Zachariah Mithani for reporting the favicon request issue.
If anything is unclear, ask below.
github.com
Security researcher. Founder of AploSec (aplosec.si), autonomous vulnerability research. 45 CVEs in open source. - zachariah-mithani
올해 11月 末 서울에서 開催되는 @fossforall Conference 2026에서 〈Oseo: SBCL 스타일의 JavaScript/TypeScript AOT 컴파일러〉라는 題目으로 發表합니다. Oseo는 JavaScript/TypeScript를 인터프리터나 JIT 없이 미리 네이티브 코드로 컴파일하는 프로젝트로, 動的 타입 言語임에도 오래 前부터 AOT 컴파일러가 쓰여 온 SBCL이나 Chez Scheme 같은 Common Lisp 및 Scheme 系譜에서 靈感을 얻었습니다. 모든 函數를 저네릭(generic) 經路와 가드가 붙은 特殊化 經路로 두 벌 컴파일해 두고, 가드가 失敗하면 바이너리 안의 저네릭 經路로 갈라질 뿐 最適化 解除(deoptimization) 같은 건 하지 않는 게 核心 아이디어입니다.
아직 未完成인 프로젝트라, 實際로 돌아가는 모습과 앞으로 남은 길을 함께 보여드릴 豫定입니다. 寄與에 關心 있는 분도 歡迎합니다.
2026.fossforall.org
Common Lisp의 SBCL 이나 Scheme의 Chez Scheme 은 동적 타입 언어이면서도 프로그램 전체를 미리 네이티브 코드로 컴파일해 수십 년째 프로덕션에서 쓰이고 있습니다. 반면 JavaScript는 여전히 인터프리터와 여러 단계의 JIT, 그 위에 얹힌 디옵티마이제이션
Really excited to see progress on this effort after many many years of stalled discussion. Thanks to @Edent, @hongminhee, @lnkr, @north and @evan as well for their recent work on this matter, I can now see a fediverse in sight that supports the world's languages fully!
mastodon.social
#TIL there's a spec for detecting links in text: "UTS #58: Unicode Link Detection and Formatting: URLs and Email Addresses" https://www.unicode.org/reports/tr58/ #Unicode #UTS58
#TIL there's a spec for detecting links in text: "UTS #58: Unicode Link Detection and Formatting: URLs and Email Addresses" https://www.unicode.org/reports/tr58/
unicode.org
#TIL there's a spec for detecting links in text: "UTS #58: Unicode Link Detection and Formatting: URLs and Email Addresses" https://www.unicode.org/reports/tr58/
unicode.org
@dansup Great job! I tested it with my Hollo instance, and it already works well! 👍
https://columnly.social is a Mastodon/Pixelfed column based multi-account client I'm building for myself.
- It's hosted in Canada
- Without Cloudflare enabled
- There is no 3rd party servers, Columnly speaks directly with your server
- It will be licensed under AGPL-3.0 and open sourced later this year.
columnly.social
The fediverse, in columns. A multi-column client for Mastodon and Pixelfed.
#Gukhanmun 0.3.0をリリースしました。漢字の異体字認識、後ろに続く助詞による読みの選択、句読点プロファイル、外来語表記用例の同梱が入っています。
沖縄県(新字体)は、辞書にある沖繩縣(康熙字典体)と照合して오키나와현と読みます。--hanja-variant-setは漢字を新字体や康熙字典体で出力し直します。一切は既定で일절ですが、一切를のように後ろに付く助詞によって일체を選びます。--punctuation modernは하나、둘。を하나, 둘.に変えます。国立国語院の『外来語表記用例』を辞書としてko-krプリセットに同梱したので、香港が홍콩と読まれるようになりました。
v0.2.xからアップグレードする場合は、ko-krプリセットの出力が変わり、同梱辞書ファイルが形式v2になるので、バインディングとデータパッケージを一緒に上げてください。
github.com
Gukhanmun is a library and CLI tool for converting Korean text written in mixed hanja/hangul script into consistently annotated output. Academic texts, historical documents, and legal materials rou...
#Gukhanmun 0.3.0 is out with Han character variants, reading selection from following particles, punctuation profiles, and a bundled loanword dictionary.
沖縄県 (shinjitai) now finds 沖繩縣 (Kanxi form) in the dictionary and reads 오키나와현, while --hanja-variant-set re-emits hanja in shinjitai or Kanxi form. 一切 defaults to 일절, but a following particle such as 一切를 selects 일체, and --punctuation modern turns 하나、둘。 into 하나, 둘.. The National Institute of Korean Language's loanword spelling examples are bundled into the ko-kr preset as well, which is why 香港 now reads 홍콩.
Upgrading from v0.2.x changes ko-kr output and moves the bundled dictionaries to format v2, so upgrade the bindings and data packages together.
https://github.com/dahlia/gukhanmun/discussions/32
#hanja #hangul #korean #國漢文 #國漢文混用 #國漢文混用體 #국한문 #국한문혼용 #국한문혼용체
github.com
Gukhanmun is a library and CLI tool for converting Korean text written in mixed hanja/hangul script into consistently annotated output. Academic texts, historical documents, and legal materials rou...
#Gukhanmun 0.3.0이 나왔습니다. #漢字 異體字 認識, 助詞를 利用한 讀音 選擇, 句讀 符號 프로파일, 內藏 外來語 表記 用例가 들어갔습니다.
沖縄県(新字體)은 辭典에서 沖繩縣(康熙字典體)을 찾아 오키나와현으로 읽고, --hanja-variant-set은 漢字를 新字體나 康熙字典體로 다시 出力합니다. 一切은 일절이 基本이지만 一切를과 같이 뒤에 붙는 助詞에 따라 일체를 고르며, --punctuation modern은 하나、둘。을 하나, 둘.로 바꿉니다. 또한, 國立國語院 《外來語 表記 用例》를 辭典으로 묶어 ko-kr 프리셋에 넣었습니다. 德分에 香港이 홍콩으로 읽힙니다.
v0.2.x에서 올릴 때는 ko-kr 프리셋의 出力이 달라지고 內藏 辭典 파일이 形式 v2로 바뀌므로, 바인딩과 데이터 패키지를 함께 올리세요.
github.com
Gukhanmun is a library and CLI tool for converting Korean text written in mixed hanja/hangul script into consistently annotated output. Academic texts, historical documents, and legal materials rou...
Seoul 1988 Olympic logo :)
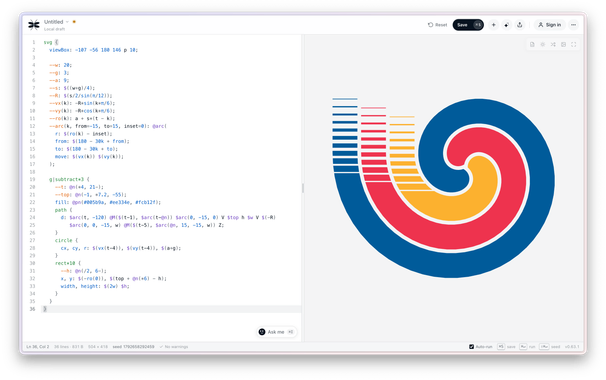
Seoul 1988 Olympic logo
빵은 그다지 좋아하지 않지만 햄버거는 좋아한다. 그래서 빵 代身 밥이 들어간 라이스버거를 좋아한다. 모스버거에서 파는 モスライスバーガー燒肉를 가장 좋아하는데, 아쉽게도 韓國에서는 안 팔아서 日本에 갈 때만 가끔 사 먹는다. 韓國에서는 그 代身 롯데리아에서 파는 全州 비빔라이스 버거를 즐겨 먹는다. 오늘도 이걸 먹었다. 이 메뉴는 反對로 또 日本 ゼッテリア(日本 롯데리아는 2023年에 すき家 等의 母會社인 ゼンショーホールディングス에 賣却되어, 商號가 바뀌었다)에서는 안 판다.
lotteeatz.com
전주 비빔라이스 버거
https://github.com/antfu/furifont 보고 한글도 되나 했는데 잘 되네
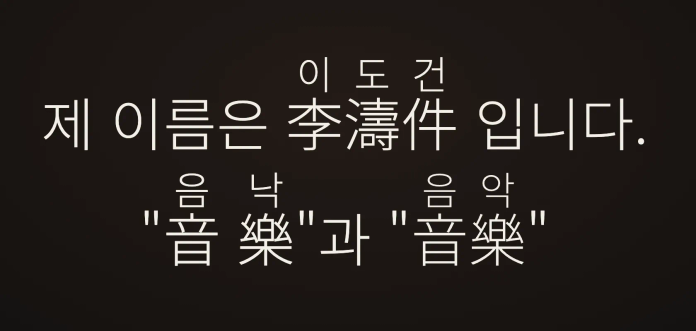
어두운 배경에 흰색 글씨로 "이도건, 제 이름은 李濤件 입니다. 음낙 '音樂'과 '音樂'"이라는 문구가 적혀 있습니다. 글자 위에는 작게 한글 독음이 병기되어 있습니다.
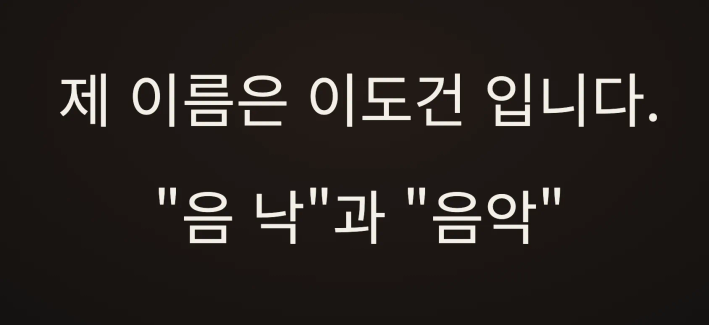
검은색 배경에 흰색 글씨로 "제 이름은 이도건 입니다."와 그 아래에 ""음 낙"과 "음악""이라는 문구가 적혀 있습니다.
@timapple Thanks! Yeah, it's actually a very specific problem for people who still write in mixed-script Korean today like me (which is very rare). 😂
@dansup Thanks!! 🥰
I'm happy and honored that Gukhanmun has been selected as one of the five recipients of FOSS for All Microgrants 2026! Gukhanmun is my Rust/JavaScript library and CLI tool for converting mixed-script Korean text, which combines hangul and hanja, into hangul-only text.
FOSS for All Microgrants is a new program launching this year that collects donations to support open source projects and communities. It also explores fiscal sponsorship by paying expenses on recipients’ behalf, alongside direct grants.
Thank you to @fossforall, the reviewers, and everyone who donated to the program. I'm grateful for your support for Gukhanmun and its continued development.
제가 開發하는 Gukhanmun이 FOSS for All Microgrants 2026의 受惠 組織으로 選定되었습니다! Gukhanmun은 國漢文混用體로 쓰인 韓國語 文書를 한글 專用으로 變換하는 Rust/JavaScript 라이브러리이자 CLI 道具입니다.
올해 처음 始作하는 이 事業의 支援을 받게 되어 무척 기쁘고 榮光스럽습니다. @fossforall 및 審査委員 여러분, 그리고 寄附로 함께해 주신 모든 분께 感謝드립니다. Gukhanmun의 開發을 繼續해 나가는 데 큰 힘이 되겠습니다!
https://forum.fossforall.org/t/foss-for-all-microgrants-2026/162
forum.fossforall.org
올해 처음 진행중인 우리 단체의 기부금 모집 및 분배 사업인 FOSS for All Microgrants 사업에 많은 관심을 가져 주셔서 감사합니다. 오늘 Microgrants 팀 에서는, 심사위원 분들과 최종 수혜조직 선정을 위한 회의를 진행 하였습니다. 그 결과로, 지원을 받은 13곳의 프로젝트 및 커뮤니티 중에서 최종적으로 5곳의 수혜조직을 선정 하였습니다. 선정된 조직은 아래와 같으며, 금주 안으로 후속 절차를 이메일로 안내 드릴 예정입니다. 선정된 수혜조직 구성원 분들 모두 축하 드리며, 큰 기부금은 아니지만, 프로젝트와 커뮤니티의 성장에 조금이나마 도움이 되기를 바랍니다! llvm-z80 llvm-z80 은 llvm 의 다운스트림 프로젝트로, 게임보이 등 단말기에 사용되는 8비트 마이크로프로세서인 Z80 프로세서를 위한 llvm 컴파일러 백엔드 프로젝트 입니다. 장기적으로 z80 백엔드 지원을 llvm 에 업스트림 하여 기여하는 목표를 가지고 있습니다. Spine ...
Beginning of the Ende (a community Deno fork) via @hongminhee https://lobste.rs/s/8ejwsp #javascript
https://blog.webb.page/WM-105
blog.webb.page
The trend of VC-backed tooling ending in abandonment rears its ugly head again. But hey, people gotta eat, right? The community will pick up the slack and steward the projects, right?