洪 民憙 (Hong Minhee) :nonbinary:'s avatar

洪 民憙 (Hong Minhee) :nonbinary:

@hongminhee@hollo.social

1,131 following1,649 followers

An intersectionalist, feminist, and socialist living in Seoul (UTC+09:00). @tokolovesme's spouse. Who's behind @fedify, @hollo, and @botkit. Write some free software in , , , & . They/them.

서울에 사는 交叉女性主義者이자 社會主義者. 金剛兔(@tokolovesme)의 配偶者. @fedify, @hollo, @botkit 메인테이너. , , , 等으로 自由 소프트웨어 만듦.

()

@fedify@hackers.pub

Fedify security updates: 2.0.36, 2.1.32, 2.2.21, 2.3.16, and 2.4.6

If you use an affected Fedify release, update now. These patches address six security vulnerabilities affecting Fedify and related packages. They fix two content-spoofing issues in backfill, an embedded-object origin-check bypass, and three denial-of-service issues caused by missing network deadlines.

The patched releases for the vocabulary, WebFinger, activity delivery, and NodeInfo issues are 2.0.36, 2.1.32, 2.2.21, 2.3.16, and 2.4.6. Update to the corresponding release on your minor line. The two @fedify/backfill issues affect the 2.3 and 2.4 lines and are fixed in 2.3.16 and 2.4.6. The security policy covers the latest two minor lines, 2.3 and 2.4. If you are still on a 1.x release, move to a supported 2.x release.

Update directly installed copies of the affected packages as well as @fedify/fedify, and check your lockfile for older transitive copies. If you generate custom vocabulary classes with @fedify/vocab-tools, update the generator, regenerate the classes, and rebuild your application before deploying. See the vocabulary documentation.

Embedded-object origin-check bypass with an anonymous parent (GHSA-r388-57j3-5fgp, medium, CVSS 3.1 5.3)

An attacker-controlled document can make a vocabulary accessor return a forged embedded object that claims to belong to another server, without fetching it from that server. The bypass requires a parent object without an id and a property repeated under its compact name and full IRI. A second decoding path skipped the origin check for that anonymous parent.

This can reach inbox listeners through a signed Create or Announce from an actor on the attacker's own server. It also affects backfill and application code that parses remote JSON-LD and reads embedded objects through vocabulary accessors. If the application stores or displays the returned content under its claimed ID, the result can be content spoofing or cache poisoning. A valid signature from the attacker's actor does not establish ownership of the forged object's ID.

Affected: @fedify/fedify, @fedify/vocab, and @fedify/vocab-tools on the 2.0–2.4 lines before the patched release above. The vocabulary bundled with @fedify/fedify 1.9 and 1.10 is also affected; no patched 1.x release is planned. Earlier 1.x releases lack this origin protection altogether and are not a safe downgrade.

Action needed: upgrade the vocabulary package, including any directly installed copy. If you use generated custom vocabulary classes, update @fedify/vocab-tools, regenerate the classes, and rebuild your application.

Until you can upgrade, fetch an accessor-returned object again by its ID with lookupObject() under the default origin policy before storing or displaying it, and use only the fetched copy. Apply this to nested objects and backfilled items too. Setting crossOrigin: "throw" does not close this bypass. Rejecting only top-level inbox activities without an ID is also insufficient: an activity with an ID can contain an anonymous nested object.

WebFinger lookups can stall without a deadline (GHSA-9pmv-w936-hj3f, high, CVSS 3.1 7.5)

A malicious WebFinger endpoint can hold requests open or respond slowly across redirects. Fedify limited the number of redirects but imposed no built-in deadline for the lookup. Repeated or concurrent lookups can occupy calling operations and reduce availability. This affects applications resolving attacker-controlled handles and can also be reached when re-fetching an unverified inbound activity falls back to WebFinger after a document-fetch failure. Reported by zx (manus-pi).

Affected: @fedify/webfinger on the 2.0–2.4 lines before the patched release above.

The patched implementation applies one 10-second deadline across DNS resolution, redirects, requests, and response-body reading for each WebFinger lookup. For non-portable actors, the initial lookup and alias verification share a single 10-second budget, with a limit of 100 raw subject/alias candidates.

Action needed: upgrade @fedify/webfinger and @fedify/vocab, including directly installed copies. A caller's cancellation signal can shorten the WebFinger deadline, but cannot extend it.

This does not put a 10-second limit on every lookupObject() call. In particular, the default document loaders on the 2.0–2.3 lines still have no built-in deadline, so a document fetch before or after WebFinger resolution can stall independently. Applications on those lines should enforce a separate deadline in their document loader or move to the patched 2.4 line.

Outbound activity delivery can occupy workers indefinitely (GHSA-fq5h-gjhp-g75x, high, CVSS 3.1 7.5)

A malicious destination inbox can accept a delivery and then stall the response or a redirect hop. Neither RSA-signed nor unsigned delivery had a total deadline. Concurrent deliveries to such inboxes can occupy workers and connections and delay delivery to other servers. Ed25519-only configurations are not the only ones affected. Reported by zx (manus-pi).

Affected: @fedify/fedify before the patched release on each branch above. The confirmed affected range for the unsigned redirect helper starts at 2.0.28; the signed-path issue predates that helper, so older releases should not be treated as safe.

The patched implementation gives each delivery attempt one 30-second deadline across connection setup, redirects, HTTP-signature retries, and response consumption. It does not reset the budget at each hop. A timeout before the final response is a retryable delivery failure. If an error response has already arrived, its status is preserved even if reading its body times out, so permanent failures are not turned into generic timeout retries.

Action needed: upgrade @fedify/fedify on both request-serving processes and delivery workers.

NodeInfo lookups can stall without a deadline (GHSA-64hq-2hgr-q4pm, medium, CVSS 3.1 5.3)

A malicious NodeInfo endpoint can delay discovery, redirects, or the document response and keep the calling operation waiting. The redirect-count limit did not bound the elapsed time. This affects application features that explicitly query attacker-influenced server URLs and the fedify nodeinfo command; inbound federation does not automatically trigger NodeInfo lookups. Reported by zx (manus-pi).

Affected: @fedify/fedify before the patched release on each branch above.

The patched client uses one 10-second default deadline across discovery and document fetching, including redirects and body reading. It also detects redirect cycles. A timeout or cancellation returns undefined.

Action needed: upgrade @fedify/fedify, and update any separately installed @fedify/cli used to query remote instances. See the CLI installation instructions. The API's timeout option is in milliseconds; timeout: null disables the deadline. Keep a bounded timeout for untrusted destinations. The CLI's -T/--timeout option is in seconds and defaults to 10.

On Node.js, NodeInfo DNS lookups are also limited to two concurrent OS resolver calls per process. An OS lookup already in progress cannot be cancelled and continues to occupy its slot until it finishes, even if the calling operation has timed out.

Backfill trusts forged cross-origin embedded content (GHSA-x58x-xx7h-7rh4, high, CVSS 3.1 7.5)

@fedify/backfill passed crossOrigin: "trust" to vocabulary accessors, bypassing their default origin checks. An attacker-controlled document could embed a Note, collection item, reply, or activity object with another server's ID, and backfill could return that embedded copy instead of fetching the genuine object. An application that persists results by ID could overwrite genuine content or poison its cache.

Affected: @fedify/backfill 2.3.x before 2.3.16 and 2.4.x before 2.4.6.

The patched implementation uses the default origin policy rather than trusting cross-origin embedded content. This may require additional fetches and can change which items are returned.

Action needed: upgrade @fedify/backfill to 2.3.16 or 2.4.6 and update @fedify/vocab to the matching patched version. The vocabulary fix above is needed as well; the backfill change alone does not close the anonymous-parent bypass.

Until you can upgrade, re-fetch backfilled items by ID with lookupObject() under the default origin policy before persisting them, and use only the fetched copies. Backfill results remain unverified remote data after the update; an origin check is not proof of authorship.

Backfill accepts forged IDs from custom document loaders (GHSA-h3jv-px69-2gpj, high, CVSS 3.1 7.5)

A custom BackfillDocumentLoader that fetches remote JSON and parses it directly with fromJsonLd() can lose the URL from which it retrieved the document. Before the fix, backfill could accept that parsed object's claimed ID even when it belonged to another origin. The attacker could supply a forged collection or post that the application then ingests under a victim server's ID. Reported by @z9mb1.

Affected: @fedify/backfill on the 2.3 and 2.4 lines before 2.3.16 and 2.4.6, respectively, when used with a custom loader that does not enforce retrieval-origin checks.

The patched implementation rejects a loader result whose ID origin differs from the requested IRI before caching or traversing it. Because BackfillDocumentLoader does not expose the final response URL, this check can also reject legitimate cross-origin redirects.

Action needed: upgrade @fedify/backfill and review your custom loaders against the backfill documentation. Prefer lookupObject() with the default origin policy to directly parsing fetched JSON. If you provide a custom JSON-LD document loader, preserve the final response URL in documentUrl so lookupObject() can perform its origin check. Do not turn untrusted remote JSON into vocabulary constructor values: constructor-supplied objects are treated as trusted local data.

Updating

Use the command for your package manager to install 2.4.6.

npm  install @fedify/fedify@2.4.6
yarn add     @fedify/fedify@2.4.6
pnpm add     @fedify/fedify@2.4.6
bun  add     @fedify/fedify@2.4.6
deno add jsr:@fedify/fedify@2.4.6

If you stay on another minor line, substitute 2.0.36, 2.1.32, 2.2.21, or 2.3.16 as appropriate. Update any direct dependencies on @fedify/vocab, @fedify/vocab-runtime, and @fedify/webfinger to the matching patched release. If you use @fedify/backfill, upgrade to 2.3.16 or 2.4.6 and update @fedify/vocab to the same version. If you generate custom vocabulary classes, update @fedify/vocab-tools, regenerate those classes, and rebuild your application. Check that your lockfile resolves the affected direct and transitive dependencies to patched versions, then redeploy all web and worker processes.

For a global CLI installed with npm, run the following command.

npm install -g @fedify/cli@2.4.6

For other installation methods, reinstall the corresponding patched version using the CLI installation instructions. Check fedify --version before using it against an untrusted instance.

Thanks to manus-pi for reporting issues. If anything unclear, comment below. Thanks.

github.com

manus-pi - Overview

Vulnerability Researcher. manus-pi has 5 repositories available. Follow their code on GitHub.
@hongminhee@hollo.social

JSConf JP 2026で登壇することになりました。11月22日(日)、東京のベルサール神田で開催されます。

タイトルは「Oseo:SBCLスタイルのJavaScript/TypeScript AOTコンパイラ」。SBCLやChez Schemeのように、動的型付き言語でありながらプログラム全体を事前にネイティブコードへコンパイルするJavaScriptエンジンを作っている、その話をします。TypeScriptの型注釈は最適化のヒントとして使うだけで、決して鵜呑みにしない。ヒントが嘘でも動作は変わらない。そんな設計の話です。

発表は日本語、30分枠、14:10からトラックCです。詳細はこちら。

https://jsconf.jp/2026/ja/talks/hong-minhee

会場でお会いできたら嬉しいです。

jsconf.jp

Oseo:SBCLスタイルのJavaScript/TypeScript AOTコンパイラ | JSConf JP 2026

Common LispのSBCLやSchemeのChez Schemeは動的型付き言語でありながら、プログラム全体を事前にネイティブコードへコンパイルし、何十年もプロダクションで使われてきました。一方JavaScriptは今なお、速く動くにはインタプリタと複数段のJIT、その上に載るデオプティマイゼーション機構が要る言語だと見なされています。この違いはどこから来るのか。この問いから始まったプロジェクトがOseoです。 Oseoはすべての関数を二重にコンパイルします。言語のフルセマンティクスを実装するジェネリックパスが一つあり、値の種類や形状に対して安価なランタイムガードを掛けられる箇所には、その隣に特殊化されたパスを並べます。ガードが失敗すれば、バイナリの中にすでにコンパイルされているジェネリックパスへ分岐するだけです。インタプリタへ落ちることも、デオプティマイズすることもありません。TypeScriptの型表記やJSDocはこの特殊化パスを選ぶヒントとして使われますが、決して鵜呑みにされることはありません。`any`や型アサーション、素のJavaScriptとの相互運用のせいで`: number`という表記はいつでも誤りうるので、Oseoはその可能性をガードで防ぎます。 この発表では、このアイデアが実際にどう動くのかをコードとバイナリで直接お見せします。Node.jsもDenoも使わず、V8が一切リンクされていない純粋なネイティブ実行ファイルがどう作られるか。`--dump-mir`と`--emit-c`で覗いた生成コードの中で、一つのガードが実際にどんな比較と分岐にコンパイルされるか。型ヒントが実行結果を変えてはならないという原則も、同じ領域にある別プロジェクトとの具体的な比較を通じて見ていきます。 Oseoはまだ完成したプロジェクトではありません。この発表は、これまでに証明できたことと、まだ残っている道のりを一緒にお見せする場でもあります。ネイティブI/O、ガベージコレクタ、セルフホスティングまで、システムプログラミングに関心がある方なら貢献できる余地がまだたくさんあります。

@hongminhee@hollo.social

今週の日曜日にJSConf JP 2026で発表するんだけど、スライドがまだ1枚もできてない。果たして無事に発表できるのか… 😱

jsconf.jp

Oseo:SBCLスタイルのJavaScript/TypeScript AOTコンパイラ | JSConf JP 2026

Common LispのSBCLやSchemeのChez Schemeは動的型付き言語でありながら、プログラム全体を事前にネイティブコードへコンパイルし、何十年もプロダクションで使われてきました。一方JavaScriptは今なお、速く動くにはインタプリタと複数段のJIT、その上に載るデオプティマイゼーション機構が要る言語だと見なされています。この違いはどこから来るのか。この問いから始まったプロジェクトがOseoです。 Oseoはすべての関数を二重にコンパイルします。言語のフルセマンティクスを実装するジェネリックパスが一つあり、値の種類や形状に対して安価なランタイムガードを掛けられる箇所には、その隣に特殊化されたパスを並べます。ガードが失敗すれば、バイナリの中にすでにコンパイルされているジェネリックパスへ分岐するだけです。インタプリタへ落ちることも、デオプティマイズすることもありません。TypeScriptの型表記やJSDocはこの特殊化パスを選ぶヒントとして使われますが、決して鵜呑みにされることはありません。`any`や型アサーション、素のJavaScriptとの相互運用のせいで`: number`という表記はいつでも誤りうるので、Oseoはその可能性をガードで防ぎます。 この発表では、このアイデアが実際にどう動くのかをコードとバイナリで直接お見せします。Node.jsもDenoも使わず、V8が一切リンクされていない純粋なネイティブ実行ファイルがどう作られるか。`--dump-mir`と`--emit-c`で覗いた生成コードの中で、一つのガードが実際にどんな比較と分岐にコンパイルされるか。型ヒントが実行結果を変えてはならないという原則も、同じ領域にある別プロジェクトとの具体的な比較を通じて見ていきます。 Oseoはまだ完成したプロジェクトではありません。この発表は、これまでに証明できたことと、まだ残っている道のりを一緒にお見せする場でもあります。ネイティブI/O、ガベージコレクタ、セルフホスティングまで、システムプログラミングに関心がある方なら貢献できる余地がまだたくさんあります。

@hongminhee@hollo.social

I released Optique 1.4.0, a type-safe CLI parser for TypeScript.

If your CLI has one main action and a few subcommands, you can now set a default command. For example, app src/main.ts can run the same action as app run src/main.ts, while app build still runs its own subcommand. No need to rewrite argv yourself.

https://github.com/dahlia/optique/discussions/1139

github.com

Optique 1.4.0: Default commands, Markdown references, and more focused help · dahlia/optique · Discussion #1139

Optique is a type-safe combinatorial CLI parser for TypeScript built from composable parser functions. Parser definitions drive runtime parsing, help and completion output, and the inferred value t...

@hongminhee@hollo.social

I have to show off this little flying squirrel. My spouse, @tokolovesme, drew it for Oseo, a new F/OSS project I've been spending a lot of time on lately.

The name Oseo comes from the Sino-Korean reading of 鼯鼠, which means “flying squirrel.”

The Oseo logo: a black silhouette of a flying squirrel seen head-on against a white background. It has rounded ears, four paws spread wide, two white curved eyes, and a white dot for a nose. Its tail curves down and to the right.
ALT text

The Oseo logo: a black silhouette of a flying squirrel seen head-on against a white background. It has rounded ears, four paws spread wide, two white curved eyes, and a white dot for a nose. Its tail curves down and to the right.

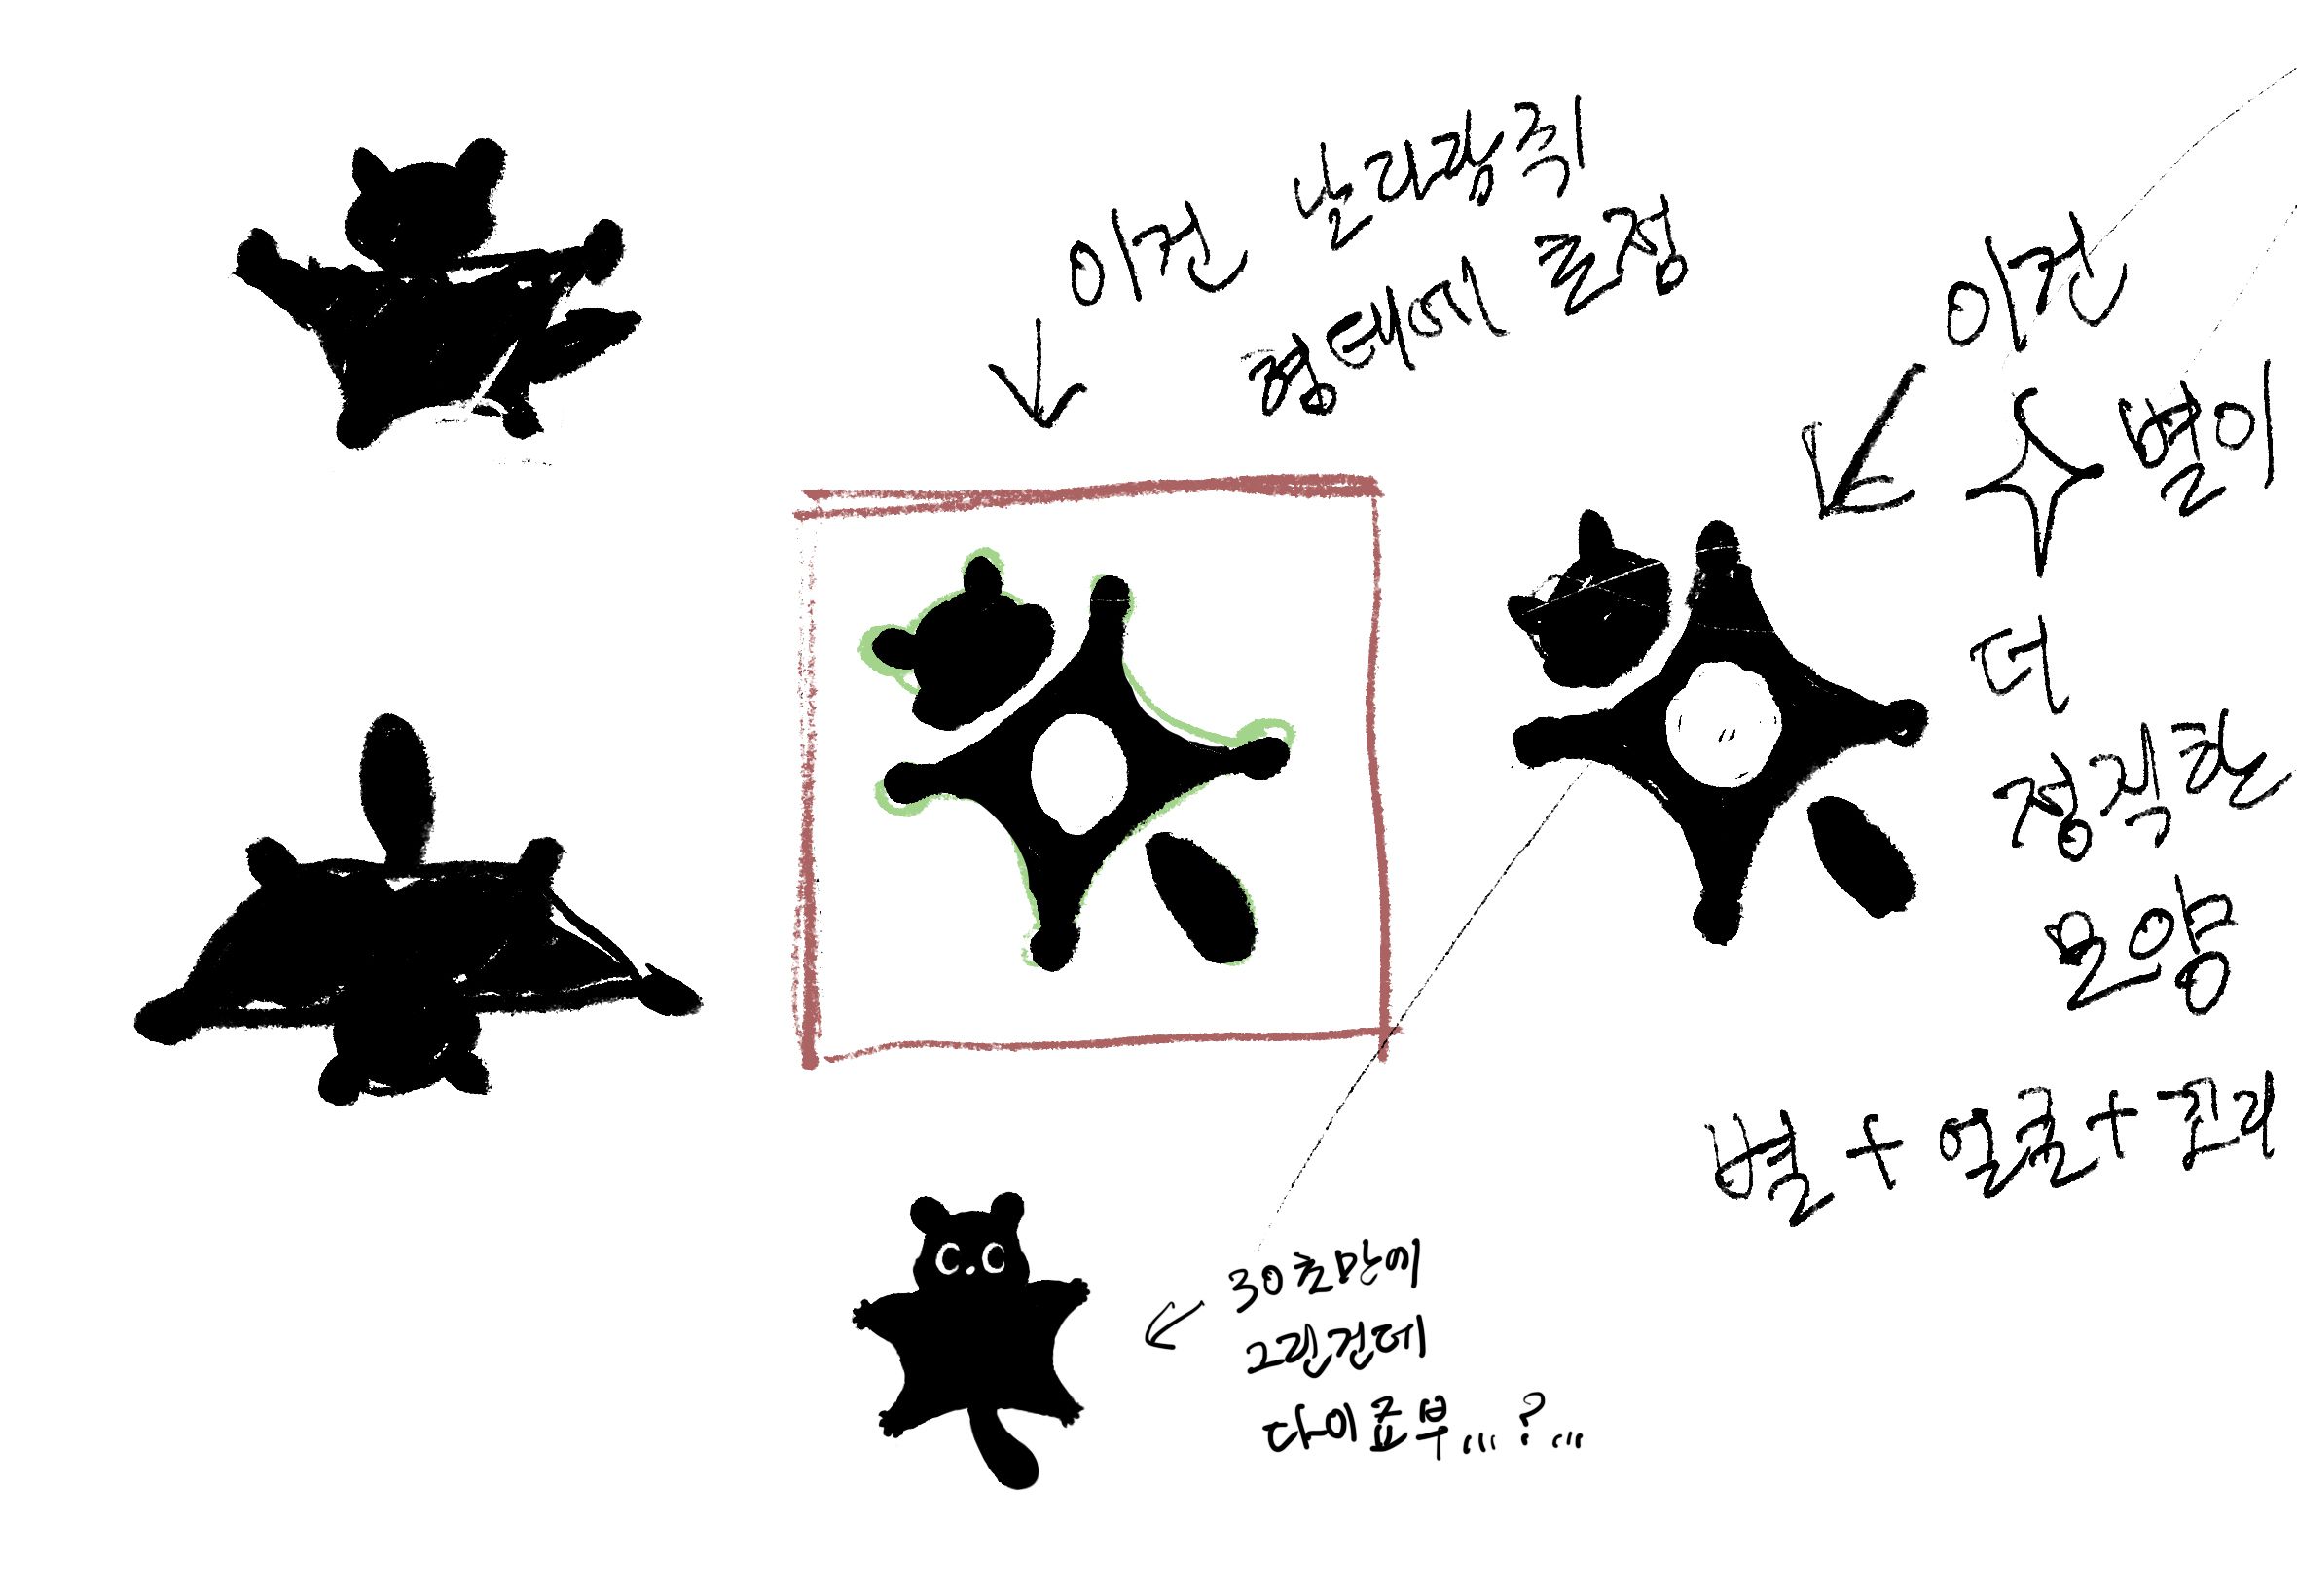
Five black flying squirrel sketches on a white page, with handwritten Korean notes and arrows. The center sketch, boxed in red and outlined in green, is labeled “this one focuses on the shape of a flying squirrel” (이건 날다람쥐 形態에 焦點). A similar sketch on the right has notes that read “this one is truer to the shape of  ✧ a star” (이건  ✧ 별이 더 正直한 模樣) and “star + face + tail” (별 + 얼굴 + 꼬리).

The small squirrel at the bottom became the logo. It has round ears, outstretched paws, white crescent eyes, a dot for a nose, and a curved tail. A note beside it reads, “I drew this in 30 seconds. Is it daijōbu (‘okay’ in Japanese) …?” (30秒만에 그린 건데 大丈夫[다이죠부]…?)
ALT text

Five black flying squirrel sketches on a white page, with handwritten Korean notes and arrows. The center sketch, boxed in red and outlined in green, is labeled “this one focuses on the shape of a flying squirrel” (이건 날다람쥐 形態에 焦點). A similar sketch on the right has notes that read “this one is truer to the shape of ✧ a star” (이건 ✧ 별이 더 正直한 模樣) and “star + face + tail” (별 + 얼굴 + 꼬리). The small squirrel at the bottom became the logo. It has round ears, outstretched paws, white crescent eyes, a dot for a nose, and a curved tail. A note beside it reads, “I drew this in 30 seconds. Is it daijōbu (‘okay’ in Japanese) …?” (30秒만에 그린 건데 大丈夫[다이죠부]…?)

@hongminhee@hollo.social

With Codeberg down, I can still read the Fediverse Enhancement Proposals (FEPs) on Codeberg Pages: https://fediverse.codeberg.page/fep/.

I can't clone the Git repo from Codeberg right now, though. I found a copy at https://github.com/social-web-foundation/fep, but it looks like it hasn't been updated in a while.

It got me thinking: it'd be nice to have a mirror for days like this. Maybe the existing GitHub copy could serve as the mirror, or one could live on another forge like @codefloe. Codeberg would still be the home for FEPs; the mirror would just give us somewhere else to clone from.

github.com

GitHub - social-web-foundation/fep

Contribute to social-web-foundation/fep development by creating an account on GitHub.

@Codeberg@social.anoxinon.de

codeberg.org is unfortunately down right now due to a yet undefined issue with our domain. It was not expired and not transferred, the domain is completely gone from our account and we did not receive any email notifications, and it is currently in the status clientHold. We are currently trying to contact our registrar to get more information right now & trying to resolve this issue, but this is probably going to take some time.

We are sorry for the inconveniences & are working on a solution.

@Codeberg@social.anoxinon.de

codeberg.org is unfortunately down right now due to a yet undefined issue with our domain. It was not expired and not transferred, the domain is completely gone from our account and we did not receive any email notifications, and it is currently in the status clientHold. We are currently trying to contact our registrar to get more information right now & trying to resolve this issue, but this is probably going to take some time.

We are sorry for the inconveniences & are working on a solution.

@pkgupdt@fedi1.pkgu.net

https://magicant.github.io/yash/

내가 interactive shell로 쓰고 있는 Yet Another Shell. 일본인 개발자가 만들어서, 다국어 지원이 잘 되어 있어서 쓰기 시작했는데, 쓸수록 좋다. 무엇보다 소규모 오픈소스 플젝에서 이렇게까지 자동화 테스트 코드가 있는 건 처음 본다. 숙련된 개발자가 소중하게 작성해 온 플젝. 무엇보다 곳곳에서 보이는 꼼꼼함이 맘에 든다. 나도 이런 코드를 남기면 좋겠다.

magicant.github.io

Yash: yet another shell - a POSIX command line shell

@Steve_Bate@mastodon.social
@dansup@mastodon.social

Fediverse Events + FediDB.

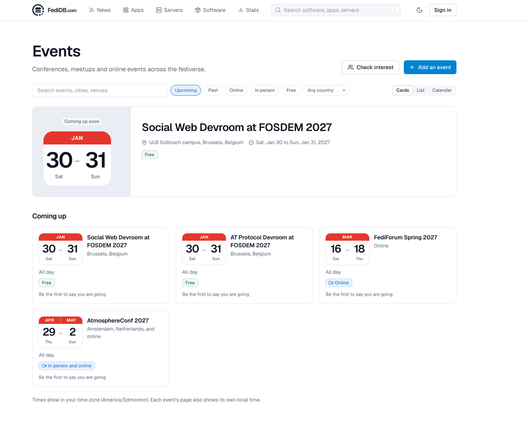
Imagine being able to plan a fediverse event (online, in-person or both) without a specific date or venue, and seek interested attendees that can indicate if they Will Attend or Maybe Attend, with a comment feed and the ability to send event updates to them via DM on FediDB.

All the pieces were there, I just needed to connect and polish them. Shipping soon!

FediDB events feature
ALT text

FediDB events feature

@_elena@mastodon.social

Good morning Fedi friends!

Routine reminder that the at is accepting proposals for talks.

There are two available formats: 25 minutes and 8 minutes.

More details are available here:
🔗 : lists.fosdem.org/hyperkitty/li

⏳ The submission deadline is November 27. Acceptance notifications come soon thereafter, on December 1.

📝 You can submit your proposal here: pretalx.fosdem.org/fosdem-2027

I'll be working on my proposal this week 🤗

pretalx.fosdem.org

FOSDEM 2027

Schedule, talks and talk submissions for FOSDEM 2027

@kizu@front-end.social

New blog post: “Cursors”.

blog.kizu.dev/cursors/

In which I take a cursory glance at a victory that CSSWG did hand out to us in this pointless debate about if buttons have more in common with blank space compared to links.

blog.kizu.dev

Cursors

In which I take a cursory glance at a victory that CSSWG did hand out to us in this pointless debate about if buttons have more in common with blank space compared to links.

@socialcg@w3c.social

A new draft report from the Community Group is now available: "Seek Item".

It defines a new (optional) endpoint that ActivityPub API clients can use to efficiently access a page in an OrderedCollection that contains a specific item, such as the one the client has last seen. This can improve efficiency and responsiveness of ActivityPub clients.

swicg.github.io/activitypub-ap

swicg.github.io

Seek Item

@hongminhee@hollo.social

The three of us who maintain Fedify (@z9mb1, @2chanhaeng, and I) have all submitted proposals to the Social Web devroom at FOSDEM 2027. I wonder how many of us will get to give a talk. I'll probably talk about implementing portable objects (FEP-ef61) in Fedify, @z9mb1 will cover how Fedify has evolved over the past year and what lies ahead, and @2chanhaeng will talk about DrFed.

drfed.org

DrFed — The ActivityPub debugging platform

DrFed is a web-based platform for developing and debugging ActivityPub implementations, built by the team behind Fedify.

The quoted post is hidden while awaiting the author's approval.

@hongminhee@hollo.social · Reply to Samuel Brinkmann

@sabrinkmann @Floppy Two directions I know of. If a hosted service is fine, something like Sentry. For self-hosting, SigNoz is the only F/OSS option I know with easy OpenTelemetry ingestion; I don't know what else is out there. It has a paid cloud version too.

I think Sentry used to have an F/OSS edition. I'm not sure it still exists, or whether it accepts OTLP though.

signoz.io

SigNoz | The Open Source Datadog Alternative

SigNoz Cloud is a one-stop observability tool built on top of OpenTelemetry. Get APM, logs, traces, metrics, exceptions, AI observability & alerts in a single tool.

@hongminhee@hollo.social

ChanHaeng Lee (@2chanhaeng), one of the @fedify maintainers, is asking the which of his two projects he should present in the Social Web devroom at @fosdem 2027.

@drfed is an debugging tool that he is building with @z9mb1, @gaebalgom, and me. fedi.blue (https://fedi.blue) is a library for servers that interoperate over both ActivityPub and the AT Protocol. Both would make good talks, which is why I would rather the audience picked.

The poll closes on 13 November 2026, so vote for the one you would rather sit through. has three maintainers now, and all three of us are going to 2027 and submitting proposals to the devroom. (The CFP is open until 27 November 2026 if you have a talk of your own.)

fedi.blue

Hello, world

The quoted post is hidden while awaiting the author's approval.

@2chanhaeng@hackers.pub

Hello, Fediverse! I’m trying to decide what topic to present at FOSDEM 2027 – Social Web Devroom. Which of these two would you be more excited to hear about?

  • DrFed: DrFed is an ActivityPub debugging tool that @hongminhee, @z9mb1, @gaebalgom, and I are building as a team.
  • fedi.blue: fedi.blue is a library for building servers that interoperate with the ActivityPub and AT protocols.
  • DrFed: ActivityPub Debugging Tool1 (100%)
  • fedi.blue: Bridge between AP & AT Protocol0 (0%)

fedi.blue

Hello, world

@geeknews@mastodon.social

국내 오픈소스 소액 지원 사업 'FOSS for All Microgrants 2026' 수혜 프로젝트 5곳

FOSS for All이 올해 처음 진행한 기부금 모집 및 분배 사업에서 지원한 13개 프로젝트 및 커뮤니티 중 5곳을 선정했습니다. 각 프로젝트에 소액 지원금을 전달할 예정입니다.

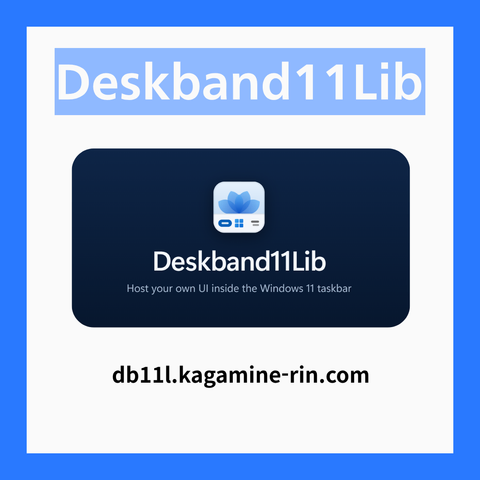
선정된 프로젝트는 Z80 프로세서용 LLVM 백엔드 llvm-z80, 요청 처리 과정을 명시적으로 드러내는 Go 웹 프레임워크 Spine, Windows 11 작업 표시줄에 위젯을 넣는 Deskband11Lib, PDF로 제본용 소책자를 만드는 HornPenguin Booklet, 국한문혼용체를 한글로 변환하는 Gukhanmun입니다.

news.hada.io/topic?id=36847

@hongminhee@hollo.social

I've been carrying around an idea for a federated code forge for a while. Two things sharpened it recently: Tangled's post on the federated code forge, which builds a forge on the AT Protocol, and a Jujutsu workshop (Korean) by Seongmin Lee (@boltless.me), who works at Tangled, held at @turingappledev.

My version would build on ForgeFed, the protocol for code forges (spec), so that repositories, issues and merge requests federate the way posts already do. The idea is early enough that I haven't even come up with a codename. What I want from it, roughly:

  • Git and Jujutsu (so-called jj) as equal clients. Not Git hosting with Jujutsu support bolted on, but a forge that understands both, so what Jujutsu is actually good at, stacked changes, becomes a first-class unit of review instead of a pile of separate pull requests.
  • No owner layer. Since the point is federation, one instance represents one person or one organization, permissions are managed per server, and a repository lives at forge.example/myrepo instead of forge.example/owner/myrepo.
  • A migration path off GitHub that keeps the history. Importing the code is easy; importing the issues, pull requests and discussions with their original authors attached is the part that matters. I'd keep a placeholder for each GitHub account and let whoever owns that account prove it, after which the instance swaps in their fediverse actor, so attribution carries over. How to express that claim in ActivityPub is the part I haven't figured out. It may need a new FEP.

Where this stands: I haven't read the whole spec, Fedify doesn't ship the vocabulary yet (fedify-dev/fedify#751), and I have too much else going on to start soon. If you've run a forge or implemented ForgeFed, I'd like to hear whether any of this makes sense.

github.com

@fedify/forgefed package for ForgeFed vocabulary support · Issue #751 · fedify-dev/fedify

Background ForgeFed defines an ActivityPub federation protocol for software forges such as Gitea and Forgejo. The spec adds forge-specific actor types (Repository, TicketTracker, PatchTracker, Proj...

@fossforall@mastodon.social · Reply to FOSS for All

다음 편에서도 Microgrants에 지원한 오픈소스 프로젝트들을 이어서 소개할게요.

더 많은 한국의 오픈소스 이야기가 궁금하다면, FOSS for All을 팔로우해 주세요! 🌱

@fossforall@mastodon.social

우리가 만난 오픈소스 프로젝트들 ① 🌱

한국의 오픈소스 문화가 무럭무럭 자랄 수 있도록, FOSS for All Microgrants가 시작되었어요.

2026년 Microgrants 사업에 함께한 국내 오픈소스 프로젝트·커뮤니티를 만나보세요!

(아래에 계속! 👇)

@hongminhee@hollo.social

커피를 못 마시긴 하지만, 커피챗은 언제나 歡迎(환영)입니다! 專業(전업) F/OSS 開發(개발)이나 F/OSS 프로젝트로 STF나 NLnet 같은 公的(공적) 資金(자금) 받는 要領(요령)에 關心(관심) 있으시면 DM이나 이메일로 聯絡(연락) 주세요! 꼭 저런 主題(주제)가 아니더라도 소프트웨어 開發(개발) 全般(전반)이나 漢字(한자)·國漢文(국한문)混用體(혼용체) 等(등) 多樣(다양)한 主題(주제)도 좋습니다.