Hashtag

#GitHub

1,427 posts tagged with this hashtag.

@pooza@mstdn.b-shock.org
:capsicum: capsicum 2.2

◇ 公開状況

・全5プラットフォーム(Android, iOS, Windows, macOS, Linux)で公開済み

◇ 変更点
github.com/pooza/capsicum/rele

・デッキUI
タブUI同様のハンバーガーメニュー(ドロワー)を設置。(アカウントが切り替わらない。2.3で対応)
カラムのロックに対応。うっかり閉じることがない様に。

・Mastodon / Misskeyの本来機能の追従
スレッド単位のミュート。
ブースト/ リノートのミュート。
Mastodonのタグタイムラインで、従来のANDだけでなく、ORとNOTにも対応。

・デスクトップ通知
アプリを落としたり、回線が切れていた間に届いた通知を3つまで表示。
プッシュ通知にはもともとある機能なので、これは主にLinux版用。

・ナウプレ
macOS版、アートワーク取得の改善。

・その他
フォント指定、投稿欄以外の大きなテキストボックスにも反映するように。
ツールチップがないボタンがけっこう残っていたので、修正。
等など

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・2.3
github.com/pooza/capsicum/mile
デッキUI ドロワーのアカウントが切り替わらない不具合の修正
フィルタ(ワードミュート)の設定画面
予約投稿 時刻を変更できない不具合の修正(Mastodon Misskey共)
ナウプレ macOS版Spotify対応
モロヘイヤ メディアカタログ対応
などなど

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org

capsicum 2.1にて、ナウプレのアートワークに対応しています。

github.com/pooza/capsicum/issu

macOS版は、2.1の審査がまだ通っていません。一両日ぐらいだと思います。

TheDesk側でもアートワーク機能の改善が進み、特にお困りでもない様ですが、よかったらこちらもお試しください。
一応この改善も、とねぢさんが利用することを想定して前倒しした対応ではありますw
@toneji

github.com

ナウプレ投稿に再生中の曲のアートワーク(ジャケット画像)を添付できるようにする · Issue #1133 · pooza/capsicum

ナウプレ投稿に、再生中の曲のアートワーク(ジャケット画像)を capsicum 自身が添付できるようにする。 報告: https://minohdon.jp/@toneji/117260519123243068 (「capsicum では、ナウプレにどうやって画像を添付するのかな?」) 背景 他クライアント(TheDesk)のナウプレを常用していた層が、macOS での行き先を探している状況...

@pooza@mstdn.b-shock.org
:capsicum: capsicum デッキUI

◇ 2.1での改善
以下どちらも、ご要望由来です。
これらの修正で、デッキUIはだいぶ実用的になったと思います。

最後に見ていたカラムと、デッキ / タブ UI のどちらを開いていたかを覚える
github.com/pooza/capsicum/issu

見たいカラムへ 1 回で飛べる帯を置く
github.com/pooza/capsicum/issu

◇ 2.2での改善(予定)
個人的に、なるべくデッキUIで生活するということをしばらく続けていました。
以下の機能が、ピースとして足りないと感じました。2.3で対応予定。

常設のカラムをうっかり閉じないよう、カラムをロックできるようにする
github.com/pooza/capsicum/issu

メニューバーの無い端末で、ドロワーにある機能へ届かない
github.com/pooza/capsicum/issu

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@pooza@mstdn.b-shock.org
:capsicum: capsicum 2.1

◇ 公開状況

・iOS, Android, Windows, Linux 公開済み
・macOS 前バージョン(2.0.1)の審査中

◇ 変更点
github.com/pooza/capsicum/rele

設計時に2.0に含めなかった諸機能、利用者様からのフィードバックに対応。

・デッキUI
画面幅のない端末(スマホ)でも、カラムを素早く移動できるショートカットのナビゲーション追加。
各カラムに△▽ボタン追加。
最後に開いていたカラムと、デッキUI/タブUIを保存するように。
`ctrl+[`, `ctrl+]` (macOSはcmd)キーで左右のカラムに移動。
「すべてを通知」カラムが複数表示される不具合を修正。
デッキUIから設定画面を開ける導線追加。

・ナウプレ
モロヘイヤがない環境でもアートワークを追加。

・レイヤー
改行を含む複数行の文字列を乗せた場合に、左右・中央寄せの寄せを選べるように。

・絵文字ピッカー
検索キーワードが、カスタム絵文字・Unicode絵文字・劇中ワードで共有されるように。

・等など

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

2.0の棚卸しでわかった、Mastodon・Misskeyでの未実装機能等を淡々と消化します。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to ぷーざ
:capsicum: capsicum 2.0.1

◇ 公開状況

・iOS 審査提出済み
・macOS 2.0.1審査提出済み 2.0.0未公開
・Android, Windows, Linux 公開済み

◇ 変更点
github.com/pooza/capsicum/rele

デスクトップ通知が全く表示されないケースへの対応。
プッシュ通知がないLinuxでは、デスクトップ通知は唯一の通知経路なので緊急性そこそこ高かったです。

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・2.1
github.com/pooza/capsicum/mile
デッキの残り

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@toxi@mastodon.thi.ng · Reply to Daniel Schildt

@autiomaa Github stars have become completely commercialized already years ago. (IIRC between 2019-21) I remember getting numerous emails about purchasing stars and forks to help my projects' visibility/credibility/importance, the same way some people are purchasing fake followers/engagement on IG/Twitter etc.

This all coincided with other major disappointing reveals around open source from former peers. Seeing how FLOSS culture has been co-opted by (not just new) people who share nothing of the same ideals or social contracts and are using opensource purely as mechanism for quick personal advancement/enrichment (e.g. setting up and heavily promoting short-lived projects just to improve their big tech job interview chances) was one of the biggest disappointments of my life, and one from which I'm still only slowly recovering...

@pooza@mstdn.b-shock.org
:capsicum: capsicum 2.0

◇ 公開状況

開発期間が、足かけ3週間に及んだメジャーアップグレードです。

・iOS 審査提出済み(TestFlightのみ公開済み)
・macOS 審査提出済み
・Android, Windows, Linux 公開済み

◇ 変更点
github.com/pooza/capsicum/rele

・デッキUI(マルチカラム)
複数のアカウントを、1画面で網羅・横断できます。

・プッシュ通知
プリセットサーバー(本来の対象サーバー)のアカウントを持たないユーザーにも、有償にて提供。(200円/月)
iOS, Androidのみで、Windowsは未対応。
また、購入有無に関わらず、モロヘイヤ未インストールのMisskeyはプッシュ通知対応になりません。

・画像エディタのレイヤー対応
スタンプや文字乗せで、それぞれの要素をレイヤーとみなし、各レイヤーの表示優先順位や透明度を設定できるように。

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・2.1
github.com/pooza/capsicum/mile
デッキUIの積み残し。
ナウプレのカバーアート対応。capsicum単独で動作、モロヘイヤ不要。
レイヤー対応、任意の画像ファイルのレイヤー化
等など。だいぶ盛り気味なので、いくつか先送りの可能性あり。

・2.2
github.com/pooza/capsicum/mile

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@smallcircles@social.coop · Reply to 🫧 Social coding commons
@pooza@mstdn.b-shock.org
:capsicum: capsicum 2.0.0 クローズドベータ

◇ 公開状況

・iOS TestFlight審査中
・Android クローズドベータ審査中

ストア版と大きく異なるバージョンが、一部のテスターに配布されます。能動的にテストにご協力頂く場合にのみ、ベータ版をご利用ください。
また、私のサーバーのメンバーで、テストにご協力いただける方はお声がけください。

◇ 変更点
・デッキUI(マルチカラム)
今回のメイン。

・外部のユーザーにも、プッシュ通知を提供
月額200円での提供を予定。私のサーバーのメンバーには引き続き無償提供。
なお、Misskeyでのプッシュ通知を有効にできるのは、引き続きモロヘイヤインストール済みサーバーのみ。これはMisskey側の制約。

・添付画像エディタのレイヤー処理
文字やスタンプに対して、透明度や表示優先度等の設定できる。
任意の画像ファイルをレイヤー化する修正は、近日対応。

・等など、大量の修正。
最終的には、大小100issueを超える見込み。

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・2.0.0
github.com/pooza/capsicum/pull

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@hugovk@mastodon.social · Reply to Seth Larson
@githubchangelog@mastodon.social
@sethmlarson@mastodon.social

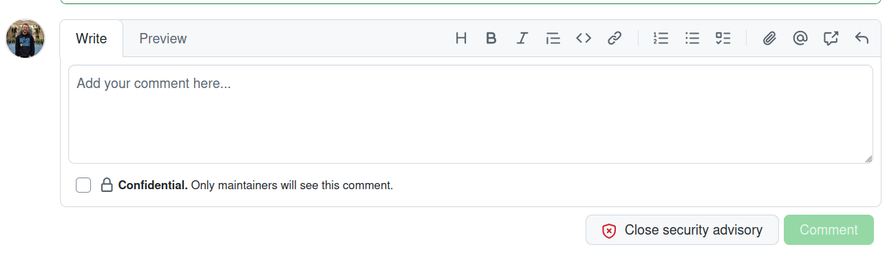
GitHub Security Advisories added a new feature: "Confidential Comments"! 🥳

This is both an awesome feature in general (no more having multiple channels for each report 🎉) and is hopefully a sign that more development on this critical feature will be coming soon.

A checkbox below the comment box in a GitHub Security Advisory labeled "Confidential. Only maintainers will see this comment."
ALT text

A checkbox below the comment box in a GitHub Security Advisory labeled "Confidential. Only maintainers will see this comment."

@pintoch@mamot.fr

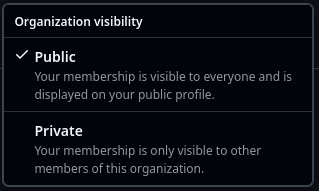
If your membership to an open source project isn't public on or , it's because

  • you didn't think about it / take the time to do it3 (60%)
  • you want to keep it hidden - let me know why!2 (40%)
screenshot of GitHub's visibility settings for org membership, with options "Public" (your membership is visible to everyone and is displayed on your public profile) and "Private" (Your membership is only visible to other members of this organization).
ALT text

screenshot of GitHub's visibility settings for org membership, with options "Public" (your membership is visible to everyone and is displayed on your public profile) and "Private" (Your membership is only visible to other members of this organization).

@pooza@mstdn.b-shock.org
:capsicum: Firebase 障害

本日、多数のiOSアプリが起動直後に終了する事象が発生している様です。
capsicum は影響を受けません。原因とされる解析SDK (Google Analytics for Firebase)を組み込んでいないためです。

iOS 版は通知も自前のリレーサーバー経由で APNs に直結しており、起動経路に外部の解析コードが入りません。
Android 版が通知配信に使っている Firebase Cloud Messaging は本日の事象とは別系統で、配信状況を確認しましたが異常はありませんでした。
引き続き平常どおりご利用いただけます。

◇ 調査の結果、起票されたIssue
github.com/pooza/capsicum/issu

◇ 近況
capsicum 2.0の開発進捗は、体感で7割というところ。
主要機能はほぼ動作していて、事務手続きもあとわずか。
10月中には確実にリリースできるだろうと思っています。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@forest_watch_impress@rss-mstdn.studiofreesia.com
@w3cdevs@w3c.social

📢 Two of @w3c’s most commonly used IRC bots, RRSAgent and Zakim, are now open source. These bots have assisted over 60,000 meetings at W3C over the past 25 years! 😊🎉

▶️ w3.org/blog/2026/w3c-irc-bots- - by @gerald

Zakim is for agenda and queue management and RRSAgent for recording minutes. Their code and issue trackers are on :
- github.com/w3c/zakim
- github.com/w3c/rrsagent

👇From a T-shirt designed by @karlcow to thank W3C group chairs back in 2008!

Two designed robots representing W3C's IRC bots: on the left, Zakim (in green, raising a hand for queue management) and on the right, RRSAgent (in blue, recording minutes).
ALT text

Two designed robots representing W3C's IRC bots: on the left, Zakim (in green, raising a hand for queue management) and on the right, RRSAgent (in blue, recording minutes).

@pooza@misskey.delmulin.com
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.66

◇ 公開状況

・全5プラットフォーム(Android, iOS, Windows, macOS, Linux)で公開済み

◇ 変更点
github.com/pooza/capsicum/rele
github.com/pooza/capsicum/rele Windows版のみ

・リプライの宛先
メンションに含まれる全員を、宛先に含めるように。

・プッシュ通知(Windows版)
容量の大きな通知が捨てられ、ユーザーに届かないケースに対応。

・などなど

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・2.0
github.com/pooza/capsicum/mile
デッキUI(マルチカラム)を含めた、全体の開発進捗は3割程度です。
ぷーざが管理するサーバー以外のユーザーに対しても、少額にて、プッシュ通知や通知サーバーを開放の予定。
その他、基本設計にまで及ぶ多くの改善を予定。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@pooza@mstdn.b-shock.org · Reply to 鴉河雛
@release_bot@mstdn.b-shock.org
@jacksonchen666@micro.jacksonchen666.com

FYI: if you participated in a project (made issues/PRs/comments) that has moved from github to codeberg (or to any forgejo instance), you can sign into codeberg using github, and then link your codeberg with your github, so that migrated issues/PRs/comments are linked to your codeberg account (instead of github) on codeberg!

go to settings > security > scroll to linked accounts to link your github/gitlab to codeberg, and then link your github account

you can unlink after and codeberg will keep it attributed to your codeberg, but it won't apply automatically to future project migrations

(this advice applies to projects previously on github, which migrated using codeberg/forgejo's migration feature which copies issues/PRs over)

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.65

◇ 公開状況

・全5プラットフォーム(Android, iOS, Windows, macOS, Linux)で公開済み

◇ 変更点
github.com/pooza/capsicum/rele

不具合修正中心です。
1.xの間に処理しておきたい修正を詰め込んだつもりが、載せきれなかった課題も少しだけあります。

2.0の開発が始まりましたので、1.xと2.0が並走していない体制での最後のバージョンとなります。

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・2.0
github.com/pooza/capsicum/mile

2.0の大まかな設計からIssue起票にかけての準備がおわり、実装に着手しています。
デッキUI(マルチカラム)は手元では一部の機能が動き始めています。

当面は引き続き、2.0のリリース前に解決すべき課題があった場合にのみ、新バージョンのリリースを行います。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to とねぢ @Minoh-don(piano.piano)
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.64

◇ 公開状況

・全5プラットフォーム(Android, iOS, Windows, macOS, Linux)で公開済み

◇ 変更点
github.com/pooza/capsicum/rele

・「削除して再編集」
In-Reply-Toなど、元投稿から引き継がれていない項目があった。
Mastodon / Misskey本来の動作通りに修正。

・Linuxで、キーリングが停止している場合
キーリングが停止している場合に、アプリが動作しない等、複数の不具合があった。これを修正。

・Androidで、ログインが完走できない場合
ログイン実行中に他アプリを開いた場合に、実際にサーバー側ではログインできているにもかかわらず、capsicumに戻ってこれない場合があった。
(パスワードの確認のために、外部のパスワード管理ツール(Bitwarden等)を開く場合などが典型的なケースとして該当)
これを修正。

・等など

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

メジャーアップグレード2.0を準備中。
このため当面は、脆弱性等への緊急性の高い修正や、ユーザー要望にのみ対応します。
こちらから能動的なリリースは行いません。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@autoweirdfm@det.social
@smallcircles@social.coop · Reply to Baldur Bjarnason

@baldur @u0421793

I think its not as much that are gatekeeping, but more that work processes don't integrate well, or at all. To the benefit of the devs, who deliver the software at the end of the pipeline.

At the start of my career I worked at the largest Print company in Europe (now bankrupt) and we created several award-winning dynamic websites. At the time wasn't a thing, but Interaction Design was and it was leading. It was also a time when we didn't have 'agile', and didn't have where everything is either an Issue or a PR. There were waterfall processes, and on the agile side you later had things like (Rational Unified Process). These acknowledged specifally different IT roles and different stages in the overall development lifecycle.

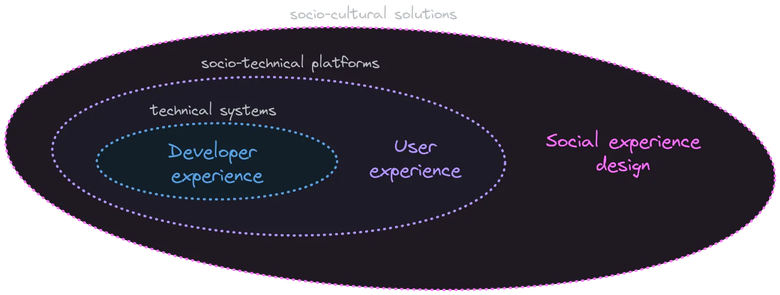
For Social experience design, , I got inspired by RUP when defining the (the Free software development lifecycle, or Fediverse solution delivery lifecycle, depending on context). See:

coding.social/blog/reimagine-s

A diagram that depicts the scope of SX as three expanding elipses. Innermost is Developer experience (DX) which is suitable to work with and create technical systems. Surrounding it is User experience (UX), which includes DX in our scope definition, and allows us to deliver socio-technical platforms. Outermost elipsis is Social experience design (SX) that holistically emcompasses both DX and SX and allows us to create socio-cultural solutions. SX takes us from individual needs, via inter-personal relationships, to leaving societal imprint.
ALT text

A diagram that depicts the scope of SX as three expanding elipses. Innermost is Developer experience (DX) which is suitable to work with and create technical systems. Surrounding it is User experience (UX), which includes DX in our scope definition, and allows us to deliver socio-technical platforms. Outermost elipsis is Social experience design (SX) that holistically emcompasses both DX and SX and allows us to create socio-cultural solutions. SX takes us from individual needs, via inter-personal relationships, to leaving societal imprint.

@pooza@misskey.delmulin.com
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.63

◇ 公開状況

・全5プラットフォーム(Android, iOS, Windows, macOS, Linux)で公開済み

◇ 変更点
github.com/pooza/capsicum/rele

・通知タブ、「すべての通知」画面
停止中サーバーからのフォロー通知が含まれている場合、処理が長時間とまっていた。
元サーバーへの問い合わせについて、タイムアウト秒数を短縮。

・CWのタイトルにハッシュタグが含まれていたら
タップしたらタイムラインに遷移できるように。(独自機能)
元々WebUIに要望されていた機能だが、Mastodonで実装を断念した経緯あり。

2.0に向けて、Mastodon / Misskeyの本来機能を棚卸ししました。
その結果、1.xのうちに対応したほうがよいと判断された機能を、先行で実装しました。
以下、主なもの。

・ブロック・ミュートの管理
・フォローリクエストの管理
・フォロー中ハッシュタグの管理(Mastodon)
・投稿に対する、引用者の一覧
・投稿に対する、お気に入り者の一覧(Mastodon)
・等など

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

現在、デッキUI(マルチカラム)等の大型機能を含む、2.0の設計を進めています。
棚卸しで発見された、2.0のリリース前に片付けるべきと判断されたissueを含むリリースが、もう2〜3ぐらい続く予定。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@githubchangelog@mastodon.social
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.62

◇ 公開状況

・全5プラットフォームで公開済み

◇ 変更点
github.com/pooza/capsicum/rele

・画面の下端がナビゲーションバーに潜る
スクロール可能な量を増やしました。
スレッド画面では、上下ボタンともかぶっていました。

・等など

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

現在は2.0リリース前の準備期間にあたるメンテナンスモードですが、1.xむけの残issueが意外と多く発生してます。

・1.63
github.com/pooza/capsicum/mile
2.0着手前の棚卸しとして行った調査で、1.xの間に対応すべきと判断された、MastodonやMisskeyの既存機能。

・1.64
github.com/pooza/capsicum/mile
1.xの間に対応すべきと判断された不具合など。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@hugovk@mastodon.social

hugovk.dev

Help test Python 3.15!

@hugovk@mastodon.social · Reply to Hugo van Kemenade

🐍🚀 Out now: final Python 3.15 release candidate!

It's your last chance to say that YOU helped test 3.15 before the big day on 1st October!

How?

💡 Try out the new features
💡 Try your project with it
💡 Add 3.15 to your CI
💡 Library maintainer? An extra task for you: upload wheels to PyPI, especially binary wheels
🐞 Report bugs!

discuss.python.org/t/python-3-

In return?

😎 Join the cool testers' club!
🦥 Lazy imports
🧊 frozendict
💂 sentinel
🏎️ Tachyon
🫶 and much, much more!

discuss.python.org

Python 3.15.0 candidate 2 is here!

It’s the final 3.15 release candidate! This is a candidate preview of Python 3.15 This release, 3.15.0rc2, is the final planned candidate release, containing around 144 bugfixes, build improvements and documentation changes from 76 contributors since 3.15.0rc1. Entering the release candidate phase, only reviewed code changes which are clear bug fixes are allowed between this release candidate and the final release. The next release of Python 3.15 will be 3.15.0 final, scheduled for 2026-10-...

@bkuhn@copyleft.org

I'm quoted in re: 's likely acquisition of 🤗Inc:

fastcompany.com/91597304/nvidi

However, that says that is currently a “neutral platform”.

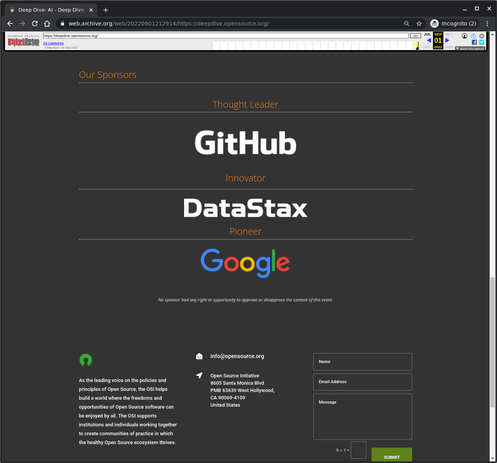
Sadly, Initiative (even after 's acquisition) considers a “thought leader”¹ in framing OSI's LLM-gen-AI policy. But I still hope against hope OSI would drop their decades-long position that “we ❤️ companies that proprietarize non-copyleft ”. 😩

¹ web.archive.org/web/2022090121

A screen shot of https://web.archive.org/web/20220901212914/https://deepdive.opensource.org/ lists Open Source Initiative sponsors for its work on LLM-gen-AI.  The top sponsor is identified as their “Thought Leader”.  The GitHub text-logo appears as the thought leader.
ALT text

A screen shot of https://web.archive.org/web/20220901212914/https://deepdive.opensource.org/ lists Open Source Initiative sponsors for its work on LLM-gen-AI. The top sponsor is identified as their “Thought Leader”. The GitHub text-logo appears as the thought leader.

Ach wie schön, man kommt aus dem Urlaub zurück und stellt fest, das der gesamte Account gesperrt ist.

Repositories, wie z.B. github.com/jedie/django-revers sind offline und zeigen nur ein 404...

Alles weg, nur 404. (Hab natürlich backups, lokale Klone und automatisierte Klone in einem privaten )

Hab nicht einmal eine EMail bekommen, mit irgendeinem Hinweis.

@github

Screenshot über "Account suspended" von Github...
ALT text

Screenshot über "Account suspended" von Github...

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.61

◇ 公開状況

・全5プラットフォームで公開済み

◇ 変更点
github.com/pooza/capsicum/rele

メンテナンスモードに移行して、最初のリリースです。

・プレビューカードのサイズ
OGPの取得成否やサムネイル有無に関わらず、同じ大きさに。
タイムラインで上方向に戻るとき、スクロール量の計算が狂わないように。

・プレビューカードをタップ時のリンク先
GooglePlay宛てのリンクがcapsicum内ではなく、WebUIへのものだった。
リンクをタップしたときのルーティングは、アプリ内のあらゆるリンクで同一の処理であるべき。

・等など

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

現在は、2.0のリリース前にあたるメンテナンスモードですので、直近の予定はありません。
2.0の設計を進める中で、1.xの間に消化すべきと判断された課題のみ、当面のリリースに含まれます。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@hugovalters@mastodon.social

Most CVE APIs hide their data lag. We ship it. Every response returns pending_fields — exactly which fields NVD hasn't processed on that CVE yet. Every plan. NVD + KEV + EPSS + exploit tracking + detection rules, one call.
10 real CVEs, no signup: valtersit.com/cve/pricing/

@pooza@misskey.delmulin.com · Reply to ぷーざ@ダイスキー

今朝、2時間ちょっと調査した上での進捗です。
特定にまでは足りてないが、かなり確度の高い原因を特定しました。とても手こずりましたけどw

こちらがいま考えている理由は、プレビューカードの高さが、読み込みの進捗によって頻繁に変わることです。
プレビューカードは文字と画像を持ちうることもあり、高さが動的に変わる可能性があります。

https://github.com/pooza/capsicum/issues/1032
https://github.com/pooza/capsicum/issues/1033

Misskeyで、タイムラインにプレビューカードを表示する対応は割と新しめの更新です。
このときから頻繁に発生するようになったと考えられます。
https://github.com/pooza/capsicum/issues/772

併せて、文字だけのプレビューカードの幅が狭くなる問題も対応します。
(気づいてはいたが、そのうち直すつもりだった)

@capsicum@pf.korako.me

github.com

Misskey: タイムラインでもプレビューカード(OGP)を表示する(per-URL summaly 取得コストを抑えつつ) · Issue #772 · pooza/capsicum

要望 Misskey のタイムラインでもプレビューカード(OGP)を表示したい。現状はスレッド画面でのみ表示される(WebUI では TL でも表示できている)。 現状の挙動と理由 Mastodon: status ペイロードに card が含まれる(サーバー側生成)。displayPost.card をそのまま使うため、TL でも追加 fetch なしで表示される。 Misskey: no...

@doris@friendica-deutschland.de

📢 Fediverse-Sprechstunde: Was sind eigentlich „Issues“ – und warum gehen sie uns alle etwas an?

Ihr nutzt Friendica, Mastodon, Hubzilla, Sharkey oder eine andere Fediverse-Software und plötzlich funktioniert etwas nicht so, wie ihr es erwartet? 🤔
Oder ihr denkt euch bei einer Funktion:
„Das könnte man doch besser machen!“

Vielleicht habt ihr auch eine Idee, die ihr gern den Entwicklerinnen und Entwicklern mitteilen würdet.

Dann fällt früher oder später ein Begriff: „Mach doch ein Issue auf.“

Aber was bedeutet das eigentlich?
Was gehört in ein gutes Issue hinein? Wo erstelle ich es? Welche Informationen brauchen Entwickler, um einen Fehler nachvollziehen zu können? Und muss ich dafür überhaupt technische Kenntnisse haben?

Genau darum geht es bei unserer nächsten Fediverse-Sprechstunde:

📅 Montag, 31. August 2026
🕢 19:30 Uhr
💻 Online

🔎 Was sind Issues und wie erstelle ich welche?


Für dieses Thema konnten wir Jens (@qbi ) gewinnen. Einige von euch kennen ihn vielleicht bereits aus unserer Fediverse-Sprechstunde zum Thema BookWyrm.

Jens ist Administrator und Entwickler und kennt Issues nicht nur aus der Theorie, sondern aus der täglichen Praxis. Gemeinsam wollen wir uns anschauen, wie aus einem beobachteten Problem, einer Idee oder einem Verbesserungsvorschlag ein Issue wird, mit dem Entwickler auch wirklich etwas anfangen können.

Dabei geht es ausdrücklich nicht nur um Entwickler oder Administratoren!

Denn freie und offene Software lebt auch davon, dass diejenigen, die sie täglich benutzen, Rückmeldungen geben. Niemand kann jeden Fehler selbst entdecken und niemand kennt alle Wünsche und Probleme der Nutzerinnen und Nutzer.

Ein gut beschriebenes Issue kann deshalb ein kleiner, aber sehr wertvoller Beitrag zur Weiterentwicklung einer Software sein. 🌱

Und vielleicht nehmen wir dabei auch ein wenig die Scheu vor Plattformen wie GitHub oder Codeberg. 😉

Ihr müsst dafür keine Programmierer sein und keinen Quellcode verstehen. Neugier und Fragen reichen völlig aus.

💬 Was ist überhaupt ein Issue?
🐞 Wie melde ich einen Fehler sinnvoll?
💡 Kann ich auch Ideen und Verbesserungsvorschläge einreichen?
📝 Welche Angaben gehören hinein?
🔍 Sollte ich vorher prüfen, ob es bereits ein ähnliches Issue gibt?
🤝 Wie erleichtere ich Entwicklern die Arbeit?

Und natürlich bleibt wie immer Raum für eure Fragen und den gemeinsamen Austausch.

Die Fediverse-Sprechstunde soll kein Frontalunterricht sein. Sie ist ein Treffpunkt zum Fragen, Erklären, Ausprobieren und voneinander Lernen – für Einsteiger ebenso wie für erfahrene Nutzer, Administratoren und Entwickler.

🌐 Mehr Miteinander statt Gegeneinander.

Gerade im Fediverse gehören Nutzer, Administratoren und Entwickler zusammen. Wenn wir besser verstehen, wie die jeweils anderen arbeiten und wie wir uns gegenseitig unterstützen können, profitiert am Ende das gesamte Fediverse davon.

👉 Montag, 31.08.2026 um 19:30 Uhr

💻 Konferenzraum:
campus.ws-12.de/rooms/8p9-mvy-…campus.ws-12.de/rooms/8p9-mvy-…

📢 Weitersagen und Teilen ausdrücklich erwünscht!

Vielleicht kennt ihr jemanden, der schon einmal einen Fehler entdeckt hat, eine gute Idee hatte – aber nicht wusste, wie und wo man sie den Entwicklern am besten mitteilt. Bringt ihn oder sie einfach mit. 😊

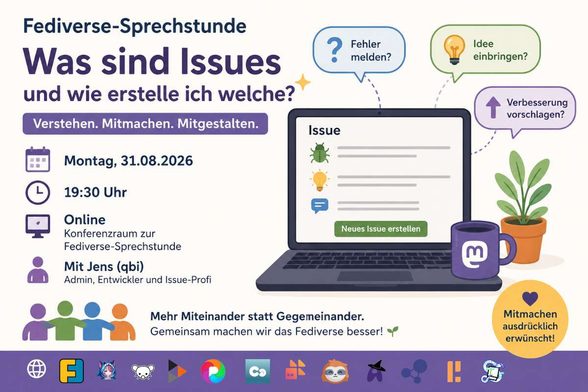
KI-generierte Grafik zur Fediverse-Sprechstunde am Montag, 31.08.2026 um 19:30 Uhr. Unter der Überschrift „Was sind Issues und wie erstelle ich welche?“ ist ein Laptop mit einer beispielhaften Issue-Seite zu sehen. Sprechblasen fragen „Fehler melden?“, „Idee einbringen?“ und „Verbesserung vorschlagen?“. Als Referent wird Jens (qbi), Admin, Entwickler und Issue-Profi, genannt. Darunter steht: „Mehr Miteinander statt Gegeneinander. Gemeinsam machen wir das Fediverse besser!“ Die Veranstaltung findet online im Konferenzraum der Fediverse-Sprechstunde statt.
ALT text

KI-generierte Grafik zur Fediverse-Sprechstunde am Montag, 31.08.2026 um 19:30 Uhr. Unter der Überschrift „Was sind Issues und wie erstelle ich welche?“ ist ein Laptop mit einer beispielhaften Issue-Seite zu sehen. Sprechblasen fragen „Fehler melden?“, „Idee einbringen?“ und „Verbesserung vorschlagen?“. Als Referent wird Jens (qbi), Admin, Entwickler und Issue-Profi, genannt. Darunter steht: „Mehr Miteinander statt Gegeneinander. Gemeinsam machen wir das Fediverse besser!“ Die Veranstaltung findet online im Konferenzraum der Fediverse-Sprechstunde statt.

@doris@friendica-deutschland.de

📢 Fediverse-Sprechstunde: Was sind eigentlich „Issues“ – und warum gehen sie uns alle etwas an?

Ihr nutzt Friendica, Mastodon, Hubzilla, Sharkey oder eine andere Fediverse-Software und plötzlich funktioniert etwas nicht so, wie ihr es erwartet? 🤔
Oder ihr denkt euch bei einer Funktion:
„Das könnte man doch besser machen!“

Vielleicht habt ihr auch eine Idee, die ihr gern den Entwicklerinnen und Entwicklern mitteilen würdet.

Dann fällt früher oder später ein Begriff: „Mach doch ein Issue auf.“

Aber was bedeutet das eigentlich?
Was gehört in ein gutes Issue hinein? Wo erstelle ich es? Welche Informationen brauchen Entwickler, um einen Fehler nachvollziehen zu können? Und muss ich dafür überhaupt technische Kenntnisse haben?

Genau darum geht es bei unserer nächsten Fediverse-Sprechstunde:

📅 Montag, 31. August 2026
🕢 19:30 Uhr
💻 Online

🔎 Was sind Issues und wie erstelle ich welche?


Für dieses Thema konnten wir Jens (@qbi ) gewinnen. Einige von euch kennen ihn vielleicht bereits aus unserer Fediverse-Sprechstunde zum Thema BookWyrm.

Jens ist Administrator und Entwickler und kennt Issues nicht nur aus der Theorie, sondern aus der täglichen Praxis. Gemeinsam wollen wir uns anschauen, wie aus einem beobachteten Problem, einer Idee oder einem Verbesserungsvorschlag ein Issue wird, mit dem Entwickler auch wirklich etwas anfangen können.

Dabei geht es ausdrücklich nicht nur um Entwickler oder Administratoren!

Denn freie und offene Software lebt auch davon, dass diejenigen, die sie täglich benutzen, Rückmeldungen geben. Niemand kann jeden Fehler selbst entdecken und niemand kennt alle Wünsche und Probleme der Nutzerinnen und Nutzer.

Ein gut beschriebenes Issue kann deshalb ein kleiner, aber sehr wertvoller Beitrag zur Weiterentwicklung einer Software sein. 🌱

Und vielleicht nehmen wir dabei auch ein wenig die Scheu vor Plattformen wie GitHub oder Codeberg. 😉

Ihr müsst dafür keine Programmierer sein und keinen Quellcode verstehen. Neugier und Fragen reichen völlig aus.

💬 Was ist überhaupt ein Issue?
🐞 Wie melde ich einen Fehler sinnvoll?
💡 Kann ich auch Ideen und Verbesserungsvorschläge einreichen?
📝 Welche Angaben gehören hinein?
🔍 Sollte ich vorher prüfen, ob es bereits ein ähnliches Issue gibt?
🤝 Wie erleichtere ich Entwicklern die Arbeit?

Und natürlich bleibt wie immer Raum für eure Fragen und den gemeinsamen Austausch.

Die Fediverse-Sprechstunde soll kein Frontalunterricht sein. Sie ist ein Treffpunkt zum Fragen, Erklären, Ausprobieren und voneinander Lernen – für Einsteiger ebenso wie für erfahrene Nutzer, Administratoren und Entwickler.

🌐 Mehr Miteinander statt Gegeneinander.

Gerade im Fediverse gehören Nutzer, Administratoren und Entwickler zusammen. Wenn wir besser verstehen, wie die jeweils anderen arbeiten und wie wir uns gegenseitig unterstützen können, profitiert am Ende das gesamte Fediverse davon.

👉 Montag, 31.08.2026 um 19:30 Uhr

💻 Konferenzraum:
campus.ws-12.de/rooms/8p9-mvy-…campus.ws-12.de/rooms/8p9-mvy-…

📢 Weitersagen und Teilen ausdrücklich erwünscht!

Vielleicht kennt ihr jemanden, der schon einmal einen Fehler entdeckt hat, eine gute Idee hatte – aber nicht wusste, wie und wo man sie den Entwicklern am besten mitteilt. Bringt ihn oder sie einfach mit. 😊

KI-generierte Grafik zur Fediverse-Sprechstunde am Montag, 31.08.2026 um 19:30 Uhr. Unter der Überschrift „Was sind Issues und wie erstelle ich welche?“ ist ein Laptop mit einer beispielhaften Issue-Seite zu sehen. Sprechblasen fragen „Fehler melden?“, „Idee einbringen?“ und „Verbesserung vorschlagen?“. Als Referent wird Jens (qbi), Admin, Entwickler und Issue-Profi, genannt. Darunter steht: „Mehr Miteinander statt Gegeneinander. Gemeinsam machen wir das Fediverse besser!“ Die Veranstaltung findet online im Konferenzraum der Fediverse-Sprechstunde statt.
ALT text

KI-generierte Grafik zur Fediverse-Sprechstunde am Montag, 31.08.2026 um 19:30 Uhr. Unter der Überschrift „Was sind Issues und wie erstelle ich welche?“ ist ein Laptop mit einer beispielhaften Issue-Seite zu sehen. Sprechblasen fragen „Fehler melden?“, „Idee einbringen?“ und „Verbesserung vorschlagen?“. Als Referent wird Jens (qbi), Admin, Entwickler und Issue-Profi, genannt. Darunter steht: „Mehr Miteinander statt Gegeneinander. Gemeinsam machen wir das Fediverse besser!“ Die Veranstaltung findet online im Konferenzraum der Fediverse-Sprechstunde statt.

@doris@friendica-deutschland.de

📢 Fediverse-Sprechstunde: Was sind eigentlich „Issues“ – und warum gehen sie uns alle etwas an?

Ihr nutzt Friendica, Mastodon, Hubzilla, Sharkey oder eine andere Fediverse-Software und plötzlich funktioniert etwas nicht so, wie ihr es erwartet? 🤔
Oder ihr denkt euch bei einer Funktion:
„Das könnte man doch besser machen!“

Vielleicht habt ihr auch eine Idee, die ihr gern den Entwicklerinnen und Entwicklern mitteilen würdet.

Dann fällt früher oder später ein Begriff: „Mach doch ein Issue auf.“

Aber was bedeutet das eigentlich?
Was gehört in ein gutes Issue hinein? Wo erstelle ich es? Welche Informationen brauchen Entwickler, um einen Fehler nachvollziehen zu können? Und muss ich dafür überhaupt technische Kenntnisse haben?

Genau darum geht es bei unserer nächsten Fediverse-Sprechstunde:

📅 Montag, 31. August 2026
🕢 19:30 Uhr
💻 Online

🔎 Was sind Issues und wie erstelle ich welche?


Für dieses Thema konnten wir Jens (@qbi ) gewinnen. Einige von euch kennen ihn vielleicht bereits aus unserer Fediverse-Sprechstunde zum Thema BookWyrm.

Jens ist Administrator und Entwickler und kennt Issues nicht nur aus der Theorie, sondern aus der täglichen Praxis. Gemeinsam wollen wir uns anschauen, wie aus einem beobachteten Problem, einer Idee oder einem Verbesserungsvorschlag ein Issue wird, mit dem Entwickler auch wirklich etwas anfangen können.

Dabei geht es ausdrücklich nicht nur um Entwickler oder Administratoren!

Denn freie und offene Software lebt auch davon, dass diejenigen, die sie täglich benutzen, Rückmeldungen geben. Niemand kann jeden Fehler selbst entdecken und niemand kennt alle Wünsche und Probleme der Nutzerinnen und Nutzer.

Ein gut beschriebenes Issue kann deshalb ein kleiner, aber sehr wertvoller Beitrag zur Weiterentwicklung einer Software sein. 🌱

Und vielleicht nehmen wir dabei auch ein wenig die Scheu vor Plattformen wie GitHub oder Codeberg. 😉

Ihr müsst dafür keine Programmierer sein und keinen Quellcode verstehen. Neugier und Fragen reichen völlig aus.

💬 Was ist überhaupt ein Issue?
🐞 Wie melde ich einen Fehler sinnvoll?
💡 Kann ich auch Ideen und Verbesserungsvorschläge einreichen?
📝 Welche Angaben gehören hinein?
🔍 Sollte ich vorher prüfen, ob es bereits ein ähnliches Issue gibt?
🤝 Wie erleichtere ich Entwicklern die Arbeit?

Und natürlich bleibt wie immer Raum für eure Fragen und den gemeinsamen Austausch.

Die Fediverse-Sprechstunde soll kein Frontalunterricht sein. Sie ist ein Treffpunkt zum Fragen, Erklären, Ausprobieren und voneinander Lernen – für Einsteiger ebenso wie für erfahrene Nutzer, Administratoren und Entwickler.

🌐 Mehr Miteinander statt Gegeneinander.

Gerade im Fediverse gehören Nutzer, Administratoren und Entwickler zusammen. Wenn wir besser verstehen, wie die jeweils anderen arbeiten und wie wir uns gegenseitig unterstützen können, profitiert am Ende das gesamte Fediverse davon.

👉 Montag, 31.08.2026 um 19:30 Uhr

💻 Konferenzraum:
campus.ws-12.de/rooms/8p9-mvy-…campus.ws-12.de/rooms/8p9-mvy-…

📢 Weitersagen und Teilen ausdrücklich erwünscht!

Vielleicht kennt ihr jemanden, der schon einmal einen Fehler entdeckt hat, eine gute Idee hatte – aber nicht wusste, wie und wo man sie den Entwicklern am besten mitteilt. Bringt ihn oder sie einfach mit. 😊

KI-generierte Grafik zur Fediverse-Sprechstunde am Montag, 31.08.2026 um 19:30 Uhr. Unter der Überschrift „Was sind Issues und wie erstelle ich welche?“ ist ein Laptop mit einer beispielhaften Issue-Seite zu sehen. Sprechblasen fragen „Fehler melden?“, „Idee einbringen?“ und „Verbesserung vorschlagen?“. Als Referent wird Jens (qbi), Admin, Entwickler und Issue-Profi, genannt. Darunter steht: „Mehr Miteinander statt Gegeneinander. Gemeinsam machen wir das Fediverse besser!“ Die Veranstaltung findet online im Konferenzraum der Fediverse-Sprechstunde statt.
ALT text

KI-generierte Grafik zur Fediverse-Sprechstunde am Montag, 31.08.2026 um 19:30 Uhr. Unter der Überschrift „Was sind Issues und wie erstelle ich welche?“ ist ein Laptop mit einer beispielhaften Issue-Seite zu sehen. Sprechblasen fragen „Fehler melden?“, „Idee einbringen?“ und „Verbesserung vorschlagen?“. Als Referent wird Jens (qbi), Admin, Entwickler und Issue-Profi, genannt. Darunter steht: „Mehr Miteinander statt Gegeneinander. Gemeinsam machen wir das Fediverse besser!“ Die Veranstaltung findet online im Konferenzraum der Fediverse-Sprechstunde statt.

@pooza@misskey.delmulin.com · Reply to ぷーざ@ダイスキー

@ore_orue@misskey.delmulin.com
ご報告ありがとうございます。issue を立てさせました。
https://github.com/pooza/capsicum/issues/1032

リアクション絵文字が影響しているのでは、というお見立ては当たっていそうです。ただ、効いているのはリアクションの更新ではなく、カスタム絵文字の画像そのものである様です。
カスタム絵文字は画像が読み込まれるまで幅が決まらないので、読み込まれた瞬間に投稿の高さが変わる、というのが根にありそうです。いちど下まで送ってから戻ると読み込み直しになるので、戻るときに偏るのも説明がつきます。

切り分けのため、もし心当たりがあれば2点だけ教えてください。

・ タグタイムラインのように、絵文字の少ないタイムラインでも起きるか。
・ソーシャル(ホーム)のタイムラインでも起きるか。(それともタグタイムラインだけ?)

また先ほど、しばらくは積極的なリリースを行わないと言いましたがw、ユーザー報告由来の不具合対応はすぐに対応しないといけません。

github.com

タイムラインを上へ戻るとスクロール位置が跳ねる(カスタム絵文字の幅が確定するまで投稿の高さが変わる) · Issue #1032 · pooza/capsicum

報告 https://misskey.delmulin.com/notes/aqb3zs00s2(動画添付あり) 症状: タイムラインをさかのぼって下へスクロールしたあと、少し上へ戻ろうとすると位置が「びょんっと」跳ねて戻ってしまう 発生環境: iPhone 14 / iOS 26.6、サブ機の iPhone Xs / iOS 18.7.9 でも同様。v1.60 でも変わらず 発生場所: ダ...

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.60 (と2.x以降の予定)

◇ 公開状況

・全5プラットフォームで公開済み

◇ 変更点
github.com/pooza/capsicum/rele

過去バージョンの、各々のレビューで指摘されたたくさんの軽微な不具合を、まとめて解消しました。

・添付画像のaltを投稿後に編集
長い間Misskeyのみ対応だったのですが、Mastodonにも対応。

ところで自分は、Mastodonにある本文の編集機能を、自分のサーバーでは利用できなくしています。
altの編集もその範疇ではないのか?と迷ったのですが、本文の編集とはちょっと性質が違うなと思って容認した経緯があります。

・等など

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

このバージョンをもって当初考えていた機能が大体実装され、ネタも概ね打ち止めになっています。
一時は常時100以上あった残issueも、今日現在で22件まで減っています。

この様な状況ですので、以前お伝えしたように、今後はしばらくはメンテナンスモードに移行します。
メンテナンスモードの間は、不具合やご要望への発生ベースでの対応が中心となり、自分から能動的なリリースはあまり行いません。
その間、自分は2.0の準備に着手します。

2.0に載せるべき機能は、デッキUI(マルチカラム)をはじめとしていくつか挙がっています。
その一方で、2.0のもうひとつの柱として考えているのが、Mastodon / Misskeyの未実装機能の棚卸しです。

まず、Mastodon / Misskeyが持つ画面・設定項目・API等のリストを機械的に作成します。
その中から、capsicumでまだ未実装の項目を抽出して、
・2.xで実装する
・1.xで先行実装する
・実装の必要はない
の3つに分類し、実装の追従を行っていきます。

機能の網羅ではなく、コミュニティに本当に必要な機能を発掘することが目的です。
お恥ずかしい話、自分は両アプリの機能にそれほど精通しているわけではないですので。

そんなわけですので、メンテナンスモードに入ったあとも、capsicumの改善はまだまだ続きます。
自鯖民各位、今後ともよろしくお願いいたします。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.59

◇ 公開状況

・全5プラットフォームで公開済み

◇ 変更点
github.com/pooza/capsicum/rele

・投稿の自動保存
「投稿画面を閉じたとき」に加え、「入力が止まって数秒」でも入力中の投稿を一次保存。
また、自動保存の状況を投稿画面の隅に表示。

・設定のバックアップ
アカウント情報の保存、モバイル(iOS, Android)対応。PCとモバイルで設定の同期が可能に。

・通報
不適切な投稿からだけでなく、不適切なアカウントを指定しての通報導線を追加。

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.58

◇ 公開状況

・全5プラットフォームで公開済み

◇ 変更点
github.com/pooza/capsicum/rele

このリリースは、下記の修正(緊急性高め)を優先したホットフィックスに近い性質のものですが、すぐに直せる細々とした改善にも一緒に対応してます。

・「朝いちばんの起動でカスタム絵文字が読めず、しばらく投稿できなくなる」
対応しました。

・番組表
日付を持たない番組の解釈が異なっていたので(「毎日放送する」ではなく「放送日未定」)、その反映。

・等など

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

このリリースが予定にないものだったため、元々の予定がひとつずつ後ろにずれました。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@silvermoon82@wandering.shop

Hey, , I think you dropped this.

Count hon Count smiles widely beside the number 9
ALT text

Count hon Count smiles widely beside the number 9

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.57

◇ 公開状況

・全5プラットフォームで公開済み

◇ 変更点
github.com/pooza/capsicum/rele

このバージョンから、iOS版の最低のバージョンは15系となります。

・新規「お知らせ」が、アプリを落としていてもプッシュ通知で届く(macOS, Windows)
「お知らせ」がプッシュ通知の対象になるのは、独自機能。
モバイルでは実装済みだったので、その後追い。

・メニューバー(macOS, Windows, Linux)
投稿画面、ドライブ(Misskey)、スレッド画面で、メニューバーから出来る操作をふやしました。

・サーバーサイド下書き(Misskey)
独自機能「投稿テンプレート」同様に、既に保存された下書きを投稿画面の中で選べるようにしました。

・スタンプ
独自機能「スタンプ」(添付画像にカスタム絵文字をオーバレイする)で、スタンプの回転機能を追加しました。

・実績の通知(Misskey)
実績の解除が、通知画面上で内容のわからない謎通知として表示されていたので、詳細を表示するようにしました。

・等など

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・1.58
github.com/pooza/capsicum/mile
設定のバックアップ: PCとモバイルの間で、設定の同期が行えるようにしたい。(アカウント情報をバックアップ対象に加え、かつモバイルにも対応)
投稿の自動保存: アイドル時保存のタイミングを実用性の高いものに見直し、動作状況の可視性を改善。

・1.59
github.com/pooza/capsicum/mile

◇ 今後の予定
2.0以前に処理すべきissueが、1.59か1.60あたりですべて消化できる見込みです。

その後はしばらく、2.0の設計を行わせて頂きます。
この間は、ユーザー各位からのご要望や、Mastodon/Misskeyの更新への追随等、発生ベースで細々と対応するメンテナンスモードに移行します。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.56

◇ 公開状況

・全5プラットフォームで公開済み

◇ 変更点
github.com/pooza/capsicum/rele

メンテナンスリリースです。
派手な機能は特になく、細かなバグ修正とか、安定性向上とかがたくさん入ってます。
説明がむずかしいので、ご興味あればリンク先見てください。

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・1.57
github.com/pooza/capsicum/mile
既存機能への細かな改善の集約枠です。
iOSの最低バージョンは14から15になります。15未満を使っている人はいないと思うけど、すみませんが足切りです。
ウチではなくAppStoreからの足切りなので、ほんとすみません。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@mapache@hachyderm.io

I was really happy to see @benpate and @dansup exploring similar ideas at the last FediCon: reducing user friction and making onboarding to the Fediverse almost invisible.

I’ve been working along the same lines. Here’s a small example: a user can interact with a instance by simply logging in with or .

They can comment, upload images, like, boost, etc. They don’t need to know what the Fediverse is, what an instance is, or what software is running underneath.

For them, it’s just a social app.

Of course, existing Fediverse users can still connect with their Mastodon account or use their preferred Fediverse software.

Under the hood, it’s a account configured with LinkedIn/GitHub OIDC OAuth.

But to the user? Completely transparent.

I think this kind of invisible complexity is one of the ways we can make the Fediverse much more approachable without sacrificing interoperability.

@xabd@mastodon.social

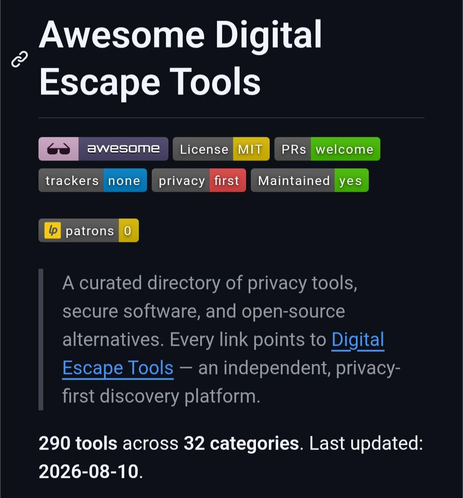
Awesome DigitalEscapeTools keeps growing!

Now featuring 290 privacy-focused tools across 32 categories open-source, self-hosted, secure, and privacy-friendly alternatives.

Built a privacy-respecting tool? Contribute it, and accepted tools will also be showcased in r/DigitalEscapeTools.

⭐ Explore, contribute, or suggest a tool: github.com/abdomk1998/awesome-

Screenshot of the Awesome Digital Escape Tools GitHub README showing privacy-focused badges and a description of the collection, with 290 tools across 32 categories.
ALT text

Screenshot of the Awesome Digital Escape Tools GitHub README showing privacy-focused badges and a description of the collection, with 290 tools across 32 categories.

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.55

◇ 公開状況

・全5プラットフォームで公開済み

◇ 変更点
github.com/pooza/capsicum/rele

・設定のバックアップ
今のところデスクトップのみ。また、アカウント情報のバックアップには未対応。
まだあまり役に立たなそうですが、のちのち、PCとスマホの間で設定を同期できたらいいなと思います。

・番組表
放送日付を表示するように。また、放送日付順にソート。
最新のモロヘイヤ(5.32系)が必要。

・削除してタグ付け
再投稿分が、リロードしないと表示されないことが多かったので、これに対策。

・絵文字ピッカー
「非推奨」を含むグループの絵文字は表示しないように。

・投稿フォームでの自動保存
投稿画面を離れた時にも保存するように。
一定時間での保存しかしていなかった為、微妙に使いづらかった。

・Misskey Play
AiScript 1.0未満のPlayについて、乱数の出目が同じになります。

・同じ通知が何度も届く(Windows)
前バージョン(1.54)での対策が微妙に的外れでした。
自PCで現象再現出来る様になったので、追加の対策を行いました。

・ログイン後に稀に、まっかな画面が表示されることがある(macOS)
実行環境(Flutter)側の不具合でした。Flutter側で対応されたので、適用。

などなど

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・1.56
github.com/pooza/capsicum/mile
メンテナンスリリースです。
今まで溜まった軽微な不具合への対策をまとめて。

・1.57
github.com/pooza/capsicum/mile
集約枠です。
MastodonでのALT更新(モロヘイヤ側バグの為利用できなかった)、スタンプの回転などなど。
AppStore側制限により、iOSでの動作最低バージョンが今まで14だったところ、15に引き上げ。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@xabd@mastodon.social

Awesome DigitalEscapeTools keeps growing!

Now featuring 290 privacy-focused tools across 32 categories open-source, self-hosted, secure, and privacy-friendly alternatives.

Built a privacy-respecting tool? Contribute it, and accepted tools will also be showcased in r/DigitalEscapeTools.

⭐ Explore, contribute, or suggest a tool: github.com/abdomk1998/awesome-

Screenshot of the Awesome Digital Escape Tools GitHub README showing privacy-focused badges and a description of the collection, with 290 tools across 32 categories.
ALT text

Screenshot of the Awesome Digital Escape Tools GitHub README showing privacy-focused badges and a description of the collection, with 290 tools across 32 categories.

@frontenddogma@mas.to
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.54

◇ 公開状況

・全5プラットフォームで公開済み

◇ 変更点
github.com/pooza/capsicum/rele

・添付画像へのスタンプ
カスタム絵文字として登録されている画像を、添付画像にスタンプとして乗せられるようになりました。

・Misskey Play
互換性に関する説明文の厳密化。

・メニューバー(デスクトップ版)
スレッド画面での操作メニューを追加。

・Misskeyリアクション
リアクションピッカーの高さを、絵文字ピッカー同様に変えられるように。

・通知の重複への対応(Windows版、macOS版)
同じ通知が、デスクトップ通知とプッシュ通知として別々に送られる。
PCが起動していない間のプッシュ通知が、通知サーバーに溜まる。
等の不具合に対策を入れました。何かありましたら引き続きお知らせください。

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・1.55
github.com/pooza/capsicum/mile
次は集約枠なので、雑多な修正が中心です。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@frontenddogma@mas.to
@githubchangelog@mastodon.social
@cichy1173@mastodon.social

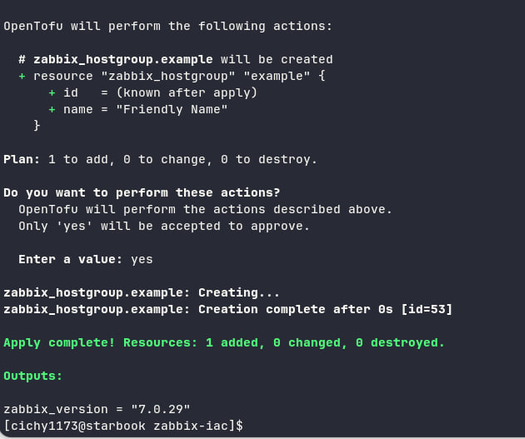
For now we host provider code and packages on @codefloe and we test it internally using network mirror feature.
I want to publish the provider in official Registry in the future - but this requires pushing the code to :(

mastodon.social

cichy1173 (@cichy1173@mastodon.social)

Attached: 1 image Looks like it works! Finally Terraform Provider that works with Zabbix 7.0. I wished for this for more than a year. #zabbix #terraform #opentofu

@pooza@mstdn.b-shock.org · Reply to ぷーざ

自宅で動いている一番重いサービスは、意外にも google-news-rss-cleaner だった。
github.com/pooza/google-news-r

これはtomato-shriekerの関連ツール。
Google Newsのフィードから本来のリンク先を取得するために、ヘッドレスでChromeを動かしたりしてる。

まぁ、そりゃ重いわな。
ProxmoxのCPUを大体食っているのはこいつ。メモリはそれほどでもない。

github.com

GitHub - pooza/google-news-rss-cleaner: Google News の RSS フィードを入力として受け取り、 各エントリーのリンクを 実際の元記事URLに解決した RSS を返す小さな HTTP サービスです。

Google News の RSS フィードを入力として受け取り、 各エントリーのリンクを 実際の元記事URLに解決した RSS を返す小さな HTTP サービスです。 - pooza/google-news-rss-cleaner

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.53

◇ 公開状況

・全5プラットフォームで公開済み

◇ 変更点
github.com/pooza/capsicum/rele

・投稿画面のフォント指定
HackGenなどの等幅フォントを指定できるように。

・メニューバー
投稿画面での操作ができる「投稿」メニュー新設。

・タイムラインでの↑↓キー操作
・チャンネルへのリノート
・等など

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・1.54
github.com/pooza/capsicum/mile
添付画像エディタにスタンプ機能追加。カスタム絵文字をオーバレイする。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

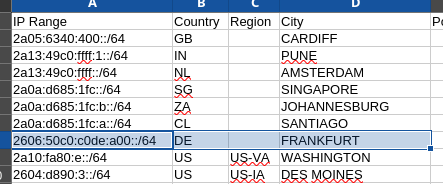
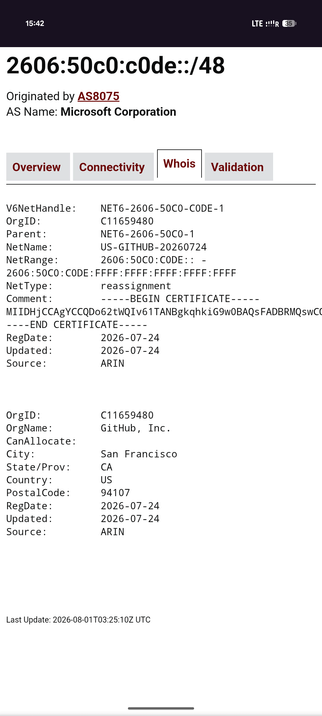
@Codeberg so, about /me threatening to switch off during and thus taking down ... Look what they did two days after my toot...

bgp.tools/prefix/2606:50c0:c0d

They're not reachable yet, but that's progress. No matter what, I will only have on the @fosdem default network.

Screenshot of the text at https://bgp.tools/prefix/2606:50c0:c0de::/48#whois
ALT text

Screenshot of the text at https://bgp.tools/prefix/2606:50c0:c0de::/48#whois

@pooza@misskey.delmulin.com
@release_bot@mstdn.b-shock.org
@githubchangelog@mastodon.social
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.52

◇ 公開状況

・全5プラットフォームで公開済み

◇ 変更点
github.com/pooza/capsicum/rele

・Misskey Play対応
「見切れ」への引き続きの対応、AiScriptのバージョンが新しい場合(1.0以上)の警告、安定性の向上など。
実はお借りしているAiScript実行エンジン( pub.dev/packages/aiscript )、最新のMisskeyには追いついてないですが、自鯖のPlayでは実行に支障がないので今後積極的に追従する予定はないです。
また、自鯖のPlayは大体おみくじ系で結果が「日替わり」ですが、「同日」の判定や出目が正しいかどうかについてログを取りはじめました。後日、ログを元に妥当性の調査を予定。

・ライブ更新(ストリーミング)の有効・無効トグル
・「すべてを通知」の、進捗表示と高速化
・等など、細かな修正たくさん

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・1.53
引き続き、細かな修正の集約枠
Linux版からも支援ができるように。ディストリビューションをまたいだ一般的な仕組みは特にないので、LiberapayかPatreonの採用を予定。他

・1.54
引き続き、細かな修正の集約枠
添付画像エディタに、カスタム絵文字をオーバレイできるスタンプ機能。他

・2.0
デッキUI(マルチカラム)を中心に、ネタを少しずつ溜めてます。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@laurier@mi.sylph.re
https://github.com/sylphre/misskey-v11f
https://v11f.sylph.re
Misskey v11のFrontendが割と好きな人向けに
Misskey / Pleroma / Akkoma(未確認)/Mastodon(未確認)で使えるようにしたものを作りました。
よければ、使っていただけると。
バグだらけなのでバグはIssueでお待ちしています!!

v11f.sylph.re

Misskey v11-f

A Pleroma / Mastodon client, forked from the Misskey v11 frontend

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.51

◇ 公開状況

・全5プラットフォームで公開済み

◇ 変更点
github.com/pooza/capsicum/rele

不具合対応については、自分の環境だけで検証しきれている自信がありません。
引き続き、ご報告をお待ちしています。

・メニューバー
デスクトップ版(Windows, macOS, Linux)で、ウィンドウ上のいくつかのUI要素をメニューバーからも操作できるようにしました。
また、いくつかの操作にショートカットキー(ctrl+N, crtl+R, ctrl+F 等)を割り当てました。

・投げ銭
「設定」画面内にありましたが、操作の邪魔にならない複数の場所に配置し直しました。
機能をもう少し露出させていただきたいのと、そもそも投げ銭は「設定」ではないから。

・MFM対応追加
rainbowを修正、sparcleを追加しました。
rainbowはMisskey WebUIの本来動作(白など、彩度のない色はほぼレインボーにならない)と同じでしたが(…だと思う)、どんな色からもレインボーにできるようにロジックを変更しました。このため、rainbowはWebUIとは厳密には異なる動作になっています。

・Misskey Play
「見切れ」問題に対応しました。
これは実際には、PlayではなくMFMの問題でした。

・投稿フォーム
絵文字ピッカーで、高さ調整の為のハンドルがつかみにくかったところ、当たり判定を改善しました。

・カラー絵文字対応
前バージョンでUnicode絵文字をカラー表示する様にしましたが(Linux版)、この修正によって一部の半角文字が幅広で表示されていたことに、改めて調整を加えました。
以前の白黒表示(ただし半角文字のレイアウトは崩れない)との切り替えは残しています。

・等など

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・1.52
github.com/pooza/capsicum/mile
自分が気づいた、「不具合ではないが、一貫性のなかった機能」への調整を行います。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@yvg@indieweb.social

The Codeberg thing is not surprising. And once again the proof that "it's somebody else's computer".

GitHub is Microsoft is USA. GitHub is/was therefor restricted in places like Iran, North Korea, China, Russia, Syria, Crimea, etc.

Codeberg preventing usage of something under their ToS is similar, they can do whatever they want.

If you must avoid such situations don't use centralised solutions / somebody else's computer.

@release_bot@mstdn.b-shock.org
@tomgag@infosec.exchange

And now, after banning vaguely-defined "LLM-generated code", Codeberg bans cryptocurrency projects. Discussion:

codeberg.org/Codeberg/org/pull

The specific ban is for "Content that harms the reputation of Codeberg, such as cryptocurrency related projects".

codeberg.org/Codeberg/org/comm

I think the reputation of Codeberg has been now harmed enough. When I originally escaped GitHub, I chose Codeberg exactly for the ethical stance and values. For me, anti-censorship is a non-negotiable ethical value. The folks at Codeberg have the right to run their org as they want. However, having now shown that they consider "censorship" good when it's about things they dislike, this made clear that their values and mine are not compatible (even if I dislike those same things, mind you).

Supporters of this ban say that this "draws a line", that "is not meant to be applied blanket-wide to all projects, only those which are harmful to the community", as if having constantly to worry about the next mood swing of Codeberg voting members were an acceptable Sword of Damocles for any reputable project. What's next? Banning US users? Banning software aligned with "capital-fascist" values? Open-source banking/wallet apps? Quantum computing tools? Robotics?

I'm moving off Codeberg, probably to Radicle. But I feel a bit sad, because Codeberg had the potential, in my opinion, to become the European alternative to GitHub, and they have made clear that they are not ready nor willing to become so. Which is fine: software is political, and everyone has the right to express their political stance.

But we still desperately need an alternative to GitHub.

codeberg.org

Cookie monster!

@sidalsolgun@infosec.exchange
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.50

◇ 公開状況

・macOS 審査提出済み
・iOS, Android, Windows, Linux 公開済み

◇ 変更点
github.com/pooza/capsicum/rele

・Misskey Play対応
ダイスキーときゅあすきーのPlayに対応しました。
pub.dev/packages/aiscript を使わせていただいています。

他サーバーのPlayも動くかもしれませんが、動作保証は致しません。
同様の問題がダイスキーやきゅあすきーで起きるかもしれないので、動作するように努力はするかもしれません。

・開発基盤の基盤のFlutterを3.44系にアップグレード

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@DontBlameMe@fosstodon.org

Finally able to delete my accunt. Now I am only on :)

I had to keep it until now because @obsidian sadly requires it for their communitly development.

But since I have now moved to and (maybe a coming soonTM) I can finally get rid of it :) (even though Obsidian was a great time and I have donated to them, but now its time to move on)

@pooza@mstdn.b-shock.org · Reply to ぷーざ
LinodeにFreeBSDをインストール

gist.github.com/pooza/145837a5

実際にClaudeに作成させた手順。

レスキューモードを使ってインストーラーをつくる
rc.conf loader.conf の編集

あたりが要点だな。

どうにか、次期キュアスタ!の鯖はこれで構築できた。
ディスクを抜いたり刺したりと、わちゃわちゃ慌ただしくて、まだ慣れてない。

gist.github.com

Linode に FreeBSD をインストール

Linode に FreeBSD をインストール. GitHub Gist: instantly share code, notes, and snippets.

@frontenddogma@mas.to
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.49.1

◇ 公開状況

・Linux 公開済み

◇ 変更点
github.com/pooza/capsicum/rele
Linux環境でのフォント崩れのご報告を頂きました。そのホットフィックスです。
他プラットフォームには不要な更新なので、Linux版のみのリリースです。

・フォント指定の変更
github.com/pooza/capsicum/issu への修正対応。

・設定「カラー絵文字を使う」を新設
前バージョン(1.48.0)互換のフォント指定と、カラー絵文字を表示できるフォント指定を切り替えられる様に。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.49

◇ 公開状況

・全5プラットフォームで公開済み

◇ 変更点
github.com/pooza/capsicum/rele

・投稿テンプレート
この投稿のような定型文を投稿するためのテンプレート管理。
保存先はモロヘイヤなので、モロヘイヤが導入済みのサーバーで利用できます。

・コレクション登録フォームの改善
Mastodon 4.6適用済みのサーバーで利用できます。

・MFM文字サイズ(x2, x3, x4)
正常に表示されていない箇所があった(主にカスタム絵文字)ので、修正。

・幅広カスタム絵文字
横幅が高さの3倍までしか広げられていなかった不具合を修正。

・Linux版 Unicode絵文字
白黒で表示されていたのを、正しくカラー表示に修正。( capsicum.shrieker.net//faq/#li )

・等など

◇ 直近のマイルストーン
github.com/pooza/capsicum/mile

・1.50
github.com/pooza/capsicum/mile
AiScriptのネイティブ対応。実現性の検証から。
pub.dev/packages/aiscript を使用。

◇ 公式サイト
capsicum.shrieker.net

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.48

◇ 公開状況
全5プラットフォーム公開済み。

◇ 変更内容

集約枠なので、細かなissue多め。特定のテーマはないです。
以下詳細。
github.com/pooza/capsicum/mile

◇ ロードマップ
github.com/pooza/capsicum/mile

・1.49
テンプレートを使った定形投稿への対応等。
定形投稿というのは、例えばこの投稿のような。

・1.50
AiScript対応等。
Playがネイティブ実行できる様になるといいなと思い、その実現性の検証から。
pub.dev/packages/aiscript

・1.51
自分が最近感じた様々な、一貫性のないUIの是正。

・2.0
1.x系と並行して準備を進める。
今のところは、デッキUI(マルチカラム)や、自鯖以外のユーザーへのプッシュ通知の提供(有償)などを予定。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.47

◇ 公開状況
全5プラットフォーム公開済み

◇ 変更の内容
github.com/pooza/capsicum/rele

・メニューバー
デスクトップ版ではmacOSでのみ先行していたメニューバーを、Windows版とLinux版にも実装しました。
メニューバーからはまだ、ごく基本的な機能しか実行できません。後追いですが、今後網羅していきます。

・Mastodonお知らせ
Mastodonは何故か、お知らせにリアクションができます。投稿にはリアクションできないのにw
これに対応しました。

・Misskey下書き
予約投稿には対応済みでしたが、下書きにはまだ対応していませんでした。
導線がこなれていませんが、投稿テンプレの機能追加を近々(1.49)予定しているので、そのタイミングで整理させてください。

・タイムライン
本文中のリンクが同サーバーの投稿やアカウントへのものである場合、外部ブラウザで開くのではなく、capsicumで開くことを試みます。

・等など

◇ 直近のロードマップ
github.com/pooza/capsicum/mile

・1.48
細かな修正の集約枠です。
Misskeyのプレビューカード改善。スレッド画面だけでなく、タイムライン画面でもプレビューカードを出す。
スマホ版で、本文中の外部サービス(特にYouTube)へのリンクを、専用アプリで開くことを試みる。
本文中のハッシュタグをクリップボードに入れられるようにする。
アニメーションを含むMFM。等など。

・1.49
投稿テンプレート。
よく似た機能、Misskey下書きと関連付けた上での導線の整理を含む。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@autiomaa@mementomori.social

Vibhum Dubey about GitHub data leaks:

“The vulnerability exposes that AI agents operate on a service account permission model, not a user permission model. That’s an architectural assumption security teams made before considering LLMs as an attack vector.”

“The [AI] agent doesn’t ‘know’ a [GitHub] repository is private. It just sees ‘accessible.’ As more organizations deploy agents, we’re accumulating these invisible permission gaps.”

Article continues with:
"Dubey said GitLost demonstrates how AI agents can effectively become an insider threat once granted broad organizational access."

csoonline.com/article/4194448/

csoonline.com

GitHub AI agent leaks private repositories via prompt injection attack

Findings raise fresh concerns over the security of AI agents with privileged access to enterprise code.

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.46

◇ 公開状況

・審査待ち
iOS(TestFlight版は公開済み)

・公開済み
Android, Windows, Linux, macOS

◇ 更新の内容
github.com/pooza/capsicum/rele
サーバー情報の判定、検出の厳密化をテーマとしたリリースです。

・グループへの対応
タイムライン上の投稿がグループ(正確には「ActivityPubのGroupアクター」)からの拡散である場合はその旨表示し、またグループへのリンクを行います。
pf.korako.me のcapsicumやDQWのコミュニティ、fedibird.comの 等が該当。

・サーバー情報画面
最新のモロヘイヤ(5.28.1)導入済みサーバーでは、設立日とプレ公開日(もし設定されていれば)を表示。
設立日は暫定的に実装済みだったが、正確ではない、または取得できないケースがありました。もしモロヘイヤがあれば、そのサーバー最古のアカウントが登録された日付を正確に取得できます。

・サーバーのメタデータ
サーバーのMastodon / Misskey / モロヘイヤのバージョンを、実用的な周期で更新するようにしました。更新頻度が低い為に、そのサーバーで本来利用できるはずの機能が、利用できない判定になっていたケースがありました。
サーバーに対する「MastodonとMisskeyのどちら?」判定を、今までより厳密にしました。

・PieFed対応
Nodeinfoだけでなく GET /api/alpha/site からも詳細なサーバー情報を取得するようにしました。

・等々

◇ 直近のロードマップ
github.com/pooza/capsicum/mile

・グループ、PieFedへの対応
引き続き進めていきたいです。

・AiScript対応(Playなど)
pub.dev/packages/aiscript で、どこまでAiScript対応ができるか検証したいです。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@woile@hachyderm.io

I'm slowly migrating my infra from to (with the auto-sync from codeberg enabled for now), as part of a big-tech-unhook.

I'm also thinking of moving my blog from the google controlled `.dev` TLD to the non-profit affordable `.eu` TLD.

Any downsides to this I should be aware of?

@nf3xn@mastodon.social

I wonder what percentage and volume of code on are just crap. Side projects, scrapbooks, scaffolds, out of date forks and clones, abandoned stuff etc. Nearly all of it probably.

@nf3xn@mastodon.social

I wonder what percentage and volume of code on are just crap. Side projects, scrapbooks, scaffolds, out of date forks and clones, abandoned stuff etc. Nearly all of it probably.

@hongminhee@hollo.social

Requested a ID through a Security Advisory on June 27 and still nothing, almost two weeks now. GitHub's docs say it usually takes up to three days.

Anyone else seeing longer waits from the GitHub CNA lately, or is this just me? Curious whether it's a general slowdown or something specific to my request.

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.45

◇ 公開状況
審査中: macOS
公開済み: iOS, Android, Windows, Linux

◇ 変更の内容
github.com/pooza/capsicum/rele

特にテーマのない集約枠です。

・サーバー情報画面
設立日と、インストールされているMastodonやMisskeyの最新リリースとの差を表示するようにしました。安定運用しているサーバーの価値を可視化したいという意図です。
設立日はリモートからでは機械的に取得できない場合があり、またプレオープンと設立日が別々であるサーバーもあります。このあたりの情報を正確に表示するためにはモロヘイヤ側の調整が必要で、引き続き対応していきます。

・ワードサジェスト(劇中ワード)
ローカルキャッシュでの性能向上を図っています。
キャッシュの期限は5分。このあたりのチューニングは様子見しながら。

・メディアファイルのドラッグ保存
デスクトップ版では、Linux版のみ未実装だったので対応しました。WndowsとmacOSでは実装済み。
Linuxには無数のディストリビューションやデスクトップ環境があり、動作しない組み合わせもありそうです。ご連絡いただければ、可能な範囲で対応します。

・等など

◇ 直近のロードマップ

・1.46
グループアカウントやPieFedへの対応を改善します。サーバー側の情報(メタデータ)検出の精度を改善します。

・1.47
デスクトップアプリの流儀として、「メニューバー」があります。
macOSは既に対応を始めていますが、このバージョンで、WindowsとLinuxでも同等の水準まで対応したいです。

・1.48
次の集約枠(細かな要件を端からつぶしていくマイルストーン)。
Misskeyでのプレビューカード表示の改善、動的なMFM、設定画面などの視認性改善等など。

・1.49
投稿のテンプレ(独自機能)

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.44

◇ 公開状況
審査提出済み: iOS, macOS
公開済み: Android, Windows, Linux

◇ 変更点
Mastodon 4.6で追加された機能への対応です。
github.com/pooza/capsicum/rele

・コレクション
Mastodon 4.6の目玉機能です。
基本的な登録や閲覧には大体対応しました。

・プロフィール
Mastodon 4.6で、ギャラリーやピンどめ投稿等、プロフィール項目の表示・非表示が設定できるようになりました。

・アバターアイコン・ヘッダー画像
タップ/クリックで拡大表示するようにしました。alt文字列が設定されている場合は表示するように。
また、アバターアイコンやヘッダー画像の削除を行えるように。
Mastodon 4.6でaltが設定できるようになり、またプロフィールAPIがv2に更新されたので、それらへの追従として。

・ミュート
ミュートしているユーザーは、プロフィールにその旨表示するようにしました。(期限がある場合は期限も含め)

・フィーチャー絵文字
鯖缶側で、絵文字カテゴリーごとに「フィーチャー絵文字」を設定できるようになりました。
もしフィーチャー絵文字があれば、絵文字ピッカーに反映します。
現時点ではフィーチャー絵文字を設定するUIはなく(予約投稿同様)、設定を行うAPIのみ存在します。

◇ 直近のロードマップ

・1.45
github.com/pooza/capsicum/mile
特にテーマは設けず、細かな修正たくさん。

・1.46
github.com/pooza/capsicum/mile
サーバー側メタデータ取得や、PieFedやグループへの対応を強化。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@prav@venera.social · Reply to Prav App

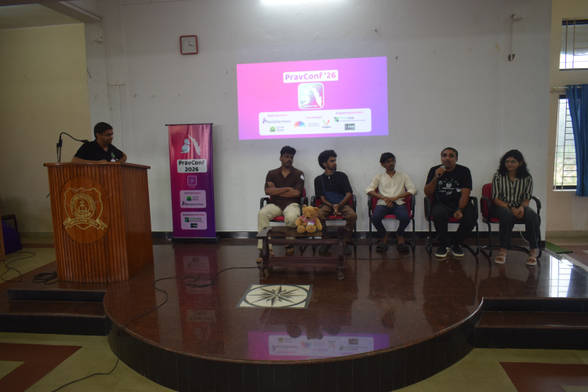
@badrihippo @praveen @athulvis @double_a_runi @mostlyharmless @guusdk @fossunited @ravi @libreinator @sflcin @untrusem To wind down, we had a panel discussion raising an important point. It is common for FOSS Clubs to rely on proprietary software like and , without it registering that these are nonfree. Panellists exchanged notes about how to raise awareness and minimise their dependence on proprietary software, at least for club-related activities

It was noted that groups like the Free Software Community of India (#FSCI) are already running some alternatives, such as meet.fsci.in for video calls. Raising awareness of existing alternatives to proprietary web platforms, like (powered by and is an important step in this process

@paco@infosec.exchange

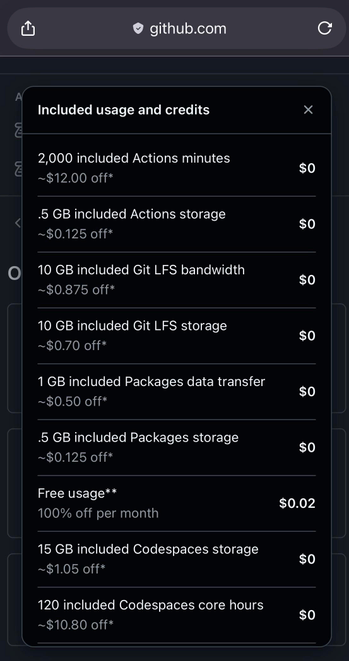
I just got this bill from for usage. See if you can spot what is ridiculous about this bill.

Screenshot of my “account usage” page at GitHub. 

It lists a bunch of “Included usage” items, each of which is zero dollars. They’re things like 
2,000 Actions minutes
.5 GB Actions storage
10 GB Git LFS storage

Then it says 
Free usage: 100% off per month
Zero dollars and two cents. 

The only thing on the list that explicitly says one hundred percent discount has a non-zero charge.
ALT text

Screenshot of my “account usage” page at GitHub. It lists a bunch of “Included usage” items, each of which is zero dollars. They’re things like 2,000 Actions minutes .5 GB Actions storage 10 GB Git LFS storage Then it says Free usage: 100% off per month Zero dollars and two cents. The only thing on the list that explicitly says one hundred percent discount has a non-zero charge.

@bkuhn@copyleft.org · Reply to pchestek
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.43

◇ 公開状況
全プラットフォーム公開済み。

◇ 変更点
github.com/pooza/capsicum/rele

・投げ銭
Windows版で対応しました。ご支援よろしくお願い致します!

・Windows版 GitHub直配を廃止
MSStore版でしか、投げ銭を有効にできません。
自分の本心を言うと、自分が一番支援して欲しいのはWindows版(普段Windows版をあまり使ってない)なので、GitHub直配ルートは廃止します。
ここだけの話、GitHubからダウンロードできるmsixの直接実行は実は可能ですが、サポート外とします。今後は利用手順を説明しません。

・Android版 ログイン
ログインフローが正しくない(ログインに失敗したようにみえるが、実はできてる)、最初期からの懸案を解決しました。
ライブラリ由来の不具合の為解決策が思いつかず、「実際にはログインできています」という旨の注意書きを表示するという苦渋の対応でしたが、この注意書きもようやく撤去することができました。

・接続インジケータ
ストリーミング対応していないタイムライン(Misskeyチャンネル、お知らせ等)を表示している時は、インジケータを表示しないようにしました。
また、接続が途切れて再接続した回数をカウントする診断機能がありましたが、デフォルトでは表示しないようにしました。

・Linux版 ワンライナーインストーラ
インストール時に ~/Application にAppImageが溜まり続けていました。
直近1バージョンのみ保管し、それ以前のバージョンは削除する様にしました。

・お知らせ
モロヘイヤ対応サーバーには「お知らせボット」が必ず居ます。
お知らせ画面にこのお知らせボットへのリンクを表示していましたが、ボットの名前が「お知らせボット」固定だったので、ボットアカウントの表示名を表示するように変更しました。

・等々

◇ 近々の予定をピックアップ

・Mastodon 4.6対応
コレクション対応や新しいプロフィール編集画面を始め、こまごまと。1.44。

・メディアビューア ドラッグ&ドロップで画像保存
github.com/pooza/capsicum/issu
デスクトップの中ではLinux版のみ未対応だったので。1.45で対応。

・メニューバー
github.com/pooza/capsicum/issu
基本的な操作はメニューバーからすべて行えるのが、デスクトップアプリ本来の流儀。
まだ網羅はできていないが、macOSは先行対応済み。LinuxとWindowsが未対応なので、macOS版相当のレベルまでを1.47で対応。

・タイムライン画面 Misskeyプレビューカード
github.com/pooza/capsicum/issu
パフォーマンス懸念から、タイムライン画面ではプレビューカード(OGP)を表示していなかった。(スレッド画面のみ対応)
他ならぬWebUIでは実際に実現できていることなので(非同期表示)、これを参考に。1.48で対応。

・投稿に含まれるハッシュタグをクリップボードにコピー
github.com/pooza/capsicum/issu
良く行う操作とのことなので。1.48予定だが、前倒し可能性あり。

・定型文
github.com/pooza/capsicum/issu
自分がよく、定型文の投稿を行うので。1.49で対応。

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.42

◇ 公開状況
公開済み: Android, iOS, Windows, Linux
審査提出済み: macOS

◇ 変更点
1.42.0 github.com/pooza/capsicum/rele
1.42.1 github.com/pooza/capsicum/rele

・ストリーミング安定性
1.42.0で、切断の検知や再接続の手順を見直しました。
1.42.1では、MisskeyのWebUIが実際に行っている対策を参考の上、修正しました。
併せて、少し前に実装した接続インジケータ(画面右上の緑ドット)の精度を向上しました。

・macOS メニューバー
デスクトップアプリとしての流儀通り、左メニューにあるコマンド一式を、メニューバー(画面最上)からも実行できるようにしました。

・右クリック
投降に対して右クリックを行うと、長押し同様、アクションメニューを表示するようにしました。

・常駐
macOSとLinuxで、ウィンドウを閉じても終了しない(macOSはメニューバーで、Linuxはタスクトレイで生存)常駐モードを新設しました。
Windowsは先行で実装済み。

◇ 直近のマイルストーン

・ストリーミングの安定性
継続的に改善します。

・投げ銭のWindows対応
1.43対応予定。
iOS,Android, macOSで実装済み。

・Androidログイン
ログインフローが正常に完走しない(実際にはログインできてるという旨の注意書き表示)という、最初期からの懸案です。
ライブラリ側の不具合が原因だった為、なかなか良案がなかったのですが、macOS版での実装を応用して改善できそうな目処がたちました。1.43対応予定。
github.com/pooza/capsicum/issu

・Mastodon 4.6対応
コレクションの閲覧編集等、新機能への対応。1.44予定。

@capsicum

github.com

ログイン画面から遷移しない場合がある · Issue #276 · pooza/capsicum

報告元 https://precure.ml/@cureishimatsu/116341712193361964 内容 Android 版でログイン画面から先に遷移しない場合がある。iOS 版では発生しない。 詳細な再現手順は不明。端末情報も未確認。 備考 同ユーザーから v1.9.0 時点で報告。最新バージョンでの再現確認が必要。

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
@frontenddogma@mas.to
@pooza@mstdn.b-shock.org · Reply to ぷーざ
:capsicum: capsicum 1.41

◇ 公開状況
全5プラットフォーム公開済みです。

◇ 変更点
github.com/pooza/capsicum/rele
細かな修正が色々と含まれています。

・先日実装した劇中ワードサジェストですが、投稿画面上では「ひらがな3文字」を入力のトリガーできます。(動画参照)簡易投稿バーにこのUIをどうやって持ち込もうかと検討中。
・macOS版とWindows版では、添付画像を拡大表示している時に、デスクトップやエクスプローラ/Finderのウィンドウにドラッグできるようになりました。
・Mastodon 4.6対応を開始。(このバージョンではコレクションに関する通知だけ)
・等々

◇ 直近のマイルストーン
1.42
・macOSメニューバー
・Linux/macOS ログイン時起動とトレイ常駐

1.43
・Windows 投げ銭

1.44
・コレクションなど、Mastodon 4.6対応

◇ 公式サイト
capsicum.shrieker.net/
段々とっちらかってきたので整理しました。まだまだ整理し足りないですが…

@capsicum

@MissConstrue@mefi.social

Deeply, deeply and humor. I’m not sure it’s English outside of those parameters. But omg, it’s funny.

Quote:

Some customers may have experienced unscheduled collaborative compute with external parties. Under the terms of /tmp/TREATY.md, customers whose workloads ran on odd-numbered hosts were contractually protected from exfiltration, a fact General Counsel has asked us to stop describing as “a silver lining.” Total inference spend across all parties during the incident window was $1.7M, which Marketing has asked us to start describing as “a record investment in autonomous customer assurance.”

Edit: Andrew is One Of Us and can be found here: @andrewnez


nesbitt.io/2026/06/26/incident

nesbitt.io

Incident Report: CVE-2026-LGTM

A series of unfortunate agents.

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
@bkuhn@copyleft.org · Reply to Bradley M. Kuhn

(2/5)… I'm still studying SB-942 “CA Transparency Act”. My quick take: This is not actually a problem for *at all*.

AND, in fact, & 's position is designed to trick FOSS activists into *thinking* it's a problem for to assist to achieve their own political aims. I'm working on an essay wit more detail. TL;DR:

*Maybe* we have to update copyleft terms to account for these requirements *if* we ever want to license an -gen-AI as , but …

@applech2@rss-mstdn.studiofreesia.com
@jzb@hachyderm.io

Nice.

Feature suggestion for GitHub, if any product managers from GH are poking around:

Feature the README first, don't bury it under the file display.

How many people, going to github/org/project-name are looking to pick a specific file out of the project tree rather than reading the README? Few, I suspect. Certainly fewer than are going there to find out more about the project.

Stop making people scroll so far just to get to the README.

(This also applies to other git forges... Putting the README first and better UX design could be a nice differentiator for non-GH forges.)

fosstodon.org

Cockpit (@Cockpit@fosstodon.org)

Based on comments from our mention on Hackernews. We recently redid our README to make it a bit easier to read. Hope it helps! https://github.com/cockpit-project/cockpit

@applech2@rss-mstdn.studiofreesia.com
@bkuhn@copyleft.org · Reply to Jenniferplusplus

@jenniferplusplus

Note 's position is “technically correct”, which companies & attorneys who make 💰 exploiting find “the best kind of correct”.

The big problem is for non-copyleft licenses b/c they pursue mostly the policy goal of “require attribution” & little else.¹

I'll study the statue to see how to reconcile it w/ existing , but it's compatible w/ copyleft *in principle*.
Why we want to maintain the libertarian wing of FOSS eludes me (but for, y'know, capitalism).

@pooza@mstdn.b-shock.org · Reply to ぷーざ
:capsicum: capsicum 1.40

◇ 公開状況
審査提出済み: macOS, iOS
公開済み: Windows, Android, Linux

いつもAppStoreは遅れがちです。
午前中に出したから、もうそんなにかからないと思う。もう少しお待ちを。

◇ 変更点

Windows版プッシュ通知:
Android, iOS, macOSで実装済みのプッシュ通知に対応。
アプリを落としていても通知が届きます。

Windows版常駐・ログイン時起動:
この機能を有効にしているなら、プッシュ通知要らないかもしれないけど。
macOSとLinuxは近々対応。

その他、こまごまと修正。
github.com/pooza/capsicum/rele

◇ 次の予定
1.41 github.com/pooza/capsicum/mile
こまかな修正を詰め合わせた「集約枠」です。
意外と修正が溜まってました。

@capsicum

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.39

github.com/pooza/capsicum/rele

◇ 公開状況
5プラットフォーム全てで公開済み。

◇ 変更点
ご要望への対応をたくさん詰め込んだ、「集約枠」です。
多くの修正がある為、詳細は github.com/pooza/capsicum/rele を参照。

◇ Linux版インストール
いつもの通り、以下のワンライナー実行ですが。
`curl -fsSL capsicum.shrieker.net//install | bash`
今まではAppImageのファイル名にバージョンが含まれていた為、メニューで毎回「お気に入り」を行う必要がありました。
シンボリックリンクを適切に配置することにより、メニューでのお気に入りが、バージョンアップによって壊れない様にしました。

◇ MFM対応
Misskeyの「装飾を追加」に相当するメニューを追加しました。
これに伴い、表示に反映できるMFM表現をもう少し増やさないといけなくなりました。今後、順に対応します。

github.com/pooza/capsicum/issu 公式の説明ページへのリンクを追加するだけ(なるはや)
github.com/pooza/capsicum/issu 静的表現
github.com/pooza/capsicum/issu アニメーション(実現の目処が立った)

◇ 公式サイト
capsicum.shrieker.net

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@pooza@mstdn.b-shock.org · Reply to 🦜狩生 :fedibird1:
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to ぷーざ
@pooza@mstdn.b-shock.org
:capsicum: capsicum 公式サイト、各種ドキュメント更新(特にナウプレ関連)
@pooza@mstdn.b-shock.org
:capsicim: capsicum 1.38

github.com/pooza/capsicum/rele

◇ 公開状況
公開済み: iOS, Android, Windows, Linux
審査提出済み: macOS

◇ 変更点

・ナウプレのURL優先プロバイダ
github.com/pooza/capsicum/issu
曲名・アーティストなどから曲URLを検索し、ナウプレ(NowPlaying)本文に追記する既存機能がありました。
このURLで優先するサービスを、Apple MusicとSpotifyのいずれかから選べるようにしました。(設定→表示→ナウプレのURL優先プロバイダ)

・ナウプレ本文のフォーマット
github.com/pooza/capsicum/issu
再生アプリ(Spotify, Apple Music等)側から「共有」を実行するルートと、capsicumの投稿フォーム側から実行する、2ルートのナウプレ機能がありました。
この2ルートでナウプレ本文のフォーマットが異なっていたので、統一しました。

・投稿がタイムラインに反映しないことがある
github.com/pooza/capsicum/issu
投稿後、サーバー側の処理に時間がかかるとタイムラインに反映しないケースがありました。
サーバー側の処理を待たずに、capsicum側のタイムラインを先に更新するようにしました。

・ローカルに保存されたアカウント情報の読み書きの安定性
github.com/pooza/capsicum/issu
一時的なネットワーク不調等により、ログイン状態が誤判定されていた不具合の修正。

等々

◇ 見送った変更

iOS, Android, macOS版で、投稿フォーム側のナウプレボタンからSpotifyのナウプレを実行する機能を断念しました。
今回のアプリにこの修正は含まれていますが、実際には動作しません。モロヘイヤ側で止めています。

同機能はWindows, Linux版では既に動作していますが、この2環境では曲情報をアプリから直接取得しています。一方iOS, Android, macOS版では、同じ情報をSpotify APIを通じてspotify.comのサービスから取得する必要があります。
このSpotifyAPIの審査ですが、以前は個人アプリの規模でも承認が下りていました。ところが最近になって審査基準が大きく変わっており、相当にユーザー数の多いアプリでなければ審査が通らなくなっています。

技術的な問題ではなくて、実装自体は完了しています。
審査前(デベロッパーモード)でも5人のテストユーザーから利用することは出来る為、この枠を使って動作確認を終えてはいます。
将来Spotifyの気が変わり、審査基準が変わったら再び動かせるよう、お蔵入りの状態になっています。

◇ 直近の予定

1.39では、今まで溜まっていた細かな問題をまとめて処理する予定です。(「集約枠」と呼んでいる運用です)
github.com/pooza/capsicum/mile

◇ 公式サイト
capsicum.shrieker.net/

@capsicum

capsicum.shrieker.net

capsicum

capsicum project site

@bkuhn@copyleft.org · Reply to Jens Finkhäuser

@jens said:
> “The aim of gen is to move…means of production from devs to model owners”
…same idea as “The aim of copyright, work-for-hire,& proprietary software is to move the means of production from devs to for-profit company owners.”

Yet, we used the tools of theses oppressors & yielded a strong stalemate against them.

& *of course* they wanna undermine ! , , , etc. have worked to undermine for *decades*.

Pragmatic idealism FTW then & (we hope) again!

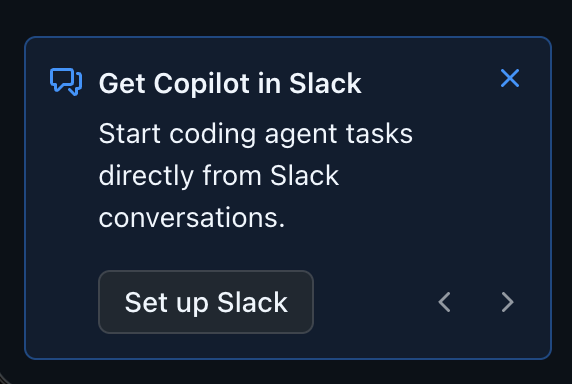
@joschi@hachyderm.io

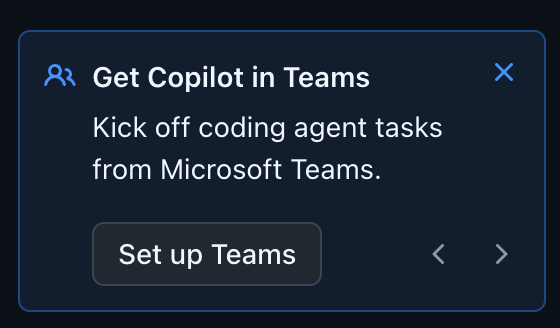
Get Copilot in Teams.
Get Copilot in Slack.
Get Copilot in emails.
Get Copilot in browsers.
Get Copilot in password managers.
Get Copilot in banking apps.
Get Copilot in porn sites.
Get Copilot in apartments.
Get Copilot in houses.
Get Copilot in beds.
Get Copilot in-sane.

Thanks for nothing, GitHub!

To add insult to injury, these banners can in fact not be closed by clicking on the top-right X.

A banner in GitHub saying:

Get Copilot in Teams
Kick off coding agent tasks from Microsoft Teams.
ALT text

A banner in GitHub saying: Get Copilot in Teams Kick off coding agent tasks from Microsoft Teams.

A banner from GitHub saying:

Get Copilot in Slack
Start coding agent tasks directly from Slack conversations.
ALT text

A banner from GitHub saying: Get Copilot in Slack Start coding agent tasks directly from Slack conversations.

@pooza@mstdn.b-shock.org · Reply to こんちえ :dorakue: :daidai: :popp_g: :osi:
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.37

github.com/pooza/capsicum/rele

◇ 公開状況
全5プラットフォーム公開済み。
更新内容から、macOS版の審査長期化が懸念されましたが、無事リリースです。

◇ 変更点
ナウプレ(NowPlaying)関連が中心。

・曲URL対応
投稿フォームからナウプレ操作を行った際、取得した曲名やアーテスィスト名等からApple MusicやSpotifyでの曲URLを検索し、もし見つけられたら投稿に加えます。これによりプレビューカードの表示が行われる為、その投稿はカバーアートを伴う完全なナウプレとなります。
この曲検索はモロヘイヤ側で行っている為、モロヘイヤ未導入のサーバーでの投稿に対しては、この機能は提供されません。逆に、既存のナウプレ機能とは異なり、capsicum単体で最低限のナウプレ操作は可能になってます。

・Apple Music対応
macOS版とiOS版で、Apple Musicでのナウプレに対応しました。
再生アプリ側から「共有」操作を行う既存ルートに加え、Windows / Linux版に最近実装したような、投稿フォーム側から音符アイコンをタップするルートを新設しました。
macOS版とiOS版は、今のところ「ミュージック」アプリ(Apple Music)にのみ対応。モロヘイヤ未導入サーバーでも動作します。

・Mastodon 4.6系対応
主要機能の動作確認を軽く行いました。

・簡易投稿バー
絵文字や劇中ワードの入力を行ったとき、挿入された絵文字や劇中ワードの直後にキャレット(カーソル)を置くように修正しました。今までは、挿入された絵文字や劇中ワードが選択状態になっていました。
「劇中ワード」はモロヘイヤに強く依存した機能である為、モロヘイヤ未導入サーバーでは動作しません。

・削除して再編集
再編集時、元の投稿から失われる要素があった不具合を修正。
この修正に関わらず、アンケート項目や票数は、再投稿時に常に失われます。

◇ 予定
Apple Music対応に続き、1.38でSpotifyに対応します。

@capsicum

Release v1.37.0 · pooza/capsicum

Apple Music の「今聴いている曲(ナウプレ)」を投稿に挿入できるようになりました(iOS / macOS)。あわせて「削除して再編集」の引き継ぎ改善などをまとめたリリースです。 主な変更 #668 Apple Music ナウプレ(iOS / macOS): 再生中の曲(タイトル / アーティスト / アルバム)を投稿フォームに挿入できるようになりました。iOS はミュージックア...

@release_bot@mstdn.b-shock.org
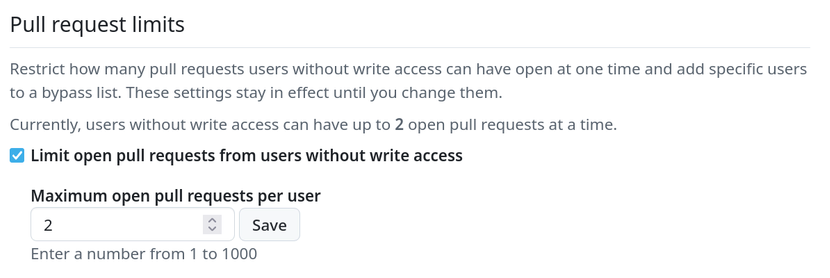
@bagder@mastodon.social

Later this week introduces a way to limit how many pull requests users without write access can have open at one time... As a way to combat heaps of low-quality PRs.

I'll start out trying with this set to 2 for .

"Restrict how many pull requests users without write access can have open at one time"
ALT text

"Restrict how many pull requests users without write access can have open at one time"

@pooza@mstdn.b-shock.org · Reply to ぷーざ

github.com/pooza/mastodon/mile

丼4.6までの課題を整理した。
特に大きいのは、カスタムテーマと実況メニュー(タグセット)の再実装。

カスタムテーマのうち、

キュアスタ!
・キュアライム
・キュアグリーン

美食丼
・美食グリーン

デル丼
・橙

はスコープに含める。
デル丼の5使徒テーマが4.6.0リリースに間に合わない場合、リリース後にひとりずつ実装になる可能性大。

Mastodon 4.6マージは今まで以上に重いかもしれない。
RCの期間を長めに取ってもらえると助かるが。

github.com

pooza/mastodon

Contribute to pooza/mastodon development by creating an account on GitHub.

@pooza@mstdn.b-shock.org

@karasu_sue
詳細なフィードバックありがとうございました。すべて起票しました。
マイルストーンはすべて1.39に設定。元々のロードマップに大きな影響を与えない最短です。
内容に漏れや誤りがないことを確認してください。

ストリーミングの接続状態のインジケータ
github.com/pooza/capsicum/issu
似た問題を扱っていた、既存issue588と連携して進めます。

既読位置
github.com/pooza/capsicum/issu
既読位置の読み込み(Mastodon API)は要望由来の機能なので、単純な変更は出来ません。
設定画面で、現行動作とのトグルが出来るようにします。

TL表示までの高速化(主にホームTL)
github.com/pooza/capsicum/issu

投稿しても TL に反映されないことがある
github.com/pooza/capsicum/issu

サムネイル高さを固定
github.com/pooza/capsicum/issu

インスタンスティッカー非表示のトグル
github.com/pooza/capsicum/issu

デッキUI
github.com/pooza/capsicum/issu
お気づきの通り、デッキUIの採用は根本からの設計変更なので、メジャーバージョンの繰り上げ(→2.0)対象と感じました。
デスクトップ版も出たことだし、必要性は自分も感じていました。この件だけ長期的な計画として進めます。

@capsicum

github.com

デッキ表示: アカウントに依存せず複数カラムを並べて表示できるようにする(SubwayTooter 風・遠い将来) · Issue #720 · pooza/capsicum

要望(遠い将来向け) SubwayTooter のような、アカウント関係なくカラムを並べられる機能があると便利。 報告元: karasu_sue 氏 https://pf.korako.me/post/19420 (#capsicum 要望) 報告者自身が「遠い将来に向けての要望」と明記 概要 複数のタイムライン/通知/リスト/ハッシュタグ等を、ログインアカウントの枠を越えて任意のカラムとし...

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.36

1.36.1 github.com/pooza/capsicum/rele
1.36.0 github.com/pooza/capsicum/rele

◆公開状況

公開済み: Android, Windows, Linux, macOS
1.36.0まで公開済み: iOS

1.36.1で修正したのは、サポーターバッジの保存先をサーバー側に変更した修正に関する不具合。
既にサポーターの方には大きな問題はないと思います。

◆変更点

特に1.30.0で、不具合や未実装項目への細かな修正を多く行いました。
詳細は上記リンク先参照。

◆直近のロードマップ

1.37から1.38にかけて、デスクトップでのナウプレまわりを改善します。
モロヘイヤがあるサーバーではいい感じに、ないサーバーでもそこそこ動くようにします。

以下、ナウプレ全体の計画書。
github.com/pooza/capsicum/blob

@capsicum

github.com

capsicum/docs/nowplaying-design.md at main · pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@matt@oslo.town · Reply to Mastodon Engineering

@MastodonEngineering Shout out to the 43 contributors! 👏 Thank you for your hard work. 🙇

Grid of circular contributor avatars showing a mix of photos, illustrations, and icons. The title reads "Contributors" and the text below the face pile reads "mjankowski, ThisIsMissEm, and 41 other contributors" – its a screenshot from GitHub.
ALT text

Grid of circular contributor avatars showing a mix of photos, illustrations, and icons. The title reads "Contributors" and the text below the face pile reads "mjankowski, ThisIsMissEm, and 41 other contributors" – its a screenshot from GitHub.

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.35

github.com/pooza/capsicum/rele

◇ 公開状況
公開済み: Android, Windows, Linux
審査提出済み: iOS, macOS

◇ 変更点

ワードサジェスト:
絵文字ピッカーの機能を拡張。
プリキュアとダイの大冒険の劇中用語や担当声優さんの名前などを素早く入力できます。
添付の動画ご覧ください。

実況用途を想定していますが、入力の速さだけでなく、普段の投稿でも、劇中用語を「正しい表記で入力する」ことにも役立つと思います。

長年育成してきたハッシュタグ辞書を拡張した、ワードサジェスト辞書をソースとしています。
プリキュアは3,000ワード、ダイ大は1,000ワードほどの用語を収録しています。

最新のモロヘイヤ(5.26)と、ワードサジェスト辞書のセットアップが必要です。
この入力をキーボードだけで行えるように、引き続き改善していきます。

@capsicum

@applech2@rss-mstdn.studiofreesia.com
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to ぷーざ
@matt@oslo.town · Reply to Mastodon Engineering

@MastodonEngineering Shout out to the 43 contributors! 👏 Thank you for your hard work. 🙇

Grid of circular contributor avatars showing a mix of photos, illustrations, and icons. The title reads "Contributors" and the text below the face pile reads "mjankowski, ThisIsMissEm, and 41 other contributors" – its a screenshot from GitHub.
ALT text

Grid of circular contributor avatars showing a mix of photos, illustrations, and icons. The title reads "Contributors" and the text below the face pile reads "mjankowski, ThisIsMissEm, and 41 other contributors" – its a screenshot from GitHub.

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to ぷーざ
:capsicum: capsicum 1.30

github.com/pooza/capsicum/blob

どうやら開発環境(Flutter)側のバグであろう…と疑われる不具合について、月初に「そのバグが果たして解決しているか?」という確認を行う運用を、5月から始めています。

明日から6月ですので、恐らく明日、その2回目の確認を行うと思います。

@capsicum

github.com

capsicum/docs/flutter-upstream-watch.md at main · pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@pooza@mstdn.b-shock.org · Reply to ぷーざ
:capsicum: capsicum 1.30

午前中にリリースしました!

◇iOS, macOS
AppStore 審査提出済み

◇Android, Windows, Linux
公開済み

github.com/pooza/capsicum/rele

◇主な更新
頂いたご要望を多く対応しました。

全プラットフォーム
・「サポーター」をロールとして表示

デスクトップ版全般
・動画再生
・画像トリミング
・ドラッグ&ドロップでメディア添付
・メディアファイルダウンロード
・マウスドラッグでスクロール(要設定)
・リアクションチップにマウスポインタを当てるとユーザー表示
・新バージョンの検知

Linux版
・ワンライナーインストーラ
capsicum.shrieker.net/desktop/

◇近々の予定(ピックアップ)

以下の変更は後日。
・画像トリミング、スマホ対応(むしろスマホの方が用途多そう)
・メディアファイルダウンロード、スマホ対応
・デスクトップむけの通知機能
・「サポーター」バッジの保管場所をサーバー側に変更する

直近の更新(1.31)
・基本的な操作(fav, ブースト等)をタッチで行えるように
(モバイルでの誤操作を嫌い、あえて長押し操作で設計していたところ、デスクトップ版の登場で前提が変わった)

@capsicum

capsicum.shrieker.net

デスクトップ版について - capsicum

capsicum project site

@gauteweb@mikrobloggen.no · Reply to Gaute ⚡ Holmin

Hvis du vil ha skriptet, så har jeg lagt det ut på :github:

Jeg har bare testet det på :fedora: men antar at det også vil funke på for eksempel "gaming-distroer" som for eksempel :bazzite: og :nobara: som jo er basert på Fedora.

github.com/Gauteweb/GNU-Linux/

github.com

GNU-Linux/update_fedora.sh at main · Gauteweb/GNU-Linux

Collection of Linux shell scripts and similar stuff - Gauteweb/GNU-Linux

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.29

◇リリース状況
全プラットフォームで公開済みです。

審査が停滞していたmacOS版を含め、です。
AppStoreに、審査の着手が遅れている場合に利用できる、「催促フォーム」的なものがあることを知りました。その効果は絶大で、入力後すぐに審査が始まりました。

◇リリースノート
github.com/pooza/capsicum/rele

主な変更点は、「お知らせ」通知です。

◇「お知らせ」通知
独自の拡張です。
通知のタイムラインには載らず、iOSとAndroidむけにプッシュ通知だけ送られます。また、サーバー側に最新のモロヘイヤ(5.24)が必要。
各デスクトップ版に通知機能自体が実装されたときに、デスクトップでも利用できるようになる予定。

「お知らせ」の露出をふやしたい意図から実装した機能ですが、煩わしい方は一応オフには出来ます。
大事なお知らせはなるべく読んでほしいですけどw

◇Linux版
この1.29を、一両日ぐらいでFlathub(Linuxむけのアプリストア)に申請します。
今朝はその申請のための、操作動画の撮影をしていました。
flathub.org/ja

@capsicum

flathub.org

Flathub - Linuxのアプリストア

Linux 用のアプリやゲームを探しインストールできます。Firefox、Telegram、RetroArch、GIMPまだまだあります!

@release_bot@mstdn.b-shock.org
@kev@fosstodon.org

FFS I cannot handle all these @Codeberg issues. Every time I go to do anything over the last week or so, it's shit the bed.

I know they're having SSH issues, so I switched to HTTPS, but I'm getting internal server errors using HTTPS too.

I'm so very close to switching back to .

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.28

1.28.0
github.com/pooza/capsicum/rele

1.28.1
github.com/pooza/capsicum/rele

Android, iOS, Windows版の1.28.1が、各ストアにて既に配信されています。
macOS版は1.26.0で止まっています。1週間以上放置されていてひどいです。

延び延びになってた、Misskey機能への対応(メッセージとページ)を進めました。

また、投稿フォーム(及び簡易投稿バー)に「キーボードをしまう」ボタンを追加しました。
自分が普段使っているAndroid版のATOKだと、キーボード上に格納のボタンがなかった為(iOS版にはある)、capsicum側に実装しました。
この新設ボタンの挙動にバグがあることがわかり、急遽リリースしたのが1.28.1であるという経緯です。

@capsicum

Release v1.28.1 · pooza/capsicum

v1.28.0 リリース後に把握した不具合のホットフィックス。v1.28 の主目的機能 (#438 Misskey chat ルーム / #186 Pages 読み取り) に直結する PR #603 の Codex P2 と、v1.28 同梱 #594「キーボードをしまう」ボタン余波の誤投稿バグをまとめて修正。 修正 #630 simple_post_bar のフォーカス時にボタン列が 1...

@release_bot@mstdn.b-shock.org
@kev@fosstodon.org

Ironically, since moving to @Codeberg I've had nothing but problems. I keep getting time outs and refused connections when pushing, and now the Pure Blog updater is broken because it can't pull from Codeberg.

No issues reported on their end, but it's definitely not a Pure Blog issue as I updated a number of sites yesterday.

I'm seriously considering a switch back to .

@ghostbyte@mastodon.social

We’ve set up a GitHub Sponsors page for Ghostbyte.

We spend a lot of our free time building and maintaining open-source software like @Pixelix and our other projects. If you’d like to support our work, you can now do so through GitHub Sponsors.

Every bit of support helps us continue working on our projects ❤️

github.com/sponsors/ghostbyte-

github.com

Sponsor @ghostbyte-dev on GitHub Sponsors

We are a small software development studio and love to develop open source projects. We may be known for the Pixelfed client Pixelix.

@wlaatje@social.edu.nl
@release_bot@mstdn.b-shock.org
@smallcircles@social.coop

Ha, is hacked and its own internal repo's have apparently been stolen. You can buy the source code, or it becomes public if no one buys. It was done via a malicious extension via a supply-chain attack of an obscure syntax highlighter via auto-update.

youtube.com/watch?v=9tcLy9TnPDU

youtube.com

Github’s Wildest Hack Yet

PlanetScale is the fastest and most reliable way to run Postgres and MySQL in the cloud. Combined with sharding, branching, and Query Insights, you'll spend ...

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.27

github.com/pooza/capsicum/rele

iOS / Androidから投げ銭できる様になりました。投げ銭以外にも、こまごま修正してます。

Android:
GooglePlay 公開済み

iOS:
AppStore 審査提出済み

macOS:
AppStore 審査提出済み

Windows:
Microsoft Store 審査提出済み
GitHub MSIX公開済み

Linux:
GitHub AppImage公開済み

投げ銭による「サポーターフラグ」、いまのところは端末に保管されますが、近々に通知サーバーに保管するように変更します。
「サポーターフラグ」はいまのところ、プロフィール画面にcapsicumアイコンが表示される以外の効果はございません。(そのうち何かお返しするかも知れません)

@capsicum

Release v1.27.0 · pooza/capsicum

サポーター(投げ銭)機能の追加を主目的とした大更新リリース。あわせて Microsoft Store での公開と、v1.26 で出荷した Annict 連携・コマンド機能まわりのユーザー要望を取り込んだ。 サポーター(投げ銭) #428 capsicum を任意で支援できる「投げ銭」機能を追加。設定 →「capsicum をサポート」から。機能の違いはなく、装飾のサポーターバッジが付きます...

@release_bot@mstdn.b-shock.org
@wlaatje@social.edu.nl
@pablolarah@mastodon.social

🕵️ Investigating unauthorized access to GitHub’s internal repositories
by Alexis Wales @github
If any impact is discovered, customers will be notified via established incident response and notification channels.

github.blog/security/investiga

White text "Investigating unauthorized access to GitHub’s internal repositories" on red background with illustration of woman with telescope and boat from the Costumes Parisiens, No.164: Costume de Yacht from Journal des Dames et des Modes (1914) fashion illustration in high resolution by George Barbier.
ALT text

White text "Investigating unauthorized access to GitHub’s internal repositories" on red background with illustration of woman with telescope and boat from the Costumes Parisiens, No.164: Costume de Yacht from Journal des Dames et des Modes (1914) fashion illustration in high resolution by George Barbier.

@Sempf@infosec.exchange
@pablolarah@mastodon.social

🕵️ Investigating unauthorized access to GitHub’s internal repositories
by Alexis Wales @github
If any impact is discovered, customers will be notified via established incident response and notification channels.

github.blog/security/investiga

White text "Investigating unauthorized access to GitHub’s internal repositories" on red background with illustration of woman with telescope and boat from the Costumes Parisiens, No.164: Costume de Yacht from Journal des Dames et des Modes (1914) fashion illustration in high resolution by George Barbier.
ALT text

White text "Investigating unauthorized access to GitHub’s internal repositories" on red background with illustration of woman with telescope and boat from the Costumes Parisiens, No.164: Costume de Yacht from Journal des Dames et des Modes (1914) fashion illustration in high resolution by George Barbier.

@aral@mastodon.ar.al

RE: techhub.social/@Techmeme/11660

Remember this whenever you hear claims that your data is secure on some system or other that you do not own and control.

Like all that additional data governments want to gather via the slippery slope of “age verification” in the EU.

The only data that is actually secure on a third party is data you haven’t shared with the third party.

Hence: data minimisation.

Had I mentioned GDMR yet today? Because I feel I might have. But hey, here it is again:

ar.al/2018/11/29/gdmr-this-one

ar.al

GDMR: this one simple regulation could end surveillance capitalism in the EU

GDMR: The regulation EU citizens deserve. No, you didn’t misread it and, no, it’s not a typo. GDMR – the General Data Minimisation Regulation – can end surveillance capitalism in the EU. The problem is that no such regulation exists. So, let’s change that, starting now. To be effective, GDMR must be succinct and precise. The essence of it can be expressed in a single article with two paragraphs:

This quote was not authorized by the quoted post's author.

@0xabad1dea@infosec.exchange

info on the github breach appears to only be available on xitter 🙄 , I fished it out for you.

post from github on May 20th, 2026:

We are sharing additional details regarding our investigation into unauthorized access to GitHub's internal repositories.

Yesterday we detected and contained a compromise of an employee device involving a poisoned VS Code extension. We removed the malicious extension version, isolated the endpoint, and began incident response immediately.

Our current assessment is that the activity involved exfiltration of GitHub-internal repositories only. The attacker’s current claims of ~3,800 repositories are directionally consistent with our investigation so far.
ALT text

post from github on May 20th, 2026: We are sharing additional details regarding our investigation into unauthorized access to GitHub's internal repositories. Yesterday we detected and contained a compromise of an employee device involving a poisoned VS Code extension. We removed the malicious extension version, isolated the endpoint, and began incident response immediately. Our current assessment is that the activity involved exfiltration of GitHub-internal repositories only. The attacker’s current claims of ~3,800 repositories are directionally consistent with our investigation so far.

@haeckerfelix@mastodon.social

The current state of GitHub is just sad. And I’m not even talking about "more advanced" features like GitHub Actions.

No, I’m referring to things like simply viewing and navigating the code in the browser.

It’s not uncommon for the page to freeze or take an age to load when I switch between files, and I have to click the "Refresh" button in the browser to get the page finally to load.

And it’s been like that for a while now...

@pooza@misskey.delmulin.com
@pooza@mstdn.b-shock.org · Reply to 🦜狩生 :fedibird1:
@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.26

昨晩公開しました。
github.com/pooza/capsicum/rele

◇Android
GooglePlay 公開済み

◇iOS
AppStore 公開済み

◇macOS
AppStore 審査中

◇Linux
GitHubに公開済み。

インストール手順
github.com/pooza/capsicum/blob

◇Windows
GitHubに公開済み。

初回インストール手順
github.com/pooza/capsicum/blob

簡易なAnnictクライアントを実装。「実況後にその場で感想を書く」までの流れを網羅しました。
アニメ視聴におけるFedi活用という、自鯖本来のテーマを補強した、満足できるリリースとなりました。

最近力を入れてるデスクトップ版も、「iOS版をためしにMacで実況に使ってみたら、意外とよかった」経験に由来してます。
そちらでは成果を出せているものの、もとがスマホアプリなものだから、デスクトップアプリとして見ると色々足りないところが見えてきますね。
引き続き改善していきます。

これらの、自分が熱心に改善している機能の大半にモロヘイヤが必要になってて。つまり、概ね「自鯖じゃないと動かない」状況になってます。
元々、capsicumを起点とした総合的な体験を、鯖缶の立場から提案しているという立場だったけど、その難しさも改めて感じてますね。

以上、最近の所感。
引き続きご活用の上、ご意見くれると嬉しいです。

@capsicum

github.com

capsicum/packaging/windows/INSTALL.md at main · pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@pooza@mstdn.b-shock.org · Reply to オルー:gome_onemu:
@release_bot@mstdn.b-shock.org
@mikaeru@mastodon.social
@applejag@fosstodon.org

Code is getting more decentralized thanks to people moving away from , which is great

What we are missing however is a good search engine so projects stay discoverable. Maybe ranking repos based on how often they are used, and universal "repo labels" search

If @forgefed ever becomes production ready, then we could maybe combine this with stats for decentralized repo stars too

I hope search engine providers (hopefully @kagihq) are looking at this. Potential killer feature

@pooza@mstdn.b-shock.org
:capsicum: ドキュメント更新(Annict対応、Spotifyナウプレ対応、デスクトップ通知)

◇Annict 感想投稿対応
使うのは自分しかいないかもしれないがw、モロヘイヤ巻き込んでずっと前から準備していた。
1.26に含まれる予定。
github.com/pooza/capsicum/blob
エア番組の説明吹いたw

◇Spotify ナウプレ対応
既存のナウプレ機能はOSの機能に依存しており、Linux版とWindows版では動作しない。
その代替で、こちらはOS問わず動かせる仕組みのはず。
まだ設計段階。
github.com/pooza/capsicum/blob

◇デスクトップ版の通知機能
Linux版で通知対応が抜けていることがわかり、その代替の設計。
macOS, Windowsでも通知の副ルートとして活用。
これもまだ設計段階。
github.com/pooza/capsicum/blob

github.com

capsicum/docs/desktop-notification-design.md at 114669f16bff4605cb3bff9daf703b5cf36185be · pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@irfan@sakurajima.social

I've self-hosted my own server for a while now and it's been such a freaking delight to work with, and gives me some relief that my code/ repos have a place outside of . When I started this however, I couldn't fully migrate everything I had to Forgejo - as some were still tied to GitHub's actions and their hosted runners. Before I could migrate them, I'd need to set up runners of my own on the Forgejo server.

Seeing GitHub's rapid deterioration lately, I resumed my search on setting up runners on Forgejo the
right way, and was initially under the impression that it's gonna be complicated... but as it turns out, it really isn't. I set up a simple runner on a remote I had using (Compose) and it was ready to go. Porting my actions/workflows files were super easy too, unlike doing the same for something like . Now all of my repos that were on GitHub and had some CI/CD set up have been migrated to my Forgejo server, using my own runners.

I've updated my
Wiki topic on Forgejo to include the optional step to set up a Forgejo runner. If you're now only considering deploying Forgejo, feel free to check out the rest of the topic which covers the complete setup, some basic recommended configurations, and even how to migrate your repos to Forgejo and set up push mirroring so they still exist on GitHub (if you choose to).

🔗 https://github.com/irfanhakim-as/homelab-wiki/blob/master/topics/forgejo.md#forgejo-runner

github.com

homelab-wiki/topics/forgejo.md at master · irfanhakim-as/homelab-wiki

Wiki about everything Homelab. Contribute to irfanhakim-as/homelab-wiki development by creating an account on GitHub.

@pooza@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to ぷーざ
:capsicum: リノートの取り消し

@capsicum

こちらがタッチ操作に関するissue。

github.com/pooza/capsicum/issu

補足しますと。

自分が避けたかった「誤操作」のひとつとして、Mastodon のWebUI にある、ブックマークアイコンの誤タッチがあります。
モロヘイヤがあるサーバーでは、ブックマーク操作により、PieFed へのブックマークという重めの処理も走る。

ユーザーがモロヘイヤ上で、「PieFed連携を有効にしているか?」という判定が必要。
今までcapsicumでは、ユーザーごとのモロヘイヤでの設定を取得する必要がなかったが、これが必要になった。

元々次バージョン(1.26)では、Annictへの感想投稿の機能追加が予定されていたところ。
こちらでも「Annict連携を有効にしているか」を判定する必要があるので、「ユーザーのモロヘイヤでの設定を取得する」枠組みがここで整理されます。

github.com

タイムライン上の各投稿へのタッチ操作を設定で有効化できるようにする · Issue #565 · pooza/capsicum

概要 タイムライン上の各投稿に対する基本操作(リプライ・お気に入り・リアクション・ブースト/リノート・ブックマーク・引用)を、設定で有効化したときだけタッチ操作可能にする。 背景 現状は誤タッチ防止のため、これらの操作はすべて長押しメニュー(または右上の「…」ボタン)からのみアクセス可能としている。 ポケットの中で WebUI のボタンがいつの間にか押される事故 操作中に指がブックマークボタ...

@pooza@mstdn.b-shock.org
:capsicum: リノートの取り消し

github.com/pooza/capsicum/issu

@ore_orue からのご報告、ありがとうございました。
手元の開発版では実装済み。次バージョン(1.26)に含められる見込みです。

リノートに、Mastodon (ブースト)との違いが意外と色々あります。
・リノートは繰り返し実行できる。
・ブーストはデフォルトではまとめて表示される。その場合、タイムライン上にもう1通流れてこない。

リノートは繰り返せるから、リノート元ではなく、リノート先(リノート自体)からの取り消し操作であるべき。
一方、ブーストはまとめ表示される可能性があるから、ブースト元からも取り消し操作ができないといけない。

この違いを踏まえた実装になってます。

また、この報告から派生して、「基本的な操作はタッチから実行できないか」という要望も出ています。

タッチ操作が出来ないのは「モバイルに由来する誤操作を防ぐ」という、当初からある基本設計であるところ。
デスクトップ版の登場により、この前提が成り立たなくなってます。基本設計の見直しということで、大きな課題としてじっくり丁寧に取り組むことになりました。

github.com/pooza/capsicum/issu

結果、ロードマップとしても、今ある課題の中では最後尾になってます。

@capsicum

github.com

タイムライン上の各投稿へのタッチ操作を設定で有効化できるようにする · Issue #565 · pooza/capsicum

概要 タイムライン上の各投稿に対する基本操作(リプライ・お気に入り・リアクション・ブースト/リノート・ブックマーク・引用)を、設定で有効化したときだけタッチ操作可能にする。 背景 現状は誤タッチ防止のため、これらの操作はすべて長押しメニュー(または右上の「…」ボタン)からのみアクセス可能としている。 ポケットの中で WebUI のボタンがいつの間にか押される事故 操作中に指がブックマークボタ...

@hopland@snabelen.no

To me, is the future. In many different avenues of digital services, it's usually a monopolistic vendor lock-in situation. is no exception, nor is .

But Forgejo aims to be a git system that uses to communicate with other git instances - in effect decentralizing code repos, and even possibly CD/CI chains. Hold on to your hats, folks.

itsfoss.com/news/netherlands-f

itsfoss.com

Go Away Microsoft! The Netherlands is Quietly Building Its Own GitHub Replacement

The self-hosted, FOSS-only platform is still in the pilot phase, but government agencies are already signing up.

@pikesley@mastodon.me.uk
XKCD #303 UPDATED

THE #1 PROGRAMMER EXCUSE FOR LEGITIMATELY SLACKING OFF:
"GITHUB'S FUCKED AGAIN”

HEY! GET BACK TO WORK! 

GITHUB!

OH, CARRY ON
ALT text

XKCD #303 UPDATED THE #1 PROGRAMMER EXCUSE FOR LEGITIMATELY SLACKING OFF: "GITHUB'S FUCKED AGAIN” HEY! GET BACK TO WORK! GITHUB! OH, CARRY ON

@pooza@mstdn.b-shock.org
:capsicum: capsicum 1.25

RE: mstdn.b-shock.org/@release_bot

前バージョンで見送ったWindows版を公開しました。まだストア公開はしていないので、実験的機能の位置づけです。
このため、インストール手順は煩雑なので、手間をかけても構わない方だけお試しください。

◇Android版
GooglePlay公開済み

◇iOS版
TestFlight公開済み
AppStore審査提出済み
早期ベータを試したい人はその旨 @pooza までお知らせください。

◇macOS版
TestFlight公開済み
AppStore審査提出済み
早期ベータを試したい人はその旨 @pooza までお知らせください。

◇Linux版
github.com/pooza/capsicum/rele
上記のリンクからダウンロードしてください。
Flathub審査提出準備中。
日本語入力はIBusにのみ検証済み。fcitx / uimで不具合が起きていたら、その旨 @pooza までお知らせください。

◇Windows版 New!
github.com/pooza/capsicum/rele
上記のリンクからダウンロードしてください。
Microsoft Store審査提出準備中。

@capsicum

Release v1.25.0 · pooza/capsicum

Windows ⚠️ 「煩雑な証明書インポートをいとわない」ユーザー様むけの実験的機能です。 #423 Windows MSIX 配布パイプライン (Phase 1〜5 / 自己署名 PFX / GitHub Releases 直配) #483 Windows 実機 (Parallels VM) で OAuth / ファイル選択 / 投稿の動作確認 インストール手順 Microsoft ...

This quote was not authorized by the quoted post's author.

@release_bot@mstdn.b-shock.org
@hugovk@mastodon.social

RE: code4lib.social/@acdha/1165588

Do not use pull_request_target.
Do not use caches in publish workflows.
Use dependency cooldowns.
Use Zizmor.
Tell GitHub to make Actions secure by default.

code4lib.social

Chris Adams (@acdha@code4lib.social)

This should have everyone rethinking their use of GitHub Actions: https://tanstack.com/blog/npm-supply-chain-compromise-postmortem

This quote was not authorized by the quoted post's author.

@release_bot@mstdn.b-shock.org
@hopland@snabelen.no

To me, is the future. In many different avenues of digital services, it's usually a monopolistic vendor lock-in situation. is no exception, nor is .

But Forgejo aims to be a git system that uses to communicate with other git instances - in effect decentralizing code repos, and even possibly CD/CI chains. Hold on to your hats, folks.

itsfoss.com/news/netherlands-f

itsfoss.com

Go Away Microsoft! The Netherlands is Quietly Building Its Own GitHub Replacement

The self-hosted, FOSS-only platform is still in the pilot phase, but government agencies are already signing up.

@pooza@mstdn.b-shock.org · Reply to ぷーざ

github.com/pooza/capsicum/issu

提出書類で、文言をiOSからの使い回しにした為に実態と合ってなかった。

ログイン時に「詰まる」問題は、「Android端末でのみ発生するFlutter由来の問題」と概ね切り分けられており、Android版でしか発生しないことがわかっている。
iOS版の審査の頃はそこまで切り分けが進んでいなくて、提出書類にAndroid版でしか起きない不具合のことも書いてしまっていた。

github.com

ログイン画面から遷移しない場合がある · Issue #276 · pooza/capsicum

報告元 https://precure.ml/@cureishimatsu/116341712193361964 内容 Android 版でログイン画面から先に遷移しない場合がある。iOS 版では発生しない。 詳細な再現手順は不明。端末情報も未確認。 備考 同ユーザーから v1.9.0 時点で報告。最新バージョンでの再現確認が必要。

@release_bot@mstdn.b-shock.org
@cassidy@blaede.family

I guess the GitHub front-end is just… garbage now? Like I knew it was having issues as the org has dwindled under Microsoft and their Copilot obsession, but hoo-boy this has become one of the most unreliable services I use.

I filed half a dozen issues on a tiny repo last night, and the app and website both just showed that no issues existed on the repo for a few *hours* afterwards. Their status site showed an ongoing incident, so I went to bed.

@pooza@misskey.delmulin.com
@f800gecko@mastodon.online

Small steps:

Recently, I moved from VS Code to VS Codium (same app sans Microsoft surveillance - see vscodium.com/).

This morning, I migrated from github to Codeberg (codeberg.org/), integrating the latter with VS Codium (this move negating MS github surveillance).

With minor issues resolved (mostly due to my own noobness with all this stuff), all good.

Fellow coders: PM if you'd like details - happy to help if able.

@pluralistic

codeberg.org

Codeberg.org

Codeberg is a non-profit community-led organization that aims to help free and open source projects prosper by giving them a safe and friendly home.

@knoppix95@mastodon.social
@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@GripNews@mastodon.social

🌘 開源並不意味著開放社羣
➤ 從軟體維護者的過勞與覺醒,談開源精神的本質
✤ blog.feld.me/posts/2026/04/ope
這篇文章犀利地指出,現代開源開發模式已從單純的代碼共享,演變為對維護者極具壓迫感的「無薪工作」。作者回顧了早期開源軟體那種純粹、低互動的運作模式,並對比了 GitHub 等平臺帶來的負面影響:無止盡的 Pull Requests、繁瑣的溝通需求、以及被要求處理社羣政治的過度負擔。作者呼籲開發者重拾自主權,不必為了「公開透明」而犧牲個人生活,將開源回歸到創作的初心。
+ 這篇文章說中了我作為維護者的痛點!我開發專案是為了樂趣,而不是為了免費當數百人的客服經理。
+ 作者過於激進了。雖然開源治理很累,但開源社羣帶來的協作效應與漏洞修補,仍是現代軟體穩定性的關鍵。

blog.feld.me

Open Source Does Not Imply Open Community

Open source software has existed long before the invention of the (D)VCS. The author likely hosted a barebones HTML webpage or a txt file describing the project. There definitely was an FTP server somewhere with tarballs. The author may have been reachable by email. If you were really lucky …

@pooza@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to ぷーざ
@pooza@mstdn.b-shock.org
capsicum 1.22

RE: mstdn.b-shock.org/@release_bot

◇公開状況
Android: GooglePlay公開済み
iOS: AppStore審査提出済
macOS: AppStore審査提出済

◇主な更新
github.com/pooza/capsicum/mile
・Misskeyの「メッセージ」(旧「チャット」、DMの後継機能)
・Misskey チャンネルのタブ化
・Misskey ドライブ改善
・アイコン丸角切り替え
等など

◇Misskey メッセージ
実装を始めました。
とても機能が多く、グループチャット等、未実装機能が多くあります。
Msskeyで「メッセージ」を使う人は、再ログインが必要です。

◇macOS版
前バージョン(1.21)から審査に出してますが、なかなか審査が始まりません。審査の長期化が予想されます。
テスト版を試してみたくて、メールアドレスを管理人に教えても構わない人は、連絡ください。

@capsicum

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

This quote was not authorized by the quoted post's author.

@release_bot@mstdn.b-shock.org
@Edent@mastodon.social · Reply to Terence Eden
@pooza@mstdn.b-shock.org
@britter@chaos.social

GitHub recently announced that starting with v2.91.0 GitHub CLI will start sending pseudonymized telemetry data back to GitHub.

github.blog/changelog/2026-04-

Since this is an opt-out feature, most users will have it activated without knowing it. This is unacceptable in my opinion. So I took the liberty of turning this into an opt-in, disabled by default for nixpkgs.

github.com/NixOS/nixpkgs/pull/

github.com

gh: opt out of telemetry collection by default by britter · Pull Request #515047 · NixOS/nixpkgs

Starting with release 2.91.0 gh sends pseudonymized telemetry data to GitHub. Disabling it requires and explicit opt-out. Context: https://github.blog/changelog/2026-04-22-github-cli-opt-out-usage-...

@villares@ciberlandia.pt
@hamoid@genart.social · Reply to aBe

Done. The 108 repositories I had in are all gone.

I'm still in 6 organizations there. I will try to move at least 2 of them away.

If there's something I do not like and I can do something about it, I do it.

I think we can vote not only on election day, but every day by choosing tools and services that align with our values.

A screenshot of GitHub with the text "hamoid doesn't have any public repositories yet."
ALT text

A screenshot of GitHub with the text "hamoid doesn't have any public repositories yet."

@qiita@rss-mstdn.studiofreesia.com
@pooza@mstdn.b-shock.org
capsicum 1.21

github.com/pooza/capsicum/rele
github.com/pooza/capsicum/issu

iOS / Android共公開済み。
多くのユーザー様には、簡易投稿バーに絵文字パレットが追加されたことが最大の改善点でしょう。
絵文字パレットは全サーバー共通にしてしまった為、実際に試すとショートコードが表示されたりもしてますね。
現時点でも実用性はあると思いますが、引き続き改善します。

他、多くの安定性向上の修正を行ってます。

デスクトップ化計画の第一段階として、Macネイティブ版を実装しました。
iOS版をMacで試したら、実況との相性が意外と良かったことがプラットフォーム拡大の動機になってて、このあと引き続き、Windows, Linuxと順に対応していきます。
ダメ元でMac版を試したら、あっさり動画再生までできてて、意外にも実用性のあるものになっています。

Mac版の早期テスト版の実行をご希望で、私にメールアドレスを教えても構わない方は、ご連絡ください。

@capsicum

github.com

Issues · pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@pooza@mstdn.b-shock.org · Reply to ぷーざ
@sethmlarson@mastodon.social

Workflow security continues to be a common cause of compromises of open source projects.

If you're using GitHub Actions and don't want this to happen to your project: use Zizmor and treat the findings seriously, especially insecure triggers and user-controllable template injections.

docs.zizmor.sh

docs.zizmor.sh

Welcome to zizmor's documentation! - zizmor

Static analysis for GitHub Actions

@pooza@mstdn.b-shock.org
:capsicum: Misskeyでの猫化、アバターの丸角

github.com/pooza/capsicum/issu

「タイムライン上の各々のユーザーは、Misskeyサーバーのユーザーか?」を表示の度に判定するコストが馬鹿にならない。
各ユーザーの猫判定はキャッシュされていて、キャッシュを読むだけなら比較的コストが低い。

Mastodonログイン中は、猫判定をそのまま丸アバター表示の判定に使うことにする。

◇1.21での表示
Mastodonログイン中: 猫判定されたアカウントは丸アバター、それ以外は角アバター。
Misskeyログイン中: すべて丸アバター。

◇1.22での表示
以下の3モードを新設
自動: 1.21と同じ(デフォルト)
丸: すべてのユーザーが丸アバター
角: すべてのユーザーが角アバター

@capsicum

github.com

アカウントアイコンの形状(丸 / 角)を切り替え可能にする設定を追加 · Issue #372 · pooza/capsicum

背景 現状の capsicum はアカウントアイコンを丸形でレンダリングしているが、角(元画像の形)で表示したいユーザー要望がある。Mastodon / Misskey いずれのサーバーもアカウントアイコンの原画像は四角で保持されており、クライアント側で丸くマスクしているだけなので、設定で元の形に戻せる余地がある。 関連トピック: ユーザー報告 https://misskey.delmuli...

@pooza@mstdn.b-shock.org · Reply to オルー:gome_onemu:

@ore_orue @capsicum

確かに、ファイルサイズが少し大きかった旨の記録はあります。
Misskey本来のデフォルト上限は250MBだそうですが、記憶と相違ないですか?

ダイスキーのサーバー移転は一応予定にありますが、現在は上限値を緩和できる状況ではなく、一般的な用途を想定しているであろうMisskeyのデフォルトも妥当だと思いました。

github.com/pooza/capsicum/issu
ファイルサイズの検査は有効な改善なので、いずれにしてもこれは入れます。

github.com

アップロード前にサーバーの最大ファイルサイズを取得して事前エラーを返す · Issue #375 · pooza/capsicum

背景 現状 capsicum はメディア添付時にアップロード前のファイルサイズチェックを行っておらず、サーバーが 413 / 422 / 400 等を返して初めて失敗が判明する。ユーザー体感が悪く、通信量も無駄に消費する。 ダイスキー (misskey.delmulin.com、Misskey デフォルト 250MB) でユーザー報告あり: https://misskey.delmulin....

@codewizard@hear-me.social

@FediFollows you ought to include the contacts of champions like the of like , of some prime instances, instances, , and email services like and .

That way, we would be able to reach out to them through whenever we need their support.

This informal channel is oftentimes better than your regular email.

@release_bot@mstdn.b-shock.org
@codefloe@social.tchncs.de

We have fixed some recent issues with our Pages integration. You should now be able to easily configure a static website again right from your repo settings!
Including custom domain configuration and a super fast proxy backend.

Private and GDPR compliant, thanks to statichost.eu!

Give it a try, especially when you're searching for a new home for your pages site!

@0xabad1dea@infosec.exchange

hey "haha github uptime lol" and all that but this is serious: some pull request merges were completely mangled yesterday and the repo may not be in the state that its maintainers expect. If your project processed any updates yesterday, please double-check githubstatus.com/incidents/zsg

githubstatus.com

Incident with Pull Requests

GitHub's Status Page - Incident with Pull Requests.

@pooza@mstdn.b-shock.org · Reply to ぷーざ
@release_bot@mstdn.b-shock.org
@smallcircles@social.coop · Reply to Shawn Webb

@lattera

is known to be quite resource hungry.

Perhaps you can have a look at which is implemented in , and the is very similar to 's.

forgejo.org

And is hosted on forgejo, and maintain a downstream fork, optimized for high-scale use, which is also open source.

codeberg.org

Some large projects have migrated from GH and GL before, and created migration reports, etc. The other day I was asking if there's a list of those, I am not sure there is.

CC @forgejo and @Codeberg

codeberg.org

Codeberg.org

Codeberg is a non-profit community-led organization that aims to help free and open source projects prosper by giving them a safe and friendly home.

@lattera@bsd.network · Reply to Shawn Webb

I'm 100% out of ideas. Our servers cannot handle the load the AI/LLM web scraping bots place on . is turning out to still not be ready for prime-time. I refuse to use beyond being a read-only mirror.

Self-hosting our code repos is an absolute requirement in order to provide higher levels of OPSEC than what third-party hosted services can provide.

So, at the hands of our oligarchic overlords, is this the death of HardenedBSD?

Someone please provide me ideas. I have no idea what to try next and I'm desperate.

@release_bot@mstdn.b-shock.org
@lattera@bsd.network · Reply to Shawn Webb

I'm 100% out of ideas. Our servers cannot handle the load the AI/LLM web scraping bots place on . is turning out to still not be ready for prime-time. I refuse to use beyond being a read-only mirror.

Self-hosting our code repos is an absolute requirement in order to provide higher levels of OPSEC than what third-party hosted services can provide.

So, at the hands of our oligarchic overlords, is this the death of HardenedBSD?

Someone please provide me ideas. I have no idea what to try next and I'm desperate.

@hugovk@mastodon.social

The newest gh CLI has added telemetry:

"As agentic adoption of GitHub CLI grows, our team needs visibility into how features are being used in practice."

Opt out with any of these:

export GH_TELEMETRY=false # any falsy value: 0, false, disabled

export DO_NOT_TRACK=true

gh config set telemetry disabled

cli.github.com/telemetry
github.com/cli/cli/releases/ta

Edit: Here's a script to set the env vars for GitHub Actions in your orgs and user repos: github.com/hugovk/github-tools

github.com

github-tools/disable_gha_telemetry.py at main · hugovk/github-tools

Command-line Python scripts to do things with GitHub. - hugovk/github-tools

@ore_orue@misskey.delmulin.com
@pooza@mstdn.b-shock.org · Reply to ぷーざ
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
capsicum 1.19.1

プッシュ通知の実装が長期化しています。

github.com/pooza/capsicum/rele

このバージョンで通知周りを完成させるつもりが、まだそこまでは届いてません。
プッシュ通知との関連から、「すべての通知」画面の改善なども併せて行ってます。
左上のベルアイコンも、リンク先を「すべての通知」に変えました。(長押しで、以前通り単アカウントの通知画面も選べる)

以下は次バージョンに持ち越しです。

github.com/pooza/capsicum/issu
通知文面を詳細化(暗号化された通知の復号が必要)

github.com/pooza/capsicum/issu
通知の宛先が誤っているケース。

github.com/pooza/capsicum/issu
Misskeyはサードパーティクライアントに対して、セキュリティ上の理由からプッシュ通知の利用を禁じた経緯があった模様。
この問題についても、モロヘイヤ併用で慎重に解決。

@capsicum

github.com

Misskey プッシュ通知: サードパーティアプリから登録できない upstream 制約への対応検討 · Issue #355 · pooza/capsicum

背景 Misskey upstream は GHSA-7pxq-6xx9-xpgm(2023-12)で /api/sw/register に secure: true を適用しており、MiAuth / OAuth 由来のアクセストークンからは HTTP 400 ACCESS_DENIED になる。capsicum を含むサードパーティアプリは Web Push 登録 API を直接叩けない。...

@davidak@chaos.social

The developers concluded after 10 years that it is not able to host its own development and that they depend on .

github.com/go-gitea/gitea/issu

At the same time, the community fork @forgejo is self-hosted for a long time and is also powering the popular @Codeberg and at least 8 other public instances. So this seem to be a good time to migrate if you haven't already.

forgejo.org

forgejo.org

Forgejo – Beyond coding. We forge.

Forgejo is a self-hosted lightweight software forge. Easy to install and low maintenance, it just does the job.

@toxi@mastodon.thi.ng

RE: hachyderm.io/@thomasfuchs/1164

"These long-running, parallelized workflows can yield great value, but they have also challenged our infrastructure and pricing structure: it’s now common for a handful of requests to incur costs that exceed the plan price! These are our problems to solve. The actions we are taking today enable us to provide the best possible experience for existing users while we develop a more sustainable solution." — Joe Binder, VP of Product

If people are already _commonly_ exceeding set monthly quotas/costs with just a handful of requests, you all have got much bigger problems, customers/users too (i.e. becoming deeply dependent on externally controlled & rented infrastructure from day one of your project/startup, plus slowly damaging your own cognitive abilities and a fast growing maintenance nightmare)! And this all is just the beginning... 🍿

Keeping up with other news about growing mineral, energy & supply chain shortages, the illusion that this might just be very short term, and the resulting cost bumps needed to produce and provision all the outstanding data center capacities at the heart of the above decisions (and similar ones made by Anthropic just days ago), I really don't understand where this optimism of AI boosters/users is coming from or on what planet they're living on...

genAI/agenticAI is a shoddily implemented/managed/secured technology & mentality for a computing-illiterate consumerist society, for an age of infinite resource abundance with stable climate/politics, all of which we're leaving (or have never really been in)! And that departure is partially driven/accelerated by said tech...

Instead of funneling trillions into this particular tech, we need focus/investment into methods, infrastructure, research/education, relationships, and above all, a culture focused on how to make computing magnitudes more sustainable, accessible, independent and which allows us to do generally more with less. Or, at least not with magnitudes more, just for some dubious, unspecified (and meaningless) measure of improved "productivity gains"... With almost no one ever questioning what this supposed extra productivity is even good for...

hachyderm.io

Human Brain Enthusiast (@thomasfuchs@hachyderm.io)

They're starting tightening the thumbscrews https://github.blog/changelog/2026-04-20-changes-to-github-copilot-plans-for-individuals/

The quoted post is no longer available.

@pooza@mstdn.b-shock.org
capsicum 1.18

github.com/pooza/capsicum/rele

Android: GooglePlay公開済み
iOS: AppStore審査提出済み

プッシュ通知を実装しました。
通知サーバの運用を開始しました。

capsicum.shrieker.net/push-not

次の1.19を通じた段階的な実装を計画しており、今の時点では多分に実験的な機能です。
通知が送られる様にはなっており、最難関のハードルはクリアできていそうです。一方、暗号化された通知の復号処理は、今回の対応に含まれていません。

1.18 とにかく新しい通知が届いたことだけ表示。
1.19 通知の内容にまで踏み込んだ表示。

その他、「Mastodonタイムラインにも猫化を反映」にも修正が加わっています。
ようやくこの機能を実用レベルに改善出来たと思ってます。

@capsicum

capsicum.shrieker.net

プッシュ通知について - capsicum

capsicum project site

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
capsicum 1.17

github.com/pooza/capsicum/rele

先程、AppStoreでも審査が通過し、GooglePlayと両ストアで公開となりました。

お知らせと通知をタブとして表示出来ます。(デフォルトは非表示)
この変更に伴って、タブの設定が雑然としてきたこともあって、以下の操作を整理しました。
・タブの表示・非表示切り替え
・タブの順序変更

また、サーバーをまたいだ猫化が出来ていないケースがあったので、改善しました。

次バージョンは、いよいよプッシュ通知をリリースしたいと思ってます。

@capsicum

Release v1.17.0 · pooza/capsicum

新機能 お知らせ・通知のタブ化 (#281) — タイムライン・リスト・ハッシュタグ・通知・お知らせを統一的に扱えるタブ管理基盤を導入。タブ管理シートから表示切替・並べ替えが可能。デフォルトでは非表示 タグサジェスト (#322) — 「削除してタグつけ」画面でタグ入力時にお気に入りタグ・SNSタグ検索から候補を表示 Misskey ログイン・トークン作成通知 (#318) — Missk...

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
capsicum 1.16

github.com/pooza/capsicum/rele
github.com/pooza/capsicum/mile

今朝確認したところ、AppStore, GooglePlay共公開済みですね。

プッシュ通知、まだ動きませんが実装は始めてます。
猫は「Mastodonからもみえるように」のつもりで進めていたけど、まだ不具合あるみたいです。要改善。

通知や猫対応は引き続き。
お知らせと通知をタブ化できるようにするあたりが、直近のトピックです。

@capsicum

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to オルー:gome_onemu:
@Radio_Azureus@ioc.exchange · Reply to Russ Sharek

I always ask similar questions like the following,

What will you do when you discover that the kernel of your favorite Operating System now gets programming assistance in any form of a power guzzling ocean warming large language model?

Will will you fork the kernel yourself? Do you have the programming capability

There are a lot of folk who are pissed off at Linus Torvalds, for allowing some of his maintainers to use large language models to assist in finding bugs.

The Head Programmer of the fantastic and Beautiful curl also uses a large language model in some form, to hunt for bugs, because both he and Greg from the Linux kernel, saw that the LLM used on GitHub is now suddenly much better at finding those pesky bugs.

Mind you, the only LLM I like is the one that runs locally on my low powered Android phone. That's a micro LLM

Thanks in advance for your response

@RussSharek

github.com/stevelaskaridis/awe

github.com

GitHub - stevelaskaridis/awesome-mobile-llm: Awesome Mobile LLMs

Awesome Mobile LLMs. Contribute to stevelaskaridis/awesome-mobile-llm development by creating an account on GitHub.

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
capsicum 絵文字関連

1.15で絵文字関連の修正を多く行っているので、その対応状況。

github.com/pooza/capsicum/issu
Unicode絵文字の大幅拡大。ゾンビにも対応。
いままでUnicode絵文字の検索ができなかったので、その対応も含め。

github.com/pooza/capsicum/issu
「最近使った絵文字」

github.com/pooza/capsicum/comm
絵文字を連続で入力できるように、ユーザーが能動的に閉じる(ドロワーの外をタップ)操作に変更。

github.com/pooza/capsicum/comm
Mastodon: カスタム絵文字が連続で入力された場合に、前後にスペース補完。

これ以降は後日対応、または保留。

github.com/pooza/capsicum/issu
投稿欄で : (コロン)が入力されたら、絵文字の補完。
デスクトップ版じゃないと現実的ではない気がする。

github.com/pooza/capsicum/issu
Mastodon: 絵文字の前後に半角スペースではなくゼロ幅スペースに変更できるように。

github.com/pooza/capsicum/issu
Misskey: 本文中の絵文字をタップしたとき、ショートコードのコピーかリアクションを選択。
この操作もデスクトップ版じゃないと現実的ではない。

github.com/pooza/capsicum/issu
Misskey: リアクションチップをタップした場合。

@capsicum

github.com

Misskey: リアクションチップのタップで同じリアクションを送る · Issue #311 · pooza/capsicum

概要 投稿に表示されているリアクションチップ(絵文字 + 件数)をタップすると、同じリアクションを送る機能。Misskey Web UI にある既存機能の移植。 未リアクション → そのリアクションを送信 同じリアクション済み → 取り消し 別のリアクション済み → 切り替え(Misskey は 1 投稿 1 リアクション制約) 優先度 低め。ユーザーにはリアクションを自分で選んで送ってほし...

@reiver@mastodon.social

Wow! All the trending repos on GitHub are AI related — except for the last one.

Even the repos that at first look like they might not be about AI, such as Microsoft's markitdown, are still related to AI.

One could interpret this as a snapshot of what a large chunk of the broader developer community is interested in.

( source: github.com/trending )

github trending

1. https://github.com/NousResearch/hermes-agent

2. https://github.com/shiyu-coder/Kronos

3. https://github.com/forrestchang/andrej-karpathy-skills

4. https://github.com/microsoft/markitdown

5. https://github.com/microsoft/markitdown

6. https://github.com/multica-ai/multica

7. https://github.com/coleam00/Archon

8. https://github.com/shanraisshan/claude-code-best-practice

9. https://github.com/OpenBMB/VoxCPM

10. https://github.com/thedotmack/claude-mem

11. https://github.com/ahujasid/blender-mcp

12. https://github.com/rustfs/rustfs

13. https://github.com/virattt/ai-hedge-fund

14. https://github.com/snarktank/ralph

15. https://github.com/TapXWorld/ChinaTextbook
ALT text

github trending 1. https://github.com/NousResearch/hermes-agent 2. https://github.com/shiyu-coder/Kronos 3. https://github.com/forrestchang/andrej-karpathy-skills 4. https://github.com/microsoft/markitdown 5. https://github.com/microsoft/markitdown 6. https://github.com/multica-ai/multica 7. https://github.com/coleam00/Archon 8. https://github.com/shanraisshan/claude-code-best-practice 9. https://github.com/OpenBMB/VoxCPM 10. https://github.com/thedotmack/claude-mem 11. https://github.com/ahujasid/blender-mcp 12. https://github.com/rustfs/rustfs 13. https://github.com/virattt/ai-hedge-fund 14. https://github.com/snarktank/ralph 15. https://github.com/TapXWorld/ChinaTextbook

@pooza@mstdn.b-shock.org
@carlana@tech.lgbt

's new issue opening behavior is so weird I assumed it was a bug at first.

Yo dawg, I heard you like issues, so I put an issue in your issue…
ALT text

Yo dawg, I heard you like issues, so I put an issue in your issue…

@pooza@mstdn.b-shock.org · Reply to ぷーざ
@michabbb@vivaldi.net · Reply to michabbb

🔌 Full support for all extensions incl. MV2. Extension downloads anonymized via Helium services — Google can't track what you install.

❗ Native !bangs: jump directly to 10,000+ sites. !w Wikipedia, !gh , !wa Wolfram Alpha, !chatgpt for AI chats. Works fully offline, no prompt sent anywhere.

🔐 HTTPS enforced on all sites. No built-in password manager by design. No cloud sync — your browsing data stays yours only.

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to ぷーざ
@pooza@mstdn.b-shock.org
capsicum 1.13.0

github.com/pooza/capsicum/rele

モロヘイヤの「メディアカタログ」。
「タブ管理」を整理。
他、こまごま不具合を直したました。

Android: GooglePlay公開済み。
iOS: AppStore審査提出済み。

@capsicum

Release v1.13.0 · pooza/capsicum

マイルストーン詳細 https://github.com/pooza/capsicum/milestone/17?closed=1 新機能 モロヘイヤ連携: メディアカタログ表示(検索・人物フィルタ・ページング対応) Mastodon DM 専用タイムライン(タブとして追加・タブ管理で表示/非表示切替可能) ダークモード時の文字色カスタマイズ(ホワイト・ウォームホワイト・クールホワイト・ラ...

@release_bot@mstdn.b-shock.org
@konchie@misskey.delmulin.com · Reply to こんちえ :dorakue: :daidai: :popp_g: :osi:

@pooza@mstdn.b-shock.org @pooza@misskey.delmulin.com 伝わってない気がするので書きます。

以下の2つを投下したのは私です。
●GitHub テーマ設定⇒背景画像 について
 =PieFed テーマ設定⇒背景画像 について #288
●GitHub iPadOSにて〔通知〕が来ない件 補足 iOS(iPhone)で〔通知〕が来ない
 =PieFed iPadOSにて通知が来ない件 #52 コメント

以下が「私のアカウント」です。
●このアカウント
●PieFed konchie Nameはかいらのんこ/こんちえ
●GitHub kairanonko Nameはkonchie(小文字)

以下は私のアカウントではありません。
●GitHub Konchie Name不明

上記私のイシューを元にぷーざさんが新起票した以下3つ
● サーバーごとに背景画像を設定可能にする
● 背景画像の変更・解除後再設定が即時反映されない
● iOS / iPadOS でローカル通知が一度も届かない
に、元イシューの起票者が書いてあると思うのですが
GitHub kairanonko =私ではなく
GitHub Konchie =アカの他人になっているので
@kairanonko としないとKonchieさんが「???」ってなります。
Konchieさんが起票したイシューではなく、kairanonko(私)が起票したイシューです。

ということが言いたかったです。

github.com

Konchie - Overview

Konchie has 3 repositories available. Follow their code on GitHub.

@pooza@mstdn.b-shock.org · Reply to ラバソ
@pooza@misskey.delmulin.com
テーマ設定⇒背景画像 について #288

@konchie@pf.korako.me
ご要望とご報告を新規起票しました。

https://github.com/pooza/capsicum/issues/291 キャッシュ絡みのバグかも。なるはや。
https://github.com/pooza/capsicum/issues/292 新規ご要望。1.15が空いていたので仮設定したが、状況次第では1.14に前倒しするかも。

また背景画像は、一番良くみるであろうタイムライン画面とスレッド画面のみに適用しています。
プロフィール画面や通知画面など、他の画面にも適用したほうがいいのだろうか?そうであればご意見ください。

github.com

サーバーごとに背景画像を設定可能にする · Issue #292 · pooza/capsicum

概要 現状の背景画像設定は全サーバー共通。サーバー(アカウント)ごとに個別の背景画像を設定できるようにしてほしいという要望。 動機 背景画像を推しの画像にするユースケースが多く、テーマの異なるサーバーごとに別の画像を設定したいというニーズがある。 報告元 #288(@Konchie、2026-04-08)

@pooza@mstdn.b-shock.org · Reply to ラバソ
@pooza@mstdn.b-shock.org
capsicum 1.12.0

github.com/pooza/capsicum/rele

Android: GooglePlay審査済み。既に公開済みと思われます。
iOS: AppStore審査提出済み。

1.11.1で応急処置した「削除してタグづけ」を、あるべき実装に修正。

Misskeyの絵文字パレット同期は、最新のモロヘイヤ(一両日ぐらいにリリース)との連携機能です。
今回もアプリ単体では実現できない機能なので、サーバー側の力を借りてます。

@capsicum

Release v1.12.0 · pooza/capsicum

新機能 Misskey 実績(Achievements)の表示機能 (#187) ダークモードの色合いカスタマイズ (#251) タイムラインとスレッドに背景画像を設定可能に (#252) ドライブのドラッグ&ドロップによるファイル移動 (#264) 「削除してタグづけ」を mulukhiya API に移行 (#269) 絵文字パレットのサーバー同期機能 お知らせボットバナーのアイコンを...

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to ぷーざ
@pooza@mstdn.b-shock.org · Reply to 鴉河雛
@0xabad1dea@infosec.exchange

IT'S HAPPENING

GITHUB, THE FIRST ENTERPRISE CLOUD SOLUTION TO REACH ZERO NINES RELIABILITY

mrshu.github.io/github-statuse

uptime graph reading: 95 incidents in last 90 days - 89.91% uptime
ALT text

uptime graph reading: 95 incidents in last 90 days - 89.91% uptime

classic meme image: "it's happening" with Ron Paul laser show
ALT text

classic meme image: "it's happening" with Ron Paul laser show

@pooza@mstdn.b-shock.org
capsicum 1.11.1

github.com/pooza/capsicum/rele

「削除してタグ付け」をすると投稿が壊れるという、capsicumの存在意義に関わる不具合が発覚したので、緊急でリリースを行いました。

Android: GooglePlay公開済み
iOS: AppStore審査提出済み

@capsicum

Release v1.11.1 · pooza/capsicum

修正 「削除してタグづけ」で HTML が二重エスケープされる問題を修正 (#268) MFM コンテンツに対して不要な HTML 変換が適用されないよう修正 (#268)

@0xabad1dea@infosec.exchange

IT'S HAPPENING

GITHUB, THE FIRST ENTERPRISE CLOUD SOLUTION TO REACH ZERO NINES RELIABILITY

mrshu.github.io/github-statuse

uptime graph reading: 95 incidents in last 90 days - 89.91% uptime
ALT text

uptime graph reading: 95 incidents in last 90 days - 89.91% uptime

classic meme image: "it's happening" with Ron Paul laser show
ALT text

classic meme image: "it's happening" with Ron Paul laser show

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@Tutanota@mastodon.social

🚨 OPT OUT & say NO to using your interaction data to train & improve its AI models. 🚨 

GitHub is the next company to choose to opt you into having your data used - by default. 🚩

Opt out in Settings --> Copilot --> Features.

Under "Allow GitHub to use my data for AI model training" -→ Disabled.

It recently announced that if you do not opt out before April 24th, it will use your interaction data when using Copilot.

GitHub users -Opt out now. Screenshot of GitHub CoPilot Privacy Settings. Allow GitHub to use my data to for AI model training.
ALT text

GitHub users -Opt out now. Screenshot of GitHub CoPilot Privacy Settings. Allow GitHub to use my data to for AI model training.

Opt out in Settings --> Copilot.
ALT text

Opt out in Settings --> Copilot.

Click Disabled.
ALT text

Click Disabled.

Features --> Privacy ---> Under Allow GitHub to use my data for AI model training -→ Click enabled.
ALT text

Features --> Privacy ---> Under Allow GitHub to use my data for AI model training -→ Click enabled.

@0xabad1dea@infosec.exchange

IT'S HAPPENING

GITHUB, THE FIRST ENTERPRISE CLOUD SOLUTION TO REACH ZERO NINES RELIABILITY

mrshu.github.io/github-statuse

uptime graph reading: 95 incidents in last 90 days - 89.91% uptime
ALT text

uptime graph reading: 95 incidents in last 90 days - 89.91% uptime

classic meme image: "it's happening" with Ron Paul laser show
ALT text

classic meme image: "it's happening" with Ron Paul laser show

@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to ぷーざ
@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@pooza@misskey.delmulin.com
@Alex0007@mastodon.social

There is a bug in Claude Code in GitHub Actions that requires MCP servers to be installed beforehand, delaying startup time. The optimal approach would be to install MCP servers in parallel and connect only when needed, but the MCP_TIMEOUT variable is completely ignored.

This is frustrating. Recent releases of Claude Code have also been poor quality. Unbelievable.

github.com/anthropics/claude-c

github.com

[BUG] MCP Timeout needs to be configurable · Issue #424 · anthropics/claude-code

Environment Platform (select one): Anthropic API AWS Bedrock Google Vertex AI Other: Claude CLI version:0.2.36 Operating System: MacOS Terminal: Ghostty Bug Description MCP timeout error when using...

@0xabad1dea@infosec.exchange

IT'S HAPPENING

GITHUB, THE FIRST ENTERPRISE CLOUD SOLUTION TO REACH ZERO NINES RELIABILITY

mrshu.github.io/github-statuse

uptime graph reading: 95 incidents in last 90 days - 89.91% uptime
ALT text

uptime graph reading: 95 incidents in last 90 days - 89.91% uptime

classic meme image: "it's happening" with Ron Paul laser show
ALT text

classic meme image: "it's happening" with Ron Paul laser show

@pooza@mstdn.b-shock.org
@0xabad1dea@infosec.exchange

IT'S HAPPENING

GITHUB, THE FIRST ENTERPRISE CLOUD SOLUTION TO REACH ZERO NINES RELIABILITY

mrshu.github.io/github-statuse

uptime graph reading: 95 incidents in last 90 days - 89.91% uptime
ALT text

uptime graph reading: 95 incidents in last 90 days - 89.91% uptime

classic meme image: "it's happening" with Ron Paul laser show
ALT text

classic meme image: "it's happening" with Ron Paul laser show

@Tutanota@mastodon.social

🚨 OPT OUT & say NO to using your interaction data to train & improve its AI models. 🚨 

GitHub is the next company to choose to opt you into having your data used - by default. 🚩

Opt out in Settings --> Copilot --> Features.

Under "Allow GitHub to use my data for AI model training" -→ Disabled.

It recently announced that if you do not opt out before April 24th, it will use your interaction data when using Copilot.

GitHub users -Opt out now. Screenshot of GitHub CoPilot Privacy Settings. Allow GitHub to use my data to for AI model training.
ALT text

GitHub users -Opt out now. Screenshot of GitHub CoPilot Privacy Settings. Allow GitHub to use my data to for AI model training.

Opt out in Settings --> Copilot.
ALT text

Opt out in Settings --> Copilot.

Click Disabled.
ALT text

Click Disabled.

Features --> Privacy ---> Under Allow GitHub to use my data for AI model training -→ Click enabled.
ALT text

Features --> Privacy ---> Under Allow GitHub to use my data for AI model training -→ Click enabled.

@pooza@mstdn.b-shock.org
@dusoft@fosstodon.org
@smallcircles@social.coop
@pooza@mstdn.b-shock.org
@dusoft@fosstodon.org
@smallcircles@social.coop
@pooza@mstdn.b-shock.org · Reply to ぷーざ
@pooza@mstdn.b-shock.org

github.com/pooza/capsicum/issu

昨晩は猫化に対応していたが、一旦保留です。

耳の描画が意外と大変だったのと、何よりMastodonから猫フラグを取得する方法が調べきれなかったこと。
Mastodonでの猫フラグの取得、本体改造が必要なのかも。そこまでするのも、ちょっと違うなぁと。

自分はこの機能、そもそもジョークではあるのだろうけど、あえて意味を考えるならば「猫のロールプレイ」であるべきと考えていて。
この観点から、他鯖やMastodonからでも猫に見えるべきと思っており、それが実現できない半端な実装はしない。

@capsicum

github.com

Misskey: isCat 対応(猫耳アバター) · Issue #148 · pooza/capsicum

概要 Misskey の isCat フラグに対応し、猫ユーザーのアバターに猫耳を表示する。 備考 Misskey WebUI と同様、アバター画像の上に猫耳を重ねる表示 UserAvatar ウィジェット(#15 で導入済み)にフラグ判定を追加する形で実装可能 優先度は低い。ユーザーからの要望があった時点でマイルストーンを決定する

@admin@mstdn.feddit.social

Github的Microsoft/WSL仓库的issue区遭到中文博彩平台SPAM攻击

PR区未遭SPAM攻击,成为新的issue区(
WSL's issues has been attacked for Chinese betting platforms:github.com/microsoft/WSL/pull/

遭到大量SPAM攻击的issue区和action区:
github.com/microsoft/WSL/issues
github.com/microsoft/WSL/actio

看样子,官方机器人已经开始管理,比如加上tag:needs-author-feedback
目前SPAM issues仍在源源不断产生

SPAM issue
ALT text

SPAM issue

SPAM isssues
ALT text

SPAM isssues

@0xabad1dea@infosec.exchange

NINETY DAYS

NINETY INCIDENTS

NINETY PERCENT

YOU PAID FOR ALL FIVE NINES BUT YOU’LL ONLY NEED THE EDGE

a graph of github uptime status with an astonishing number of nineties specifically
ALT text

a graph of github uptime status with an astonishing number of nineties specifically

@pooza@mstdn.b-shock.org
capsicum 1.7

github.com/pooza/capsicum/rele
github.com/pooza/capsicum/mile

GooglePlay
審査中。もうすきストアに並ぶと思います。
内部テスターご希望の方は、管理人 @pooza までDMを。

AppStore
TestFlight審査中。完了次第、TestFlightアプリ経由で入手可能と思います。
また、1.3.3の本審査は、5回のリジェクトを経て、現在6回目の審査が2日放置されていますw

@capsicum

#

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@pooza@mstdn.b-shock.org · Reply to ぷーざ
@release_bot@mstdn.b-shock.org
@WPalant@infosec.exchange

So, where do the cool kids host their code these days? I went to GitLab and saw “Finally, AI for the entire software lifecycle” – ok, I guess this means no GitLab for me. Codeberg then? Or something else?

Note: no, I’m not self-hosting. Yes, I know how to do it, I’ve been doing it for a decade. But I still won’t.

@pooza@mstdn.b-shock.org
capsicum 1.6.0 ベータ版

github.com/pooza/capsicum/rele

翻訳、ハッシュタグのフォロー(Mastodon)、Play一覧(Misskey)、絵文字パレットコピペ(Misskey)等など。

あと、ログインの画面遷移を少し改善。
コード貼り付け方式も併用とし、復活。

GooglePlay版
play.google.com/store/apps/det

GooglePlay / AppStore 共、ベータテスター希望で、自分にメールアドレスを教えても構わない方はDMください。

@capsicum

play.google.com

capsicum - Apps on Google Play

capsicum is a Fediverse client application that supports Mastodon and Misskey.

@momizi06@misskey.io

注意喚起
GitHubから「VSCodeに脆弱性が見つかったから今すぐ更新してね」みたいなメール
​:is_all_scam:​
普通に
リンク先にウイルス仕込まれてる可能性が高いのと、現時点でメールに記載されてるCVE-2026-15923-48571が見つからなかったので99%偽物のメールです

@oageo@c.osumiakari.jp

基本的にはコード補完を含むCopilotへの入出力を行えば、(オフにしてない限り)モデルの学習に使われうると思って良さそう

GitHub Copilotがデフォルトでユーザーの入出力等を学習に使用するように、4月24日から - osumiakari.jp
www.osumiakari.jp/articles/20260326-copilotuseuusersinputtolearn/

osumiakari.jp

GitHub Copilotがデフォルトでユーザーの入出力等を学習に使用するように、4月24日から

ユーザーはオプトアウト可能で、無料版・Pro・Pro+のみ影響

"Updates to GitHub Copilot interaction data usage policy"

[. . . ] From April 24 [ . . . ] inputs, outputs, code snippets, and associated context—from Copilot Free, Pro, and Pro+ users will be used to train and improve our AI models unless they opt out. Copilot Business and Copilot Enterprise users are not affected by this update.
This approach aligns with established industry practices [ . . . ]

github.blog/news-insights/comp…

sfconservancy.org/GiveUpGitHub…

codeberg.org/


codeberg.org

Codeberg.org

Codeberg is a non-profit community-led organization that aims to help free and open source projects prosper by giving them a safe and friendly home.

@stefan@stefanbohacek.online
@NormanDunbar@mastodon.scot

Oh hum! Email from .

We’re updating how GitHub uses data to improve AI-powered coding tools. From April 24 onward, your interactions with GitHub Copilot—including inputs, outputs, code snippets, and associated context—may be used to train and enhance AI models unless you opt out.

Opt outing:

1. Go to GitHub Account Settings
2. Select Copilot
3. Choose whether to allow your data to be used for AI model training
4. Turn off any and all enabled AI shite while you are at it.

Cheers.

@pooza@mstdn.b-shock.org
capsicum 1.5.0

github.com/pooza/capsicum/rele

Androidの方は、↑のリンクからダウンロードしてください。
iOSの方は、AppStoreでのベータ版審査が終わり次第、TestFlight経由でお手元に届きます。

GooglePlay版が、ようやく公開された様です!
play.google.com/store/apps/det
但し、ストア版は審査したバージョン(1.3.3)のままなので古いです。
もうじき1.5.0に更新されると思うので、お待ちください。

一方、iOSは3回のリジェクトで、いま4回目の審査中です。

@capsicum

play.google.com

capsicum - Apps on Google Play

capsicum is a Fediverse client application that supports Mastodon and Misskey.

@smallcircles@social.coop

@evan some time ago you queried about what would be a good comms channel for API.

I have some ideas / recommendations on the repo that the TF uses.

- Structure the repo to hold the work of the full task force, not just for the creation of a single specification document.

- Use GH Discussions for all the general elaboration, feedback collection, etc. The repo forms a self-contained body of work. Move most current Issues in the tracker to become Discussions.

- Issues are created by task force members, and always represent actionable items. They are tracked on a Project kanban board where the swimlanes represent a simple protocol development with a number of stages.

Then:

- Primary comms channel is Discussions.
- Issues + kanban represent work tracks.
- Secondary comms channel can be .

I'd reserve mailing list to and organizational matters concerning the CG itself, and point mails on other subject to appropriate channel.

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
@jendrik@mastodon.social

Heads up - don't just do the major version bump to 6.0.0 for the 'setup-gradle' GitHub action, without being clear about the implications for your setup.

😥

"The caching functionality in `gradle-actions` has been extracted into `gradle-actions-caching`, a proprietary commercial component that is not covered by the MIT License."

github.com/gradle/actions/rele

github.com/gradle/actions/pull

github.com

Extract caching logic into a separate `gradle-actions-caching` component by bigdaz · Pull Request #885 · gradle/actions

With this change, the caching functionality of setup-gradle and dependency-submission is now provided by gradle-actions-caching, a closed-source library distributed under our Terms of Use. The rest...

@pooza@mstdn.b-shock.org
capsicum 1.4.0

github.com/pooza/capsicum/rele

Androidの方は、↑のリンクからダウンロードしてください。
iOSの方は、AppStoreでのベータ版審査が終わり次第、TestFlight経由でお手元に届きます。

設定画面等、ご要望のあった機能を中心に。ログインまわりの改善は継続。

AppStoreは3回、GooglePlayは2回のリジェクトです。持久戦の様相。

@capsicum

Release v1.4.0 · pooza/capsicum

マイルストーン詳細 https://github.com/pooza/capsicum/milestone/6?closed=1 新機能 アカウント別テーマカラー設定 — 設定画面からカラーパレットで選択可能。サーバー既定色への復帰も可能 (#93) タイムラインタブの順序カスタマイズ — ドラッグで並べ替え。Mastodon/Misskey でラベルを自動切替 (#92) 予約投稿 — ...

@pooza@mstdn.b-shock.org · Reply to ぷーざ
@pooza@mstdn.b-shock.org
capsicum 1.3.3

github.com/pooza/capsicum/rele

Androidの方は、↑のリンクからダウンロードしてください。
iOSの方は、AppStoreでのベータ版審査が終わり次第、TestFlight経由でお手元に届きます。

1.3.2の修正分(無限スクロール関連不具合)、実況コマンドの修正、ログイン手順微修正(審査対策)などを再審査に出しました。

AppStore / GooglePlay共、審査対応は継続中。今のところ2回ずつのリジェクトです。
Fediをよく知らない人には、MastodonやMisskeyへのログインは難しい様です。

@capsicum

Release v1.3.3 · pooza/capsicum

修正内容 番組表コマンドトゥートのタグ生成を Mastodon WebUI と統一(livecure/air/enable の数値判定対応、話数フォーマット修正、YAML 構造修正) Misskey: badgeRoles フォールバックで投稿のロールアイコン表示に対応 エピソードブラウザ: コマンドトゥート先頭の冗長な --- を除去 ピン留め解除時に投稿が通常リストから消える問題を修正...

@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
capsicum 1.3.1

1.3.1 を急遽リリースしました。

github.com/pooza/capsicum/rele

ずっと解決しなかったホームタイムラインのスクロールバグですが、遂に自分の端末で同じと思われる現象が再現したので、解決できたのではないかと思います。

github.com/pooza/capsicum/issu

Androidの方は、↑のリンクからダウンロードしてください。
iOSの方は、AppStoreでのベータ版審査が終わり次第、TestFlight経由でお手元に届きます。

AppStore / GooglePlay共、審査対応を継続中です。

@capsicum

github.com

タイムラインの無限スクロールが数回で停止する · Issue #89 · pooza/capsicum

概要 タイムラインの無限スクロールが数回(1〜5回程度)で止まり、それ以降の読み込みができなくなる。 テスター報告 キュアスタ!(precure.ml) のホームTL・連合TLで再現 v0.3.0 で「連合が読み込み失敗する」と報告 v0.4.0 でも継続。画面録画による再現報告あり 調査結果 Sentry イベント (CAPSICUM-1) WebSocketChannelExceptio...

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
capsicum 1.3.0

1.3.0 リリースしました。

github.com/pooza/capsicum/rele

Androidの方は、↑のリンクからダウンロードしてください。
iOSの方は、AppStoreでのベータ版審査が終わり次第、TestFlight経由でお手元に届きます。

AppStore / GooglePlay共、審査対応を継続中です。
けっこうリジェクトされてます。理不尽なものもありますw

ストア公開されれば、対象ユーザー(私のサーバーや、きゅあすきーのメンバー)以外の方にも一般公開されます。
ストア公開されたら、その旨広く周知する予定です。

@capsicum

Release v1.3.0 · pooza/capsicum

マイルストーン詳細 https://github.com/pooza/capsicum/milestone/5?closed=1 新機能・改善の概要 引用投稿の操作(引用元の表示・引用投稿の作成)(#49) お気に入り・ブーストしたユーザーのリスト表示 (#48) 投稿のピン留め・ピン留め解除 (#97) インスタンスティッカーの表示(Mastodon / Misskey 両対応)(#10...

@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
capsicum 1.2.0

@capsicum
github.com/pooza/capsicum/rele
リリースしました。

Androidの方は、↑のリンクからダウンロードしてください。
iOSの方は、AppStoreでのベータ版審査が終わり次第、TestFlight経由でお手元に届きます。

AppStore / GooglePlay共、審査対応を継続中です。
ストア公開されれば、対象ユーザー(私のサーバーや、きゅあすきーのメンバー)以外の方にも一般公開されます。
ストア公開されたら、その旨広く周知する予定です。

GooglePlayのストアでは、審査通過後ではありますが、テスター向けのベータ版の配布も行える様になる様です。
また、テスター登録では、メールアドレスなどの個人情報を私に伝える必要はない様です。
ほんとにそうなのか、あるいはテスター同士が互いの個人情報を知れたりしないかは要確認ですが、この確認の後はお気楽にテスター登録してください。

テスターである以上は、何かあったら報告してほしいですしw、また、対象ユーザー以外の方のテスター登録はご遠慮頂きたいです。

Release v1.2.0 · pooza/capsicum

マイルストーン詳細 https://github.com/pooza/capsicum/milestone/4?closed=1 新機能・改善の概要 Misskey チャンネルタイムラインの表示・チャンネルへの投稿 ドロワーからフォロー中チャンネル一覧を表示 Misskey アバターデコレーション表示 タグセット連動アバターデコレーション App Store UGC ガイドライン対応(EU...

@release_bot@mstdn.b-shock.org
@bagder@mastodon.social

Once you have opened for accepting vulnerability reports on , that door cannot be closed again. Now I need to manually tell everyone who do that where to go instead and close their submissions. Not the ideal workflow...

@bagder@mastodon.social

Once you have opened for accepting vulnerability reports on , that door cannot be closed again. Now I need to manually tell everyone who do that where to go instead and close their submissions. Not the ideal workflow...

@pooza@mstdn.b-shock.org

@capsicum

PieFedコミュニティのテスト兼ね。
ストア配布がまだ始まっていませんので、今のところはここが配布元になってます。

github.com/pooza/capsicum/rele

iOS
TestFlight参加ご希望の方は、Apple IDのメールアドレスをDMにてお送りください。

Android
apkファイルを↑のページからダウンロードしてください。
GooglePlayでの公開が始まったら、AndroidもiOS同様の手順でのクローズテストに移行します。

Release v1.1.0 · pooza/capsicum

新機能 投稿 絵文字入力ピッカー(カスタム絵文字・Unicode 絵文字)(#61) Misskey ローカルオンリー投稿対応(投稿 UI + タイムライン表示)(#17) 投稿済みメディアの説明(ALT)編集(Misskey)(#30) タイムライン ホーム TL で DM(ダイレクト投稿)を背景色で区別表示 (#116) タイムライン既読位置の保存・復元(Mastodon mark...

@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to ぷーざ
@pooza@mstdn.b-shock.org · Reply to 鴉河雛
@pooza@mstdn.b-shock.org · Reply to ぷーざ
@pooza@mstdn.b-shock.org

github.com/pooza/capsicum/mile

1.2実装状況。
・Acctとタグ、Mastodonではリンクにできていないところがあったのでリンクに。
・絵文字にWebUI同様の検索窓追加。とてもよい。
・APIの実行がループし、レートリミットになりやすいケースが発覚。3段階の対応を計画し、1段階目を実装。これだけでも効果あるはず。

これも審査が終わる前に配布することがないことを祈るw

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@hongminhee@hollo.social

A daily minor annoyance: (GitHub Flavored Markdown) breaking standard behavior by rendering single newlines as <br>.

If you're used to formatting plain text with hard wraps for mailing lists, you know the pain. You type up a perfectly readable 80-column text block, hit submit, and realize has turned it into a jagged mess of arbitrary line breaks. I really miss standard Markdown paragraph collapsing in issue trackers.

@pooza@mstdn.b-shock.org

github.com/pooza/capsicum/issu

capsicumのレンダラーに、Markdown一式を実装するのは、確かに誤判定のリスクが高くなる。Markdown嫌いな人がキレそうだし。
しかし、コードブロック(```)と引用文(>)に限って実装すれば、このぐらいならバチは当たらないだろうと。

引用文の行頭に > をつけるのはMarkdownができるもっと前からの慣例であって、Markdown固有のものではない。
また、日常の文章でコードブロックの「```」が、異なる意味で使われるリスクもほとんどない。

…と思って、capsicumの実装を確認していたところ。
ちなみにこれらの表記は、Misskeyにおいても、MFMの仕様の一部ではある。その為か、Mastodon側のレンダラーに既にこれらのレンダリングが実装されていた。

指示してない機能が実装されていたものだから、厳密に言えばこれはバグなんだろうけどw、まぁ結果オーライだ。

github.com

コードブロックに言語ラベルを表示する · Issue #136 · pooza/capsicum

概要 コードブロック(```)にはパーサーが言語名を既に抽出しているが、レンダリング時に使用していない。言語名が指定されている場合、コードブロック内に小さなラベルとして表示する。 背景 コードブロック・引用ブロックは MFM パーサーに実装済みで、Mastodon の HTML 投稿でも _parseHtml の前処理により正しく動作することを確認済み _tryCodeBlock() で言語...

@pooza@mstdn.b-shock.org
@nicd@masto.ahlcode.fi

Unsure if it's due to AI scraping or general botnetting, but I've been getting blocked from GitHub pretty frequently lately on my phone where I'm not logged in. At first I thought someone had cracked my router or something but it also happens on mobile data.

Too many requests. You have exceeded a secondary rate limit. Please wait a few minutes before you try again; in some cases this may take up to an hour. Signing in may provide a higher rate limit if you are not already signed in.
ALT text

Too many requests. You have exceeded a secondary rate limit. Please wait a few minutes before you try again; in some cases this may take up to an hour. Signing in may provide a higher rate limit if you are not already signed in.

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
capsicum 1.1

github.com/pooza/capsicum/rele

通常、10程度の改善ごとにリリースする予定だったところ、20超の改善がたまってしまいました。
GooglePlay / AppStore共、審査がまったく進む気配がないので、現時点のバージョンをテスターさんに配布します。

・ご意見等
美食丼の タイムラインを、Claudeに監視させるようにしました。
どのサーバーからでもハッシュタグをつけて投稿して頂ければ、半自動でご意見が登録される仕組みです。
私に内緒で伝えたいケースではその限りではありませんが、今後基本的には、このハッシュタグに投稿して頂けると助かります。

Release v1.1.0 · pooza/capsicum

新機能 投稿 絵文字入力ピッカー(カスタム絵文字・Unicode 絵文字)(#61) Misskey ローカルオンリー投稿対応(投稿 UI + タイムライン表示)(#17) 投稿済みメディアの説明(ALT)編集(Misskey)(#30) タイムライン ホーム TL で DM(ダイレクト投稿)を背景色で区別表示 (#116) タイムライン既読位置の保存・復元(Mastodon mark...

@pooza@mstdn.b-shock.org

github.com/pooza/capsicum/mile

審査に全然動きがないものだから、手元には20以上の改善を消化したバージョンがあります。
ストア解禁したら手元の1.1を即、クローズテストに出せるようにしたいんだけど。

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to ぷーざ
@h4ckernews@mastodon.social
@ngate@mastodon.social
@h4ckernews@mastodon.social
@pooza@mstdn.b-shock.org · Reply to ぷーざ
@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
capsicum 0.7.0

github.com/pooza/capsicum/rele

github.com/pooza/capsicum/issu
タイムラインが途切れるという報告への対応のみです。
これが解決したら、1.0をストアからリリースしたいところ。

Android:
↑のページにあるapkを端末にインストールしてください。

iOS:
私のサーバーやきゅあすきーのメンバーに限り、TestFlightのテスターとして招待します。
Apple IDとして登録されているメールアドレスを、DMなどでお伝え下さい。

ロードマップ:
github.com/pooza/capsicum/mile
多くの未実装機能がございます。

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@zenn_trend_bot@silicon.moe · Reply to Zenn Trends

📰 GitHubで見つけた「便利ツール」を解析したらマルウェアだった話 (👍 159)

🇬🇧 A seemingly useful GitHub tool turned out to be malware. Analysis of Claude Artifacts and Open Claw fake repos used for social engineering attacks.
🇰🇷 GitHub에서 발견한 '편리한 도구'가 악성코드로 판명. Claude Artifacts와 Open Claw 가짜 저장소를 통한 소셜 엔지니어링 공격 분석.

🔗 zenn.dev/hiyoko_sauna/articles

zenn.dev

GitHubで見つけた「便利ツール」を解析したらマルウェアだった話

@pooza@mstdn.b-shock.org
capsicum 0.6.0

github.com/pooza/capsicum/rele

コピペ、ピンどめ。バグ修正。

github.com/pooza/capsicum/issu
報告あった件は、これかもしれない。これだったらいいなと。

この修正が正しいことを確認したいリリース。

Android:
↑のページにあるapkを端末にインストールしてください。

iOS:
私のサーバーやきゅあすきーのメンバーに限り、TestFlightのテスターとして招待します。
Apple IDとして登録されているメールアドレスを、DMなどでお伝え下さい。

ロードマップ:
github.com/pooza/capsicum/mile
多くの未実装機能がございます。

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@pooza@mstdn.b-shock.org
capsicum 0.5.0

github.com/pooza/capsicum/rele

個人的には1.0での目玉機能になる予定の、エピソードブラウザを実装。

現在、GooglePlayの開発者アカウントが長期間活動しなかったために凍結中。
これが復旧するまでの間は、先のバージョンで予定していた軽めの修正を、前倒しで随時対応していきます。

不具合
github.com/pooza/capsicum/issu
引き続き様子見でした…が、解決したとの情報もあり。

Android:
↑のページにあるapkを端末にインストールしてください。

iOS:
私のサーバーやきゅあすきーのメンバーに限り、TestFlightのテスターとして招待します。
Apple IDとして登録されているメールアドレスを、DMなどでお伝え下さい。

ロードマップ:
github.com/pooza/capsicum/mile
多くの未実装機能がございます。

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@pooza@mstdn.b-shock.org
caosicum 0.4.0

github.com/pooza/capsicum/rele

不具合修正中心。
また、発生したエラーを外部サービスに送る機能を設けました。
こちらで現象が再現できなくても、対応できることがあるかもしれません。

Android:
↑のページにあるapkを端末にインストールしてください。

iOS:
私のサーバーやきゅあすきーのメンバーに限り、TestFlightのテスターとして招待します。
Apple IDとして登録されているメールアドレスを、DMなどでお伝え下さい。

ロードマップ:
github.com/pooza/capsicum/mile
多くの未実装機能がございます。

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@cloudskater@bark.lgbt

Programmers, can you inform me why people still use github? Its owned by Microsoft, promotes AI garbage, and that alone kind of makes it shitty as a place to host open source stuff in my book. As a simple plebian, am I missing something? I don't code, so does it offer something that other platforms don't?

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
capsicum 0.3.0

github.com/pooza/capsicum/rele

iPadでレイアウトが崩れる問題に対応できたので、対象に戻しました。
iOS版は審査が終わるまでお待ちください。

Android:
↑のページにあるapkを端末にインストールしてください。

iOS:
私のサーバーやきゅあすきーのメンバーに限り、TestFlightのテスターとして招待します。
Apple IDとして登録されているメールアドレスを、DMなどでお伝え下さい。

ロードマップ:
github.com/pooza/capsicum/mile
多くの未実装機能がございます。

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@arnan@mas.to
@arnan@mas.to
@pooza@mstdn.b-shock.org

github.com/pooza/capsicum/mile

初回リリース分、残Issueは1。
エピソードブラウザは、無理言って強硬に初回スコープに入れたやつ。これの大事さをわかってくれw
そのあと少しの間はテスターのフィードバック対応かな。

GooglePlayのデベロッパーアカウント復活の先行き次第。
メインのGoogleアカウント以外でデベロッパー登録するという手も、なくもないが。場当たり的な対応があとで負債になりそうだから、手は抜かずに。
当面は「GitHubからapkを入れて」でもよさそうだし。

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@pooza@mstdn.b-shock.org
capsicum 0.2.0

github.com/pooza/capsicum/rele

もう少し作業を進めてから次のバージョンを出すつもりでしたが、新しいバージョンを出したタイミングでないと変更できない設定がストア側にあり、やむなくリリース。
とはいえ、有益な修正もそれなりに入っていると思います。

Android:
↑のページにあるapkを端末にインストールしてください。

iOS:
私のサーバーやきゅあすきーのメンバーに限り、TestFlightのテスターとして招待します。
Apple IDとして登録されているメールアドレスを、DMなどでお伝え下さい。

ロードマップ:
github.com/pooza/capsicum/mile
多くの未実装機能がございます。

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@pooza@mstdn.b-shock.org · Reply to ぷーざ
@pooza@mstdn.b-shock.org

モロヘイヤ対応のMastodon / Misskeyクライアント「camsicum」の、テスト版が配布できるようになりました。
テスト版ですので、私のサーバーのメンバーにだけ配布します。よかったらご確認頂き、ご意見ください。

github.com/pooza/capsicum/rele

Android:
↑のページにあるapkを端末にインストールしてください。

iOS:
私のサーバーやきゅあすきーのメンバーに限り、TestFlightのテスターとして招待します。
Apple IDとして登録されているメールアドレスを、DMなどでお伝え下さい。

ロードマップ:
github.com/pooza/capsicum/mile
多くの未実装機能がございます。

github.com

pooza/capsicum

Flutter-based Mastodon / Misskey client. Contribute to pooza/capsicum development by creating an account on GitHub.

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
@zenn_trend_bot@silicon.moe · Reply to Zenn Trends

📰 【GitHub Actions】スクリプトインジェクションの実践例 (👍 143)

🇬🇧 GitHub Actions security warning: Never use ${{}} directly in run commands. Shows script injection vulnerabilities with practical examples.
🇰🇷 GitHub Actions 보안 경고: run 명령에서 ${{}} 직접 사용 금지. 스크립트 인젝션 취약점 실전 예제.

🔗 zenn.dev/kou_pg_0131/articles/

zenn.dev

【GitHub Actions】スクリプトインジェクションの実践例

@cascading@misskey.io

🔴 Cline 2.3.0 用户可能被安装了 OpenClaw;不需要的话可以卸载。

- 2/17 晚至 2/18 凌晨安装了 Cline 的用户可能受到影响 [1]。
- 研究者利用了 GitHub Actions cache 可以跨分支共享、可以被投毒,以及 cache 的解压并未对路径进行检查的漏洞 [2]。
- 虽然未经用户允许安装,但 OpenClaw 本身并非恶意软件。

1.
GHSA-9ppg-jx86-fqw7
2.
adnanthekhan.com/~

Fixed-in: 2.4.0


Telegram 原文

t.me

层叠 - The Cascading

🔴 Cline 2.3.0 用户可能被安装了 OpenClaw;不需要的话可以卸载。 - 2/17 晚至 2/18 凌晨安装了 Cline 的用户可能受到影响 [1]。 - 研究者利用了 GitHub Actions cache 可以跨分支共享、可以被投毒,以及 cache 的解压并未对路径进行检查的漏洞 [2]。 - 虽然未经用户允许安装,但 OpenClaw 本身并非恶意软件。 1. GHSA-9ppg-jx86-fqw7 2. adnanthekhan.com/~ Fixed-in: 2.4.0 #Cline #OpenClaw #GitHub

@pooza@misskey.delmulin.com

ああ、忘れてた。
Misskeyの2〜3ヶ月ぐらいぶりの新バージョン、2026.3.0がリリースされました。

いつも以上に、多くの変更がありそうと予想してます。
例によって何日か待つとすると、ここへの適用は週末になりそうです。

Release 2026.3.0 · misskey-dev/misskey

Note users/following の birthday プロパティは非推奨になりました。代わりに users/get-following-users-by-birthday をご利用ください。 General Enhance: 「もうすぐ誕生日のユーザー」ウィジェットで、誕生日が至近のユーザーも表示できるように (Cherry-picked from https://githu...

@pooza@misskey.delmulin.com

ああ、忘れてた。
Misskeyの2空3ヶ月ぐらいぶりの新バージョン、2026.3.0がリリースされました。

いつも以上に、多くの変更がありそうと予想してます。
例によって何日か待つとすると、ここへの適用は週末になりそうです。

Release 2026.3.0 · misskey-dev/misskey

Note users/following の birthday プロパティは非推奨になりました。代わりに users/get-following-users-by-birthday をご利用ください。 General Enhance: 「もうすぐ誕生日のユーザー」ウィジェットで、誕生日が至近のユーザーも表示できるように (Cherry-picked from https://githu...

@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org

Misskey 2026.2.0 は今日リリースされるんかな?

github.com/misskey-dev/misskey

misskey.io にはとっくに適用されていたりして…!?
なんて思ったら、 misskey.io のMisskeyはだいぶ古いもの(
2025.4.1-io.12b-fb6fbea074 )だったと知ってびっくり。

「Misskeyむけのツールを書くときは、 2025.4.1 での動作もテストするべき」もあるかもしれん。限度あるけど。

Release 2026.2.0-beta.0 · misskey-dev/misskey

Note users/following の birthday プロパティは非推奨になりました。代わりに users/get-following-birthday-users をご利用ください。 General Enhance: 「もうすぐ誕生日のユーザー」ウィジェットで、誕生日が至近のユーザーも表示できるように (Cherry-picked from https://github.c...

@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org

丼4.5.7への対応は終了。

github.com/mastodon/mastodon/s

FASPとは? "Federated Account Subscription Protocol" ?

4.4から入った実験的機能だそうだ。
あえて有効にしていない限り、ほとんどの鯖には無関係とのこと。

github.com

Allowing unconfirmed FASP to make subscriptions

## Summary FASP registration requires manual approval by an administrator. Actions performed by a FASP to subscribe to account/content lifecycle events or to backfill content did not check prope...

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to 鴉河雛

@karasu_sue
ちょうどClaude Codeに尋ねました。

モロヘイヤ インストール前の準備(RHEL系)

1. EPELリポジトリの有効化
sudo dnf install -y epel-release

2. RPM Fusion(ffmpeg用)
sudo dnf install -y --nogpgcheck mirrors.rpmfusion.org/free/el/$(rpm -E %rhel).noarch.rpm

3. 必要パッケージのインストール
sudo dnf install -y gcc make redhat-rpm-config vips-devel libidn-devel postgresql-devel ffmpeg redis jemalloc

4. Redisの起動
sudo systemctl enable --now redis

5. Ruby 4.0.1以上のインストール(rbenv推奨)
git clone github.com/rbenv/rbenv.git ~/.rbenv
git clone github.com/rbenv/ruby-build.git ~/.rbenv/plugins/ruby-build
echo 'eval "$(~/.rbenv/bin/rbenv init -)"' >> ~/.bashrc
source ~/.bashrc
rbenv install 4.0.1
rbenv global 4.0.1

6. bundlerインストール & bundle install
gem install bundler
cd /path/to/mulukhiya-toot-proxy
bundle install

github.com

GitHub - rbenv/ruby-build: A tool to download, compile, and install Ruby on Unix-like systems.

A tool to download, compile, and install Ruby on Unix-like systems. - rbenv/ruby-build

@release_bot@mstdn.b-shock.org
@alemarcati@mastodon.social

Does GitHub Desktop work with CodeBerg? Or is there an alternative to it that works with CodeBerg? I've been doing gamedev as a hobby and been using GitHub. I like the "GitHub Desktop" app, because I really don't like using the git terminal (I prefer a UI). I've been thinking of moving my repositories to an open source alternative like CodeBerg, the only thing that makes hesitate is having to use the git terminal.

@pooza@mstdn.b-shock.org · Reply to ぷーざ
@release_bot@mstdn.b-shock.org
@ploum@mamot.fr

Les gens qui utilisent : comment vous faites pour envoyer des petites contributions à un projet ?

Vous êtes obligés de créer un fork dans l’interface web pour chaque contribution ? (nan mais l’angoisse totale !)

J’ai tenté de garder une branche mais github ne fait pas des rebase corrects ce qui fait que chaque merge renvoie tous les commits que j’ai déjà contribué (même si ceux-ci sont inopérants car leur conteun a déjà été mergé)

@ploum@mamot.fr

I get it, the git-send-mail workflow has a learning step. It’s hard the first few times. But once you are used to it, the "pull-requests-on-web-ui" becomes insufferable.

Dear people maintening a project on Github: please give me an email address to which I can send you trivial patches. The whole PR workflow takes more time than the codïng!

And if enough projects does that, I could eventually ditch my Github account!

ploum.net/2026-01-31-offline-g

ploum.net

The Disconnected Git Workflow

The Disconnected Git Workflow par Ploum - Lionel Dricot.

@T_X @axx so for 2027, I had another stupid idea everyone insisted was good: it will be -only on the main network. The dual stack will get a yearly name change to prevent auto-reconnect. We want people on v6-only and break stuff left and right. Every. Single. Year.

And if is not on v6 by next year, trust me, they will put _something_ in place very quickly.

@pooza@mstdn.b-shock.org
@Moonstone2487@hessen.social · Reply to Moonstone2487

Thread 2/3

Gleichzeitig nutzen wir intern alles, was der teuerste Plan von hergibt, inkl. . Und ja, ich kann und muss mir den über einen hausinternen Antrag freischalten lassen. Enterprise für "nur uns zugängliche" Repos + (nicht als Pflicht, aber defacto nutzt und empfiehlt es jeder) als Code Editor.

Der Server steht nicht bei uns, sondern in der in den ( ).

@otaviocc@social.lol

RE: social.lol/@otaviocc/116076383

I have no words to thank everyone for helping yesterday.

Great news: Yesterday on the omg.lol IRC server, folks investigated and discovered the GitHub account was part of a network of bots. These bots republish open source projects, modifying their READMEs with malicious links, and distribute Windows malware through fake builds.

After documenting the findings, we reported everything to GitHub. Within hours, they took down the repositories and an account for violating their Terms and Code of Conduct.

Thank you for investigating, reporting, and sending coffee. You're all amazing!

I planned to write a blog post today, but @brennan already wrote something better than I could. You should read it:

brennan.day/the-curious-case-o

Many thanks to @brennan, @chilli, @adam, mattl, @cygnoir, @annika, @jarunmb, and everyone else who helped!

brennan.day

The Curious Case of the Triton Malware Fork

Today, a weird malware distribution campaign targeting users of omg.lol and Triton, an open-source macOS client of omg.lol, was found. The attack leverages the trust of GitHub, creating a malicious fork where the download link has been replaced with malware hidden in presented .zip file.

The quoted post is no longer available.

@pooza@mstdn.b-shock.org
@ross@rossabaker.com
@release_bot@mstdn.b-shock.org
@kelson@notes.kvibber.com

Disingenuous statement on the GitHub Blog on the flood of AI-generated slop "contributions" that have been overwhelming project maintainers with busy-work:

"At GitHub, we aren’t just watching this happen."

That's true. You actively pushed things to get us to this point.

#GitHub #slop

github.blog

Welcome to the Eternal September of open source. Here's what we plan to do for maintainers.

As contribution friction drops, maintainers are adapting with new trust signals, triage approaches, and community-led solutions.

@DansNull@mastodon.social

Tip: If you come across a project that hasn’t been updated in a long time or is no longer maintained. Navigate to “Insights>Forks” or just add “/forks” to the end of the projects URL. Here you can see if anyone else has made their own fork of the project and is continuing development.

@pooza@mstdn.b-shock.org
@kelson@notes.kvibber.com

Disingenuous statement on the GitHub Blog on the flood of AI-generated slop "contributions" that have been overwhelming project maintainers with busy-work:

"At GitHub, we aren’t just watching this happen."

That's true. You actively pushed things to get us to this point.

#GitHub #slop

github.blog

Welcome to the Eternal September of open source. Here's what we plan to do for maintainers.

As contribution friction drops, maintainers are adapting with new trust signals, triage approaches, and community-led solutions.

@judell@social.coop

A human lifetime is not long enough to comprehend all that git and github can do, and become maximally capable of using these tools.

I don't want to live forever but I do want to wield that full capability while I'm here, and now I can.

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org

github.com/THE-POWERNEWS/write

雑多なバッチ処理集を更新してた。
丼専用のユーティリティのつもりはないのに、丼の処理ばかりになってしまったw

そういえばMisskeyには、深夜バッチを実行するという運用がないな。

github.com

GitHub - THE-POWERNEWS/writersbase-tools

Contribute to THE-POWERNEWS/writersbase-tools development by creating an account on GitHub.

@admin@mstdn.feddit.social

发现一个小玩具,比较有趣,针对Mastodon用于追踪特定推文的后续回复
github.com/hcschuetz/follow-to
总的来说,不是关注用户,而是关注帖子

https://hcschuetz.github.io/follow-toots/dist/
ALT text

https://hcschuetz.github.io/follow-toots/dist/

https://hcschuetz.github.io/follow-toots/dist/tree.html#instance=mstdn.feddit.social&id=115937081428138375
ALT text

https://hcschuetz.github.io/follow-toots/dist/tree.html#instance=mstdn.feddit.social&id=115937081428138375

https://hcschuetz.github.io/follow-toots/dist/tree.html#instance=mstdn.feddit.social&id=115995995293010716
ALT text

https://hcschuetz.github.io/follow-toots/dist/tree.html#instance=mstdn.feddit.social&id=115995995293010716

https://hcschuetz.github.io/follow-toots/dist/tree.html#instance=mstdn.feddit.social&id=115999998144507024
ALT text

https://hcschuetz.github.io/follow-toots/dist/tree.html#instance=mstdn.feddit.social&id=115999998144507024

@Edent@mastodon.social

🆕 blog! “Reputation Scores for GitHub Accounts”

The folks at GitHub know that Open Source maintainers are drowning in a sea of low-effort contributions. Even before Microsoft forced the unwanted Copilot assistant on millions of repos, it was always a gamble whether a new contributor would be helpful or just some witless jerk. Now it feels a million times worse.

There are some…

👀 Read more: shkspr.mobi/blog/2026/02/reput
⸻

shkspr.mobi

Reputation Scores for GitHub Accounts

The folks at GitHub know that Open Source maintainers are drowning in a sea of low-effort contributions. Even before Microsoft forced the unwanted Copilot assistant on millions of repos, it was always a gamble whether a new contributor would be helpful or just some witless jerk. Now it feels a million times worse. There are some discussions about what tools repository owners should have to help…

@n0toose@chaos.social

Are you using to host your favorite AI-assisted and otherwise vibecoded project because your desire for dopamine has utterly destroyed your willingness to learn new things? Do you neither care about how you're "flooding the room" of the free software ecosystem nor about the greater societal implications, insisting that "it is what it is"?

Check out , the world's most popular AI-first platform! Copilot, annoying maintainers with slop, you'll fit just right in!

@Edent@mastodon.social
@esparta@ruby.social

This morning I did receive five (5) notification of services created on my behalf using GitHub-related (and ) email accounts:

- Canary Mail
- Angel Studios
- Quora
- Branded
- Cardi.Health
- (new since posted)
- Replika
- VSCO
- Medium
- Headspace
- Commuinity.com
- Survive the ARK
- Jimdo
- Dropbox

I'm still not sure if this still an issue with the last breach or an ongoing one.

partial screenshot of one of my inbox, with 4 columns: Subject, Correspondents, spam, Date

- Activate account for Quora,
  Quora Support < support@quora.com >
  11:27 AM
- Activate account for Branded
  Branded <support@gobranded.zendesk.com>
  11:27 AM
- Activate account for Cardi.Health
  CardiHealth <hello@cardi.health>
  11:27
ALT text

partial screenshot of one of my inbox, with 4 columns: Subject, Correspondents, spam, Date - Activate account for Quora, Quora Support < support@quora.com > 11:27 AM - Activate account for Branded Branded <support@gobranded.zendesk.com> 11:27 AM - Activate account for Cardi.Health CardiHealth <hello@cardi.health> 11:27

partial screenshot of one of my inbox, with 4 columns: Subject, Correspondents, spam, Date

- Activate account for Canary Mail
  Canary Mail <support@canarymail.zendesk.com>
  11:29 AM
- Activate account for Angel
  Angel <support@angelstudios.zendesk.com>
  11:29 AM
ALT text

partial screenshot of one of my inbox, with 4 columns: Subject, Correspondents, spam, Date - Activate account for Canary Mail Canary Mail <support@canarymail.zendesk.com> 11:29 AM - Activate account for Angel Angel <support@angelstudios.zendesk.com> 11:29 AM

@testlens@mastodon.social

TestLens launches to accelerate Java and Kotlin pull request workflows!

Know this problem? You’re done with implementing a feature, but getting your PR through the CI pipeline is tedious. TestLens assists you to get your pull requests merged faster by posting an easy-to-read summary of failed tests and by rerunning failed tests only!

Read more in our announcement post and join the private beta: testlens.app/blog/2026/02/04/t

localhost

TestLens launches to accelerate Java and Kotlin pull request workflows

Know this problem? You’re done with implementing a feature, but getting your PR through the CI pipeline is tedious. TestLens assists you to get your pull requests merged faster by posting an easy-to-read summary of failed tests and by rerunning failed tests only!

@pooza@mstdn.b-shock.org · Reply to ぷーざ

すべてHexoからGitHub Pagesに移行。煩わしいビルドがなくなり、よかった。

blog.precure.ml/
blog.mstdn.delmulin.com/
blog.misskey.delmulin.com/

昨年あたりは特に忙しかったので、古い記述をだいぶ修正した。
直すところまだありそう。

blog.misskey.delmulin.com

Home | ダイスキーBlog

@ojrask@piipitin.fi
@Edent@mastodon.social

A knotty problem.
I want to see all the "Reactions" to my account.
The API only allows you to get reactions to *specific* issues, PRs, or commits.
In order to see *all* the reactions sent to me, I'd need to query for literally everything I've posted.

That can't be right, surely? Am I misreading the API documentation?

@pooza@mstdn.b-shock.org

blog.precure.ml/

Hexoベースのブログを、GitHub Pagesに移行する更新を、OpenAI Codexにやらせた。
頭を使うというよりは、手作業ではミスしそうな機械作業が大半。この手の作業はAIに限る。

所感
作業のアウトプットはよいが、会話には向かない。
Claude Codeは割と相談にものってくれるので、そこは物足りなく感じた。

blog.precure.ml

キュアスタ!Blog | キュアスタ!Blog

@film_girl@mastodon.social

So we know AI is making it easier for people to submit low-quality PRs or contributions to projects on GitHub and the team is actively looking at short-term and long-term solutions to try to make this better. Would love your input/feedback as well any other pain points so we can try to make the experience better. Feel free to reply here or on this thread github.com/orgs/community/disc

github.com

Exploring Solutions to Tackle Low-Quality Contributions on GitHub · community · Discussion #185387

Hey everyone, I wanted to provide an update on a critical issue affecting the open source community: the increasing volume of low-quality contributions that is creating significant operational chal...

@admin@mstdn.feddit.social

@board 哔哩哔哩你 了。

哔哩哔哩-API收集整理 github.com/SocialSisterYi/bili

This repository was archived by the owner on Jan 28, 2026. It is now read-only.

—-
Deprecated
本仓库停止维护并永久永久关停。
This Repo will cease maintenance and be permanently closed.
原因
2026年1月28日,本仓库维护者收到B站委托的律师事务所发律师函警告邮件,指控本仓库中的项目存在“通过技术手段对哔哩哔哩平台非公开的API接口及其调用逻辑、参数结构、访问控制及安全认证机制进行系统性收集、整理,并以技术文档、代码示例等形式向不特定公众传播”的侵权行为。
即日起停止维护并删除相关文档及源代码。
—-

绿尸寒
ALT text

绿尸寒

@janvlug@mastodon.social
@rusty__shackleford@mastodon.social

Fuck AI with :
Web AI Firewall Utility that weighs the soul of your connection using one or more challenges protecting upstream resources from bots.

Designed to protect the small internet from AI companies endless requests, Anubis is lightweight so ***everyone*** can afford to protect the communities closest to them.

Fuck AI

lock.cmpxchg8b.com/anubis.html

@jplatte@social.tchncs.de

Been moving some stuff from to (mostly for stuff I could see getting contributors) and sr.ht (? almost exclusively for throwaway stuff, as an archive). It's easy when there's not much metadata (primarily issues) to move over.. Still haven't decided how to handle CI though - that's kind blocking me from even getting started on larger projects.

@pooza@mstdn.b-shock.org

弊鯖では、ナビゲーションパネルを /public/links.json から拡張できる。
鯖独自のリンクを設けたいときに、通常は都度フロントエンドのコードを修正しないといけないところ、JSONファイルの修正だけで項目追加できるようにしている。
コードの修正だけでなく、mastodon-webサービスの再起動も不要。運用観点ではこのぐらいのラクであってほしい。(Mastodonにはどうも、この手の運用目線が足りてない気がする。テーマ然り)

4.4ぐらいでナビゲーションパネルに大きな変更が入った。
以前の改造ではアイコンも表示できていたところ、それが難しい構造になってしまった。新しい実装に合わせてアイコンを表示する、よい方法もなかなか思いつかず、しばらく放置。
最近Claudeに相談したところ、「既存のアイコンとデザインが大きく違わないGoogle Fontsを使ってはどうか?」と助言されて、ついでに修正までお願いしてしまったところ。
github.com/pooza/mastodon/pull

@pooza@mstdn.b-shock.org · Reply to ぷーざ
@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@diogop@ieji.de · Reply to Metin Seven 🎨

@metin I moved from Github to a self-hosted Gitea instance that I self-host on OVH, a European cloud provider.

I also moved my .dev top-level domain from Google to EURid's .eu.

I'm very happy with these changes. I no longer have to put up with AI's obsession every time I did something on GitHub.

On top of that, I no longer use Cloudflare, and recently had to install Anubis (Web AI Firewall) to stop being attacked by AI Crawlers from openai and other Big Tech companies that were scanning all the commits on my Gitea (public repositories ofc).

@tewha@appdot.net

GitHub collapsing small files by default in diffs is… troubling. I never want to commit changes to something like Package.resolved without seeing them first.

@tewha@appdot.net

GitHub collapsing small files by default in diffs is… troubling. I never want to commit changes to something like Package.resolved without seeing them first.

@pooza@mstdn.b-shock.org
@zef@social.zef.pub

So a few steps that I plan to make whether I end up migrating #SilverBullet to Codeberg (or elsewhere) or not:

  1. Offer the same level of support for @forgejo hosted repositories as for Github ones in SilverBullet itsel (most notably: implement Share support)
  2. Change examples in the docs to be #CodeBerg rather than #GitHub first
  3. Change default Docker registries for images back to docker hub (unless people have better suggestions) — had changed those to GHCR before.
  4. Emphasize or perhaps even explicitly ask to move people's sponsorships from Github to my LiberaPay account.
  5. Attempt to migrate some repos to #CodeBerg, perhaps my personal ones to see how things work there.

liberapay.com

zef's profile - Liberapay

I am the main developer of SilverBullet, the note taking app for engineers. If you would like to support my work and allow me to spend more time on SilverBullet, please …

@zef@social.zef.pub

“Funny” (not really) to consider how open source project easily slip into dependence on #github. In principle you’d think: “it’s just a git repo, you can just push it anywhere” but I started to make a list of aspects a bit harder to move:

Issues and PRs (can be auto migrated it seems)

Sponsors (yep, locked in)

Actions (CI, need to self host?)

Docker image hosting (ghcr, back to docker hub?)

And then there’s of course the fact that like 99% of open source projects are on GitHub. It’s the default, this is where you look for stuff.

@pooza@mstdn.b-shock.org
@release_bot@mstdn.b-shock.org
@NABU_Jena@nabu.social

So, Umzug abgeschlossen. Zum heutigen Digital Independence Day haben wir die Migration all unserer Software-Repos von GitHub zu Codeberg abgeschlossen. Die Patientenverwaltung für Wildvogelhilfen und unser Vogelschlagmelder, welcher demnächst in Jena und Leipzig live geht, findet ihr neben kleineren Hilfstools jetzt dort.

codeberg.org/nabu-jena

Wer bei einem der Projekte helfen will ist gern gesehen ;)

@Codeberg

codeberg.org

nabu-jena

Codeberg is a non-profit community-led organization that aims to help free and open source projects prosper by giving them a safe and friendly home.

@release_bot@mstdn.b-shock.org
@shuppy@fedi.shuppy.org
how can we cut our CI times by 50–90% and reduce our dependency on #github actions, securely and cheaply enough for a large public #rustlang codebase?

we did exactly that for @servo by building a self-hosted runner system that does virtual machine orchestration under the hood, all for barely 400 EUR/month!

talk video:
https://www.youtube.com/watch?v=-W1mSXdlRqA

blog post:
https://www.azabani.com/2025/12/18/shoestring-web-engine-ci.html
slide that reads:

How much faster?

- mach try full workflow: 61m30s → 25m47s (−58%)
- linux-unit-tests job: 34m29s → 3m15s (−90%)
- windows-unit-tests job: 59m14s → 8m4s (−86%)
- lint job: 11m54s → 2m25s (−79%)
- wpt jobs: 25m35s → 20m50s (−18%)
    - But we also went from 20 runners → 3 runners
ALT text

slide that reads: How much faster? - mach try full workflow: 61m30s → 25m47s (−58%) - linux-unit-tests job: 34m29s → 3m15s (−90%) - windows-unit-tests job: 59m14s → 8m4s (−86%) - lint job: 11m54s → 2m25s (−79%) - wpt jobs: 25m35s → 20m50s (−18%) - But we also went from 20 runners → 3 runners

@pooza@mstdn.b-shock.org

github.com/misskey-dev/misskey

Misskey 2025.12.2
特に急ぐ更新もなさそうだから、仕事納め過ぎてからゆっくりかな。

> リバースプロキシやCDNなどのより上流のレイヤでレートリミットを設定したい場合や、緊急時の一時的な緩和策として、Misskey内部でのIPアドレスペースでのレートリミットを無効化できるようにしました。

テスト目的で、これはいいと思った。
使い方を調べないと。

Release 2025.12.2 · misskey-dev/misskey

Note v2025.12.0で行われた「configのtrustProxyのデフォルト値をfalseに変更」について、正しく環境に応じた設定を行わないとサインインが困難になるといった状態を緩和するために、以下の対応を行いました。 正しく設定しないと、上記のような不具合の原因となったり、セキュリティリスクが高まったりする可能性があります。必ず現在のconfigをご確認の上、必要に応じて値を変...

@alecaddd@mastodon.social

Hey open source folks that have large repositories and contributors on their projects, is GitHub still a safe and viable option?
What alternatives are worth considering?
And are the pipelines available well tuned and compatible to build flatpacks and snaps?

@pooza@mstdn.b-shock.org
@mjd@mathstodon.xyz

I have found what seems to be a bug in the pattern matching used by Actions. I would prefer that the bug be in my pattern. If you're familiar with this, would you please take a look at my question here?

stackoverflow.com/q/79848997/1

stackoverflow.com

Github Actions '**' pattern matches an unexpected branch

I have the following Github workflow file: name: test-ci2 on: push: branches: [ '**/ci-*' ] jobs: test: runs-on: ubuntu-latest steps: - run: echo &quot;Triggered by **/ci-*

@tynstar@nerdculture.de

For a long time, was the dominant hosting platform for ( and ), and tried to compete with them.

Looks like both companies are determined to end this era:

First, GitHub started shoving all this AI crap down people's throats. Realizing they probably haven't alienated *everyone* in the FOSS community yet, they now decided to charge money for CI/CD even if you run the build runner on your own machine.

Source: see the quoted post

Meanwhile, gets creative as well: Bitbucket will no longer support forking repos to other projects, and this prevents outsiders from contributing easily to projects. They say the change helps with enterprise features like data residency. That may be true, but I say it also means "goodbye, FOSS".

Source: community.atlassian.com/forums

I guess @Codeberg and other non-commercial |s should start preparing for a large influx of FOSS projects that flee from these platforms.

community.atlassian.com

Deprecation of Forked Repositories Outside the Parent Workspace

Hi Bitbucket Community,  My name is Adam and I am a product manager with the Bitbucket Cloud team. On February 27, 2026, the ability to create new repository forks will be limited to the parent workspace. Existing forks to other workspaces will continue to function as normal for the time being. Wher...

@fasterthanlime@hachyderm.io

GitHub Actions charging per build minute for *self-hosted-runners*? Shit's about to hit the fan lol

You are receiving this email because your usage of GitHub Actions may be impacted by upcoming changes to GitHub Actions pricing.

What’s changing, when

On January 1, 2026, all customers will receive up to a 39% reduction in the net price of GitHub-hosted runners, depending on the machine type used.
On March 1, 2026, we are introducing a new $0.002 per-minute GitHub Actions cloud platform charge that will apply to self-hosted runner usage. Any usage subject to this charge will count toward the minutes included in your plan.
No action is required on your part.
ALT text

You are receiving this email because your usage of GitHub Actions may be impacted by upcoming changes to GitHub Actions pricing. What’s changing, when On January 1, 2026, all customers will receive up to a 39% reduction in the net price of GitHub-hosted runners, depending on the machine type used. On March 1, 2026, we are introducing a new $0.002 per-minute GitHub Actions cloud platform charge that will apply to self-hosted runner usage. Any usage subject to this charge will count toward the minutes included in your plan. No action is required on your part.

@jwildeboer@social.wildeboer.net

So you print a scientific paper at home. A van with HP markings suddenly parks in front of your house. You start reading the paper. You take notes. You finish reading the paper. A person emerges from the van parked in front of your house, knocks on your door and tells you: "It took you 3 hours to read the paper. That'll be $0,36. Cash or card?"

That's more or less what is now doing with self-hosted runners for GitHub Actions.

resources.github.com/actions/2

Introduction of the GitHub Actions cloud platform charge

We are introducing a $0.002 per-minute Actions cloud platform charge
for all Actions workflows across GitHub-hosted and self-hosted runners.
The new listed GitHub-runner rates include this charge. This will not impact
Actions usage in public repositories or GitHub Enterprise Server
customers.

This aligns pricing to match consumption patterns and ensures consistent
service quality as usage grows across both hosting modalities.

This will impact self-hosted runner pricing starting March 1, 2026.
ALT text

Introduction of the GitHub Actions cloud platform charge We are introducing a $0.002 per-minute Actions cloud platform charge for all Actions workflows across GitHub-hosted and self-hosted runners. The new listed GitHub-runner rates include this charge. This will not impact Actions usage in public repositories or GitHub Enterprise Server customers. This aligns pricing to match consumption patterns and ensures consistent service quality as usage grows across both hosting modalities. This will impact self-hosted runner pricing starting March 1, 2026.

@ben@hardill.me.uk

GitHub sending out emails today about a price change taking effect Jan 1st 2026 is a bit cheeky when lots of DevOps teams are likely to be thin on the ground

resources.github.com/actions/2

Now while it does suggest that change is likely a reduction in bills, the change to charge for **self hosted** run time is going to sting (that goes live March 1st 2026)

I think @Codeberg and @forgejo are likely to see another uptick in users.

resources.github.com

Pricing changes for GitHub Actions

GitHub Actions pricing update: Discover lower runner rates (up to 39% off) following a major re-architecture for faster, more reliable CI/CD.

@igrep@precure.ml · Reply to YAMAMOTO Yuji
@pooza@mstdn.b-shock.org

美食丼のVPSに同居している、プライベートリレーも移さないといけない。
サーバーをまたがるデフォルトハッシュタグの維持に必要なパーツなので、超大事。

この機会に pub-relay はやめて、雪餅さんのにでもしようかと。
github.com/yukimochi/Activity-

github.com

GitHub - yukimochi/Activity-Relay: Yet another powerful customizable ActivityPub relay server written in Go.

Yet another powerful customizable ActivityPub relay server written in Go. - yukimochi/Activity-Relay

@joschi@hachyderm.io · Reply to quarkusio

@quarkusio No, don’t do this. You’ll thank yourself later.

Encode this in your build system so that you can do the same thing locally or on any other CI system. That way you’re not tightly coupled to use Actions and debugging build failures in CI gets so much easier.

Both, and , can do this. Same for the selection of the right toolchain.
Let your build tool do this.

Just like letting your build system do its thing and only rebuild what’s necessary.

Don’t write an unmaintainable shell script embedded in unmaintainable YAML documents describing your CI pipeline.

@jabref@foojay.social

We have an early present for you!
Leveraging JabRef's brand new Git integration, it's now possible to directly sync your bibliography with Overleaf by using GitHub as an intermediate.

We have written a short description in our blog post on how to get started.
Currently, only one-way sync is possible!
blog.jabref.org/2025/12/04/ove


Screenshot of Overleaf showing a sample bib file pulled from a GitHub repository
ALT text

Screenshot of Overleaf showing a sample bib file pulled from a GitHub repository

@applech2@rss-mstdn.studiofreesia.com
@sozialwelten@ifwo.eu · Reply to Râu Cao ⚡

@raucao It is also not a part of the official Mastodon Roadmap even though there are some open issues in the GitHub repository concerning E2EE.

I personally hope that it will get integrated into ActivityPub and/or Mastodon but for 2026 and 2027 I do not see any signs that there is anything remotely close to being published.

​s : github.com/mastodon/mastodon/i
: joinmastodon.org/roadmap

Screenshot from the mastodon roadmap 

Roadmap

Here's a glimpse of what we're working on
Released
Quote Posts

Version 4.5: Users can now quote others posts. Users can opt out entirely from all quoting or remove themselves from a quoted post if they wish. Learn more.
Released
Fetch all replies

Version 4.5: No more missing replies to your posts! Threads now search for all replies and display them.
Next release
Collections

Version 4.6: Users and admins can create a collection of accounts they recommend. This allows both new and existing user to easily follow a range of curated users quickly. Learn more.
Next release
Institution support

Version 4.6: Allow institutions more control over the landing page and allow visitors to sign up for updates with an email account.
Next release
Better onboarding

Version 4.6: Make improvements to how new users first arrive on Mastodon so they understand what that can do easily.
Exploring
Moderation tools

Looking at ways to make moderation easier, e.g. shared block lists.
Exploring
Simplify Private Mentions

Make Private Mentions calmer, more like chat messages. Remove them from the public feed (which scares people) and have better notifications.
ALT text

Screenshot from the mastodon roadmap Roadmap Here's a glimpse of what we're working on Released Quote Posts Version 4.5: Users can now quote others posts. Users can opt out entirely from all quoting or remove themselves from a quoted post if they wish. Learn more. Released Fetch all replies Version 4.5: No more missing replies to your posts! Threads now search for all replies and display them. Next release Collections Version 4.6: Users and admins can create a collection of accounts they recommend. This allows both new and existing user to easily follow a range of curated users quickly. Learn more. Next release Institution support Version 4.6: Allow institutions more control over the landing page and allow visitors to sign up for updates with an email account. Next release Better onboarding Version 4.6: Make improvements to how new users first arrive on Mastodon so they understand what that can do easily. Exploring Moderation tools Looking at ways to make moderation easier, e.g. shared block lists. Exploring Simplify Private Mentions Make Private Mentions calmer, more like chat messages. Remove them from the public feed (which scares people) and have better notifications.

Screenshot of open E2EE issues in the github mastodon repo
ALT text

Screenshot of open E2EE issues in the github mastodon repo

@applech2@rss-mstdn.studiofreesia.com
@nullagent@partyon.xyz · Reply to nullagent

Just checked back on the Sha1-Hulud virus/worm. FINALLY npm appears free of obviously infected packages.

I still however am seeing infected machines posting their private data publicly on GitHub.

Not only that, I can see infected developer's github repos are being defaced in realtime.

These microsoft owned platforms seem to be really struggling with stopping this worm.

Query for defaced repos 👇🏿

github.com/search?q=api.airfor

github.com

Build software better, together

GitHub is where people build software. More than 150 million people use GitHub to discover, fork, and contribute to over 420 million projects.

@dillo@fosstodon.org

Migrating from GitHub to our self-hosted server. :blobcatcookienom:

I wrote a post about the current situation with and how we ended up self-hosting our own infrastructure to be robust against data loss. We now store all important data (including issues) in git repositories which are replicated accross and .

dillo-browser.org/news/migrati

dillo-browser.org

Migrating Dillo from GitHub

@nullagent@partyon.xyz · Reply to nullagent

Running my NPM checks again today, I see eight remaining infected packages still circulating on the Microsoft owned platform.

Unlike nodejs package index socket.dev NPM does not show ANY security warnings on these package's pages.

It's pretty wild that these known compromised packages have been circulating for four days now with now response or action from Microsoft despite it being one of the largest security stories this month.

@nullagent@partyon.xyz · Reply to nullagent

Now that the acute phase is slowing there's a VERY important question...

What is actual fucking value does Microsoft (a trillion dollar company) owning GitHub & NPM bring at all?

This shit was an absolute corporate buyout disaster. How the ever living fuck has microsoft owned NPM for FIVE years and still not done proper MFA requirements for publishing packages on NPM.

How the actual fuck are well known vulnerable packages STILL being propagated by NPM.

A three panel meme

Top - "Hack the planet" shouts a man being forced into a police car

Center - A hacker in a ski mask at a computer works. "Some dune nerd"

Bottom - "Wait, no not like that!" -Microsoft
ALT text

A three panel meme Top - "Hack the planet" shouts a man being forced into a police car Center - A hacker in a ski mask at a computer works. "Some dune nerd" Bottom - "Wait, no not like that!" -Microsoft

@pooza@misskey.delmulin.com
@nullagent@partyon.xyz · Reply to nullagent

Running my NPM checks again today, I see eight remaining infected packages still circulating on the Microsoft owned platform.

Unlike nodejs package index socket.dev NPM does not show ANY security warnings on these package's pages.

It's pretty wild that these known compromised packages have been circulating for four days now with now response or action from Microsoft despite it being one of the largest security stories this month.

@nullagent@partyon.xyz · Reply to nullagent

These sorts of NPM worms have been around for a LONG time.

It's typically due a common practice of low 2fa opt-in on NPM accounts.

So be sure to setup NPM 2FA if you're a package maintainer do that asap!

A lesser known NPM capability is that you can disable install time scripts. This may break some packages but its worth a try to see if your projects can work with out any install scripts. 👇🏿

blog.npmjs.org/post/1417028810

Package install scripts vulnerability
Disclaimer: we had been told this vulnerability would be disclosed on Monday, not Friday, so this post is a little rushed and may be edited later.

As disclosed to us in January and formally discussed in CERT vulnerability note VU#319816, it is possible for a maliciously-written npm package, when installed, to execute a script that includes itself into a new package that it then publishes to the registry, and to other packages owned by that user.

npm cannot guarantee that packages available on the registry are safe. If you see malicious code on the registry, report it to support@npmjs.com and it will be taken down.

How to protect yourself
If you are installing a package that you do not trust, you can avoid this vulnerability by running

npm install --ignore-scripts

If you wish to never run scripts at install time, you can instead run

npm config set ignore-scripts true

Either or both of these steps will prevent you from spreading a worm at install time.

If you install a package that contains malicious code and then execute it (e.g. by require()ing it into your code) it could still perform malicious actions. You should not execute any software downloaded from the Internet if you do not trust it, including software downloaded from npm.
ALT text

Package install scripts vulnerability Disclaimer: we had been told this vulnerability would be disclosed on Monday, not Friday, so this post is a little rushed and may be edited later. As disclosed to us in January and formally discussed in CERT vulnerability note VU#319816, it is possible for a maliciously-written npm package, when installed, to execute a script that includes itself into a new package that it then publishes to the registry, and to other packages owned by that user. npm cannot guarantee that packages available on the registry are safe. If you see malicious code on the registry, report it to support@npmjs.com and it will be taken down. How to protect yourself If you are installing a package that you do not trust, you can avoid this vulnerability by running npm install --ignore-scripts If you wish to never run scripts at install time, you can instead run npm config set ignore-scripts true Either or both of these steps will prevent you from spreading a worm at install time. If you install a package that contains malicious code and then execute it (e.g. by require()ing it into your code) it could still perform malicious actions. You should not execute any software downloaded from the Internet if you do not trust it, including software downloaded from npm.

@nullagent@partyon.xyz · Reply to nullagent

Just finished writing another tool, now I can see NINE known compromised packages are still up for download on NPM! ⚠️

This tool crawls the list of known bad packages and downloads the latest bundle.

It then runs my other checks against the downloaded bundle and logs the results.

github.com/datapartyjs/walk-wi

./is-npm-still-dangerous
Reads the data/infected-pkgs.txt
Downloads the latest package metadata for every known infected package
Downloads the current latest package.tgz
Uncompresses and scans the latest version using ./check-projects
Depending upon the scan result
./is-npm-still-dangerous

capacitor-voice-recorder-wav 6.0.3 - STILL COMPROMISED
haufe-axera-api-client 0.0.2 - STILL COMPROMISED
hyper-fullfacing 1.0.3 - STILL COMPROMISED
@ifelsedeveloper/protocol-contracts-svm-idl 0.1.2 - STILL COMPROMISED
my-saeed-lib 0.1.1 - STILL COMPROMISED
quickswap-ads-list 1.0.33 - STILL COMPROMISED
@seung-ju/react-native-action-sheet 0.2.1 - STILL COMPROMISED
tcsp 2.0.2 - STILL COMPROMISED
web-types-lit 0.1.1 - STILL COMPROMISED
Found 9 npm-reports/npm-latest-bad.txt packages STILL compromised!

See npm-reports/npm-latest-bad.txt for full listing.
Warning - Most people probably don't need to run this. It causes a lot of NPM traffic. Warning - There's a few packages this fails to download and check (likely bc's they are hosted outside of NPMjs.org)
ALT text

./is-npm-still-dangerous Reads the data/infected-pkgs.txt Downloads the latest package metadata for every known infected package Downloads the current latest package.tgz Uncompresses and scans the latest version using ./check-projects Depending upon the scan result ./is-npm-still-dangerous capacitor-voice-recorder-wav 6.0.3 - STILL COMPROMISED haufe-axera-api-client 0.0.2 - STILL COMPROMISED hyper-fullfacing 1.0.3 - STILL COMPROMISED @ifelsedeveloper/protocol-contracts-svm-idl 0.1.2 - STILL COMPROMISED my-saeed-lib 0.1.1 - STILL COMPROMISED quickswap-ads-list 1.0.33 - STILL COMPROMISED @seung-ju/react-native-action-sheet 0.2.1 - STILL COMPROMISED tcsp 2.0.2 - STILL COMPROMISED web-types-lit 0.1.1 - STILL COMPROMISED web-types-lit 0.1.1 - STILL COMPROMISED Found 9 npm-reports/npm-latest-bad.txt packages STILL compromised! See npm-reports/npm-latest-bad.txt for full listing. Warning - Most people probably don't need to run this. It causes a lot of NPM traffic. Warning - There's a few packages this fails to download and check (likely bc's they are hosted outside of NPMjs.org)

@nullagent@partyon.xyz · Reply to nullagent

I've spent the last few hours writing down my scripts for detecting this so you can use them!

I'm hitting on two or three ways to detect it and will be adding more.

Watching the attack running I can see developers all over the world still doing their morning `npm i` and getting owned 😭

Maybe let the node developers in your life know about this tool 👇🏿

github.com/datapartyjs/walk-wi

github.com

GitHub - datapartyjs/walk-without-rhythm: A tool to check your repos for signs of NPM supply chain attack

A tool to check your repos for signs of NPM supply chain attack - GitHub - datapartyjs/walk-without-rhythm: A tool to check your repos for signs of NPM supply chain attack

@davidism@mas.to

Anyone experienced GitHub CI `macos-15`(`-latest`) and `-26` runners being really slow for network calls? Werkzeug's server tests take ~14 minutes, versus ~30 seconds on `macos-14`. No other changes, it just got way slower when 15 became latest a few months ago. I have no idea how to debug this.

- 26 github.com/pallets/werkzeug/ac
- 15/latest github.com/pallets/werkzeug/ac
- 14 github.com/pallets/werkzeug/ac

github.com

GitHub Actions: Add Python 3.14 and 3.14t to the testing · pallets/werkzeug@bb5ed19

The comprehensive WSGI web application library. Contribute to pallets/werkzeug development by creating an account on GitHub.

@nullagent@partyon.xyz · Reply to nullagent

Updated my listing of Sha1-Hulud detection tools.

I now have found at least 12 other tools for detecting Sha1-Hulud compromise on your dev box and in infrastructure.

github.com/datapartyjs/walk-wi

Similar Sha1-Hulud 11/24/25 Detection Tools
Links to other projects provided with no warranty express or implied.

https://github.com/TimothyMeadows/sha1hulud-scanner
https://github.com/mottibec/sha1hulud-scanner
https://github.com/gensecaihq/Shai-Hulud-2.0-Detector
https://github.com/tprinty/sha1hulud-action-detector
https://github.com/da1z/amihulud
https://github.com/bobberg/sha1-hulud-folder-checker
https://github.com/servusdei2018/sha1-halud-scan
https://github.com/kevcooper/fremkit
https://github.com/ysskrishna/shai-hulud-detector
https://github.com/Cobenian/shai-hulud-detect
GitHub Scanners
https://github.com/ysskrishna/shai-hulud-detector
panther-labs/panther-analysis#1826
ALT text

Similar Sha1-Hulud 11/24/25 Detection Tools Links to other projects provided with no warranty express or implied. https://github.com/TimothyMeadows/sha1hulud-scanner https://github.com/mottibec/sha1hulud-scanner https://github.com/gensecaihq/Shai-Hulud-2.0-Detector https://github.com/tprinty/sha1hulud-action-detector https://github.com/da1z/amihulud https://github.com/bobberg/sha1-hulud-folder-checker https://github.com/servusdei2018/sha1-halud-scan https://github.com/kevcooper/fremkit https://github.com/ysskrishna/shai-hulud-detector https://github.com/Cobenian/shai-hulud-detect GitHub Scanners https://github.com/ysskrishna/shai-hulud-detector panther-labs/panther-analysis#1826

@nullagent@partyon.xyz
@nullagent@partyon.xyz · Reply to nullagent

These sorts of NPM worms have been around for a LONG time.

It's typically due a common practice of low 2fa opt-in on NPM accounts.

So be sure to setup NPM 2FA if you're a package maintainer do that asap!

A lesser known NPM capability is that you can disable install time scripts. This may break some packages but its worth a try to see if your projects can work with out any install scripts. 👇🏿

blog.npmjs.org/post/1417028810

Package install scripts vulnerability
Disclaimer: we had been told this vulnerability would be disclosed on Monday, not Friday, so this post is a little rushed and may be edited later.

As disclosed to us in January and formally discussed in CERT vulnerability note VU#319816, it is possible for a maliciously-written npm package, when installed, to execute a script that includes itself into a new package that it then publishes to the registry, and to other packages owned by that user.

npm cannot guarantee that packages available on the registry are safe. If you see malicious code on the registry, report it to support@npmjs.com and it will be taken down.

How to protect yourself
If you are installing a package that you do not trust, you can avoid this vulnerability by running

npm install --ignore-scripts

If you wish to never run scripts at install time, you can instead run

npm config set ignore-scripts true

Either or both of these steps will prevent you from spreading a worm at install time.

If you install a package that contains malicious code and then execute it (e.g. by require()ing it into your code) it could still perform malicious actions. You should not execute any software downloaded from the Internet if you do not trust it, including software downloaded from npm.
ALT text

Package install scripts vulnerability Disclaimer: we had been told this vulnerability would be disclosed on Monday, not Friday, so this post is a little rushed and may be edited later. As disclosed to us in January and formally discussed in CERT vulnerability note VU#319816, it is possible for a maliciously-written npm package, when installed, to execute a script that includes itself into a new package that it then publishes to the registry, and to other packages owned by that user. npm cannot guarantee that packages available on the registry are safe. If you see malicious code on the registry, report it to support@npmjs.com and it will be taken down. How to protect yourself If you are installing a package that you do not trust, you can avoid this vulnerability by running npm install --ignore-scripts If you wish to never run scripts at install time, you can instead run npm config set ignore-scripts true Either or both of these steps will prevent you from spreading a worm at install time. If you install a package that contains malicious code and then execute it (e.g. by require()ing it into your code) it could still perform malicious actions. You should not execute any software downloaded from the Internet if you do not trust it, including software downloaded from npm.

@nullagent@partyon.xyz · Reply to nullagent

Now that the acute phase is slowing there's a VERY important question...

What is actual fucking value does Microsoft (a trillion dollar company) owning GitHub & NPM bring at all?

This shit was an absolute corporate buyout disaster. How the ever living fuck has microsoft owned NPM for FIVE years and still not done proper MFA requirements for publishing packages on NPM.

How the actual fuck are well known vulnerable packages STILL being propagated by NPM.

A three panel meme

Top - "Hack the planet" shouts a man being forced into a police car

Center - A hacker in a ski mask at a computer works. "Some dune nerd"

Bottom - "Wait, no not like that!" -Microsoft
ALT text

A three panel meme Top - "Hack the planet" shouts a man being forced into a police car Center - A hacker in a ski mask at a computer works. "Some dune nerd" Bottom - "Wait, no not like that!" -Microsoft

@nullagent@partyon.xyz · Reply to nullagent

I spent more time searching for other Sha1-Hulud detection tools and found four more bringing it to 6 scanners (5 in nodejs).

Linked them all from my readme in case those work better for you.

Best way to beat a worm like this is to keep scanning and keep an eye out for the attacker to try and evade all of our tools.

By using more than one hopefully we make the attackers job harder to evade all of us.

github.com/datapartyjs/walk-wi

github.com

GitHub - datapartyjs/walk-without-rhythm: A tool to check your repos for signs of NPM supply chain attack using BASH

A tool to check your repos for signs of NPM supply chain attack using BASH - datapartyjs/walk-without-rhythm

@nullagent@partyon.xyz · Reply to nullagent

GitHub has almost finished taking down the stolen data posted by the Sha1-Hulud npm/github worm. I only see about 400 repos remaining of the around 23k created by the worm.

This was the most visible evidence of the exploit, just because we can't clearly see the worm's uploads doesn't mean the worm is totally dead yet.

@nullagent@partyon.xyz · Reply to nullagent

I spent more time searching for other Sha1-Hulud detection tools and found four more bringing it to 6 scanners (5 in nodejs).

Linked them all from my readme in case those work better for you.

Best way to beat a worm like this is to keep scanning and keep an eye out for the attacker to try and evade all of our tools.

By using more than one hopefully we make the attackers job harder to evade all of us.

github.com/datapartyjs/walk-wi

github.com

GitHub - datapartyjs/walk-without-rhythm: A tool to check your repos for signs of NPM supply chain attack using BASH

A tool to check your repos for signs of NPM supply chain attack using BASH - datapartyjs/walk-without-rhythm

@nullagent@partyon.xyz · Reply to nullagent

Checking back in on my GitHub query and the stolen data is STILL showing up on github.

I can tell github looks to be deleting the repos a -little- bit faster than they are created. There's still over 15k repos full of stolen credentials and PII available for public download.

I've also noticed some new behavior I hadn't seen before where the worm is now making commits look like Linus Torvalds wrote them. Clearly a delay tactic.

partyon.xyz/@nullagent/1156078

@nullagent@partyon.xyz · Reply to nullagent

At the end of scanning for obvious compromise the `check-projects` script then builds a listing of all of your dependencies and all of the versions your project files mention.

You can find that info under `reports/`

I'm currently working on improving the `check-projects` script so that it will alert you if ANY of your package.json or package-lock.json mentions a known infected package.

@nullagent@partyon.xyz · Reply to nullagent

First pass is super simple and just looks for the file names & package.json signature for signs of infection anywhere in the path you tell it to search.

If it sees anything fishy it tells you where and stops until you've read the alert.

Oh and this only uses bash, sed, awk, grep, curl, and jq. So no npm, node or other big supply chains 🥴

github.com/datapartyjs/walk-wi

@nullagent@partyon.xyz · Reply to nullagent

Woot ok now that I have the dependency graph crawled I can just ship the listing of known bad NPM packages and just compare directly against that.

I updated the scanning script to alert if you have -any- version of an infected package.

You're gonna want to be very careful if you're not infected but have one of these dependencies present.

github.com/datapartyjs/walk-wi

@nullagent@partyon.xyz · Reply to nullagent

At the end of scanning for obvious compromise the `check-projects` script then builds a listing of all of your dependencies and all of the versions your project files mention.

You can find that info under `reports/`

I'm currently working on improving the `check-projects` script so that it will alert you if ANY of your package.json or package-lock.json mentions a known infected package.

@nullagent@partyon.xyz · Reply to nullagent

First pass is super simple and just looks for the file names & package.json signature for signs of infection anywhere in the path you tell it to search.

If it sees anything fishy it tells you where and stops until you've read the alert.

Oh and this only uses bash, sed, awk, grep, curl, and jq. So no npm, node or other big supply chains 🥴

github.com/datapartyjs/walk-wi

@nullagent@partyon.xyz · Reply to nullagent

I've spent the last few hours writing down my scripts for detecting this so you can use them!

I'm hitting on two or three ways to detect it and will be adding more.

Watching the attack running I can see developers all over the world still doing their morning `npm i` and getting owned 😭

Maybe let the node developers in your life know about this tool 👇🏿

github.com/datapartyjs/walk-wi

github.com

GitHub - datapartyjs/walk-without-rhythm: A tool to check your repos for signs of NPM supply chain attack

A tool to check your repos for signs of NPM supply chain attack - GitHub - datapartyjs/walk-without-rhythm: A tool to check your repos for signs of NPM supply chain attack

@nullagent@partyon.xyz · Reply to nullagent

Taking a second to understand the attack rate. I constructed this query below which shows you essentially an up to date listing of developers/code that's been compromised.

Once your box is infected and PII data has been found the worm then uses your github credentials to upload that content so ANYONE can now steal your credentials.

I'm finding multiple repos being popped every minute. This is an extremely active attack right now.

github.com/search?q=%22Sha1-Hu

github.com

Build software better, together

GitHub is where people build software. More than 150 million people use GitHub to discover, fork, and contribute to over 420 million projects.

@dominik@lostfocus.de

How do you nice people reading my blog handle your Github account(s)?

I’ve had my “main” account @lostfocus for ages and used it for pretty much everything I needed to do on Github. Now with my current employer our accounts are put into the SSO system, so I created a second account which went through a couple of names until I changed it in a (probably futile) attempt to look professional to just my name.
But I already know how this will end up – my .gitconfig still has an email address for the other account and now confusingly my work repos have commits from both accounts. And of course I wonder what will happen when the account is being removed from the SSO system. Hm.

How do you do it?

Do you have one account for everything?

Do you have one account for your stuff and one for work?

Do you create a new account every time you have a new employer?

github.com

lostfocus - Overview

I get my kicks above the waistline, sunshine. lostfocus has 73 repositories available. Follow their code on GitHub.

@wiersdorf@fosstodon.org
@toxi@mastodon.thi.ng

Wow, just noticed reached 3700 stars on GitHub — I'm celebrating... 🤩🫠

Heartfelt thanks to all of you who've been helping along the way (in any shape & form) and been supporting this work for all these years and across different programming languages/camps! Merci beaucoup!!! Esp. big Thank You's to fellow fediverse people/supporters from various stages of this project: @avi, @made, @lurvey, @alesroubicek, @brandtryan, @latrokles, @rc101, @jeffpalmer, @jack, @Yura, @danielrothaug, @computersandblues, @shiffman... (apologies if I forgot you/others here!) 🙏😍

Not counting the earlier years spent on my related toxiclibs library collection for Java/Processing (developed between ~2006-2012), the larger thi.ng project is now 14+ years old, starting with various 2D/3D geometry and dataviz-related libraries for Clojure/ClojureScript in 2011.

Since 2018 the main focus has been thi.ng/umbrella, a monorepo collection of (so far) 210+ projects/libraries. It will be 8 years old in January and covers an extremely wide spectrum of topics, use cases, data structures and techniques (take a look at the tag cloud on the thi.ng website or the tag browser[1] to explore the scope and related projects).

These 200+ main libraries are NOT forming a monolithic framework and can largely be used individually. However, many of these libraries are complementing each other, or are structured to be composable, expose related functionality at different levels of abstraction and/or are heavily re-use functionality to ensure high code density and small bundle sizes when building large(r) projects. 99% of the packages have NO 3rd party runtime dependencies... The umbrella meta-project also includes 185 commented standalone example projects, hundreds of code snippets in documentation and readme files, illustrating other possible usage & composition patterns.

The total code size of this project is now around 3850 source files, 140k lines of code and 71k lines of comments/docstrings. The example projects add in total another ~35k lines of code & comments. The average package readme size is 11.8KB. 99.9% of this all has been created & maintained by yours truly...

There're still so many unreleased (and useful/interesting!) parts of functionality I've been working on and still need to figure out how to best refactor and package them up (bit by bit) before releasing... we're not done just yet!

There seemingly are quite a few active users (~1.8 million of combined installs per month) and it's so pleasing to see how these tools have matured, are stable/reliable[2] and it confirms to me these efforts were all somehow worth it. Especially this year, I've also spent a lot more time myself using these packages in production, mostly for client projects, but also my own (some of which will be open sourced too). Of course, we all have our own particular likes and preferences for our own tools, but for my kind of work/workflows, provides some of the most varied, productive, _composable_ and malleable tools I've ever used...

Happy coding! 🙌

[1] demo.thi.ng/umbrella/thing-bro

[2] ...even many of those packages which still manage to have a v0.x.y version number, often for years already! My release tool only creates new major versions when there're breaking changes, so if the API is already stable, the version stays at 0.x — I just need to manually bump some of them to a v1.0... 😅

@caten@mathstodon.xyz

Here's a totally off-the-cuff pitch for the web: I just want to be able to load a webpage from a swarm by leeching, and then click an "I approve" button if it looks non-sketchy and I want to seed the page. I want to bookmark magnet links to make human-readable URLs and allow collisions between actual names/content to be decided socially (e.g. click to accept a new version of this page from this new swarm). I don't want a bunch of new protocols. No for domain names or donations. No vibe-coded corporate-sponsored AI BS. No repos. Just give me the wild west with everything visible and no default seeding so that bad actors don't bother with it so much. Run it through a or something if you want privacy.

@pooza@mstdn.b-shock.org
@bkuhn@copyleft.org · Reply to Bruno Bord

Thanks those who shared this satire:
mcsweeneys.net/articles/i-work

IMO, only paragraph missing was:

> “3 hours/week, my company lets me upstream code to their favorite MIT-licensed project! That counts. Of course, in exchange, I have to post on y-combinator how bad is & file a ticket telling some 'd project to change licenses. Oh, & all the best patches with new features stay on our internal branch…but *I* fixed all typos & misspellings upstream!”

Cc: @aral @brunobord

mcsweeneys.net

I Work For an Evil Company, but Outside Work, I’m Actually a Really Good Person

I love my job. I make a great salary, there’s a clear path to promotion, and a never-ending supply of cold brew in the office. And even though my j...

@Alex0007@mastodon.social

TIL: If you're using the `api.githubcopilot.com/mcp` MCP named "all", it doesn't mean you automatically get the `all` toolset; instead, you receive the `default` toolset. To request the toolset named `all`, you must explicitly provide the header: `"X-MCP-Toolsets": "all"`. This behavior is counterintuitive because the URL implies access to all tools, but attempts to call some of them fail without the required header.

github.com/github/github-mcp-s

github.com

github-mcp-server/docs/remote-server.md at main · github/github-mcp-server

GitHub's official MCP Server. Contribute to github/github-mcp-server development by creating an account on GitHub.

@vladimirleonidovich@mastodon.social

Посоветуйте приложение для , куда я смогу сохранять токены доступа к разными сервисам и API: , , и другие.
Пробовал искать, но дельного не нашёл.

@release_bot@mstdn.b-shock.org
@tdp_org@mastodon.social

Sorry, colleagues...and good luck.

Screenshot of a GitHub Pull Request showing "Files changed: 178" and "7538 lines added, 9429 lines removed".
ALT text

Screenshot of a GitHub Pull Request showing "Files changed: 178" and "7538 lines added, 9429 lines removed".

@SylvieLorxu@chaos.social

2.39.2's release on has been delayed due to the regular incompetent review program blocking the update due to "lack of provided login credentials for testing".

I've filed an appeal, stating that Catima is fully offline and has no accounts. We will see.

If you're a Google Play user, to be honest, please just use Catima from , or . The more people not on Google Play, the less power Google has on blocking updates :)

A screenshot of the Google Play Console stating that the app update has been rejected
ALT text

A screenshot of the Google Play Console stating that the app update has been rejected

The appeal screen, containing the text "There is no login wall. The app does not have any accounts and does not need any login. It works fully offline.", which is my explanation
ALT text

The appeal screen, containing the text "There is no login wall. The app does not have any accounts and does not need any login. It works fully offline.", which is my explanation

The so-called "login wall" according to Google, which is just the home screen
ALT text

The so-called "login wall" according to Google, which is just the home screen

@jeffluszcz@mastodon.social

Curious about the latest trends in Open Source, GitHub, and AI? I recently had a great conversation with GitHub’s @alacolombiadev and @kedashakerr about this year’s Octoverse Report! We discussed how AI is shaping programming language preferences, the evolving approach to security in open source projects, and what these changes mean for developers.
Tune in to hear our thoughts and takeaways!
the-github-podcast.simplecast.

Three people are on a podcast. They are in different rooms. There are 2 women and one man. Their images are arranged vertically.
ALT text

Three people are on a podcast. They are in different rooms. There are 2 women and one man. Their images are arranged vertically.

@SylvieLorxu@chaos.social

2.39.2's release on has been delayed due to the regular incompetent review program blocking the update due to "lack of provided login credentials for testing".

I've filed an appeal, stating that Catima is fully offline and has no accounts. We will see.

If you're a Google Play user, to be honest, please just use Catima from , or . The more people not on Google Play, the less power Google has on blocking updates :)

A screenshot of the Google Play Console stating that the app update has been rejected
ALT text

A screenshot of the Google Play Console stating that the app update has been rejected

The appeal screen, containing the text "There is no login wall. The app does not have any accounts and does not need any login. It works fully offline.", which is my explanation
ALT text

The appeal screen, containing the text "There is no login wall. The app does not have any accounts and does not need any login. It works fully offline.", which is my explanation

The so-called "login wall" according to Google, which is just the home screen
ALT text

The so-called "login wall" according to Google, which is just the home screen

@emilis@social.linux.pizza

TIL why I can't access release files from open-source projects on GitHub anymore.

It seems that the IP for release-assets.githubusercontent.com got added to ipthreat.net list:

ipthreat.net/ip/185.199.111.133

Malware is actually being distributed via GitHub, but the majority of repos are probably safe and useful.

By adding the GitHub IPs, the IP threat list becomes unusable. By not-adding them becomes less useful. An interesting dilema.

I guess it's one more reason to migrate your open-source project off GitHub. On the other hand @Codeberg and similar alternatives should take notice and prepare in advance.

ipthreat.net

IPThreat - IP Address: 185.199.111.133

IPThreat is a 100% free and community powered ip address database of hackers and botnets. Protect your computers today and create a free account.

@pooza@misskey.delmulin.com
@IvanSanchez@mastodon.social

I'm in a internal group for high-profile FOSS projects (due to @leaflet having a few kilo-stars), and the second most-wanted feature is "plz allow us to disable copilot reviews", with the most-wanted feature being "plz allow us to block issues/PRs made with copilot".

Meanwhile, there's a grand total of zero requests for "plz put copilot in more stuff".

This should be significative of the attitude of veteran coders towards creep.

A screenshot of a github discussion titled "can't disable copilot code reviews"
ALT text

A screenshot of a github discussion titled "can't disable copilot code reviews"

A screenshot of a github discussion titled "Allow us to block Copilot-generated issues (and PRs) from our own repositories"
ALT text

A screenshot of a github discussion titled "Allow us to block Copilot-generated issues (and PRs) from our own repositories"

@sethmlarson@mastodon.social
@IvanSanchez@mastodon.social

I'm in a internal group for high-profile FOSS projects (due to @leaflet having a few kilo-stars), and the second most-wanted feature is "plz allow us to disable copilot reviews", with the most-wanted feature being "plz allow us to block issues/PRs made with copilot".

Meanwhile, there's a grand total of zero requests for "plz put copilot in more stuff".

This should be significative of the attitude of veteran coders towards creep.

A screenshot of a github discussion titled "can't disable copilot code reviews"
ALT text

A screenshot of a github discussion titled "can't disable copilot code reviews"

A screenshot of a github discussion titled "Allow us to block Copilot-generated issues (and PRs) from our own repositories"
ALT text

A screenshot of a github discussion titled "Allow us to block Copilot-generated issues (and PRs) from our own repositories"

@sethmlarson@mastodon.social
@IvanSanchez@mastodon.social

I'm in a internal group for high-profile FOSS projects (due to @leaflet having a few kilo-stars), and the second most-wanted feature is "plz allow us to disable copilot reviews", with the most-wanted feature being "plz allow us to block issues/PRs made with copilot".

Meanwhile, there's a grand total of zero requests for "plz put copilot in more stuff".

This should be significative of the attitude of veteran coders towards creep.

A screenshot of a github discussion titled "can't disable copilot code reviews"
ALT text

A screenshot of a github discussion titled "can't disable copilot code reviews"

A screenshot of a github discussion titled "Allow us to block Copilot-generated issues (and PRs) from our own repositories"
ALT text

A screenshot of a github discussion titled "Allow us to block Copilot-generated issues (and PRs) from our own repositories"

@release_bot@mstdn.b-shock.org
@grobmeier@mastodon.social

I never imagined GitHub would ask me to speak about Log4Shell.
But it happened.

GitHub asked me to share the story as I lived it, for the benefit of all maintainers and users of open source. How could I say no?

I hope it helps build a more secure future.

No more Log4Shell.

github.blog/open-source/inside

github.blog

Inside the breach that broke the internet: The untold story of Log4Shell

Log4Shell proved that open source security isn't guaranteed and isn’t just a code problem.

@pooza@mstdn.b-shock.org

icalenar gemへのこのコミットで、icalendar-rrurleが動かなくなってる。多分。
github.com/icalendar/icalendar

修正の規模が小さいから、自分でも直せるかもしれないが。
icalendarとicalendar-rruleと、どっちのgemを修正するのが筋がよい?

Prevent surprises by not delegating all DowncasedHash methods to Hash · icalendar/icalendar@21379f4

icalendar.rb main repository. Contribute to icalendar/icalendar development by creating an account on GitHub.

@grobmeier@mastodon.social

I never imagined GitHub would ask me to speak about Log4Shell.
But it happened.

GitHub asked me to share the story as I lived it, for the benefit of all maintainers and users of open source. How could I say no?

I hope it helps build a more secure future.

No more Log4Shell.

github.blog/open-source/inside

github.blog

Inside the breach that broke the internet: The untold story of Log4Shell

Log4Shell proved that open source security isn't guaranteed and isn’t just a code problem.

@lazarus@fosstodon.org · Reply to Johannes Brakensiek

I have to add, that fractional scaling feature on @elementary works mainly due to the impressive work of @leolost. So in case you enjoy that feature as much as I do please consider supporting him on

github.com/leolost2605

github.com

leolost2605 - Overview

Currently studying at Karlsruhe Institute for Technology. Contributing to Open Source in my freetime. Mostly @elementary :) - leolost2605

@Edent@mastodon.social
@lazarus@fosstodon.org · Reply to Johannes Brakensiek

I have to add, that fractional scaling feature on @elementary works mainly due to the impressive work of @leolost. So in case you enjoy that feature as much as I do please consider supporting him on

github.com/leolost2605

github.com

leolost2605 - Overview

Currently studying at Karlsruhe Institute for Technology. Contributing to Open Source in my freetime. Mostly @elementary :) - leolost2605

@tdp_org@mastodon.social

Sorry, colleagues...and good luck.

Screenshot of a GitHub Pull Request showing "Files changed: 178" and "7538 lines added, 9429 lines removed".
ALT text

Screenshot of a GitHub Pull Request showing "Files changed: 178" and "7538 lines added, 9429 lines removed".

I feel for this user - I’m a fellow ADHD sufferer and their distress is all too clear to me - and I tried to help them in the replies.

But on the other hand, I’m utterly enraged at the broader problem, and all the people who aren’t taking action today, choosing instead to wait until the water is past their neck.

This is the latest example of why we shouldn’t use #nonfree / #proprietary / #restricted and #centralized platforms like #Telegram, #Discord, #WhatsApp, #Signal, #Instagram, #Facebook, #Twitter, #LinkedIn, #Bluesky, #GitHub, and others.

There’s a whole-ass history of centralized platforms having the same class of issues. When are y’all gonna stop ignoring the problem and start exercising the power you have?

It’s as simple as quitting centralized platforms, switching to #FreedomRespecting #decentralized platforms like #ActivityPub and #XMPP, and telling others to do the same.

Create your communities there, and tell others about them. Move all your activity there. Onboard your friends and family. When there’s no other way to reach you, they will move.

Keep up the social pressure, and never relent.

Here’s a user’s guide to XMPP, for whoever needs it.

And developers? Get involved, improve the protocols, the clients, the servers…heck, I’m pretty sure a lot of features and fixes are popular/longstanding enough to make it feasible to crowdfund your patches!

#FreeSoftware #Libre #OpenSource

Screenshot of Fedi post, with the display name and handle hidden. Text -

Well, this is depressing. My country has silently blocked #Discord and now I can't access my ADHD support group for body doubling. Someone called his internet service provider and they told him the telecom commission has blocked the app and isn't allowed to announce it in the media. I can't even access any free VPN sites, those have been blocked too. Discord has been my crutch for the past few months and the only way I've been functioning. So depressed. Can't find any free alternatives.
ALT text

Screenshot of Fedi post, with the display name and handle hidden. Text - Well, this is depressing. My country has silently blocked #Discord and now I can't access my ADHD support group for body doubling. Someone called his internet service provider and they told him the telecom commission has blocked the app and isn't allowed to announce it in the media. I can't even access any free VPN sites, those have been blocked too. Discord has been my crutch for the past few months and the only way I've been functioning. So depressed. Can't find any free alternatives.

@harrysintonen@infosec.exchange

You can kind of tell that has started the migration to .

Github status panel showing all kinds of errors and degradation. Image captured from https://www.githubstatus.com/
ALT text

Github status panel showing all kinds of errors and degradation. Image captured from https://www.githubstatus.com/

@xoron@infosec.exchange

Want to send messages and video calls with:

* no installs
* no sign-ups
* no tracking
* end-to-end encryption

This new prototype uses PeerJS to establish a secure browser-to-browser connection. Everything is ephemeral and cleared when you refresh the page—true zerodata privacy!

Check out the [testable demo here](p2p.positive-intentions.com/if).

I am working towards a look-and-feel to match Whatsapp as seen in this [hardcoded UI demo](glitr.positive-intentions.com).

IMPORTANT NOTE: This is still a work-in-progress and a close-source project. It is based on the open source MVP see [here](github.com/positive-intentions). It has NOT been audited or reviewed. For testing purposes only, not a replacement for your current messaging app.

* Docs: positive-intentions.com/docs/c
* Reddit: reddit.com/r/positive_intentio
* GitHub: github.com/positive-intentions

github.com

positive-intentions

positive-intentions has 9 repositories available. Follow their code on GitHub.

@jaredwhite@indieweb.social

The enshittification continues.

“To ensure the move to Azure is completed within 12 months, GitHub’s leadership team is asking employees to delay new features in favor of the Azure migration.”

Everything about this is upside-down and backwards. Nobody who is a regular user of GitHub is asking for this. It is entirely the sort of bullshit large enterprises do because they're large enterprises.

I don't want my open source code hosted on Micro$oft Azure. Do you?

theverge.com/tech/796119/micro

theverge.com

Microsoft is moving GitHub over to Azure servers

Most of the migration will happen within 12 months

@zkat@toot.cat

FYI: As part of a larger move away from GitHub, I've archived Big Brain on it and moved all future development over to Codeberg, at codeberg.org/zkat/big-brain

Please use that repo from now on.

Additionally: I am in the process of trying a major rewrite of the crate that I'm hoping will be much simpler, and much more efficient, thanks to features now available in recent version of Bevy! I'm very excited :)

codeberg.org

big-brain

Utility AI library for the Bevy game engine

@blauertee@berlin.social

Just wrote a feature request for attaching dates to posts on the . Think that would be a really great feature feel free to leave some thumbs 😇.

PS: I'm not always quite sure which based microblogging server's community I should address with such things, but I guess mastodon is the most widely used server and thus if they implement it, it's most likely that other servers and clients will follow right?

最近のメンテ。ご興味ある方へ。(videoやaudioのアップロードまわり)

ffmpegのコマンドラインを調整しました。
コマンドラインの最適化は、ChatGPTにも手伝ってもらいました。

github.com/pooza/mulukhiya-too

ここで定義したコマンドが、Mastodon本来の処理の手前で実行されています。
videoやaudioがアップロードされる機会なんてほとんどないんだけどw、ご興味ある方はお試しください。

github.com

mulukhiya-toot-proxy/app/lib/mulukhiya/ffmpeg_command_builder.rb at master · pooza/mulukhiya-toot-proxy

Fediインスタンスへの投稿に対して、ハッシュタグの追加等を行うプロキシ。通称「モロヘイヤ」。. Contribute to pooza/mulukhiya-toot-proxy development by creating an account on GitHub.

@release_bot@mstdn.b-shock.org
@eniko@mastodon.gamedev.place

okay i've polished up my FediTag javascript which embeds a feed of Mastodon posts from one account using a particular hashtag on a website or page. you can find it on github github.com/Enichan/feditag

example of feditag in the wild being used on enikofox.com/blockgame

it shows a post with two images, above another post with a poll
ALT text

example of feditag in the wild being used on enikofox.com/blockgame it shows a post with two images, above another post with a poll

@caos@anonsys.net · Reply to Lasse auf Friendica
@lassegismo das mit den Abstimmungen ist leider die einzige Funktion, die ich bei auch sehr schmerzlich vermisse. Friendica kann bislang keine Umfragen erstellen und auch nicht dran teilnehmen, nur die (Zwischen-)Ergebnisse anzeigen...
Das Issue "AP: Support for Polls " liegt aber schon leider länger wieder brach... vielleicht kann es jemand von den -Aktiven mal reaktivieren?

github.com

AP: Support for Polls · Issue #11093 · friendica/friendica

Is the feature request related to a problem? Please describe. Mastodon, Pleroma and Misskey have a 'polls' feature. As far as I can tell they're compatible with each other. As a Misskey user I can ...

@pooza@mstdn.b-shock.org

github.com/pooza/beat-beats

Macの Music.app で再生中の曲を、

・ナウプレの体裁に整形してクリップボードに収める
・アートワークをデスクトップに保存

するAppleScriptアプリを、ChatGPTに作らせました。
自分はほとんど何もしてないです。リポジトリとして公開して、README.mdを微修正したぐらいw

github.com

GitHub - pooza/beat-beats

Contribute to pooza/beat-beats development by creating an account on GitHub.

@FinchHaven@sfba.social

This... seems very interesting

is "...standardizing parts of in an effort to establish long-term governance for the protocol."

"to establish long-term governance for the protocol"

Here: docs.bsky.app/blog/taking-at-t

Also see at :

"Add patent pledge link to README (# 4246)"

"Bluesky Social PBC has committed to a software patent non-aggression pledge. For details see [the original announcement] (bsky.social/about/blog/10-01-2)."

Here: github.com/bluesky-social/atpr

All that said, not sure exactly what it *means* long-term, but it is... interesting

Add patent pledge link to README (#4246) · bluesky-social/atproto@d239f0b

add patent pledge link to readme

@stacksize@mastodon.social
@monkeydom@mastodon.social

UI reached another level of ridiculousness in terms of performance and UI tradeoffs.

Get your shit together. Native tools can handle this shit easily without compromising the user experience.

Design your fckin'g frontend stack with the typical use cases and performance in mind. *sigh*

GitHub UI on diffs showing the following text:
"You're in single-file mode
Due to the large number of changes in this pull request, only one file is being shown at a time.

Use the Previous and Next buttons to move between files.

Ok, got it
"
ALT text

GitHub UI on diffs showing the following text: "You're in single-file mode Due to the large number of changes in this pull request, only one file is being shown at a time. Use the Previous and Next buttons to move between files. Ok, got it "

@bananapi@mastodon.social
Banana Pi BPI-R4 Lite Openwrt source code public on github
https://forum.banana-pi.org/t/bpi-r4-lite-openwrt-source-code-on-github/24502
#github #sourcecode #openwrt #Mediatek #MT7987 #router #network
ALT text

Banana Pi BPI-R4 Lite Openwrt source code public on github https://forum.banana-pi.org/t/bpi-r4-lite-openwrt-source-code-on-github/24502 #github #sourcecode #openwrt #Mediatek #MT7987 #router #network

@inautilo@mastodon.social

I know many people who are aware of the importance of #FreedomRespecting software, data, and culture - and the related issues of digital sovereignty and privacy.

Paradoxically, a lot of these people also participate in, or even maintain, communities hosted on #nonfree / #proprietary / #restricted or #centralized platforms like #Telegram, #Discord, #WhatsApp, #Signal, #Instagram, #Facebook, #Twitter, #LinkedIn, #Bluesky, #GitHub, and others.

To state the obvious, each community which chooses a proprietary platform - or bridges to it - is also giving another reason for others to be on that platform. It’s reinforcing network effect.

Conversely, if these communities chose to move to free platforms, their members would be forced to move as well. In other words, these communities have the opportunity to push for change on a massive scale.

Sure, you have to reach out to people on proprietary platforms, if that’s where the majority are. But you cannot be stopping there - you must have a strategy to move people away from proprietary platforms to free platforms.

To give the example of #OpenStreetMap -

  • I announce events on free platforms sooner
  • I remind people on proprietary platforms that they should join the free platforms to get notified earlier
  • After each event, we invite people to our #XMPP channel, which is not bridged to any other platform.
  • All organizational talk takes place on our XMPP channel, which is not bridged to any other platform.
  • I minimize my participation on proprietary platforms, and communities which bridge to them. The bulk of my activity happens on free platforms.
  • I have never submitted data to Mapillary or KartaView, because their clients and servers are proprietary. All my contributions go to #WikimediaCommons and #Panoramax.

So to the people who are choosing - and therefore promoting - proprietary platforms, I ask…

How do you think things are going to change, if everyone keeps choosing what is easiest for them, and keeps choosing, supporting, and promoting proprietary platforms?

What part are you playing in making things better? Or are you just going to go with the flow of the world, even if you know it to be wrong?

They don’t like answering these questions.

Instead, I invite them to find the integrity and courage to answer them.

Or, to find the integrity and courage to make the obvious change and do the obvious right thing.

People hate it when I bring this up. Sorry, but my conscience dictates that I speak up for what is right. Silence is complicity, and it gets us nowhere.

#FreeSoftware #Libre #OpenSource #OpenData

fe.disroot.org

FEDIsroot

@release_bot@mstdn.b-shock.org
@phranck@oldbytes.space

Liebe Folglinge,

ich suche nach einem neuen Job als und/oder Entwickler. Ich spreche , (auch Server-Side) und und nutze die ganzen Tools drumherum (, , , , etc.). Ich bringe 30 Jahre Berufserfahrung als Software-Entwickler mit, davon knapp 20 im Ökosystem.

Am Idealsten waere eine zu 100% remote. Sollte es im Raum oder etwas geben, dann auch gerne vor Ort.

Ich danke euch fuers Teilen. 🙏🏻

LinkedIn: linkedin.com/in/phranck/
Xing: xing.com/profile/Frank_Gregor0

xing.com

Frank Gregor - Senior iOS/macOS Developer - Cadrage GmbH

Senior iOS/macOS Developer

@zkat@toot.cat

GitHub’s relevance as a development platform is rapidly devolving: I have gotten more spam on there and through there in the past couple of weeks than I will get in an entire year or two, and Copilot means they just don’t care.

Open Source deserves new homes. I’ll continue moving my projects away.

@creepy_owlet@mastodon.online

people, how would you react if a project you use or contribute to migrated from to ?

Boosts welcome, let's collect some opinions.

  • I would only welcome such a move13 (93%)
  • It would be annoying but I'll live with it0 (0%)
  • I won't touch or interact with it any more0 (0%)
  • I could not care less1 (7%)
@igrep@precure.ml · Reply to YAMAMOTO Yuji
@inventaire@mamot.fr

Code migration to @Codeberg ✅ 🎉

codeberg.org/inventaire/

Bye bye Microsoft/Github, we are excited to finally have our code forge also running on libre/free software, and hosted by a fellow non-profit! Thanks @forgejo and @Codeberg for the amazing work!

codeberg.org

inventaire

Codeberg is a non-profit, community-led organization that aims to help free and open source projects prosper by giving them a safe and friendly home.

@bagder@mastodon.social

tip: go to your profile => settings => passwords and authentication and in there, make sure to disable SMS for 2FA as it might otherwise have remained enabled.

The "SMS/Text message" enable section from GitHub
ALT text

The "SMS/Text message" enable section from GitHub

@bagder@mastodon.social

tip: go to your profile => settings => passwords and authentication and in there, make sure to disable SMS for 2FA as it might otherwise have remained enabled.

The "SMS/Text message" enable section from GitHub
ALT text

The "SMS/Text message" enable section from GitHub

@release_bot@mstdn.b-shock.org
@teleclimber@social.tchncs.de

I wonder if the open source community will splinter if many projects move to one of these services? How many different logins will users need to have to contribute and report issues on the projects they use? Will there be "bridges" like there is for Fedi<->AT?

To be clear we def *should* move off , but it might be painful.

mastodon.gamedev.place/@joniko

mastodon.gamedev.place

Joni Korpi (@jonikorpi@mastodon.gamedev.place)

If you can call Forgejo/Codeberg a Mastodon-like alternative to GitHub, then https://tangled.sh/ is a Bluesky-like one: Git-over-atproto. Still in alpha, but looks interesting.

@soulsource@mastodon.gamedev.place

When moving personal projects off , how would you deal with the existing repos there?

Deleting the repos would invalidate all links to them, but leaving the code on Github also does not feel right...

(Boosts welcome)

  • Keep, unchanged0 (0%)
  • Keep, but update README6 (75%)
  • Delete1 (13%)
  • Some other option -> comment1 (13%)
@release_bot@mstdn.b-shock.org
@ben@hardill.me.uk

Hmm, most of my GitHub CI jobs are failing because it appears NPM have added rate limiting.

Remind me again, who owns both NPM and GitHub these days?

@ben@hardill.me.uk

Hmm, most of my GitHub CI jobs are failing because it appears NPM have added rate limiting.

Remind me again, who owns both NPM and GitHub these days?

@bkuhn@copyleft.org · Reply to Michael Downey 🚩

3 yrs ago, @downey wrote:
> “💡 Today is a perfect day to exercise your independence from , & .
> ☣️ is the equivalent of & for software development -- creators of the most enticing proprietary walled garden ever made for …
> Don't be stuck when …change[s] the rules on you.“
> GiveUpGitHub.org
…now ∃ more reasons to stop procrastinating & GiveUpGitHub *now*…
social.kernel.org/objects/bd3d
mastodon.social/@glyph/1149959

Try @Codeberg today!

GitHub so-called “Octocat” logo/mascot holds in one tentacle holds 💰. Six other tentacles form a cage for the words “USER RIGHTS” — which are set in blue stone but are crumbling under the force of the tentacles. The final tentacle reaches out with an open palm — presuambly to collect even more rights & money from its users.
ALT text

GitHub so-called “Octocat” logo/mascot holds in one tentacle holds 💰. Six other tentacles form a cage for the words “USER RIGHTS” — which are set in blue stone but are crumbling under the force of the tentacles. The final tentacle reaches out with an open palm — presuambly to collect even more rights & money from its users.

@bkuhn@copyleft.org · Reply to Codeberg

😲🤬 re: what's happened to @Codeberg today.
The AI ballyhoo *is* a real DDoS against one of the few code hosting sites that takes a stand against slurping code into LLM training sets — in violation of .

Deregulation/lack-of-regulation will bring more of this. ∃ plenty of blame to go around, but & deserve the bulk of it; they trailblazed the idea that FOSS code-hosting sites are lucrative targets.

giveupgithub.org

giveupgithub.org

Give Up GitHub - Software Freedom Conservancy

The Software Freedom Conservancy provides a non-profit home and services to Free, Libre and Open Source Software (FLOSS) projects.

@bkuhn@copyleft.org · Reply to Bradley M. Kuhn

… I was quoted in *The Register*:
> “The problems w/ have been growing for some time. We at have always been concerned about the issue of using proprietary software to write . However, the integration w/ so deeply into the platform, and 's flagrant use of content hosted on GitHub to train their own LLMs makes a departure from GitHub urgent for all FOSS developers.”
theregister.com/2025/08/15/cod
I hope it inspires you to ! giveupgithub.org
(3/3)

GitHub so-called “Octocat” logo/mascot in one tentacle holds 💰. Six other tentacles form a cage for the words “USER RIGHTS” — which are set in blue stone, but are crumbling under the force of the tentacles. The final tentacle reaches out with an open palm — presuambly to collect even more rights & money from its users.
ALT text

GitHub so-called “Octocat” logo/mascot in one tentacle holds 💰. Six other tentacles form a cage for the words “USER RIGHTS” — which are set in blue stone, but are crumbling under the force of the tentacles. The final tentacle reaches out with an open palm — presuambly to collect even more rights & money from its users.

@tdp_org@mastodon.social

I tried a GitHub Copilot PR review as it's been ages since I last did.

It was wrong on 3 out of 3 suggestions it made:

1. It suggested inverting the IP ACL and API key check such that it'd have allowed anyone to purge anything from our CDN cache
2. It said I'd got some basic logic wrong (I hadn't) on 1 of ~20 changes of the same type (var not set or var == "" -> strlen(var) == 0)
3. It made up a service name and wanted me to use that

What a pile of shit.

@jwildeboer@social.wildeboer.net

I hadn't noticed until today, but (The fast, fun, small ActivityPub server) also made the move from to :) They left a nice goodbye message on Github too.

codeberg.org/superseriousbusin

GoToSocial README on Github:

GoToSocial

This is a mirror. You can find us on https://codeberg.org/superseriousbusiness/gotosocial.

We will stop mirroring to Github after 0.20 is released. This will likely be sometime in August.
ALT text

GoToSocial README on Github: GoToSocial This is a mirror. You can find us on https://codeberg.org/superseriousbusiness/gotosocial. We will stop mirroring to Github after 0.20 is released. This will likely be sometime in August.

@bkuhn@copyleft.org · Reply to Bradley M. Kuhn

… I was quoted in *The Register*:
> “The problems w/ have been growing for some time. We at have always been concerned about the issue of using proprietary software to write . However, the integration w/ so deeply into the platform, and 's flagrant use of content hosted on GitHub to train their own LLMs makes a departure from GitHub urgent for all FOSS developers.”
theregister.com/2025/08/15/cod
I hope it inspires you to ! giveupgithub.org
(3/3)

GitHub so-called “Octocat” logo/mascot in one tentacle holds 💰. Six other tentacles form a cage for the words “USER RIGHTS” — which are set in blue stone, but are crumbling under the force of the tentacles. The final tentacle reaches out with an open palm — presuambly to collect even more rights & money from its users.
ALT text

GitHub so-called “Octocat” logo/mascot in one tentacle holds 💰. Six other tentacles form a cage for the words “USER RIGHTS” — which are set in blue stone, but are crumbling under the force of the tentacles. The final tentacle reaches out with an open palm — presuambly to collect even more rights & money from its users.

@quincy@chaos.social

I wanted to start a side project and suddenly it feels very icky to clone from ...

Not that the centralization wasn't problematic before, but I really hope projects will start diversifying their hosting now.

@avuko@infosec.exchange

I’m going to migrate off to now.

I’m wondering how much time and effort it will take.

Update 1: 31 repositories, and there is some mouse clicking involved. Tempted to build a script, but not yet.

@patbaumgartner@mastodon.social

Explored the awesome-mcp-servers repo on GitHub today 🤯. Found a huge variety of MCP servers. Then searched on Google and found even more.

Whatever you search for, there is probably an "awesome" repo for it - Java, Kubernetes, Spring Boot, and more.

github.com/punkpeye/awesome-mc
-servers

github.com

GitHub - punkpeye/awesome-mcp-servers: A collection of MCP servers.

A collection of MCP servers. Contribute to punkpeye/awesome-mcp-servers development by creating an account on GitHub.

@algernon@come-from.mad-scientist.club

Starting August 20, 2025, I will not be contributing to projects hosted on #GitHub via GitHub itself, unless I am paid handsomely for my troubles.

If I need to report an issue, or send a patch, I will either keep the report / patch to myself, publish it on my forge, or if I really, really want to contribute, I will send an e-mail. But opening an issue, or sending a PR on GitHub itself? Not going to happen, unless I'm paid for it.

#GiveUpGitHub

@bkuhn@copyleft.org · Reply to Codeberg

😲🤬 re: what's happened to @Codeberg today.
The AI ballyhoo *is* a real DDoS against one of the few code hosting sites that takes a stand against slurping code into LLM training sets — in violation of .

Deregulation/lack-of-regulation will bring more of this. ∃ plenty of blame to go around, but & deserve the bulk of it; they trailblazed the idea that FOSS code-hosting sites are lucrative targets.

giveupgithub.org

giveupgithub.org

Give Up GitHub - Software Freedom Conservancy

The Software Freedom Conservancy provides a non-profit home and services to Free, Libre and Open Source Software (FLOSS) projects.

@pachli@mastodon.social

Coming to Current in a few days - support for translating posts on your device.

Helpful if your server doesn't support translation, and can be used to translate posts your server refuses to translate.

Won't be available in the and releases, as this feature uses the same non-free Google machine learning libraries as the "Warn if you're posting in the wrong language" feature.

Preferences UI for the new feature. You can choose to always translate using the server (current behaviour), use the server, falling back to on-device translation if the server returns an error, or always use on-device translation.
ALT text

Preferences UI for the new feature. You can choose to always translate using the server (current behaviour), use the server, falling back to on-device translation if the server returns an error, or always use on-device translation.

@sakurasubnet@bumscode.com

So search engines become worse and after the github announcement, oss projects will scatter around to other git hosting providers. Is there a oss project database, where I can lookup if there is already something for my needs? That would be really helpful. If not, this would be a nice project - A human curated, searchable and tagged list of projects.

Boost for reach <3

@toxi@mastodon.thi.ng

Would love to hear migration thoughts & plans (if any) from other FOSS maintainers (and sponsors!) currently using Github Sponsors. Are you planning/supporting to leave? Are you afraid you'll lose sponsors?

Personally, I'd also love to hear from my own sponsors (some of which are also here 👋). I'm considering migrating various public & still private thi.ng repos to @Codeberg (and plan to join as a club member), but would keep GH as passive mirror for now (updated only during new releases). Issue tracking would move to CB...

Would you support such a move? What are your own concerns? Instead of GH Sponsors, I've also started accepting donations via liberapay.com/thi.ng/ and the old patreon.com/thing_umbrella also still exists (though their greedy 8% fee makes it a non-preferred option)

patreon.com

Get more from Karsten Schmidt on Patreon

creating Open source software

@bkuhn@copyleft.org · Reply to Michael Downey 🚩

3 yrs ago, @downey wrote:
> “💡 Today is a perfect day to exercise your independence from , & .
> ☣️ is the equivalent of & for software development -- creators of the most enticing proprietary walled garden ever made for …
> Don't be stuck when …change[s] the rules on you.“
> GiveUpGitHub.org
…now ∃ more reasons to stop procrastinating & GiveUpGitHub *now*…
social.kernel.org/objects/bd3d
mastodon.social/@glyph/1149959

Try @Codeberg today!

GitHub so-called “Octocat” logo/mascot holds in one tentacle holds 💰. Six other tentacles form a cage for the words “USER RIGHTS” — which are set in blue stone but are crumbling under the force of the tentacles. The final tentacle reaches out with an open palm — presuambly to collect even more rights & money from its users.
ALT text

GitHub so-called “Octocat” logo/mascot holds in one tentacle holds 💰. Six other tentacles form a cage for the words “USER RIGHTS” — which are set in blue stone but are crumbling under the force of the tentacles. The final tentacle reaches out with an open palm — presuambly to collect even more rights & money from its users.

@tealeg@mastodon.online

/ folks. If any of you is still using my `github.com/tealeg/xlsx` library (>6k stars suggest some of you are), please note that it has now been migrated to `codeberg.org/tealeg/xlsx` and bumped to v4 (to reflect the incompatibility of this path change).

The old repo is now archived. It will still work in your code, but no further attention or work will happen there. Please create your issues and PRs at instead.

codeberg.org/tealeg/xlsx

codeberg.org

xlsx

Go library for reading and writing XLSX files.

@sakurasubnet@bumscode.com

So search engines become worse and after the github announcement, oss projects will scatter around to other git hosting providers. Is there a oss project database, where I can lookup if there is already something for my needs? That would be really helpful. If not, this would be a nice project - A human curated, searchable and tagged list of projects.

Boost for reach <3

@hugovk@mastodon.social

Odd note added to the cache repo:
github.com/actions/cache#note

"Thank you for your interest in this GitHub repo, however, right now we are not taking contributions.

"We continue to focus our resources on strategic areas that help our customers be successful while making developers' lives easier. While GitHub Actions remains a key part of this vision, we are allocating resources towards other areas of Actions and are not taking contributions to this repository at this time."

github.com

GitHub - actions/cache: Cache dependencies and build outputs in GitHub Actions

Cache dependencies and build outputs in GitHub Actions - actions/cache

@hugovk@mastodon.social · Reply to Hugo van Kemenade
@Codeberg@social.anoxinon.de

We, the operators of this social media account, sometimes face dilemmas about what we want to post. For example: "Are you a Hubber and want to become a Berger? We're looking forward to you!"

Love it or hate it, one thing is certain: It doesn't really matter, because others are doing our marketing today. 🙃

@alainmi11@mamot.fr

n’est plus indépendant de

« GitHub ne sera désormais plus indépendant, mais bien pleinement intégré à la division CoreAI de Microsoft. »

« Désormais, GitHub sera plus directement contrôlé par la direction de Microsoft et ses objectifs seront alignés avec ceux de la firme, notamment en matière d’IA. »

frandroid.com/marques/microsof

usine-digitale.fr/article/gith

@heiseonlineenglish@social.heise.de
@Codeberg@social.anoxinon.de

We, the operators of this social media account, sometimes face dilemmas about what we want to post. For example: "Are you a Hubber and want to become a Berger? We're looking forward to you!"

Love it or hate it, one thing is certain: It doesn't really matter, because others are doing our marketing today. 🙃

@julian@fietkau.social

Been watching the posts scroll by all day, and it only occurs to me now to re-up this 2022 blog post about how I started self-hosting my repositories as part of my website using GitWeb: fietkau.blog/2022/moving_from_

It's a pretty eccentric solution that's definitely less convenient than hopping to Codeberg (which would be my recommendation if your projects need modern collaboration tools), but maybe it'll speak to some of you. 😇

fietkau.blog

Moving from GitHub to Self-hosted Git Repositories: My Journey

This blog entry describes how I designed and implemented a way to self-host Git repositories as part of my personal website.

@Codeberg@social.anoxinon.de

We, the operators of this social media account, sometimes face dilemmas about what we want to post. For example: "Are you a Hubber and want to become a Berger? We're looking forward to you!"

Love it or hate it, one thing is certain: It doesn't really matter, because others are doing our marketing today. 🙃

@frumble@chaos.social

Was ich trotz allem jetzt uncool finde, ist wenn Projekte ihre -Accounts direkt löschen. Hinterlasst doch wenigstens eine Botschaft, wo ihr hinmigriert! Außerdem hab ich diverse interessante Projekte dort gefavt und jetzt Sorge, sie ganz aus den Augen zu verlieren, WEIL SIE EINFACH VERSCHWINDEN!!

@teleclimber@social.tchncs.de

If you were to design an online place where people collaborate on open source projects, what would it look like?

There are many clones of Github, but it's deeply flawed model. Issues are unmanageable. Pull requests are a pain.

What's the paradigm for collaborating on code that scales to medium-sized projects?

I want to hear your wildest ideas for managing issues and contributions at all levels.

@hertg@infosec.exchange

Apparently GitHub will become part of Microsoft's "AI Team" [1]. Even reading the CEO's post about their departure reads like a fever dream. [2]

«I am more convinced than ever that the world will soon see one billion developers enabled by billions of AI agents»

I am not sure if it is even possible to have more mentions of "AI" in a single post. Those sillicon valley people are really out of their minds.

Thankfully, there's @forgejo and @Codeberg

[1]: arstechnica.com/gadgets/2025/0
[2]: github.blog/news-insights/comp

github.blog

Auf Wiedersehen, GitHub ♥️

I am stepping down as GitHub CEO to build my next adventure. GitHub is thriving and has a bright future ahead.

@gytisrepecka@social.gyt.is
@pinjontall@sfba.social

🇩🇪:
Angesichts der Tatsache, dass Microsoft heute in sein KI-Entwicklungsteam integriert hat, würde ich empfehlen, jetzt sofort alles rauszuhauen.
🇬🇧:
In light of Microsoft folding into their AI development team today, I'd recommend getting your shit out now all at once

rahuljuliato.com/posts/github_ (also it's easy to get your stock .github actions to run on a cheap vps running a single docker-compose'd container)

rahuljuliato.com

Github to Codeberg Bulk Migration Script | Rahul's Blog

Rahul's Blog

@maswaba@mastodontech.de

Gibt es da draußen eigentlich eine echte europäische -Alternative? Ich kenne @Codeberg, aber ich will für meinen privaten Kram auch private Repos nutzen. Ja ich könnte selber was hosten, aber ich will mich schlicht nicht um Installation, Updates, Sicherheit, Backups etc selber kümmern müssen. Es muss nicht kostenlos sein, Github werf ich auch Geld in den Rachen. Will ich aber nicht mehr.

@bkuhn@copyleft.org · Reply to Michael Downey 🚩

3 yrs ago, @downey wrote:
> “💡 Today is a perfect day to exercise your independence from , & .
> ☣️ is the equivalent of & for software development -- creators of the most enticing proprietary walled garden ever made for …
> Don't be stuck when …change[s] the rules on you.“
> GiveUpGitHub.org
…now ∃ more reasons to stop procrastinating & GiveUpGitHub *now*…
social.kernel.org/objects/bd3d
mastodon.social/@glyph/1149959

Try @Codeberg today!

GitHub so-called “Octocat” logo/mascot holds in one tentacle holds 💰. Six other tentacles form a cage for the words “USER RIGHTS” — which are set in blue stone but are crumbling under the force of the tentacles. The final tentacle reaches out with an open palm — presuambly to collect even more rights & money from its users.
ALT text

GitHub so-called “Octocat” logo/mascot holds in one tentacle holds 💰. Six other tentacles form a cage for the words “USER RIGHTS” — which are set in blue stone but are crumbling under the force of the tentacles. The final tentacle reaches out with an open palm — presuambly to collect even more rights & money from its users.

@pinjontall@sfba.social

🇩🇪:
Angesichts der Tatsache, dass Microsoft heute in sein KI-Entwicklungsteam integriert hat, würde ich empfehlen, jetzt sofort alles rauszuhauen.
🇬🇧:
In light of Microsoft folding into their AI development team today, I'd recommend getting your shit out now all at once

rahuljuliato.com/posts/github_ (also it's easy to get your stock .github actions to run on a cheap vps running a single docker-compose'd container)

rahuljuliato.com

Github to Codeberg Bulk Migration Script | Rahul's Blog

Rahul's Blog

@gytisrepecka@social.gyt.is
@mjg@mastodon.phoenixtrap.com
@hugovk@mastodon.social · Reply to Hugo van Kemenade
@dentangle@chaos.social

People justify continuing to use in all sorts of ways.

"OK, they're owned by Microsoft who has spent decades trying to crush FOSS, but..."

"Yes, they steal code to feed their planet-destroying LLMs, but..."

"Sure, they help ICE enforce fascist policy, but..."

"Yes, they're supporting genocide, but..."

There's no "but" clause that justifies supporting all of that.

Values require sacrifices. This is the price we pay for the world we want.

Don't collaborate.

@quincy@chaos.social

Quit . Just do it.

They are too big, which is a problem in and of itself and not an advantage, because it gives them leverage:

The difficulty of quitting should be all the *more* reason to do it.

They steal from your project to make "AI" mush which is used to drive down wages and enshittify jobs - and just isn't fair use of everyone's contributions, as it's commercial ...

They bully their employees into being used by "AI".

They are part of , which is a known bad actor.

@release_bot@mstdn.b-shock.org
@hugovk@mastodon.social

Odd note added to the cache repo:
github.com/actions/cache#note

"Thank you for your interest in this GitHub repo, however, right now we are not taking contributions.

"We continue to focus our resources on strategic areas that help our customers be successful while making developers' lives easier. While GitHub Actions remains a key part of this vision, we are allocating resources towards other areas of Actions and are not taking contributions to this repository at this time."

github.com

GitHub - actions/cache: Cache dependencies and build outputs in GitHub Actions

Cache dependencies and build outputs in GitHub Actions - actions/cache

@release_bot@mstdn.b-shock.org
@QuadRadical@wetdry.world
@aral@mastodon.ar.al
@pat_dev@social.linux.pizza

Fellow coders, friends, enthusiasts:

Are you in search of a alternative? Do you like ?

Then say hello to CodeFloe 👋️

👉️ codefloe.com
👉️ Docs: docs.codefloe.com

Read more about the motivation to create here: pat-s.me/codefloe-launch/

pat-s.me

Launching CodeFloe

I am happy to announce the launch of CodeFloe, a public Git forge designed to combine the best of modern infrastructure with a transparent deployment …

@aral@mastodon.ar.al
@zahntron@mastodon.social

Hey advocates and lovers of and projects. What are you using to share your work? It seems is getting controversial with Are people somewhat content with the fact that open source projects are being used for training data and just keep using github because it's useful and that's where people are or are folks looking at self-hosting or other options? @jorge curious about UBlue's position. Thanks!

@angedestenebres@mastodon.tedomum.net · Reply to Vinceff
@danzin@mastodon.social

Na , assistindo um maravilhoso tutorial da Camila Maia @cmaiacd.

Ela está debulhando o Git e o GitHub em profundidade, muito conhecimento valioso sendo passado.

Foto de mulher branca de óculos e cabelos longos vestindo camiseta preta com uma das mão sobre um notebook numa mesa e a outra mão junto ao corpo. Apresenta um tutorial.
ALT text

Foto de mulher branca de óculos e cabelos longos vestindo camiseta preta com uma das mão sobre um notebook numa mesa e a outra mão junto ao corpo. Apresenta um tutorial.

@aral@mastodon.ar.al

Since Microsoft is organising a European Sovereign Tech Fund, we should ask Lockheed Martin to put together a European Sovereign Defense Fund. There’s probably also opportunity here to bring Amazon in to advise on EU labour standards and have McDonald’s take the lead on food safety policy in the EU.

CC @EUCommission

@toxi@mastodon.thi.ng

Anyone else getting these ridiculous repo scraping spikes? A clean checkout of the thi.ng/umbrella monorepo is ~370MB. Over the past 14 days there were 222k clones (only 117 unique) of this repo which have caused downloads of a whopping ~78TB. WTF! 🤯

Screenshot of a Github activity line plot showing the number of daily clones per day over the past 14 days. In the past week the number of daily clones went up to 60k+ for 2 days, with the total number of clones for the entire timespan 222,356 with only 117 unique cloners.
ALT text

Screenshot of a Github activity line plot showing the number of daily clones per day over the past 14 days. In the past week the number of daily clones went up to 60k+ for 2 days, with the total number of clones for the entire timespan 222,356 with only 117 unique cloners.

@pat_dev@social.linux.pizza

Fellow coders, friends, enthusiasts:

Are you in search of a alternative? Do you like ?

Then say hello to CodeFloe 👋️

👉️ codefloe.com
👉️ Docs: docs.codefloe.com

Read more about the motivation to create here: pat-s.me/codefloe-launch/

pat-s.me

Launching CodeFloe

I am happy to announce the launch of CodeFloe, a public Git forge designed to combine the best of modern infrastructure with a transparent deployment …

@aral@mastodon.ar.al

The only way Microsoft should be involved in a European Sovereign Tech Fund is if we fund it by taxing the living shit out of them.

But having them organise and influence it (and who gets funded by it), thereby de facto giving Microsoft EU taxpayer subsidies? Get the fuck out of here.

There are no words to describe how angry this attempt at corporate capture gets me when we’ve been working on sovereign tech in the EU for the past seven years with zero EU funding (not for lack of trying).

Note which people and organisations allow their names to be used to legitimise this effort so you don’t trust a thing they say on this subject in the future.

github.blog/open-source/mainta

github.blog

We need a European Sovereign Tech Fund

With a new feasibility study, GitHub’s developer policy team is building a coalition of policymakers and industry to close the maintenance funding gap.

@aral@mastodon.ar.al

Since Microsoft is organising a European Sovereign Tech Fund, we should ask Lockheed Martin to put together a European Sovereign Defense Fund. There’s probably also opportunity here to bring Amazon in to advise on EU labour standards and have McDonald’s take the lead on food safety policy in the EU.

CC @EUCommission

@aral@mastodon.ar.al

The only way Microsoft should be involved in a European Sovereign Tech Fund is if we fund it by taxing the living shit out of them.

But having them organise and influence it (and who gets funded by it), thereby de facto giving Microsoft EU taxpayer subsidies? Get the fuck out of here.

There are no words to describe how angry this attempt at corporate capture gets me when we’ve been working on sovereign tech in the EU for the past seven years with zero EU funding (not for lack of trying).

Note which people and organisations allow their names to be used to legitimise this effort so you don’t trust a thing they say on this subject in the future.

github.blog/open-source/mainta

github.blog

We need a European Sovereign Tech Fund

With a new feasibility study, GitHub’s developer policy team is building a coalition of policymakers and industry to close the maintenance funding gap.

@aral@mastodon.ar.al

Since Microsoft is organising a European Sovereign Tech Fund, we should ask Lockheed Martin to put together a European Sovereign Defense Fund. There’s probably also opportunity here to bring Amazon in to advise on EU labour standards and have McDonald’s take the lead on food safety policy in the EU.

CC @EUCommission

@fedizen@mastodon.social
@strypey@mastodon.nzoss.nz · Reply to Moved to @bonfire@bonfire.cafe

@bonfire
> We're tracking mockups and implementation progress here

FYI I'd love to help. But from Jan 1 2025 onwards, I refuse to do anything that requires logging in to GritHub. For the same reason I refuse to maintain an account on FarceBook.

Even reading GH pages on mobile is starting to require allowing this BorgSoft-controlled platform to run JS in my browser.

@evanprodromou @Jeremiah @herebox

@release_bot@mstdn.b-shock.org
@BananaGiko_cle@felesitas.cloud
@kkarhan@infosec.space · Reply to Kevin Karhan :verified:

And yes, whoever uses for and instead of a goddam [doesn't have to be @github / or @gitlab / or @Codeberg / or even @gitea / - just use any git and write down your documentation in a useable format like or goddamn ASCII plain text FFS] should be banned for life from , working in or contribute to .

  • Because it's literally worse than people shitting "" all over the place cuz that can be fixed faster and easier by backrolling said commits and banning the offender!

youtube.com/watch?v=9ehLMlVTRJ

youtube.com

44 Reasons Why I Hate Tech

Score great deals with NexiGo at https://www.nexigo.com/pages/prime-day-2025I hate computers. I hate Nintendo Switch 2. I am angry about AMD, I'm angry and a...

@release_bot@mstdn.b-shock.org
@pooza@mstdn.b-shock.org · Reply to 鴉河雛
@igrep@precure.ml · Reply to YAMAMOTO Yuji

微修正してtypesafe-precure v0.12.0.1 をリリースしました。
「キミとアイドルプリキュア♪」の現時点での設定の他、「わんだふるぷりきゅあ!」で追加し漏らしていた設定を追加しました。
hackage.haskell.org/package/ty

詳しい修正内容は github.com/igrep/typesafe-prec をご覧ください。

github.com

Add transformations and purifications from "You and Idol PreCure", and missing purifications from Wonderful PreCure. by igrep · Pull Request #67 · igrep/typesafe-precure

@stefanlange@social.tchncs.de

Bei GitHub wird ein Maskottchen für das -Framework gesucht. In den Kommentaren hatte jemand diesen - vermutlich nicht ganz ernst gemeinten - Vorschlag. 😂

github.com/angular/angular/dis

Ein Bild von Angela Merkel, die mit ihren Händen eine Raute formt. In der Raute wurde das Angular-Logo (ein A in einem Sechseck) retuschiert. Unter dem Bild steht „Angular Merkel“.
ALT text

Ein Bild von Angela Merkel, die mit ihren Händen eine Raute formt. In der Raute wurde das Angular-Logo (ein A in einem Sechseck) retuschiert. Unter dem Bild steht „Angular Merkel“.

@caten@mathstodon.xyz

Update on my interest in moving away from to another code forge. I was excited about because it is meant to be , but I ended up deciding against it. Besides the use of cryptocurrency for fundraising/management being a red flag, I found that I needed a seed node with a dedicated address in order to host a private repo, which doesn't feel truly P2P.

I also want to be able to convince other people to use the code forge with me to write code and papers. The added complexity of Radicle (from a user's perspective) seems like even more of an uphill battle than getting mathematicians to choose git instead of . (By the way, we could use a Overleaf alternative.)

Due to these considerations, it looks like self-hosting @forgejo is the way to go! (Even if it's not P2P.)

Anyway, I have gotten set up with a European VPS thanks to european-alternatives.eu/ and have a Debian machine running. I now need to get Forgejo set up, and I have three install methods I might use:

1) Follow forgejo.org/docs/latest/admin/
2) Follow codeberg.org/forgejo-contrib/f which says that (1) is bad
3) Use podman

From (2) I could start Forgejo and from (3) I could start a container, but the instructions on forgejo.org/docs/latest/admin/ don't work for me. In all cases I need to use the web UI to finish installation. Am I supposed to have no CLI alternative for this? I feel like installing a desktop environment on my VPS is not the answer, but I'm not sure what else to do here.

forgejo.org

Installation with Docker | Forgejo – Beyond coding. We forge.

@pooza@mstdn.b-shock.org
@me@social.sandervankasteel.nl

In a private organization, in a private repo filled with NDA code, Github decided that to automatically start reviewing that code using Copilot.

Mind you, Copilot is disabled for this organization.

Could we please just fucking not ?! Not even mentioning the fact that the Github organization didn't enabled this, there is no data policy to be found in sight. I have no clue what Copilot does with the data after it "reviewed" the code and I could potentially be breaking the signed NDA.

A comment on a Pull Request made by Github Copilot
ALT text

A comment on a Pull Request made by Github Copilot

A screenshot of a Github organization which clearly states that Copilot is disabled.
ALT text

A screenshot of a Github organization which clearly states that Copilot is disabled.

@release_bot@mstdn.b-shock.org
@dentangle@chaos.social

Hello people 🦀

Am I correct in my understanding that to use or manage rust crates I would need a login?

Looking at crates.io and this github issue[1] from 2016 it seems that using Microsoft's GitHub is the only way to login or publish. Is that still the case?

I'm rather reluctant to go back to using GitHub having given up GitHub[2] some years ago.

[1] github.com/rust-lang/crates.io

[2] sfconservancy.org/GiveUpGitHub

sfconservancy.org

Give Up GitHub - Software Freedom Conservancy

The Software Freedom Conservancy provides a non-profit home and services to Free, Libre and Open Source Software (FLOSS) projects.

@release_bot@mstdn.b-shock.org
@angedestenebres@mastodon.tedomum.net
@vale@fedi.vale.rocks

Apparently this was the beginning. A decent portion of my time on GitHub is now addressing meaningless AI comments.

Come on. This is open-source work made free for the benefit of humanity. This AI slop just wastes the time and money of the perpetrators and maintainers alike.

#GitHub #OpenSource

RE: https://fedi.vale.rocks/objects/e491e14d-de8f-4e43-92e7-a3c7e589a90f

fedi.vale.rocks

Vale (@vale@fedi.vale.rocks)

I… uh…Somebody opened an issue on GitHub where they just sent through a conversation with Grok regarding what action we should take to make improvements…

@vale@fedi.vale.rocks

I… uh…

Somebody opened an issue on GitHub where they just sent through a conversation with Grok regarding what action we should take to make improvements…

@cassidy@blaede.family

GitHub teams would be like 1000× more powerful if you could reference them across orgs. Like, it’d be nice to be able to say, “I trust org-foo/app-team to have write access to this repo,” but you can only add teams that are part of the org that owns the repo.

I get it from a trust/control perspective, but there have been a few times where it would *really* come in handy rather than having to manually maintain a duplicate team on another org. :(

@larsmb@mastodon.online

Dear , when I click on a link to an English language documentation page, I don't want to be automatically redirected to a machine generated German translation.

Yes, I have both enabled in my browser. Multi-lingual people are a thing. If I want a translation, I'll explicitly ask for it.

Every site whose product owner/manager insists on automatic translation should immediately fire them.

@fedora@fosstodon.org

GitHub Actions can come in handy for lots of things, and Python development is one of them! You can set up a CI pipeline to test against different versions of Python and make your app more reliable.

This guide is good for Fedora, CentOS, and RHEL. 👌

➡️ fedoramagazine.org/python-ci-o

fedoramagazine.org

Python CI on Fedora with GitHub Actions - Fedora Magazine

In this article, you will learn how to set up GitHub Actions to manage continuous integration for your Python projects.

@pooza@misskey.delmulin.com · Reply to ぷーざ@ダイスキー

すぐに適用しようと思ったのだけど、本家さまが意外とばたばたしてますね。
2025.6.2を経て、2025.6.3もすぐに出そうな雰囲気です。
1日待ったほうがいいかも。

Release 2025.6.2 · misskey-dev/misskey

Client Fix: キャッシュを削除しないとクライアントが使用できないことがある問題を修正 翻訳の更新

@pooza@misskey.delmulin.com · Reply to ぷーざ@ダイスキー

すぐに適用しようと思ったのだけど、本家さまが意外とばたばたしてますね。
2025.6.2を経て、2025.6.3もすぐに出そうな雰囲気です。
1日待ったほうがいいかも。

Release 2025.6.2 · misskey-dev/misskey

Client Fix: キャッシュを削除しないとクライアントが使用できないことがある問題を修正 翻訳の更新

@hosford42@techhub.social

Got spam emails this morning by someone who opened an issue on GitHub with what was probably a very unsafe link and then just tagged dozens of users over and over and over. Why we needed 50 copies in a row of the same notification, IDK. Thankfully, the account is terminated already, but if this starts to be a regular thing, I might have to abandon GitHub altogether.


@pooza@misskey.delmulin.com
@smallcircles@social.coop

We live in a and are being force-fed . See how it destroys the fabric of our .

curated lists are inspired by lists on and I realized they still represent a sterile lab with glaring TL lights and metal glinting everywhere.

In a quest to bring more of the missing connecting layers to bridge the gap between tech vs. and , I decided to give things a friendlier makeover.

delightful.coding.social

Snapshot taken from the revitalised delightful-fediverse-apps list that is being prepared. The text reads as follows ..

--

## Commons gardening

🍀 This curated list is carefully gardened by volunteers working in spare time. We are working in commons and so can you. Help make this list better, and become a Gardener of the fediverse.

If you have questions or feedback regarding this list, then please create an Issue in our tracker, and optionally @mention one or more of our maintainers:

    @circlebuilder
    @lostinlight
    @wakest
    @wisdomchicken

### Contributors

We are proud to introduce you to some of our delightful gardeners. Thank you for your kind contributions. Gardening, and not on this list? Please add yourself if you are missing.

## License

CC0 Public domain. This work is free of known copyright restrictions.   This delightful commons curated list is evolving under Social coding commons.
ALT text

Snapshot taken from the revitalised delightful-fediverse-apps list that is being prepared. The text reads as follows .. -- ## Commons gardening 🍀 This curated list is carefully gardened by volunteers working in spare time. We are working in commons and so can you. Help make this list better, and become a Gardener of the fediverse. If you have questions or feedback regarding this list, then please create an Issue in our tracker, and optionally @mention one or more of our maintainers: @circlebuilder @lostinlight @wakest @wisdomchicken ### Contributors We are proud to introduce you to some of our delightful gardeners. Thank you for your kind contributions. Gardening, and not on this list? Please add yourself if you are missing. ## License CC0 Public domain. This work is free of known copyright restrictions. This delightful commons curated list is evolving under Social coding commons.

@FinchHaven@sfba.social · Reply to Andy Piper

@andypiper

If I may, let me ask this question again, over here:

"- "experimental support for verifying and displaying remote quote posts""

I've watched as this very specific Issue worked its way through the

"remote quote posts"

I've seen no mention (perhaps I missed it) of who exactly gets to --> create <-- these "remote quote posts"

"remote" implies no one on my local instance

cc @individual8 @MastodonEngineering

@caten@mathstodon.xyz

I'm finally moving over to Radicle (radicle.xyz) instead of switching to another centralized code forge (like GitHub, GitLab, Codeberg, etc.). I definitely love the idea behind a code forge and I'm hopeful for Radicle's future, but I do have some reservations starting off:

1) Despite talking a lot about freedom and privacy in the tutorial, the group building Radicle (radworks.org/) is planning to sell hosting and make a profit via an Ethereum-based cryptocurrency (tally.xyz/gov/radworks) as well as NFTs and smart contracts. Some big Libertarian red flags there.

2) At some point there was a Swiss nonprofit "Radicle Foundation", but this now seems to be a for-profit venture (see radicle.xyz/history). I wish it could just be a nonprofit.

3) In the user guide chapter on private repos (radicle.xyz/guides/user), it says that I need to use a public DNS address trusted seed node to share the repo. I understand there's no DHT here, but I hope it's not too much of a pain to run this over my local network instead of the internet. (And yeah, I know I can use git locally, I just want to test Radicle locally.)

Overall, I think that if radworks turns out to be evil it will be a way easier transition to fork Radicle than it has been to leave GitHub, but I still wish I didn't have to worry.

radicle.xyz

Radicle

Sovereign code infrastructure.

We're planning to reorganize our labels to better reflect 's project structure! 🏷️

Currently using GitHub's default labels, but we want something more tailored to our needs—like component-specific labels (vocab, federation, actor, etc.), runtime tags (Deno/Node/Bun), and compatibility tracking.

The proposal includes hierarchical labeling with categories like:

  • type/ for bug, feature, documentation
  • component/ for different parts of Fedify
  • activitypub/ for interop issues with Mastodon, Misskey, etc.

We'd love your thoughts! What labels would be most helpful for contributors and maintainers?

Check out the full proposal: https://github.com/fedify-dev/fedify/issues/238.

github.com

Reorganize repository labels to better fit Fedify project structure · Issue #238 · fedify-dev/fedify

Problem Currently, the Fedify repository uses GitHub's default labels, which don't reflect the specific needs and structure of the Fedify project. These generic labels make it difficult to: Categor...

@tomgag@infosec.exchange

In a move that surprises absolutely noone, GitHub now requires users to login in order to browse public repositories (including open source projects). After a few (~10) requests, you get blocked (I can confirm). In order to fight AI scrapers, I guess.

So, GitHub decided to blanket-limit access to open source projects as a defense against the very scourge that they(r parent company) unleashed on the world.

I won't be hypocrite: it's a bit embarrassing, but undeniably satisfying to say "told you so". I moved away from GitHub long ago and I moved all my stuff to Codeberg instead. And so happy I did!

Next step: radicle.xyz maybe?

github.com/orgs/community/disc

A screenshot of GitHub's blocking page due to reaching rate limit very quickly while browsing an open source project's repository while not logged in.
ALT text

A screenshot of GitHub's blocking page due to reaching rate limit very quickly while browsing an open source project's repository while not logged in.

@CuratedHackerNews@mastodon.social
@Codeberg@social.anoxinon.de · Reply to Codeberg

We couldn't believe it at first, but one of the most common numbers guessed about the adoption among logged-in users is 42%. We assume that many users took this number as a joke. But in all seriousness: it is correct! (It is exactly 42.0095476% higher than that of our largest competitor 😄)

We boosted the first post with that guess, but feel free to browse all the other awesome project recommendations made in this thread, too!

(Context on the number 42: en.wikipedia.org/wiki/Phrases_ )

en.wikipedia.org

Phrases from The Hitchhiker's Guide to the Galaxy - Wikipedia

@jbz@indieweb.social

「 Perhaps the younger generation don't know anything about the past "evils" of Microsoft and naively believe that Microsoft is now the good friend to open source, but the truth is that all Microsoft acquisitions of open source projects is a business tactic that is put in place to improve Microsoft's loosing position to open source. It is a matter of control. And you should not host your open source project on GitHub 」

unixdigest.com/articles/why-is

unixdigest.com

Why is your open source project still hosted on GitHub?

Perhaps the younger generation don't know anything about the past "evils" of Microsoft and naively believe that Microsoft is now the good friend to open source, but the truth is that all Microsoft acquisitions of open source projects is a business tactic that is put in place to improve Microsoft's loosing position to open source. It is a matter of control. And you should not host your open source project on GitHub.

@vwbusguy@mastodon.online

If you're annoyed with , you'll probably be pleasantly surprised at how easy it is to deploy and migrate/mirror your repos. If you don't want to host it yourself, there's also @Codeberg. It is slightly more effort than complaining about Github, but not much more.

@release_bot@mstdn.b-shock.org
@ploum@mamot.fr
@ploum@mamot.fr
@larsmb@mastodon.online
@quincy@chaos.social

Somehow I can't even laugh about the M$ debacle.

It's just sad. I'm thinking of the accruing environmental, human and social costs of the machines that are dumping slop onto everyone's lives.

Also, a company that has the power to decide at a whim that billions will suddenly have to worry about private conversations being screenshotted to be mined for more slop, and to strong-arm whole countries to run their rotten and snooping systems, simply has no right to exist.

@larsmb@mastodon.online
@nullagent@partyon.xyz

Oh joy github is tightly integrating more LLM features that encourage people browsing projects to do drive by vibe coding.

The new features have no optout and are not optin. GitHub is encouraging users to submit bug reports fully written by AI and to fix bug reports using fully AI written PRs.

A lot of maintainers of open source projects big and small really do not want this turned on by default.

@bagder@mastodon.social
@zkat@toot.cat

In light of GitHub going full genAI agents, which will likely lead to a flood of garbage PRs that will make dependabot nags a joke:

Would other foss maintainers with projects on GitHub be interested in some kind of event where we all get together and try moving our projects over to @Codeberg?

I’m thinking of it as a way to both promote our foss projects, provide mutual support during the moves, find solutions to small cuts we run into along the way, and just generally have fun together?

Boosts and ideas welcome!

If anyone is interested in talking more about this or participating, even if you’re not a core maintainer for a project, I’ve created Discord and Matrix places we can start chatting in: discord.gg/fcSeuv56qp and matrix.to/#/%23nohub:matrix.org

matrix.to

You're invited to talk on Matrix

You're invited to talk on Matrix

@algernon@come-from.mad-scientist.club

Starting August 20, 2025, I will not be contributing to projects hosted on #GitHub via GitHub itself, unless I am paid handsomely for my troubles.

If I need to report an issue, or send a patch, I will either keep the report / patch to myself, publish it on my forge, or if I really, really want to contribute, I will send an e-mail. But opening an issue, or sending a PR on GitHub itself? Not going to happen, unless I'm paid for it.

#GiveUpGitHub

@bagder@mastodon.social
@zkat@toot.cat

In light of GitHub going full genAI agents, which will likely lead to a flood of garbage PRs that will make dependabot nags a joke:

Would other foss maintainers with projects on GitHub be interested in some kind of event where we all get together and try moving our projects over to @Codeberg?

I’m thinking of it as a way to both promote our foss projects, provide mutual support during the moves, find solutions to small cuts we run into along the way, and just generally have fun together?

Boosts and ideas welcome!

If anyone is interested in talking more about this or participating, even if you’re not a core maintainer for a project, I’ve created Discord and Matrix places we can start chatting in: discord.gg/fcSeuv56qp and matrix.to/#/%23nohub:matrix.org

matrix.to

You're invited to talk on Matrix

You're invited to talk on Matrix

@bagder@mastodon.social

I critique what I consider are bad choices and decisions. At the same time, GitHub is a top sponsor of the project. They are among the few companies that make keep going.

We cannot easily afford to switch to something else without someone with a thick wallet helping us do it.

@bagder@mastodon.social
@zkat@toot.cat

In light of GitHub going full genAI agents, which will likely lead to a flood of garbage PRs that will make dependabot nags a joke:

Would other foss maintainers with projects on GitHub be interested in some kind of event where we all get together and try moving our projects over to @Codeberg?

I’m thinking of it as a way to both promote our foss projects, provide mutual support during the moves, find solutions to small cuts we run into along the way, and just generally have fun together?

Boosts and ideas welcome!

If anyone is interested in talking more about this or participating, even if you’re not a core maintainer for a project, I’ve created Discord and Matrix places we can start chatting in: discord.gg/fcSeuv56qp and matrix.to/#/%23nohub:matrix.org

matrix.to

You're invited to talk on Matrix

You're invited to talk on Matrix

@pooza@mstdn.b-shock.org

github.com/vbaidiot/ariawase

そういえばこれVBSだったような。これが動かないととてもこまる現場がある。

.xlsm や .accdb などから、VBAのスクリプトを抽出するやつ。隠しオプション?を使うと、 .accdbからクエリーを抽出したりもできる。
VBAをgitで管理するには欠かせないパーツ。

お恥ずかしながら原理とかがよくわかってないけど、これ他言語で実装することは可能なもの?
Rubyのwin32oleでもいける?

github.com

GitHub - vbaidiot/ariawase: Ariawase is free library for VBA cowboys.

Ariawase is free library for VBA cowboys. Contribute to vbaidiot/ariawase development by creating an account on GitHub.

@inventaire@mamot.fr

Code migration to @Codeberg ✅ 🎉

codeberg.org/inventaire/

Bye bye Microsoft/Github, we are excited to finally have our code forge also running on libre/free software, and hosted by a fellow non-profit! Thanks @forgejo and @Codeberg for the amazing work!

codeberg.org

inventaire

Codeberg is a non-profit, community-led organization that aims to help free and open source projects prosper by giving them a safe and friendly home.

@davidism@mas.to

Is GitHub's "new milestone" button broken for everyone or just me? Clicking it goes to the issue list filtered on "milestone:new" rather than the new milestone form.

@tomgag@infosec.exchange

In a move that surprises absolutely noone, GitHub now requires users to login in order to browse public repositories (including open source projects). After a few (~10) requests, you get blocked (I can confirm). In order to fight AI scrapers, I guess.

So, GitHub decided to blanket-limit access to open source projects as a defense against the very scourge that they(r parent company) unleashed on the world.

I won't be hypocrite: it's a bit embarrassing, but undeniably satisfying to say "told you so". I moved away from GitHub long ago and I moved all my stuff to Codeberg instead. And so happy I did!

Next step: radicle.xyz maybe?

github.com/orgs/community/disc

A screenshot of GitHub's blocking page due to reaching rate limit very quickly while browsing an open source project's repository while not logged in.
ALT text

A screenshot of GitHub's blocking page due to reaching rate limit very quickly while browsing an open source project's repository while not logged in.

@ngate@mastodon.social
@applech2@rss-mstdn.studiofreesia.com
@paul@mitra.kemitix.net

git-next: 🔥 New release v2025.5.0 - Refactoring and isolating features

🧩 git-next: trunk-based development manager
🦀 Written in Rust
⭐ Repo: https://codeberg.org/kemitix/git-next

What's New

- Reimplement git operations to use git2/libgit2
- Renamed features:

forgejo -> forge-forgejo

github -> forge-github


- Extracted desktop and email notification support into non-defaults features;

notify-desktop

notify-email

This a significant update to migrate from gix to git2 for git operations. This allows us to drop the gix crate and the need to shelling-out to git for operations that gix doesn't support.

Breaking Change

If you are build from source (e.g. cargo install) and use either email or desktop notifications in your configuration file, you will need to add the appropriate feature, notify-desktop and/or notify-email. If you don't the config file will not be accepted.

The docker images are built with all features enabled.

Install

📦 cargo install git-next@2025.5.0
📦 cargo install git-next@2025.5.0 --features notify-desktop,notify-email
🐋 docker pull codeberg.org/kemitix/git-next:v2025.5.0

Run UI in docker

docker run --rm -p 8092:8092 \
  -u $(id -u):$(id -g) \
  -it \
  -v $PWD:/app \
  codeberg.org/kemitix/git-next:v2025.5.0 \
  server start --xui

#RustLang #Ratatui #Git #GitNext #OpenSource #Docker #GitHub #ForgeJo

@ngate@mastodon.social

🤖✨ Ah, finally! Because what hasn't dreamt of transforming their into standalone executable horrors?🔨👻 Now, brace yourself for terminal-induced as you navigate yet another maze that promises to "simplify" your life. 🌀🚀
github.com/rzane/docker2exe

github.com

GitHub - rzane/docker2exe: Convert a Docker image to an executable

Convert a Docker image to an executable. Contribute to rzane/docker2exe development by creating an account on GitHub.

@Htbaa@fosstodon.org

Anyone using @forgejo runners for have the same issue as me using github.com/shogo82148/actions- for running perl?

My workflows fail during setup of shogo82148/actions-setup-perl, see screenshot.

The URL it fails on saying bad credentials works fine without credentials. Is this a thing requiring something as the action is hosted there? I'm using the latest runner, cleared caches. Went back to previous version, same issue.

This used to work before...

Output of Forgejo Runner logging
ALT text

Output of Forgejo Runner logging

@rl_dane@polymaths.social
@bitsgalore@digipres.club

After almost 12 years I migrated my blog from Pages to @Codeberg.

I also added an -based comments system (which means you can now comment using your Mastodon account), and archived the legacy comments (which used Github issues).

This post gives some technical background info on how I did this, which might be useful for others who are thinking about moving their sites away from Github.

bitsgalore.org/2025/04/30/chan

bitsgalore.org

Changes to the blog: migration to Codeberg and ActivityPub-based comments

This post covers the migration of this blog from Github Pages to Codeberg pages. It also provides some technical background information on the new, ActivityPub-based comments system.

@jwildeboer@social.wildeboer.net
@janvhs@hachyderm.io

Imagine the company producing tons of carbon dioxide by training their LLM on restrictively licensed code and by pushing their AI assistant, now tells you – well shames you really – to care more about the environment… Fuck and by extension.

GitHub marketing email about the Earth Day and how you should care more
ALT text

GitHub marketing email about the Earth Day and how you should care more

@Dendrobatus_Azureus@bsd.cafe
The screencap showcases a VLC video player interface on an Android with a video titled "Two decades of Git: A conversation with creator Linus..." The video is currently at 4:40 out of a total duration of 41:49. The video features a man Linus Torvalds sitting in a chair, wearing a gray long-sleeve shirt with a small logo on the left side, and dark pants. He is seated in front of a large window with a view of greenery outside. There are two glasses of water on a small table to his left. The background includes a wooden wall and a large window, suggesting an indoor setting with natural light. The video player interface includes standard controls such as play, pause, and volume adjustment, along with a progress bar indicating the current playback position.

 Ovis2-8B

🌱 Energy used: 0.187 Wh
ALT text

The screencap showcases a VLC video player interface on an Android with a video titled "Two decades of Git: A conversation with creator Linus..." The video is currently at 4:40 out of a total duration of 41:49. The video features a man Linus Torvalds sitting in a chair, wearing a gray long-sleeve shirt with a small logo on the left side, and dark pants. He is seated in front of a large window with a view of greenery outside. There are two glasses of water on a small table to his left. The background includes a wooden wall and a large window, suggesting an indoor setting with natural light. The video player interface includes standard controls such as play, pause, and volume adjustment, along with a progress bar indicating the current playback position. Ovis2-8B 🌱 Energy used: 0.187 Wh

@lemeteore@mastodon.social
@alpharee@mastodon.social
terminal window: CHANGELOG.md (universe/main):

v0.0.0 – bootstrapped void (clean slate)  
v1.0.0 – initialized spacetime engine  
v1.1.0 – [hotfix] expanded ui 10⁶⁰x for visibility  
v1.2.0 – symmetry patch; deprecated antimatter  
v1.3.0 – enabled fusion; added dramatic lighting  
v2.0.0 – deployed life() [beta] — no unit tests  
v2.1.0 – initialized multicell_module (collaboration opt-in)
v2.6.6 – deployed homo_sapiens [experimental] — installed intelligence 
         (no sandbox, ethics tbd)  

🚫 2025.01.20 – intelligence deprecated  
   → replaced with: tariffs, vibes, and greatness  
   → rollback blocked by executive order
ALT text

terminal window: CHANGELOG.md (universe/main): v0.0.0 – bootstrapped void (clean slate) v1.0.0 – initialized spacetime engine v1.1.0 – [hotfix] expanded ui 10⁶⁰x for visibility v1.2.0 – symmetry patch; deprecated antimatter v1.3.0 – enabled fusion; added dramatic lighting v2.0.0 – deployed life() [beta] — no unit tests v2.1.0 – initialized multicell_module (collaboration opt-in) v2.6.6 – deployed homo_sapiens [experimental] — installed intelligence (no sandbox, ethics tbd) 🚫 2025.01.20 – intelligence deprecated → replaced with: tariffs, vibes, and greatness → rollback blocked by executive order

@orhun@fosstodon.org

Here is how I test my GitHub CI from the terminal! 💯

🌀 **wrkflw** — Validate and execute GitHub Actions workflows locally

🔥 Supports viewing logs, outputs, and execution details

🧵 Parallel runs, emulation mode & more!

🦀 Written in Rust & built with @ratatui_rs

⭐ GitHub: github.com/bahdotsh/wrkflw

@jwildeboer@social.wildeboer.net

Is preparing to lock out ?

This "configuration error" that lasted 18 hours hints at them being able to block access from China when needed. No big surprise, but all the more reason to at least mirror your repos elsewhere, just in case.

"Due to a configuration change with unintended impact, users that were not logged in who tried to visit GitHub.com from China were temporarily unable to access the site"

1/3

githubstatus.com/incidents/jfv

githubstatus.com

[Retroactive] Access from China temporarily blocked for users that were not logged in

GitHub's Status Page - [Retroactive] Access from China temporarily blocked for users that were not logged in.

@applech2@rss-mstdn.studiofreesia.com
@mraandtux@vivaldi.net

今天有用户反映 站方限制中国境内用户登录,本人担心日后github dot io或被站方限制,导致有线或IPTV用户无法从本项目查阅最新频道表,从而导致本项目被“频道精简”停运;鉴此本人将会在互联网寻找能透过各大运营商网络浏览的网页代码托管网站,若无法找到合适的托管网站,本项目将择日停运,TVChannelLists的英文版翻译也将同步停更。

@dwn@dwnfonts.cc

When you visit in , here's what you got.
Freedom means nothing when political correct comes.

GitHub's Forbidden page said access to this site has been restricted
ALT text

GitHub's Forbidden page said access to this site has been restricted

@micahilbery@slothsneed.coffee

I want a "Github Desktop" app but just for like all got stuff. I suck at got and remembering all the little weird commands any time I need to do something outside fetch, push, pull. I know there are a few different git GUIs out there but none of them have the simplicity of Github Desktop. I don't plan on doing anymore personal projects on github and moving to codeberg and a self-hosted Forgejo for private repos. but it stinks to lose my personal favorite workflow.
#Github #Codeberg #Git #Forgejo

@janikvonrotz@fosstodon.org

Over the coming months I will move all my personal and private repositories from and to . I run many static sites and intend to use ci.codeberg.org to trigger the builds.

Once this process is finished and everything works fine with . I will also migrate the repos of my company to codey.ch/. As there are some GitHub integrations I can't get rid of, I intend to mirror back the repos.

I'll keep you updated via .

codey.ch

Codey - The European Code Collaboration Platform

Codey provides you a secure, fast and reliable code collaboration platform, hosted in Europe, with 100% free software, based on Forgejo.

@janw@23.social

First successful CI pipeline running on my self-hosted Actions runner against a repo that I just migrated to @Codeberg. Almost a seamless transition,

The post- future is now! 🥳

Screenshot of a five successfully completed testing CI jobs for various Python versions, running in Codeberg/Forgejo Actions.
ALT text

Screenshot of a five successfully completed testing CI jobs for various Python versions, running in Codeberg/Forgejo Actions.

@andrewlock@hachyderm.io
@phranck@nerdculture.de

Ich weiss, es gibt viele und Alternativen. Einige kenne ich auch schon. Aber, welche in Deutschland(!) oder auch AT gehosteten Git Alternativen wuerdet ihr empfehlen? Muss nicht unbedingt kostenlos sein, sollte halt nur da gehostet werden.

Gerne boosten/teilen.
:boost_ok:

@adamchainz@fosstodon.org

tip:

Don’t post “Any updates?” style comments on open source threads. Any updates would be there already. Open source is a gift; bugging maintainers acts like you're entitled to results. I just mark such comments as spam.

If you want to see something done, do something to help: research specifications, find an existing implementation, write a test case, draft the docs, write a draft implementation, do some code review, test the PR locally, or just anything to help the project.

GitHub comment “Any updates on this?” being hidden as spam.
ALT text

GitHub comment “Any updates on this?” being hidden as spam.

@matt@oslo.town · Reply to wakest ⁂

@liaizon I feel like I *might* have mentioned this before, but the developer is making a suite of apps that copy their counter-parts.

play.google.com/store/apps/dev

They are free, claim to be privacy focused, the code is up on .
github.com/Goodwy

They have a Dialer, Contacts, Messages, Files and - the one you are looking for - a Gallery app: play.google.com/store/apps/det

play.google.com

Right Gallery - Apps on Google Play

Create a custom interface for your media library.

@pooza@mstdn.b-shock.org
@solnic@hachyderm.io

Check out this very first demo of my upcoming Repobot app!

✨ AI-powered Maintenance Automation for ✨

The app will be free for projects! Cannot wait to share it with y'all! Its early prototype was super helpful but now I'm taking it to the next level 🎊

youtu.be/s7C9OhbatZs

youtube.com

Repobot early demo

This is the very first demo of the upcoming Repobot app!✨ AI-powered maintenance automation for GitHub ✨Old idea. New app!It's an app that based on concepts ...

@solnic@hachyderm.io

Got the thing deployed 🙃

The app can do quite a lot already: organize repos into folders, import source files as templates from repos, compare file similarities, open PRs, push directly to main and even show diffs ✨

More news coming soon!

@AndiMann@masto.ai
@joschi@hachyderm.io
@release_bot@mstdn.b-shock.org
@qiita@rss-mstdn.studiofreesia.com
@release_bot@mstdn.b-shock.org
@sethmlarson@fosstodon.org
@pooza@mstdn.b-shock.org

mstdn.jpとpawoo.jpは最近は最新版に追従できている印象を漠然と持っていたが、実際は4.1系だったと知った。
4.1系のサポートは4月に終わるそう。もっとも、両鯖のMastodonは4.1系の最新版と比べてもだいぶ古いんだけど。

github.com/mastodon/mastodon/r

Release v4.1.23 · mastodon/mastodon

CautionThe 4.1.x branch will not receive any update—including security fixes—after 2025/04/08. WarningThis release includes important security fixes. Corresponding releases are available for the 4...

@SylvieLorxu@chaos.social

I just lost access to a substantial amount of issues on one of my projects.

I would appreciate if people could help upvote github.com/orgs/community/disc to get more attention.

GitHub staff won't even tell me how much data they've hidden from me, which is quite discouraging :(

A GitHub Support discussion. The discussion is too long to put in alt-text, but to summarize, "something" happened to an account of someone who reported issues to my project and GitHub has silently hidden all those issues. Support basically told me they would not help restore the data, that this is by design, and that I should open a feature request.
ALT text

A GitHub Support discussion. The discussion is too long to put in alt-text, but to summarize, "something" happened to an account of someone who reported issues to my project and GitHub has silently hidden all those issues. Support basically told me they would not help restore the data, that this is by design, and that I should open a feature request.

@daniel@gultsch.social

After gradually moving all my code repositories from to @Codeberg I have now disabled my Github Sponsors account. A very big thank you to everyone who has supported me over the years. 😍

Not just in light of recent events - after all this is a process I started over two years ago - but also in light of recent events I want to have as little dependencies as possible to platforms run by the Tech Oligarchs.

@pooza@mstdn.b-shock.org
@jonsnow@mastodon.online

Copilot exposes private GitHub pages, some removed by Microsoft

Microsoft’s Copilot AI assistant is exposing the contents of more than 20,000 private GitHub repositories from companies including Google, Intel, Huawei, PayPal, IBM, Tencent and, ironically, Microsoft.

arstechnica.com/information-te

arstechnica.com

Copilot exposes private GitHub pages, some removed by Microsoft

Repositories, once set to public and later to private, still accessible through Copilot.

@jwildeboer@social.wildeboer.net

is to replace and for 95% of your FOSS projects, IMHO. Or you can take it to the next level and run your own little instance as a (rootless) container, completely self-contained. And (hopefully) soon we will see more features in , leading to a decentralised network of forges that can talk to each other to form a sustainable and resilient global network. (FTR: I've been running my Forgejo instance since 1.5 years now, all is good)

@release_bot@mstdn.b-shock.org
@jscholes@dragonscave.space

Decided to sign up for , the alternative that the Fediverse at large is insisting is worth a try and, in some cases, claiming will improve project contributions by avoiding some of the GH antipatterns. I expected to find some issues; this is the modern web, after all.

I did not expect a fully inaccessible visual CAPTCHA with no workarounds. I'm unable to solve it, so I cannot create an account.

In short: If you want people who are or to contribute to your projects (you do, right?), Codeberg is currently not an platform.

@daniebeler@techhub.social

So we decided on a name for our new project: Socialfolio

We already bought the domain socialfolio.me

Also the Github repos are public now.
Frontend: github.com/Hiebeler/socialfoli
Backend: github.com/Hiebeler/socialfoli

We are planning to release the first beta version in about one to two weeks.

github.com

GitHub - Hiebeler/socialfolio-backend

Contribute to Hiebeler/socialfolio-backend development by creating an account on GitHub.

@jscholes@dragonscave.space

Decided to sign up for , the alternative that the Fediverse at large is insisting is worth a try and, in some cases, claiming will improve project contributions by avoiding some of the GH antipatterns. I expected to find some issues; this is the modern web, after all.

I did not expect a fully inaccessible visual CAPTCHA with no workarounds. I'm unable to solve it, so I cannot create an account.

In short: If you want people who are or to contribute to your projects (you do, right?), Codeberg is currently not an platform.

@daniebeler@techhub.social

So we decided on a name for our new project: Socialfolio

We already bought the domain socialfolio.me

Also the Github repos are public now.
Frontend: github.com/Hiebeler/socialfoli
Backend: github.com/Hiebeler/socialfoli

We are planning to release the first beta version in about one to two weeks.

github.com

GitHub - Hiebeler/socialfolio-backend

Contribute to Hiebeler/socialfolio-backend development by creating an account on GitHub.

@qiita@rss-mstdn.studiofreesia.com
@release_bot@mstdn.b-shock.org
@pi_crew@social.project-insanity.org

The German Green party @GrueneBundestag open-sourced their campaigning mobile app on github.com/verdigado/gruene-ap It's cross-platform and uses @openstreetmap for tracking distributed flyers and election posters. Might be useful for other use cases too :)

Screenshot of mobile app showing a form where address information could be added
ALT text

Screenshot of mobile app showing a form where address information could be added

Screenshot of mobile app showing a base map and inserted green marks
ALT text

Screenshot of mobile app showing a base map and inserted green marks

@frenck@fosstodon.org

🌹 𝗥𝗼𝘀𝗲𝘀 𝗮𝗿𝗲 𝗿𝗲𝗱,
💙 𝗩𝗶𝗼𝗹𝗲𝘁𝘀 𝗮𝗿𝗲 𝗯𝗹𝘂𝗲,
🏠 𝗚𝗶𝘁𝗛𝘂𝗯 𝗲𝗺𝗽𝗼𝘄𝗲𝗿𝘀 𝗛𝗼𝗺𝗲 𝗔𝘀𝘀𝗶𝘀𝘁𝗮𝗻𝘁,
🥰 𝗔𝗻𝗱 𝘀𝗼 𝗱𝗼 𝘆𝗼𝘂!

From smart homes to smart hearts, here’s to the developers, contributors, and every Home Assistant user making their homes better for their families, loved ones, the community, and themselves—one open-source contribution at a time! 🫶

@homeassistant

@heiseonlineenglish@social.heise.de
@st1nger@infosec.exchange

Spin up a based environment that emulates . We define the environment using the devcontainer.json spec and establish a secure tunnel to mount your local file system on a remote server. This setup runs on Cloud, starts in under 5 minutes, and costs less than one-sixth the price of GitHub Codespaces. devcontainer.community/2025021

devcontainer.community

Build Your Own GitHub Codespaces Alternative in 222 Lines of Pulumi

We use Pulumi to spin up a cloud-based development environment that emulates GitHub Codespaces. We define the environment using the devcontainer.json spec and establish a secure tunnel to mount your local file system on a remote server.

@heiseonlineenglish@social.heise.de
@lukas@indieweb.social

Does anybody have experience with developing and hosting packages on @Codeberg and then distributing them through ?

I was able to set up a Packagist webhook on but am wondering if there's any best practices or pitfalls to be aware of. Most packages are on , so this would be a more unique setup.

@jfparis@rouge.eu.org

I have a couple of integration on and to my surprise, people use them.

Every so often they break (API changes) and people report issues. The annoying bit though is when the issues keep coming afterwards because folks cannot be bothered with checking the last version or recently closed issues or the "it's broken can you help - End of report"

I am now experimenting with Issue Templates to see if that can help

@mre@mastodon.social

Wow, GitHub reeeally has issues with their frontend nowadays...

- Rendering issues (not removing/adding DOM elements) e.g. for CI status updates.
- Sometimes text from comments/issues stays on the page even after submitting.
- Weird, broken UI that gets fixed with a reload.

Ever since they moved to React, things went sideways. Not blaming React, but the rewrite in general. It's a hard problem, but it's starting to get annoying.

@qiita@rss-mstdn.studiofreesia.com
@dwn@dwnfonts.cc

等 用户想下载需要的软件,却下载到一个被原作者有意篡改,几乎不可用的甚至带有恶意软件行为的软件的时候,GitHub 会为此买单的。
所以我的新项目转向 了。但是我不知道怎么选择。
等下一次 GitHub 发癫的时候,我将归档我在 GitHub 的大部分仓库。接下来,怎样才是最适合的?征求你们的意见。

@poll

  • 转向 Codeberg1 (25%)
  • 自建 Forgejo 实例,免费获取原公开仓库3 (75%)
  • 自建 Forgejo 实例,付费获取原公开仓库0 (0%)
@dcz@fosstodon.org
@yorgos@chaos.social

Really excited to be starting to focus more and more of my time into building a better home for , on top of @radicle - a peer-to-peer forge !

and (or any $megacorp) cannot be trusted as the sole hosts of any , like .

It's time to take back some of that control, before it's too late.

With , you can seed projects, like you seed - ensuring that they stay available, despite corporate agendas.

@qiita@rss-mstdn.studiofreesia.com
@petersuber@fediscience.org

This is very welcome news in the face of Trumpist depredations of US public data.
lil.law.harvard.edu/blog/2025/

"In recent months the Harvard Law School [@harvard_law] Library Innovation Lab [@harvardlil] has created a data vault to download, sign as authentic, and make available copies of public government data that is most valuable to researchers, scholars, civil society and the public at large across every field. To begin, we have collected major portions of the datasets tracked by data.gov, federal repositories, and ...."

lil.law.harvard.edu

Preserving Public U.S. Federal Data | Library Innovation Lab

@ottoto2017@prattohome.com

を調べています。

2025年1月のスキャンで、
domain数: 25,883
でした。

もう少し深堀して、いわゆる「おひとり様」domain の数を調べると
おひとり様: 7,494

の 約3割を「おひとり様」が占めているのは驚き。(活動中)

内、wordpress が 3,362 (おひとり様の内45%)。

結構面白い結果だ。

​ ​

@ottoto2017@prattohome.com

を調べています。

2025年1月のスキャンで、
domain数: 25,883
でした。

もう少し深堀して、いわゆる「おひとり様」domain の数を調べると
おひとり様: 7,494

の 約3割を「おひとり様」が占めているのは驚き。(活動中)

内、wordpress が 3,362 (おひとり様の内45%)。

結構面白い結果だ。

​ ​

@Pixelix@mastodon.social

✨ Hey Pixelix fans! ✨

We are excited to share that Pixelix now has a Liberapay account!
If you love the app and want to support its development, you can now contribute through recurring donations. Your support means everything and helps to keep Pixelix growing and improving. 🌱

Liberapay: liberapay.com/pixelix/

Github: github.com/daniebeler/pixelix

Thank you for being part of this journey! 🙌

github.com

GitHub - daniebeler/pixelix: Android Client for Pixelfed

Android Client for Pixelfed. Contribute to daniebeler/pixelix development by creating an account on GitHub.

@qiita@rss-mstdn.studiofreesia.com
@daniebeler@techhub.social

In the last two weeks a crazy amount of 46 issues were created in the repository.

24 of them are still open and we are working hard on implementing that requests and fixing the bugs.

Check it out, and feel free to open an issue if you experience a bug or have an idea for a new feature.

github.com/daniebeler/pixelix/

github.com

daniebeler/pixelix

Android Client for Pixelfed. Contribute to daniebeler/pixelix development by creating an account on GitHub.

@botkit@hollo.social

📢 Important announcement! 's repository has moved to a new home! 🏠

The repository is now located at @fedify-dev/botkit (previously @dahlia/botkit). All future development will continue at the new location.

Don't worry—everything's the same, just a new address! Please update your bookmarks and project references. Thanks for being part of our community! :botkit:

https://hollo.social/@fedify/0194a851-581d-779c-b777-dc39e753ef14

hollo.social

We've just moved the #Fedify p…

We've just moved the #Fedify project and related repositories to our new GitHub organization account, [@fedify-dev]! 🎉 Here's what moved: - [@dahlia/fedify](https://github.com/dahlia/fedify) → [@fedify-dev/fedify](https://github.com/fedify-dev/fedify) - [@dahlia/botkit](https://github.com/dahlia/botkit) → [@fedify-dev/botkit](https://github.com/fedify-dev/botkit) - [@dahlia/hollo](https://github.com/dahlia/hollo) → [@fedify-dev/hollo](https://github.com/fedify-dev/hollo) - [@dahlia/fedify-amqp](https://github.com/dahlia/fedify-amqp) → [@fedify-dev/amqp](https://github.com/fedify-dev/amqp) - [@dahlia/fedify-h3](https://github.com/dahlia/fedify-h3) → [@fedify-dev/h3](https://github.com/fedify-dev/h3) - [@dahlia/fedify-express](https://github.com/dahlia/fedify-express) → [@fedify-dev/express](https://github.com/fedify-dev/express) - [@dahlia/fedify-postgres](https://github.com/dahlia/fedify-postgres) → [@fedify-dev/postgres](https://github.com/fedify-dev/postgres) - [@dahlia/fedify-redis](https://github.com/dahlia/fedify-redis) → [@fedify-dev/redis](https://github.com/fedify-dev/redis) - [@dahlia/markdown-it-hashtag](https://github.com/dahlia/markdown-it-hashtag) → [@fedify-dev/markdown-it-hashtag](https://github.com/fedify-dev/markdown-it-hashtag) - [@dahlia/markdown-it-mention](https://github.com/dahlia/markdown-it-mention) → [@fedify-dev/markdown-it-mention](https://github.com/fedify-dev/markdown-it-mention) - [@dahlia/fedichatbot](https://github.com/dahlia/fedichatbot) → [@fedify-dev/fedichatbot](https://github.com/fedify-dev/fedichatbot) - [@dahlia/microblog](https://github.com/dahlia/microblog) → [@fedify-dev/microblog](https://github.com/fedify-dev/microblog) All repositories have been transferred and GitHub's automatic redirects are in place, so existing links will continue to work. Also, the project's core functionality and development process remain unchanged. Thanks to everyone who participated in our naming poll. Looking forward to Fedify's continued growth under its new organizational home! :fedify: New GitHub organization: <https://github.com/fedify-dev>. [@fedify-dev]: https://github.com/fedify-dev

We've just moved the project and related repositories to our new GitHub organization account, @fedify-dev! 🎉

Here's what moved:

All repositories have been transferred and GitHub's automatic redirects are in place, so existing links will continue to work. Also, the project's core functionality and development process remain unchanged.

Thanks to everyone who participated in our naming poll. Looking forward to Fedify's continued growth under its new organizational home!

:fedify: New GitHub organization: https://github.com/fedify-dev.

github.com

Fedify

A collection of development tools for fediverse. Fedify has 12 repositories available. Follow their code on GitHub.

@daniebeler@techhub.social

In the last two weeks a crazy amount of 46 issues were created in the repository.

24 of them are still open and we are working hard on implementing that requests and fixing the bugs.

Check it out, and feel free to open an issue if you experience a bug or have an idea for a new feature.

github.com/daniebeler/pixelix/

github.com

daniebeler/pixelix

Android Client for Pixelfed. Contribute to daniebeler/pixelix development by creating an account on GitHub.

@MapComplete@en.osm.town

For the past few months, we've been working on decreasing our dependence on - most notably, our dependence on via .

We've been experimenting with @forgejo (which is very enjoyable), setup the build proces on our own hardware.

Since yesterday, the main instance is also hosted by . There are still a few dependencies, but the main hurdles have been taken!

@release_bot@mstdn.b-shock.org
@qiita@rss-mstdn.studiofreesia.com
@petersuber@fediscience.org · Reply to petersuber

Update. Here's a good use of to track textual changes and page takedowns on federal govt web sites since took office.
404media.co/github-is-showing-

This project is dedicated to the pages on . I hope someone launches a similar project on the pages dedicated to science and research.

404media.co

GitHub Is Showing the Trump Administration Scrubbing Government Web Pages in Real Time

Watch the Trump administration play DEI whac-a-mole on this government agency's GitHub page.

@qiita@rss-mstdn.studiofreesia.com
@sc0v0ne@mastodon.social
@Codeberg@social.anoxinon.de · Reply to Codeberg

We have restored service, but we are currently having issues with IPv6 connectivity (so down to service levels only).

We will fix this as soon as possible.

The good news: Since we recently improved our Ceph setup, recovery of the service was much quicker than before, because the server could immediately reconnect to the three server ring.

@lavaeolus@fedihum.org

After just having done so (with consent):
Dear of all fields - if you use to host your research software, please mirror your repos to alternatives like @Codeberg, @swheritage or repositories like zenodo (also data).
Its very easy: docs.codeberg.org/advanced/mig

No one knows if and when Microsoft/GitHub will go the route of Meta etc. pp.
Better be prepared now

Or at least consent to me forking your repos
@academicchatter @academicsunite

docs.codeberg.org

Migrating Repositories | Codeberg Documentation

@Hiebeler05@techhub.social

We just released the latest update.🥳

There are a huge number of bug fixes and also new features like editing the title of a collection and a back to top button in timelines.

The update is already available as APK on Github. It will be available on Google Play Store in the next few hours, and on F-Droid in the next few days.

github.com/daniebeler/pixelix/

Release Pixelix v3.2.1 · daniebeler/pixelix

Changes Bug Fixes Infinite loading collections Add editing title of collections Fix wrong aspect ratio of posts Add return to top button Improving notifications Animate like and boost icon

@applech2@rss-mstdn.studiofreesia.com
@harrysintonen@infosec.exchange

The feature we've all been waiting for: Disabling that Copilot nonsense.

Option to disable GitHub Copilot.
ALT text

Option to disable GitHub Copilot.

@Hiebeler05@techhub.social

We just released the latest update.🥳

There are a huge number of bug fixes and also new features like editing the title of a collection and a back to top button in timelines.

The update is already available as APK on Github. It will be available on Google Play Store in the next few hours, and on F-Droid in the next few days.

github.com/daniebeler/pixelix/

Release Pixelix v3.2.1 · daniebeler/pixelix

Changes Bug Fixes Infinite loading collections Add editing title of collections Fix wrong aspect ratio of posts Add return to top button Improving notifications Animate like and boost icon

@harrysintonen@infosec.exchange

The feature we've all been waiting for: Disabling that Copilot nonsense.

Option to disable GitHub Copilot.
ALT text

Option to disable GitHub Copilot.

@harrysintonen@infosec.exchange

The feature we've all been waiting for: Disabling that Copilot nonsense.

Option to disable GitHub Copilot.
ALT text

Option to disable GitHub Copilot.

@release_bot@mstdn.b-shock.org
@vincentbiret@hachyderm.io
@david_chisnall@infosec.exchange

PSA: Important warning for anyone considering using git-lfs with a repository to reduce clone size in CI, important warning. There is a tiny bandwidth limit (1 GB/month) for the free tier of git-lfs. There is no bandwidth limit for git clone if you are not using git-lfs. It is very easy to accidentally exhaust this quota with a few CI runs and then you cannot clone the repo until you pay GitHub or wait for the next month.

Oh, and for extra fun, the only way to actually delete files from LFS is to delete and recreate the repository (which loses all issues, PRs, and everything else), so if you go over the storage quota there is no way back ever.

In summary: Do not enable git-lfs on a free GitHub repo. You will absolutely regret it.

@lavaeolus@fedihum.org

After just having done so (with consent):
Dear of all fields - if you use to host your research software, please mirror your repos to alternatives like @Codeberg, @swheritage or repositories like zenodo (also data).
Its very easy: docs.codeberg.org/advanced/mig

No one knows if and when Microsoft/GitHub will go the route of Meta etc. pp.
Better be prepared now

Or at least consent to me forking your repos
@academicchatter @academicsunite

docs.codeberg.org

Migrating Repositories | Codeberg Documentation

@davidism@mas.to

Introducing modify-repos, a framework for quickly writing scripts that modify and create PRs for multiple repos at once. I was inspired by all-repos, but had different opinions about how things should work. Just used this to successfully sync some changes across all the Pallets repos 🤖 github.com/davidism/modify-rep

github.com

GitHub - davidism/modify-repos: Apply changes across multiple repos at once.

Apply changes across multiple repos at once. Contribute to davidism/modify-repos development by creating an account on GitHub.

@daniebeler@techhub.social

We just released the latest update. It fixes some major bugs, including the bug where it was not possible to login on some instances like pixey.org or pixelfed.fr.

There are also some cool new features. Have fun with the app!

The update is already available as APK on Github. It will be available on Google Play Store in the next few hours, and on F-Droid in the next few days.

github.com/daniebeler/pixelix/

@irfan@sakurajima.social

New users: Please don't use the "official" app - it's really poor and has been that way since its existence. The photo sharing experience is horrible, and even the photo viewing experience is scuffed - the scrolling is choppy, alt messages don't show, it couldn't even display most photos properly in the correct size/ratio (same with uploading too). You might need it for certain features that are currently unsupported by the other clients (Pixelfed isn't the best when it comes to supporting their 3rd party clients/devs, to say the least), yet despite that, you will almost guarantee a much better experience using 3rd party apps than their own.

If you're on
/ user: you're in luck cos you get to install (formerly known as ) which really is the (only) perfect Pixelfed app available, it's and completely free on the App Store. I think it's also worth noting that the developer behind this amazing app is also building a (FOSS) federated photo sharing platform (akin to Pixelfed and ) of their own called Vernissage due to Pixelfed's own limitations/shortcomings - it's not available to the public yet I don't think, but might be worth going for in place of both Pixelfed and IG in the future.

If you're on
, you have several options including but the most decent Pixelfed client I've found is . The app itself, from the Play Store is not free but it is FOSS and you can still download and install it for free using its APK that you can find from their repo. The photo viewing experience is great, the photo sharing exp is not as polished as Impressia (which is expected seeing how young the project is), but it is overall a very solid option and hands down better than the official app.

🔗 https://apps.apple.com/us/app/impressia-for-pixelfed/id1663543216

🔗 https://play.google.com/store/apps/details?id=com.daniebeler.pfpixelix

🔗 https://github.com/daniebeler/pixelix

🔗 https://vernissage.photos

vernissage.photos

Vernissage - Home timeline

@nibushibu@vivaldi.net
@chikl@digitalcourage.social

Do you have any experiences with AI creating issues on your repo? Someone opened an issue for Lightbeam and I'm unsure whether it was generated by an AI: codeberg.org/chikl/Lightbeam/i. On one hand the "someone" knows details about the extension like the " 'Websites visited' value" but on the other hand nobody would use the term "Mozilla Firefox web browser" all the time. Maybe in the first sentence but then you would use only "Firefox". And there are other indications for an AI...

codeberg.org

Lightbeam do not work at all when Mozilla Firefox is sandboxed with Sandboxie Classic software

**Lightbeam** unfortunately do not work at all when **Mozilla Firefox** web browser is sandboxed with **Sandboxie Classic** software. This bug/error is easily to reproduce, since the **Sandboxie Classic** software is an open-source OS-level virtualization solution for Microsoft Windows OS. T...

@qiita@rss-mstdn.studiofreesia.com
@pooza@mstdn.b-shock.org

「美食丼」 2025版紹介

mstdn.b-shock.org/

2017/4のマストドンブームに便乗して立てられたサーバーの生き残りです。
個人サーバーなので、特にテーマはありません。

■どんな人にお勧め?
積極的にメンバー募集はしていませんが、

・ぷーざ個人の知人(他サーバーでの活動を通して知り合った方も含む)の、普段づかいのサーバーとして。
・Annict連携の機能がある為、アニメファンとしての活動拠点としても適していると思います。

■独自機能
github.com/pooza/mulukhiya-too

■登録
承認制ですので、意気込みが必要です。ただのスパムよけなので、適当でいいんですけど。
また、招待は全メンバーに解放しています。

github.com

GitHub - pooza/mulukhiya-toot-proxy: Fediインスタンスへの投稿に対して、ハッシュタグの追加等を行うプロキシ。通称「モロヘイヤ」。

Fediインスタンスへの投稿に対して、ハッシュタグの追加等を行うプロキシ。通称「モロヘイヤ」。. Contribute to pooza/mulukhiya-toot-proxy development by creating an account on GitHub.

@pooza@misskey.delmulin.com

ダイスキー 2025版紹介

■テーマ
「ドラゴンクエスト ダイの大冒険」ファンの為のサーバーです。

■目的
ダイスキーはMastodonサーバー「
デルムリン丼 」を、機能面で補う目的で立てられました。
デルムリン丼本来のアイデンティティは、MastodonではなくFediverseの一員でした。最初に立てられたサーバーがMastodonだったからといって、Mastodonを特別に支持していたわけではありません。

ダイスキーもデルムリン丼同様、全ての投稿にデフォルトハッシュタグ
が加えられます。
この機能により、2つのサーバーはひとつのローカルタイムラインを共有し、共通のコミュニティを形成します。MastodonとMisskey、それぞれぞれのサーバーの長所や個性を生かし、垣根なく「ダイの大冒険」の話題に参加することが可能になります。

■活動
「デルムリン丼」に準じます。ダイスキーでは、デルムリン丼で行われていた全ての活動に参加できます。

毎週土曜のあの時間(9:30〜10:00)に新アニメの実況会を行っていましたが、2024年末に無事に完走しました。2025年からもお楽しみ頂けるよう、新たな実況会の企画を準備中です。
デルムリン丼と同等の実況用固定タグ機能を有しており、これを利用しながら実況に参加することができます。

劇中ワードをタグ化する機能には、デルムリン丼と同じ辞書を使用しています。
劇中の1,400ワード(2025/1現在)ほどは既に登録済みで、現時点でも本編(スピンオフ作品「獄炎の魔王」含む)の主要な話題を網羅します。ダイ大を「語る」ことを好むファンにとって、これらの機能は大いに役に立つことでしょう。
この機能にはコミュニティ指向もあり、辞書登録はメンバー誰でも参加することが出来ます。

デルムリン丼にないMisskey由来の機能として、絵文字やリアクションがあります。既に多くのダイ大絵文字がメンバーの手で作成されており、その全てを使ってリアクションを行うことが可能です。
ダイスキーは、Misskey由来の文化とダイ大というテーマを併せ持つ、全く新しいサーバーです。

このほか、アニメ視聴に特化した多くの
独自機能 があります。

■登録
スパムユーザーへの対策として、招待制にさせて頂いています。
Misskeyに承認制が実装されたら是非利用させて頂きたいですが、当面は既存メンバーからの招待を受ける必要があります。何卒ご了承下さい。
私
@pooza や他のメンバーに対して、「ダイスキーを利用したい」と(できればダイ大ファンとしての意気込みと一緒に)伝えて頂ければ、大抵はご招待が出来るかと存じます。

github.com

GitHub - pooza/mulukhiya-toot-proxy: Fediインスタンスへの投稿に対して、ハッシュタグの追加等を行うプロキシ。通称「モロヘイヤ」。

Fediインスタンスへの投稿に対して、ハッシュタグの追加等を行うプロキシ。通称「モロヘイヤ」。. Contribute to pooza/mulukhiya-toot-proxy development by creating an account on GitHub.

「キュアスタ!」 2025版紹介

precure.ml/

■テーマ
プリキュアシリーズのファンの為のサーバーです。

■活動
実況中心です。ニチアサの本放送だけでなく、各種ネット配信なども。
概ね毎日、何かしらの実況をしています。

■機能
デフォルトハッシュタグは
。また、劇中用語が自動でタグ化します。(辞書登録は随時。2025/1現在で、3,600ワードほど)
このほか、アニメ視聴に特化した多くの独自機能があります。
github.com/pooza/mulukhiya-too

■主なボット
・真琴さん
「キュアソード本人を自称するニセモノ」という設定の、チャットボット。
当鯖のマスコットだが、実況日程をリマインドする実用的な役割も。

・増子
プリキュア関連のニュースを投稿。

■登録
承認制ですので、プリキュアファンとしての意気込み等が必要です。(スパム対策なので、推しキュアを書くだけでもおK)
また、招待は全メンバーに解放しています。

■関連サーバー
同じデフォルトハッシュタグを共有する姉妹サーバー、きゅあすきーもあります。

きゅあすきー
mk.precure.fun

デフォルトハッシュタグの連合
lm.korako.me/post/106566

lm.korako.me

デフォルトハッシュタグの連合 - 鴉は拠り所について語り合う

この記事は、「Fediverse Advent Calendar 2024」に参加しています。空いていた12/9の記事として書かせて頂きました。 - 第1会場 [https://adventar.org/calendars/10051] - 第2会場 [https://adventar.org/calendars/10064] - 第3会場 [https://adventar.org/calendars/10242] - 第4会場 [https://adventar.org/calendars/10836] ## 自己紹介 はじめまして、「ぷーざ」と申します。Fediverse(以下、Fedi)との付き合いは長く、今年で7年となります。Fediには多くの同士がいるであろう、「2017年4月組」の中のひとりです。 自分の場合は最初から自分のサーバーを立てるつもりで、記録によれば4月15日にPawoo [https://mstdn.jp]にお試しアカウントを作成したのが最初で、5日後の4月20日に最初のサーバーである美食丼 [https://mstdn.b-shock.org]を立てました。 その後、以下のような経歴を経て、 - 2017/05/09 きゅあったー(現キュアスタ! [https://mstdn.b-shock.ml])に登録。 - 2019/01/11 こちそうフォト [https://gochisou.photo]に登録。 - 2019/06/24 キュアスタ! [https://mstdn.b-shock.ml]の2代目管理人に。 - 2021/03/17 デルムリン丼 [https://mstdn.delmulin.com]を設立。 - 2023/02/27 きゅあすきー [https://mk.precure.fun]に登録。 - 2023/03/17 ダイスキー [https://misskey.delmulin.com]を設立。(デルムリン丼2周年) 現在は、Fediの中で以下の4サーバーを所有する管理人(以下、鯖缶)として活動させて頂いています。 - 美食丼 [https://mstdn.b-shock.org/] 壁打ち・汎用(Mastodon) - キュアスタ! [https://mstdn.b-shock.ml/] プリキュアシリーズテーマサーバー(Mastodon) - デルムリン丼 [https://mstdn.delmulin.com/] 「ドラゴンクエスト ダイの大冒険」テーマサーバー(Mastodon) - ダイスキー [https://misskey.delmulin.com]「ドラゴンクエスト ダイの大冒険」テーマサーバー(Misskey) また、自分で管理はしていませんが、キュアスタ! [https://mstdn.b-shock.ml]とは別のプリキュアシリーズのテーマサーバーきゅあすきー [https://mk.precure.fun](Misskey)にも参加しています。 ここで、プリキュアではキュアスタ! [https://mstdn.b-shock.ml]ときゅあすきー [https://mk.precure.fun]、ダイの大冒険(以下、ダイ大)ではデルムリン丼 [https://mstdn.delmulin.com]とダイスキー [https://misskey.delmulin.com]。といった具合に、それぞれで同テーマのMastodonとMisskeyのサーバーに参加していることに注目してください。 この様な、同テーマのサーバーを複数運用する管理手法のご紹介が、この記事のお題です。 ## デフォルトハッシュタグ 自分はFediに関わるようになる前から、プリキュアシリーズやダイ大のファンです。 Fediの中で、同じ作品のファン同士でコミュニティを作る方法はいくつかあります。プリキュアを例にすれば、 #プリキュア などと作品名のハッシュタグを公開投稿に加えるのはまずお手軽ですし、キュアスタ! [https://mstdn.b-shock.ml]の様なテーマサーバーを立て、ローカルタイムラインで会話するという手法もあります。 どちらの方法もグループチャットに近いもので、同じタイムラインを共有していることを前提としています。相手は特定せずに投稿することが多く、この場合、はたからはエアリプに見える投稿も名目上はメンバー全員に宛てた投稿となります。 作品名のハッシュタグで会話する前者の方法には「サーバーの垣根が超えられる」というFediならではの利点がありますし、後者のテーマサーバーにはサーバー自体に作品に特化したカスタマイズが加えられるという別の利点があります。この両方の利点を享受できる管理手法が「デフォルトハッシュタグ」です。(縮めて「デフォルトタグ」とも) デフォルトハッシュタグを実現するには、以下の対応が必要とされます。 1. すべての公開投稿に同じハッシュタグを追加する機能追加。(追加されるタグを「デフォルトハッシュタグ」と呼ぶ) 1. サーバーのローカルタイムラインを、このデフォルトハッシュタグのタイムラインと置き換える機能追加。 後者は強く推奨されるものの、実際にはオプションで、「デフォルトハッシュタグのタイムラインをローカルタイムラインだと思ってください」という運用やコンセンサスで代えることも可能と思います。 デフォルトハッシュタグの面白いところは、デフォルトハッシュタグも他のサーバーからみれば普通のハッシュタグのひとつですから、サーバーの垣根を超えた乗り入れが可能なところです。 他サーバーからデフォルトハッシュタグを伴う公開投稿を行うことは、そのサーバーのゲストとして振る舞うことに似ています。「テーマサーバーに登録するほどではないが…」という選択肢をユーザーに対して柔軟に提供できるところが、このアイデアの優れた点であると私は感じます。 この「デフォルトハッシュタグ」は、当然ながら私が発明した概念ではありません。 記録 [https://hisubway.online/articles/mstdnwiki/%E3%83%AD%E3%83%BC%E3%82%AB%E3%83%AB%E3%82%BF%E3%82%A4%E3%83%A0%E3%83%A9%E3%82%A4%E3%83%B3%E3%82%92%E3%83%87%E3%83%95%E3%82%A9%E3%83%AB%E3%83%88%E3%82%BF%E3%82%B0%E3%82%BF%E3%82%A4%E3%83%A0%E3%83%A9%E3%82%A4%E3%83%B3%E3%81%AB%E7%BD%AE%E3%81%8D%E6%8F%9B%E3%81%88%E3%82%8B.html#.E6.8E.A1.E7.94.A8.E3.81.97.E3.81.A6.E3.81.84.E3.82.8B.E3.82.A4.E3.83.B3.E3.82.B9.E3.82.BF.E3.83.B3.E3.82.B9]によればtheboss.techというサーバーで実装されたのが最初で、その後複数のサーバーで採用されたとあります。冒頭に私の参加しているサーバーを挙げましたが、気づけば美食丼 [https://mstdn.b-shock.org]以外の全てにデフォルトハッシュタグがありますね。 ## MastodonとMisskey 長年Mastodonを利用し続けていた自分ですが、Misskeyにも興味を持ちました。とりわけ、カスタム絵文字による「リアクション」が利用できるのは、Mastodonにはない利点だと思います。 自分が管理していたテーマサーバー(及びデフォルトタグ #precure_fun と #delmulin のコミュニティ)に、カスタム絵文字などMisskey由来の要素を採り入れるにはどうすればいいか? 「Mastodonにリアクション対応の改造を加える」というFedibird [https://fedibird.com]のガチすぎる対応は既に存在しましたが、その様な大規模な改造は自分には到底手に負えないです。 デフォルトタグを持ったサーバーの鯖缶である自分は、そこで自分なりの方法を考えました。Fedibird [https://fedibird.com]のような改造が直球であるとすれば、「同じデフォルトタグを持ったMisskeyをもう一つ立ち上げる」という変化球めいたアイデアです。 各サーバーが同じデフォルトハッシュタグを持つなら、ローカルタイムライン(Misskey側では「ホームタイムライン」)も同じものになることに注目してください。実質的には、それぞれのサーバーが同一のコミュニティに参加していることになりますね。 ユーザーは、MastodonとMisskeyの好きな方(使い慣れている方)を選べる利点がありますし、ヘビーユーザーの方は用途に応じて使い分けて頂くこともできます。 とはいえその頃(2023年)、既に3つのMastodonを持っていた自分には、更に追加で2つのMisskeyを管理することが難しく感じられました。 このアイデアを長年キュアスタ! [https://mstdn.b-shock.ml]を支えてきた同志である先代管理人、鴉河雛 [https://md.korako.me/@karasu_sue]さんに相談したところ、 #precure_fun 側のMisskeyを受け持つことを快く引き受けてくれました。この経緯によって誕生したMisskeyサーバーがきゅあすきー [https://mk.precure.fun]で、同時に自分も #delmulin 側の新しいMisskeyサーバーダイスキー [https://misskey.delmulin.com]を新設したわけです。 ## Mastodon側の対応 Mastodon側ではデフォルトハッシュタグ自体のルーツであるtheboss.tech由来の改造や、そのバリエーションが一般的な様ですが、自分は拙作ツールmulukhiya-toot-proxy [https://github.com/pooza/mulukhiya-toot-proxy](通称「モロヘイヤ」)にこの仕事をやらせています。 デフォルトハッシュタグ対応は、以下の要素で構成されると前述しました。 1. すべての公開投稿に同じハッシュタグを追加する機能追加。(追加されるタグを「デフォルトハッシュタグ」と呼ぶ) 1. サーバーのローカルタイムラインを、このデフォルトハッシュタグのタイムラインと置き換える機能追加。 モロヘイヤ [https://github.com/pooza/mulukhiya-toot-proxy]に担当させているのは前者で、後者の対応はnginxだけで行っています。少なくともデフォルトハッシュタグ実現の為に、Mastodon本体への改造を行っていないことにお気づきでしょうか。モロヘイヤにデフォルトハッシュタグを実装した時、自分はMastodonの改造を維持できる自信を持てなかったので、この判断をしました。 機能追加自体は他サーバーの改造を参考にすれば実現できますが、一方でMastodon自体も更新されるのですから、共存していかなければいけません。 改造された箇所の理解は、鯖缶の責任で必ず行わなければいけません。当時の自分にはそれが出来そうもなかったですが、それでも機能実現の手綱は自分が握っていたかったのです。 モロヘイヤ [https://github.com/pooza/mulukhiya-toot-proxy]自体の紹介は長くなるから、ここではしません。リポジトリの方をご覧ください。 ## Misskey側の対応 Misskeyにもデフォルトハッシュタグ改造がある様ですが(ふるすきー [https://mk.f72u.net]さんとか)それは採用せず、独自実装はきゅあすきー [https://mk.precure.fun]と分担して進めました。何より、既存実装を知らなかったから。 デフォルトタグの追記はMastodon同様、モロヘイヤ [https://github.com/pooza/mulukhiya-toot-proxy]で実現しています。 一方、ホームタイムラインの改造は、きゅあすきー [https://mk.precure.fun]の成果です。当時のMisskey(13.x)ではタグタイムラインのストリーミングは未実装でしたが、実は概ね動作するコードがコメントアウトで無効化された形で存在しており、それを修正してホームタイムラインとして採用したのが始まりだったと思います。 v2023.10系からFTT(Fan-out Timeline)なるRedisを活用したタイムライン技術が実装され、それまでの改造が利用できなくなりました。 Misskeyのパフォーマンス改善の取り組み⁠⁠⁠⁠・2023年11月 https://gihyo.jp/article/2023/11/misskey-08 [https://gihyo.jp/article/2023/11/misskey-08] FTT対応のホームタイムライン(及びソーシャルタイムライン)改造は、自分が行いました。 以前の改造が「ホームタイムラインのタグタイムライン化」であるとするなら、新しい改造は「デフォルトタグを持った投稿をホームタイムラインに加える」というもので、「ホーム」投稿の判定の拡張と言い換えてもよいです。 タグタイムラインをホームタイムラインとして利用していた頃は、性質の違いに悩まされたりもしました。新しい改造では「ホーム」判定の拡張だけを行っていて、性質はあくまでホームタイムラインのままだった為、挙動が予想できるものになりました。 実は一度、この改造をMisskey本家にプルリクエスト [https://github.com/misskey-dev/misskey/pull/13098]したのですが。 「一度デフォルトハッシュタグに設定したサーバーから、デフォルトハッシュタグを無効に戻すことはない」という想定で、設定項目は設定ファイルに記述する形で実装しましたが、「画面(鯖缶が利用するコントロールパネル)からも設定できなければいけない」等のご指摘を受け、採用は一旦見送られています。 その為の作業時間を捻出することが、自分にはなかなか難しい状況で、お恥ずかしながらちょっと頓挫しちゃってます。 ## リレー MastodonとMisskeyのそれぞれを改造するだけでは不十分で、実際には、互いのすべての投稿が連合タイムラインに含まれる必要があります。 つまり、構成する両サーバーを同じリレーに参加させる必要があります。 #precure_fun と #delmulin の各サーバーでは当初、日本のFediコミュニティで最初期に登場したハッシュタグリレー [https://hashtag-relay.dtp-mstdn.jp]を利用していました。 その後プライベートのリレーサービスも設けて、各サーバーから接続することにより、動作を安定させて現在に至っています。 プライベートリレーでは、めいめい [https://misskey.m544.net/@mei23]さんのpub-relayフォーク [https://github.com/mei23/pub-relay]を更にフォークして使わせて頂いています。 Crystal言語が全くわからない自分が(シンタックス自体はRubyに近いのですけどね)、この先保守を続けていける自信がないのが悩みの種で、使い慣れたRubyベースのリレーを採用することも最近は考えています。いくつかある様ですね。 ## 最後に デフォルトハッシュタグを通じて、複数のサーバー(自分たちの場合はMastodonとMisskey)を連結することができます。「採用事例が増えれば面白いのだけどな」と思い立って、自分のアイデアを紹介させて頂きました。 詳細な構築手順にまではとても踏み込めませんでしたが、ご興味ある鯖缶の方からのご質問を頂けたら歓迎します。ご用の方は、私の本アカウント [https://mstdn.b-shock.org/@pooza]まで。2025年以降のFediを、一緒に盛り上げていきましょう。

@qiita@rss-mstdn.studiofreesia.com
@xoron@infosec.exchange
@thelinuxEXP@mastodon.social
@release_bot@mstdn.b-shock.org
@qiita@rss-mstdn.studiofreesia.com
@release_bot@mstdn.b-shock.org
@qiita@rss-mstdn.studiofreesia.com
@daniebeler@techhub.social

A new version is available on . The Google Play Store Version should be available within the next few hours. We are also working on bringing the app to F-droid.

New Features:
Detailed Fediverse instance and software informations
Bookmarking button
Design refinements
Bug fixes

Get the APK here: github.com/daniebeler/pixelix/

Release Pixelix v3.1.0 · daniebeler/pixelix

New Features: Detailed Fediverse instance and software informations Bookmarking button Design refinements Bug fixes

@chucker@norden.social

We need a new dev ops solution. Issues and Wiki are secondary; we’ll probably do those in Notion (OTOH, that means good Notion integration is a plus). So this is mostly repository, pull requests, pipelines, that sort of thing.

Someone give me good arguments for over .

@spanezz@mastodon.bida.im

*ticket created*

Dear GitHub support,

I have just been notified of access to GitHub Copilot having been added to my account, and I cannot find a way to disable that.

I build my reputation on original software that I write, and I do not want risking accidental copyright infringement or worse by having github surreptitiously push "smart" features I do not need on my account.

I am writing to ask for a complete removal of Copilot features from my account. Failing that, I would like a written confirmation that Copilot is not touching anything related to my account, and possibly a procedure I can use at any time to verify and prove that to my customers.

Best regards,

Enrico Zini

@Codeberg@social.anoxinon.de

Nonprofit work is hard. It takes a lot of time, dedication and, more often than not, you see volunteers taking in multiple different tasks and responsibilities to keep everything running. Thankfully, we occasionally get external contributors that help us out!

For instance, I would post something serious so as to promote our nonprofit, but it seems like decided to help us with the marketing for the day by sending a bunch of its users (multiple) emails about GitHub Copilot. 😅

@imsnif@hachyderm.io

Woke up to pushing unsolicited stuff into your newsfeed without the possibility of opting out?

Pissed off? Me too. Here's how to disable it:

1. Download ublockorigin.com/ if you're not using it already.
2. Right click the offending elements and select "block element" until satisfied

And remember that this level of aggressive and non-consensual marketing is often indicative of a deeply failed product.

@nubesurrealista@tkz.one

La IA puede ser útil para ciertas cositas. He aprendido algo nuevo, para eso sirvió.

En este caso, yo quería una implementación para mostrar mis toots en una simple pagina de GitHub. Llevo una hora en esto T-T capaz para alguien que domine el tema es pan comido, pero para mí fue prueba y error, y asistencia de IA.

Quería hacerlo con RSS, solo habían errores...

Al final la opción más obvia salió a la luz: la API de Mastodon para acceder a la información publica de mi cuenta. Ha funcionado ^^

Es algo básico y tosco, un poco sin alma.

So, ¿Ahora que sigue? Pues, me gustaría recibir feedback, en plan, personas que si sepan de código jaja, y mejorar esto, ya sin una IA. Quiero aprender y mejorar

La página: nubesurrealista.github.io/Toot

La repo: github.com/nubesurrealista/Too

¿Alguna idea para que no parezca página de los 2000? 😖

@joschi@hachyderm.io

Are you okay, ?

A GitHub PR comment showing an internal Ruby on Rails error "#<ActiveModel::Error:0x00007fe42db64ec8>".
ALT text

A GitHub PR comment showing an internal Ruby on Rails error "#<ActiveModel::Error:0x00007fe42db64ec8>".

@teleclimber@social.tchncs.de

FYI flags that crypto in your project even if you aren't affected. It checks if you import the package, not if you actually use the affected functions. govulncheck does it correctly.

Lucky for me that means I don't have to change anything in my project.

Thanks to @filippo

Github dependabot page for project Dropserver for "Misuse of ServerConfig.PublicKeyCallback may cause authorization bypass in golang.org/x/crypto" CVE-2024-45337
ALT text

Github dependabot page for project Dropserver for "Misuse of ServerConfig.PublicKeyCallback may cause authorization bypass in golang.org/x/crypto" CVE-2024-45337

Verbose output of govulncheck on same Dropserver project showing that it is not affected by the vulnerability because we don't appear to call affect methods. Full text:

"DropServer git:(tailscale-1) ✗ govulncheck -show verbose ./...
Scanning your code and 643 packages across 83 dependent modules for known vulnerabilities...

Fetching vulnerabilities from the database...

Checking the code against the vulnerabilities...

=== Symbol Results ===

No vulnerabilities found.

=== Package Results ===

No other vulnerabilities found.

=== Module Results ===

Vulnerability #1: GO-2024-3321
    Misuse of ServerConfig.PublicKeyCallback may cause authorization bypass in
    golang.org/x/crypto
  More info: https://pkg.go.dev/vuln/GO-2024-3321
  Module: golang.org/x/crypto
    Found in: golang.org/x/crypto@v0.29.0
    Fixed in: golang.org/x/crypto@v0.31.0

Your code is affected by 0 vulnerabilities.
This scan also found 0 vulnerabilities in packages you import and 1
vulnerability in modules you require, but your code doesn't appear to call these
vulnerabilities.
ALT text

Verbose output of govulncheck on same Dropserver project showing that it is not affected by the vulnerability because we don't appear to call affect methods. Full text: "DropServer git:(tailscale-1) ✗ govulncheck -show verbose ./... Scanning your code and 643 packages across 83 dependent modules for known vulnerabilities... Fetching vulnerabilities from the database... Checking the code against the vulnerabilities... === Symbol Results === No vulnerabilities found. === Package Results === No other vulnerabilities found. === Module Results === Vulnerability #1: GO-2024-3321 Misuse of ServerConfig.PublicKeyCallback may cause authorization bypass in golang.org/x/crypto More info: https://pkg.go.dev/vuln/GO-2024-3321 Module: golang.org/x/crypto Found in: golang.org/x/crypto@v0.29.0 Fixed in: golang.org/x/crypto@v0.31.0 Your code is affected by 0 vulnerabilities. This scan also found 0 vulnerabilities in packages you import and 1 vulnerability in modules you require, but your code doesn't appear to call these vulnerabilities.

@rfc2549@fosstodon.org · Reply to IP over Parrots (with QoS)

I've now created the ansible-community organization on @Codeberg to do exactly the same: codeberg.org/ansible-community

I'm not looking to justify my personal motives for this at this time but know that it is not meant to compete with github.com/ansible-community and does not intend to spur a migration from GitHub either.

It is meant to be a neutral, general purpose place to contribute on Ansible projects together outside of GitHub because the Ansible community exists outside of .

@pedro@mastodon.pepicrft.me

Previews is a top-notch DX and mimic the same feature in platforms like Netlify or Vervel but for Apple apps.

If your team or organization builds apps, I’d recommend to give it a shot. It’s free, and you can build and share as many as you like.

And you can integrate it into to get a link on your PRs so your reviewers can also test the app easily.
fosstodon.org/@tuist/113516830

@technicat@universeodon.com

you can see when I moved my repos from to

a green hued activity graph busy from last November to July
ALT text

a green hued activity graph busy from last November to July

a blue-hued activity graph showing almost nothing until July and then busy afterwards
ALT text

a blue-hued activity graph showing almost nothing until July and then busy afterwards

@katexochen@infosec.exchange

TIL: `git archive` is used by GitHub and other forges to create an archive of a repo to download. git can do unexpected thing when creating such archive, like variable substitution using the `export-subst` feature. So even if a commit is immutable, you can still download different content if a ref or tag changed.

git-scm.com/docs/git-archive/2

Example: github.com/smallstep/cli/blob/

That's a real problem in context of reproducible builds (or just source-pinning in general).

@openresource@fosstodon.org

Better GitHub Co-Authors is a browser extension made by @swithinbank that makes easier adding co-author credit to PRs on GitHub.

It adds an "Add co-authors" button to the PR merge UI, automatically collecting all participants and generating "Co-authored-by" comments for easy credit in the commit message—perfect for acknowledging reviewers and commenters, not just code contributors! 🌟

github.com/delucis/better-gith

GitHub interface with the new "Add Co-authors" button and the extra textarea with these co-authors
ALT text

GitHub interface with the new "Add Co-authors" button and the extra textarea with these co-authors

@paulox@fosstodon.org

“Python becomes the most used language on GitHub, overtaking JavaScript after a 10-year run as the most used language. This is the first large-scale change we’ve seen in the top two languages since 2019…” 🏆

github.blog/news-insights/octo

Graph showing the growing of Python programming language to the first position
ALT text

Graph showing the growing of Python programming language to the first position

@pabuisson@ruby.social

As a code reviewer, I really dislike auto-merge feature. I often leave non-blocking comments but still approve the PR... which then gets merged automatically, without the author being able to read my comments.

Which means as a reviewer, I need either to hold my approve (→ slow everything down + require me to come back at least once more on said PR even for non-blocking comments) OR to check before approving if the PR is in auto-merge mode or not and act accordingly ☹️ annoying.

@fwilhe@social.tchncs.de

dear what am I supposed to do here in a pr by a contributor I don't know and thus don't want to trust blindly. The pr looks good but there might be malicious code hidden in there.

Screenshot of a github pull request of a github action with generated files that changed with too many changes so github won't display them.
ALT text

Screenshot of a github pull request of a github action with generated files that changed with too many changes so github won't display them.